Freedom251 › Workplace Investigation Software
SentinelOps
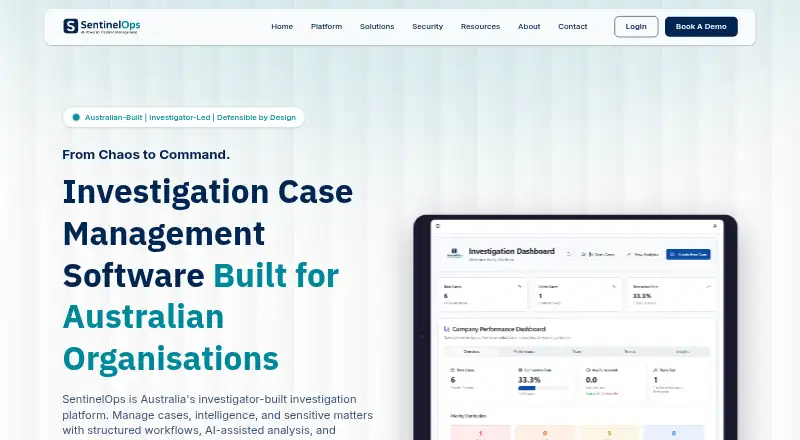
What SentinelOps is
SentinelOps is an Australian investigator-built platform for managing investigation cases and operational intelligence. It supports structured intake, triage, assignment, configurable workflows, case linking, taxonomy-based categorisation, and lifecycle tracking. Evidence tools include secure storage, integrity checks, cryptographic fingerprinting, and chain-of-custody controls. AI assistance covers pattern and anomaly detection, natural-language search, OSINT analysis, and report drafting, with investigator review and approval required. OSINT capabilities include public-source entity research, social media, corporate registries, media monitoring, and sanctions screening. Customer data is hosted only in Australian data centres, without offshore replication or cross-border transfer. Records, evidence, attachments, and audit logs are encrypted at rest and in transit; append-only audit logs are cryptographically chained and include read-access records. Users access the managed service through modern browsers on desktop, tablet, or mobile. Integrations include a RESTful API, webhooks, identity standards, and documented connected systems such as Azure AD, Okta, Splunk, Microsoft Sentinel, and Google Drive. Pricing is available on request. SentinelOps says it is not currently ISO 27001 certified and has not been assessed against a specific Essential Eight maturity level.
Who it suits
SentinelOps is intended for Australian enterprise, government, and regulated-industry organisations. Its listed audiences include security, HR, financial crime, insurance, and investigative consultancy teams.
What it does well
- Case workflows cover intake, triage, assignment, and tracking
- Evidence tools include chain-of-custody controls
- Customer data stays in Australian data centres
- Encrypted records and tamper-evident audit logs
What to know first
- Pricing is available on request
- Not currently ISO 27001 certified
- No specific Essential Eight maturity assessment
Limits
SentinelOps is a paid service and pricing is available on request. It is not currently ISO 27001 certified and has not been assessed against a specific Essential Eight maturity level.
Getting started
- Visit the SentinelOps website
- Contact the team to ask about pricing and service arrangements
- Arrange the 30-minute investigator-led demo
- Discuss hosting arrangements with the team if your organisation has specific hosting mandates
- Access the managed service through a modern browser on desktop, tablet or mobile
SentinelOps is an Australian-built investigation case-management and operational-intelligence service for organisations handling sensitive matters. It suits enterprise, government and regulated teams that need formal evidence controls alongside OSINT and investigator-reviewed AI. Its main appeal is the combination of Australian-only hosting and auditable workflows; buyers needing recognised security certifications should be cautious.
Overview
SentinelOps structures investigations from intake and triage through assignment, configurable workflow stages and lifecycle tracking. Case linking and taxonomy-based categorisation help teams connect related matters and keep large caseloads organised. This is a substantial operational system for security, HR, financial-crime, insurance and investigative-consultancy work, not a lightweight personal task tracker.
The service is managed and hosted exclusively in Australian data centres, with no offshore replication or cross-border transfer. Organisations with particular hosting mandates can discuss arrangements with the company. Australian residency is a practical advantage for local data-governance requirements, but it does not replace independent certification.
Key features
Evidence management combines secure storage, cryptographic fingerprinting, integrity verification and chain-of-custody controls. Tamper-evident, append-only audit logs are cryptographically chained and include read-access records, giving supervisors a clearer accountability trail when files are viewed or handled. Case records, evidence, attachments and logs are encrypted both in transit and at rest.
OSINT tools support public-source entity research, social media, corporate registries, media monitoring and sanctions-list screening. AI can detect patterns and anomalies, search in natural language, analyse OSINT and draft reports. Investigator review and approval remain required, so the features assist professional judgement rather than automate final decisions.
REST API access, webhooks, SAML 2.0, OpenID Connect and SCIM provisioning support integration and identity administration. Supported systems include Azure AD, Okta, Splunk, Microsoft Sentinel, QRadar, Elastic, SAP SuccessFactors, Workday, Oracle HCM, SharePoint Online and Google Drive. Interview management and findings-and-remediation workflows extend its usefulness beyond simple case registers.
Multi-factor authentication is enforced for every user, while enterprise customers can use standards-based single sign-on. The compliance design references Australian Government ISM expectations and supports AUSTRAC, Positive Duty, SOCI Act, WHS and whistleblower obligations. SentinelOps is not ISO 27001 certified and has not been assessed against a specific Essential Eight maturity level, which may disqualify it from procurement programmes requiring those credentials.
Pricing
SentinelOps uses paid, custom pricing: contact the company for a quote. That approach may suit organisations needing an appropriately scoped enterprise deployment, but it prevents straightforward budget comparison and leaves seat, usage and renewal terms to commercial discussion. The company offers a 30-minute investigator-led demo and says enquiries receive a response within one business day.
Platforms
The platform is delivered as a managed web service and API. Modern browsers provide access on desktop, tablet and mobile devices. Its Australian-hosted managed deployment avoids running infrastructure yourself, while organisations with mandatory hosting arrangements should confirm whether their requirements can be met before committing.
Who it's for
SentinelOps is aimed at Australian enterprise, government and regulated-industry organisations, including security, HR, financial-crime, insurance and investigative-consultancy teams. It is a strong fit where chain of custody, immutable auditability, local residency and integration with identity, security or HR systems are central requirements. Smaller teams seeking a low-cost, self-serve case tool, or buyers that must show ISO 27001 or a defined Essential Eight maturity assessment, should shortlist alternatives instead.
Pros and cons
Pros
- Strong evidence accountability: fingerprinting, integrity checks, custody controls and chained audit records support defensible investigations.
- Broad intelligence workflow: OSINT coverage and investigator-reviewed AI reduce manual searching and reporting work without removing approval.
- Australian data residency: exclusive local hosting and no cross-border transfer address strict domestic data-handling needs.
- Enterprise integration: API, webhooks, SSO, SCIM and numerous security, HR and document-system connectors support existing estates.
Cons
- Certification gap: it is not ISO 27001 certified and has no specific Essential Eight maturity assessment.
- Opaque cost: pricing is available only on request, so procurement teams cannot compare published plans or limits.
- Managed-service constraints: organisations with fixed hosting mandates must negotiate arrangements with the provider.
Alternatives
Workplace Investigation Software is a useful category shortlist when you want to compare several investigation products before requesting quotes.
FocusOSHR is the better starting point for a small or budget-conscious team: its free plan costs 0.00 USD forever and allows up to 10 total cases, with basic case management and five document templates, though that cap is far below an enterprise investigation workload.
Pulpstream Employee Relations suits organisations wanting a paid employee-relations platform across Android, iOS, web, Windows and API, with a flat fee per employee or user quoted by the vendor.
Safecall Investigation Case Management is a SaaS web-based investigation option when you prefer a focused product with pricing supplied on request.
Sodales Employee Relations, Civica Complaints Management and BoardEffect are alternatives with vendor-quoted pricing; consider them when their specific employee-relations, complaints or board-management scope matches your need.
Tyler CAD is the alternative to consider for self-hosted or Windows-based enterprise CAD requirements rather than investigation case management.
atworkCare is another paid web option to evaluate alongside SentinelOps.
Verdict
Choose SentinelOps if your Australian organisation needs structured investigations, defensible evidence handling, OSINT and controlled AI assistance in one managed service. Look elsewhere when ISO 27001 or a defined Essential Eight assessment is mandatory, when self-hosting is non-negotiable, or when you need transparent published pricing before engaging sales.
Verdict
SentinelOps brings case workflows, evidence handling, OSINT, and AI assistance together for investigative teams. Organisations should note its stated certification limits and confirm pricing and hosting arrangements with the company.
Questions
How is SentinelOps priced?
It is a paid service, with pricing available on request.
Where is customer data hosted?
Customer data is hosted exclusively in Australian data centres, without offshore replication or cross-border transfer.
What devices can access SentinelOps?
It is accessible in modern web browsers on desktop, tablet and mobile devices.
Does SentinelOps support single sign-on?
Enterprise customers can use standards-based single sign-on. Multi-factor authentication is enforced for every user.
Which systems does it integrate with?
Documented connections include Azure AD, Okta, Splunk, Microsoft Sentinel, QRadar, Elastic, SAP SuccessFactors, Workday, Oracle HCM, SharePoint Online and Google Drive. It also provides a RESTful API and webhooks.
Is SentinelOps ISO 27001 certified?
No. SentinelOps states it is not currently ISO 27001 certified and has not been assessed against a specific Essential Eight maturity level.
Facts from SentinelOps's own pages
- Access
- The platform is accessible through modern web browsers on desktop, tablet and mobile devices. · sentinel-ops.app, 30 Sept 2026
- AI and OSINT
- SentinelOps provides AI-assisted analysis, OSINT integration, pattern detection and intelligent report drafting. · sentinel-ops.app, 1 Oct 2026
- AI assistance
- AI features provide pattern and anomaly detection, natural-language search, OSINT analysis and report drafting while requiring investigator review and approval. · sentinel-ops.app, 30 Sept 2026
- Audience
- The platform is intended for Australian enterprise, government and regulated-industry organisations, including security, HR, financial crime, insurance and investigative consultancy teams. · sentinel-ops.app, 1 Oct 2026
- Audit trails
- Audit logs are tamper-evident, append-only and cryptographically chained, including records of read access. · sentinel-ops.app, 1 Oct 2026
- Authentication
- Multi-factor authentication is enforced for every user, and enterprise customers can use standards-based single sign-on. · sentinel-ops.app, 1 Oct 2026
- Case management
- The platform supports structured intake, triage, assignment, configurable workflows, case linking, categorisation and lifecycle management. · sentinel-ops.app, 1 Oct 2026
- Certification limit
- SentinelOps states that it is not currently ISO 27001 certified and has not been assessed against a specific Essential Eight maturity level. · sentinel-ops.app, 30 Sept 2026
- Compliance position
- SentinelOps says it is not currently ISO 27001 certified and has not been assessed against a specific Essential Eight maturity level. · sentinel-ops.app, 1 Oct 2026
- Compliance posture
- SentinelOps is designed around Australian Government ISM expectations and supports frameworks including AUSTRAC, Positive Duty, SOCI Act, WHS and whistleblower obligations. · sentinel-ops.app, 30 Sept 2026
- Connected systems
- Documented integrations include Azure AD, Okta, Splunk, Microsoft Sentinel, QRadar, Elastic, SAP SuccessFactors, Workday, Oracle HCM, SharePoint Online and Google Drive. · sentinel-ops.app, 30 Sept 2026
- Data residency
- All customer data is hosted exclusively in Australian data centres with no offshore replication or cross-border transfer. · sentinel-ops.app, 1 Oct 2026
- Deployment
- SentinelOps is delivered as a managed Australian-hosted service, while organisations with specific hosting mandates are asked to contact the team to discuss arrangements. · sentinel-ops.app, 1 Oct 2026
- Encryption
- Case records, evidence, attachments and audit logs are encrypted at rest and in transit. · sentinel-ops.app, 1 Oct 2026
- Evidence
- Evidence management includes secure storage, cryptographic fingerprinting and chain-of-custody controls. · sentinel-ops.app, 1 Oct 2026
- Evidence handling
- Evidence management includes secure storage, chain-of-custody controls and integrity verification for files. · sentinel-ops.app, 30 Sept 2026
- Headquarters
- Australia · sentinel-ops.app, 23 Sept 2026
- Integrations
- The RESTful API supports case, evidence, user, reporting and webhook integrations, with API keys, OAuth 2.0, rate limiting and IP allowlisting. · sentinel-ops.app, 1 Oct 2026
- OSINT
- OSINT capabilities cover public-source entity research, social media, corporate registries, media monitoring and sanctions-list screening. · sentinel-ops.app, 30 Sept 2026
- Purpose
- SentinelOps is an Australian investigation case management and operational intelligence platform. · sentinel-ops.app, 1 Oct 2026
- Security
- Data is encrypted in transit and at rest, with cryptographically chained tamper-evident audit logs. · sentinel-ops.app, 30 Sept 2026
- Support
- SentinelOps offers a 30-minute investigator-led walkthrough and discovery calls. · sentinel-ops.app, 1 Oct 2026
- Supported systems
- Pre-built or supported integrations include Azure AD, Okta, Splunk, Microsoft Sentinel, QRadar, Elastic, SAP SuccessFactors, Workday, Oracle HCM, SharePoint Online and Google Drive. · sentinel-ops.app, 1 Oct 2026
Where SentinelOps stands on Freedom251
- Workplace Investigation Software#25 of 29