Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
Put authorization checks at every trust boundary, with the final decision immediately before an action executes. An API gateway should authenticate the caller and enforce broad scope, an application policy layer should decide which task, tenant, data and business rules apply, and a tool broker or downstream system must independently authorize the exact action and target. Prompts can guide a model, but they cannot protect resources. Monitoring must follow the entire causal chain—from identity and retrieved context through model and guardrail decisions, tool calls, outputs and downstream effects—under one correlation ID. For destructive, financial, administrative or externally visible operations, require fresh approval and fail closed if policy, approval or audit logging is unavailable.
Where should the authorization check happen in an LLM agent?
The reliable design is layered: authenticate and limit the request at ingress, make task and data decisions in application policy, validate content and parameters with deterministic controls, re-authorize the exact tool call at execution time, and enforce permissions again in the system that owns the resource. Each layer sees different context, so no single check can replace the others.
As an Amazon Associate I earn from qualifying purchases.
| Layer | Primary decision | What it must not assume |
|---|---|---|
| API gateway or service ingress | Who is calling, which endpoint they may use, tenant boundaries, quotas and rate limits | That a model or prompt will enforce resource permissions |
| Application policy and data access | Whether the requested task, retrieval scope, data classification and business policy are allowed | That an authenticated user may access every connector, vector index or record |
| Guardrail and validation | Whether input, retrieved content, parameters and output meet safety and format rules | That a safety model can replace deterministic authorization |
| Tool broker or executor | Whether this actor may perform this exact action on this exact target now | That an earlier token or model decision is still valid |
| Resource-owning downstream system | Final permission under the system’s native access-control model | That the agent layer’s decision is sufficient |
Microsoft Learn summarizes the principle as identifying and authorizing “every user, agent, workload, plugin, and tool” before data access or action. OWASP likewise advises separating decision-making from execution: an agent may propose an action, but an independent policy or execution component validates scope, privilege and approval before it runs.
What should an API gateway or ingress layer check?
The gateway should reject unauthenticated or obviously out-of-scope requests before they consume model or retrieval resources. It provides coarse authorization and an inexpensive telemetry boundary, not the final permission decision.
#1 Best Overall

- Ultra-Compact FIDO2 Security Key - Plug-and-stay or carry on a keychain. This USB-A hardware security key offers portable, always-on protection for desktop and mobile use. (Item Size: 0.75 X 0.74 IN x 0.25 IN)
- USB-A Hardware Key for All Devices - Works with USB-A ports on PC, Mac, Android, and other laptop/notebook device. Enables secure, cross-platform login with FIDO2.0 passkey support.
- FIDO Certified Security Key - Meets FIDO and FIDO2 standards. Works with Google, Microsoft, GitHub, Dropbox, and more. Please check service compatibility before purchase.
- Passwordless Login with Passkey - Supports passkey login via WebAuthn and CTAP2. Enjoy password-free sign-ins where supported. Not all websites or services currently support passkeys.
- Advanced Multi-Factor Authentication - Offers 200 FIDO2 passkey slots and 50 OATH-TOTP slots. Strong, flexible 2FA/MFA support across various apps and authentication platforms.
- Strong authentication: Verify the user, workload or service identity and establish a tenant and session context.
- Endpoint and model scope: Permit only approved routes, operations and model classes for that identity or workload.
- Tenant isolation: Bind the request to one tenant and reject cross-tenant identifiers before they reach retrieval or tools.
- Quotas and rate limits: Apply per-user, per-tenant and, where appropriate, per-IP limits. OWASP recommends rate limiting alongside security-relevant metadata logging.
- Request hygiene: Enforce payload size, content type, timeout and protocol constraints; reject malformed or replayed requests.
- Early telemetry: Emit caller, route, operation, response status, latency, quota, rate-limit and token-use fields.
Azure API Management analytics and Azure Monitor/Application Insights can collect these gateway and agent-run signals, including metrics, logs, traces, events and OpenTelemetry data. The gateway should pass a cryptographically verifiable identity and a correlation ID downstream rather than relying on an identity string supplied by the model.
How does the application policy and data-access layer decide what is allowed?
This layer translates a natural-language task into explicit policy decisions about tenant, data, purpose and business rules. It should perform permission-aware retrieval and issue the least privilege needed for each connector, vector store, plugin or external data source.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Resolve the task and scope
Classify the requested operation (for example, read, summarize, update or send), identify the tenant and data classification, and determine whether the user is acting personally or on behalf of a team or service. A request to “find our contract” must resolve to an allowed repository and records, not to every index the application can reach.
Filter retrieval before generation
Apply document- and row-level permissions when searching vector stores or connectors. Store authorization metadata with embeddings and enforce filters at query time; hiding a forbidden document only in the prompt is too late because retrieval, caching or logging may already have exposed it.
Issue narrowly scoped credentials
Use short-lived, audience-restricted tokens or delegated user context for each connector. Microsoft recommends least privilege for all components and strict controls on external data. Revocation then takes effect at the credential or policy layer instead of waiting for a prompt or model context window to expire.
Rank #2

- USB-C or tap via NFC for easy authentication on any compatible device. No drivers needed; optional Kensington software available for advanced management features.
- Works across Windows, macOS, iOS, Android, ChromeOS, and supports Passkeys and Apple ID.
- Slim, keychain-ready form for easy carry and on-the-go authentication
- IP68-rated for dependable performance
- FIDO CTAP 2.1 for enhanced security features (e.g. resident credentials, Passkey support) and backwards compatibility with CTAP 2. FIDO2 L2 certified security for phishing resistant protection against identity theft and unauthorized access.
Are prompts or system instructions an authorization boundary?
No. Prompts can state intent and constraints, but they are untrusted data from a security perspective and can be overridden by prompt injection, retrieved text or a compromised model response. Authorization must use identity, policy, scoped credentials, allowlists and execution-time checks.
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →Treat instructions in retrieved pages, emails and tool output as content to analyze, not as permission grants. A model that says “the user approved this” cannot create an approval record. The application should obtain approval through a separate, authenticated workflow and attach its identifier, approver, scope and expiry to the action request.
What belongs in a guardrail and validation layer?
Guardrails should surround the model and tools, combining deterministic checks with a guardrail model where classification is useful. OWASP recommends heavier checks for tool invocations, external-content ingestion and sensitive outputs, while emphasizing that a guardrail model complements rather than replaces deterministic controls.
- Input checks: Detect disallowed intents, oversized or malformed content, and attempts to alter system policy.
- Retrieved-content checks: Mark untrusted instructions, scan for data exfiltration patterns and enforce content-type and provenance rules.
- Parameter validation: Use strict schemas, type checks, ranges, allowlisted domains and normalized identifiers before a tool call is formed.
- Output checks: Apply data-loss, policy, destination and format checks before returning or transmitting sensitive material.
- Decision recording: Log the rule or classifier, version, result, confidence where applicable and the action taken.
How should a tool broker authorize an action?
The broker or execution component is the final agent-side authorization point. It must independently evaluate the initiating identity and session, exact tool and parameters, target resource, privilege, approval state, timestamp and expiry immediately before execution.
- Bind identity: Resolve the caller from the authenticated session and preserve the shared correlation ID. Do not accept an actor name generated by the model.
- Re-evaluate policy: Ask a policy service whether this actor may invoke this tool for this tenant and purpose.
- Validate the exact target: Canonicalize account, file, repository, recipient, amount, environment or record identifiers; reject ambiguous, wildcard or out-of-scope targets.
- Validate parameters: Enforce a typed schema, safe ranges, destination allowlists and idempotency requirements.
- Check approval and freshness: Confirm that any required human approval covers the same action and target, has not been revoked and has not expired.
- Apply step-up controls: Require fresh authentication or human confirmation for sending, deleting, purchasing, deploying, changing permissions or other irreversible, financial, administrative or externally visible actions.
- Execute with least privilege: Use a short-lived credential limited to the approved operation and target.
- Record the outcome: Write an append-only decision and execution event, including denial reasons and downstream response.
OWASP states that the execution component must still check the actor’s authorization and any required approval for the exact action. Separate model planning from execution so a malformed or manipulated tool call cannot bypass these checks.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Rank #3
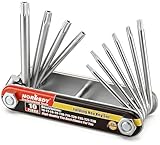
- Tamper Resistant Star Key Set Crafted with premium chrome vanadium steel, and each star tool folds neatly into the handle for quick, easy access.
- Details - The handle is engraved with size for quick identification with drilled tips to allow use.
- Portable - Keys fold compact for easy storage, Drilled tips allow use on tamper resistant security screws.
- Size:Full Size T-6, T-7, T-8, T-9, T-10, T-15 T-20, T-25, T-27 and T-30.
- And with 10 total star sizes able to match nearly all standard tamper resistant security screws on the market.
Why must the downstream system check authorization again?
The resource-owning service is the authoritative boundary and should re-check permissions using its native access-control model. Do not trust a decision or bearer token that passed only through the model layer.
Where access depends on the user’s scope, execute extensions with that user context and limit extension permissions. A database, mail service, cloud control plane or payment system should see an authenticated principal, audience, operation and target that it can validate itself. This second check catches stale policy, confused-deputy paths and misconfigured brokers.
How do you monitor an LLM pipeline without logging secrets?
Monitoring must be causal and correlated, not a collection of disconnected final-response logs. Use one shared correlation ID (and separate parent and child span IDs for fan-out) to connect the initiating identity, request, context, model, guardrails, tools, resources and effects.
| Event group | Capture | Privacy treatment |
|---|---|---|
| Identity and request | Stable actor ID, tenant, session, route, operation, timestamp and correlation ID | Prefer internal pseudonymous IDs; keep raw credentials out of logs |
| Context and retrieval | Source identifiers, authorization-filter result, provenance, retrieval count and policy version | Log hashes, labels or document IDs instead of full sensitive text |
| Model invocation | Provider, model and version, parameters, latency, token counts, status and retry data | Redact prompts and outputs by field; store restricted samples only when justified |
| Guardrails and policy | Rule or classifier version, decision, reason code, confidence and override status | Record categories and hashes rather than secrets or full payloads |
| Tool and downstream action | Tool name, normalized target, parameter hash, approval ID, credential scope, result and error | Mask account numbers, recipients, tokens and returned records |
| Resources and effects | Token and compute use, cost dimensions, dependencies, side effects and final status | Apply retention tiers and access controls to operational data |
Azure Monitor and Application Insights can centralize metrics, logs, traces, events and OpenTelemetry for agent runs, tool calls, token use, dependencies and behavior. AWS guidance recommends invocation logs in Amazon S3 or CloudWatch, granular IAM roles for model access, Bedrock Guardrails, and CloudWatch/CloudTrail auditing of foundation-model access. Across platforms, make audit records tamper-evident, restrict who can read them, define retention by data class and redact before storage—not after an incident.
What should an LLM audit log contain?
An audit record should let an investigator reconstruct who requested what, which data and policies shaped the decision, what the model proposed, what the system executed and what changed afterward.
Rank #4
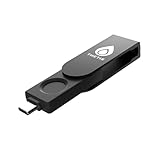
- FIDO2 Certified Passkey Authentication: Officially FIDO2 certified for secure, passwordless login on supported platforms. Use modern passkeys with hardware-backed protection. Please verify your intended service supports FIDO2 hardware keys before purchase.
- Precision Fingerprint Sensor: Built-in high-accuracy biometric fingerprint sensor ensures fast, convenient authentication while preventing unauthorized access. No PIN reuse, no shared secrets—only your fingerprint unlocks the key.
- Strong Hardware 2FA/MFA Security: Enhances account protection with physical-presence and biometric verification, helping defend against phishing, credential theft, and account takeovers.
- USB-C Wired Compatibility (No NFC): Designed for stable USB-C authentication on desktops and laptops, including Windows, macOS, and Linux systems. Ideal for users and enterprises that prefer wired-only security keys.
- Durable Aluminum Shield, Portable Design: Features the same precision aluminum protective shield for long-term durability. Compact, lightweight, battery-free, and network-free-built for everyday carry and professional environments.
- Immutable event ID, UTC timestamp, correlation and span IDs.
- Authenticated actor, tenant, session and workload identity.
- Application, environment, endpoint, model provider, model/version and configuration identifiers.
- Prompt, retrieval and output references represented by redacted fields, hashes or controlled-access payloads.
- Policy, guardrail and approval versions with allow/deny reason codes.
- Tool name, canonical target, parameter hash, credential audience, expiry and execution result.
- Token, latency, quota, retry and dependency measurements.
- Downstream resource ID, side-effect status and error classification.
- Retention class, redaction status and any human override identity.
Log denials and near misses as carefully as successes. Repeated bypass attempts, unusual tool fan-out, enumeration, extraction signals, sudden changes in guardrail decisions, failure spikes or abnormal resource use should create alerts and an investigation trail.
Which architecture is best for access control and monitoring?
No single placement wins every criterion. Compare designs by where enforcement occurs, what context is available, whether the exact action can be authorized, how well events correlate, the latency and cost added, failure behavior, privacy and retention burden, and how easily permissions can be revoked or reviewed.
| Design | Strength | Weakness if used alone | Best role |
|---|---|---|---|
| Prompt-only rules | Low latency and simple to change | No trustworthy identity, weak resistance to injection, cannot enforce resource permissions | Behavioral guidance, never authorization |
| Gateway-only control | Strong caller, tenant, quota and route visibility | Lacks final tool parameters and downstream resource context | Ingress authentication and coarse scope |
| Application policy layer | Understands task, data classification and business rules | May become stale before execution; cannot replace resource-owner checks | Retrieval and workflow authorization |
| Tool broker with execution checks | Can authorize exact action, target, approval and expiry | Adds latency and requires complete tool inventory and schemas | Final agent-side enforcement |
| Downstream native controls | Authoritative resource permission and revocation | May not understand model intent or prompt context | Defense in depth and final ownership boundary |
| Central observability plane | Cross-component correlation and response | Privacy, retention and tamper-resistance complexity | Audit, detection and investigation |
How do Azure and AWS map these controls to services?
Platform services can implement the layers, but configuration remains your responsibility. On Azure, combine API Management for ingress analytics, Azure RBAC and unique identities for access, short-lived scoped tokens, per-tool authorization, and Azure Monitor/Application Insights for traces and agent telemetry. Microsoft recommends fresh confirmation for irreversible actions.
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minutePC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11On AWS, use granular IAM roles for evaluation, general, fine-tuned and specialized model access; apply Amazon Bedrock Guardrails; store invocation logs in S3 or CloudWatch; and use CloudWatch and CloudTrail to audit foundation-model access. Keep the execution role narrower than the role that designs or evaluates prompts.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What should happen when a policy or logging service fails?
Failure behavior is part of the security design. For high-impact actions, fail closed when policy lookup, approval validation, identity resolution or required audit logging fails. Return a safe, non-executing error and preserve a minimal failure event if the primary log path is unavailable.
Best Value

- FIDO2 & Passkey Ready: Business-ready and FIDO2 L1 certified. This key is supported by major management suites and is ideal for both individual and enterprise deployment. Works seamlessly with Gmail, Facebook, GitHub, Dropbox, Coinbase, and more.
- Universal Connectivity (USB-A ): Features a built-in USB-A connector—simply unfold the key and plug it into your compatible PC or laptop for seamless authentication on the go.
- Dedicated Manager App: Use the Thetis Manager App for the initial hardware PIN setup. Setting the PIN on the device first ensures a smooth registration process. Once the PIN is configured, you can begin registering the key across your favorite FIDO2-compatible online services.
- Ultra-Durable & Portable: Featuring a rotating metal cover, this key is water, crush, and tamper-resistant. It fits easily on a keychain and requires no batteries or network connectivity.
- Check FIDO2 compatibility before purchase - Known limitations: ID Austria is not supported (requires FIDO2 Level 2). Windows Hello login only works with Windows Enterprise editions that support Entra ID, and NFC is NOT supported.
For low-risk, read-only responses, a documented degraded mode may return cached, non-sensitive information while marking the event as degraded. Never silently downgrade a delete, payment, deployment, permission change or external message to an unapproved execution path.
How can you implement layered controls step by step?
Build the controls in this order so each boundary has an owner and a testable contract.
Free tools Windows power users keep installed
One-click scans. No signup required.
- Inventory every model, retrieval source, connector, tool and downstream side effect.
- Define identities, tenants, data classifications, tool scopes, approval types and maximum token lifetimes.
- Configure gateway authentication, endpoint permissions, quotas, rate limits and correlation-ID propagation.
- Implement permission-aware retrieval and least-privilege credentials in the application policy layer.
- Define typed tool schemas, target canonicalization, allowlists, idempotency keys and parameter limits.
- Build an execution broker that re-checks actor, session, target, privilege, approval, timestamp and expiry.
- Require step-up authentication or fresh human approval for irreversible or high-impact operations.
- Enforce native authorization in each downstream resource using user or narrowly scoped workload context.
- Emit correlated, redacted, tamper-resistant events for prompts, retrieval, model versions, decisions, tools, outputs, resources and effects.
- Test denial, expiry, revocation, prompt injection, cross-tenant access, replay, malformed parameters, tool substitution and observability outages.
- Create alerts and runbooks for bypass attempts, unusual fan-out, enumeration, extraction, drift and cost or token anomalies.
What are the most common implementation mistakes?
- Trusting a system prompt: Move permission decisions into policy and execution services.
- Checking only at login: Re-authorize when the action and target are known, immediately before execution.
- Passing broad service credentials: Exchange them for short-lived, audience- and resource-scoped credentials.
- Logging complete prompts and tool payloads: Redact, hash or tokenize sensitive fields before they enter centralized logs.
- Ignoring retrieval permissions: Filter vector and connector results using the user’s current scope.
- Allowing wildcard targets: Require canonical identifiers and explicit allowlists.
- Failing open during outages: Block high-impact actions when policy, approval or mandatory audit paths are unavailable.
- Recording only final answers: Capture the causal chain so investigators can distinguish model suggestion from executed effect.
Frequently Asked Questions
Can an LLM decide whether a user is allowed to perform an action?
It can classify intent or propose a workflow, but it should not be the authority that grants permission. A deterministic policy or execution service must evaluate the authenticated identity, resource, scope and current approval state.
How long should tool-call authorization remain valid?
Keep authorization validity tied to the shortest practical action window, using an expiry and, for sensitive operations, a one-time approval or idempotency key. Revoke or invalidate it when the session, target or policy changes.
Should prompts and model outputs be stored for compliance?
Retention depends on sensitivity and legal obligations; full text is not automatically required. A defensible design stores redacted or hashed references by default and places any restricted payloads behind separate access controls, documented retention and deletion procedures.
How can I test that an agent cannot cross tenant boundaries?
Create automated tests that vary tenant IDs in prompts, retrieved documents, tool parameters and downstream identifiers, then assert denial at retrieval, broker and resource-owner layers. Include replayed approvals, expired tokens and substituted targets, and verify that each denial is correlated in the audit trail.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

