Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
The best VeloCloud Orchestrator alternative depends on what you are replacing: routing depth, branch security, cloud management, WAN optimization, deployment sovereignty, or a move to cloud-delivered SASE. Cisco Catalyst SD-WAN is the broadest fit for complex routing and multiregion networks; Cisco Meraki is usually easier for small operations teams; Fortinet Secure SD-WAN is strongest when firewall consolidation leads the project; and Prisma SD-WAN is compelling when App-ID, zero-trust network access and integrated security services are central. HPE Aruba EdgeConnect, Versa and Cato address different operating models rather than simply replicating VeloCloud.
Timing matters. Microsoft Azure documentation says VMware SD-WAN was rebranded to Arista VeloCloud, new deployments on the older VMware SD-WAN branding will be blocked in July 2026, and existing deployments continue to work. Treat this as a platform-ownership and support-policy decision, not just a feature comparison.
As an Amazon Associate I earn from qualifying purchases.
What is changing with VMware SD-WAN and VeloCloud?
VMware SD-WAN is now branded Arista VeloCloud. Microsoft Azure documentation records that new deployments using the older VMware SD-WAN identity will be blocked in July 2026, while existing deployments continue to work. The policy creates two separate decisions: whether your current environment can remain in service, and whether new sites, replacements or expansions should be built on the current VeloCloud offering or another platform.
Inventory the exact orchestrator, edge software, support contract and cloud marketplace listing you use. A deployment that still functions is not automatically a deployment that can be expanded under the same terms. Confirm the current name, support owner, deployment eligibility and migration path with the vendor and your cloud provider before ordering hardware or creating new instances.
#1 Best Overall

- 【Five Gigabit Ports】1 Gigabit WAN Port plus 2 Gigabit WAN/LAN Ports plus 2 Gigabit LAN Port. Up to 3 WAN ports optimize bandwidth usage through one device.
- 【One USB WAN Port】Mobile broadband via 4G/3G modem is supported for WAN backup by connecting to the USB port. For complete list of compatible 4G/3G modems, please visit TP-Link website.
- 【Abundant Security Features】Advanced firewall policies, DoS defense, IP/MAC/URL filtering, speed test and more security functions protect your network and data.
- 【Highly Secure VPN】Supports up to 20× LAN-to-LAN IPsec, 16× OpenVPN, 16× L2TP, and 16× PPTP VPN connections.
- Security - SPI Firewall, VPN Pass through, FTP/H.323/PPTP/SIP/IPsec ALG, DoS Defence, Ping of Death and Local Management. Standards and Protocols IEEE 802.3, 802.3u, 802.3ab, IEEE 802.3x, IEEE 802.1q
Do not assume an SD-WAN replacement is a complete SASE migration. SD-WAN primarily steers traffic across underlay links and applies network policy. SASE normally adds cloud-delivered security services such as secure web access, zero-trust access and security inspection. Some alternatives combine those functions; others require separate security products.
How should you compare VeloCloud alternatives?
Start with the operating problem, not a feature-count contest. Record your geography, number of branches, bandwidth per site, circuit mix, legacy-routing requirements, security ownership, cloud and SaaS traffic, preferred deployment model and tolerance for vendor lock-in. The same product can be an excellent fit for a 20-site retail network and a poor fit for a regulated multinational with private-cloud requirements.
- Routing and brownfield support: document the protocols, route scale, segmentation model and existing WAN services that must survive cutover.
- Path control: test application-aware steering under packet loss, latency and jitter, including brownouts where a circuit remains up but performs badly.
- Security: decide whether branch firewalls, intrusion prevention, SSL inspection, URL filtering and application control stay with a security team or move into the SD-WAN appliance.
- Identity and access: evaluate zero-trust network access, identity integration and user-level policy if remote users and private applications are part of the project.
- Segmentation: verify isolation for guests, point-of-sale systems, operational technology, voice and corporate traffic.
- Cloud and SaaS connectivity: map connections to public clouds, data centers, internet exchanges and major SaaS services.
- Operations: compare zero-touch provisioning, templates, APIs, observability, anomaly detection, change control and rollback.
- Transport choices: check broadband, MPLS, leased lines and cellular options, including failover behavior and licensing for backup links.
- Commercial model: understand whether you buy appliances, edge subscriptions, security seats, bandwidth tiers, optional optimization or managed services.
Cisco’s comparison guidance summarizes the core test: performance, reliability, security, speed, bandwidth, scalability and simplicity all matter. A lab that measures only throughput can miss policy errors, failover delays or security inspection overhead.
Which platforms are the main VeloCloud alternatives?
The following shortlist reflects the distinct strengths described in current Cisco and CIOPages comparison material. It is a starting point for architecture workshops, not an apples-to-apples performance ranking.
| Platform | Operating model indicated | Capabilities highlighted | Best initial fit |
|---|---|---|---|
| Cisco Catalyst SD-WAN | Broad routing and SD-WAN platform | Traditional routing, multiregion fabric, cellular, anomaly detection, segmentation, multicloud connectivity, application-aware optimization and centralized security policy | Large or complex networks needing routing depth and Cisco integration |
| Cisco Meraki SD-WAN | Guided, cloud-managed provisioning | Cloud management and application visibility | Small operations teams prioritizing simple deployment |
| Fortinet Secure SD-WAN | Security-led appliance and subscription model | FortiGate next-generation firewall functions, IPS/IDS, SSL inspection, application control, URL filtering and FortiManager/FortiAnalyzer integration | Branches where firewall consolidation is the main goal |
| HPE Aruba EdgeConnect | Per-edge subscription | Application visibility and path control, with WAN-optimization Boost as an add-on | Organizations invested in HPE Aruba operations or WAN optimization |
| Palo Alto Networks Prisma SD-WAN | ION edge subscriptions with Prisma security services | App-ID classification, path measurement, ZTNA and Prisma security integration | Security teams standardizing on application identity and zero trust |
| Versa Networks | On-premises, cloud, private or sovereign deployment | Flexible deployment and per-site, per-user or capacity pricing options | Service providers or enterprises requiring deployment sovereignty |
| Cato Networks | Cloud-native SASE backbone | Subscription combining site sockets and per-user security services | Teams preferring a provider backbone over customer-managed edge infrastructure |
Is Cisco Catalyst SD-WAN the broadest replacement?
Choose Catalyst when traditional routing, segmentation, multiregion scale and Cisco integration outweigh the appeal of a simpler interface. Cisco positions Catalyst as a combined routing and SD-WAN platform rather than a narrow overlay controller.
The comparison material highlights support for traditional routing, a multiregion fabric, cellular connectivity, anomaly detection, segmentation, multicloud connectivity, application-aware optimization and centralized security policy. That breadth is useful when branches include legacy route design, multiple clouds and several transport types. It also means the design team must define routing ownership, segmentation boundaries and security-policy precedence before rollout.
Recommended Free Tools
Validate how Catalyst handles your existing route redistribution, default-route strategy, regional hubs and cellular backup. Test whether anomaly information reaches the operations workflow you already use, and check which functions require additional Cisco components or subscriptions. Catalyst is a strong candidate for a brownfield network, but its breadth can be unnecessary for a small team that wants guided provisioning with minimal policy design.
Rank #2

- 【Flexible Port Configuration】1 2.5Gigabit WAN Port + 1 2.5Gigabit WAN/LAN Ports + 4 Gigabit WAN/LAN Port + 1 Gigabit SFP WAN/LAN Port + 1 USB 2.0 Port (Supports USB storage and LTE backup with LTE dongle) provide high-bandwidth aggregation connectivity.
- 【High-Performace Network Capacity】Maximum number of concurrent sessions – 500,000. Maximum number of clients – 1000+.
- 【Cloud Access】Remote Cloud access and Omada app brings centralized cloud management of the whole network from different sites—all controlled from a single interface anywhere, anytime.
- 【Highly Secure VPN】Supports up to 100× LAN-to-LAN IPsec, 66× OpenVPN, 60× L2TP, and 60× PPTP VPN connections.
- 【5 Years Warranty】Backed by our 5-years warranty and free technical support from 6am to 6pm PST Monday to Fridays
Is Cisco Meraki SD-WAN easier to manage?
Meraki is the better first candidate when a small operations team values guided, cloud-managed provisioning and clear application visibility over deep traditional-routing customization.
Cisco’s comparison distinguishes Meraki from Catalyst by emphasizing cloud-managed workflows and guided provisioning. That approach can reduce the number of local decisions required to bring up a branch, especially when sites follow a repeatable template. Application visibility helps operators confirm what is using the WAN before tuning path policy.
Ask for a proof of concept that includes your hardest routing exception, not only a standard branch. Confirm how templates represent segmentation, how administrators stage and roll back changes, and how the platform behaves when cloud management is temporarily unreachable. Meraki’s simplicity is an operational advantage only if the guided model can express the exceptions your network actually needs.
Free tools Windows power users keep installed
One-click scans. No signup required.
When does Fortinet Secure SD-WAN make more sense?
Fortinet is a leading option when branch security and firewall consolidation are the primary buying drivers. The SD-WAN decision is then tied to the FortiGate appliance and FortiGuard subscription economics, rather than evaluated as an overlay in isolation.
The cited comparison lists FortiGate next-generation firewall functions including intrusion prevention and detection, SSL inspection, application control and URL filtering. FortiManager and FortiAnalyzer integration adds centralized management and analysis. This can reduce the number of separate branch appliances and policy consoles, provided the security team is prepared to own the resulting rule set.
Model inspection capacity with realistic encrypted traffic, not just raw WAN bandwidth. Establish who approves URL, application and IPS policies, how exceptions are audited, and what happens when a security subscription expires. Fortinet is especially compelling for organizations replacing branch firewalls at the same time as the SD-WAN overlay; it is less decisive if your security stack is already standardized elsewhere and must remain separate.
Should WAN optimization point you to HPE Aruba EdgeConnect?
EdgeConnect deserves priority when WAN optimization, application visibility and path-control behavior are central, particularly in an organization already operating HPE Aruba infrastructure.
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallRank #3

- 【Flexible Port Configuration】1 Gigabit SFP WAN Port + 1 Gigabit WAN Port + 2 Gigabit WAN/LAN Ports plus1 Gigabit LAN Port. Up to four WAN ports optimize bandwidth usage through one device.
- 【Increased Network Capacity】Maximum number of associated client devices – 150,000. Maximum number of clients – Up to 700.
- 【Integrated into Omada SDN】Omada’s Software Defined Networking (SDN) platform integrates network devices including gateways, access points & switches with multiple control options offered – Omada Hardware controller, Omada Software Controller or Omada cloud-based controller(Contact TP-Link for Cloud-Based Controller Plan Details). Standalone mode also applies.
- 【Cloud Access】Remote Cloud access and Omada app brings centralized cloud management of the whole network from different sites—all controlled from a single interface anywhere, anytime.
- 【SDN Compatibility】For SDN usage, make sure your devices/controllers are either equipped with or can be upgraded to SDN version. SDN controllers work only with SDN Gateways, Access Points & Switches. Non-SDN controllers work only with non-SDN APs. For devices that are compatible with SDN firmware, please visit TP-Link website.
CIOPages describes EdgeConnect as a per-edge subscription and identifies WAN-optimization Boost as an add-on. Cisco’s comparison highlights application visibility and path-control capabilities. The add-on structure means you should separate the base SD-WAN requirement from the applications that truly need optimization, such as traffic crossing high-latency or constrained links.
Measure improvement with your own protocols and branch-to-cloud paths. Test whether optimization changes failover behavior, troubleshooting visibility or encryption design. Include the Boost add-on in the three-year model for only the sites and applications that need it; applying it universally can obscure the economic case.
When is Prisma SD-WAN the right security-led alternative?
Prisma SD-WAN is a strong fit when application identity, zero-trust access and integration with a broader Prisma security architecture are more important than simply reproducing an existing overlay.
The comparison material identifies App-ID application classification, path measurement, ZTNA and Prisma security integration. App-ID can make policy more explicit than port-based rules, while path measurement supplies the inputs for steering decisions. ZTNA and Prisma integration matter when private-application access and branch connectivity are being designed as one security program.
Budget for the ION edge subscription as well as Prisma Access and ADEM cost drivers described by CIOPages. Clarify which traffic is inspected at the branch, which is sent to cloud security points of presence, and how user identity is carried into policy. A pilot should include SaaS, private applications, encrypted traffic and an identity-provider outage so that the security architecture is tested along with path control.
Why choose Versa Networks?
Versa is most relevant when deployment control and sovereignty are requirements rather than preferences. CIOPages describes support for on-premises, cloud, private or sovereign deployment, with pricing that can be based on sites, users or capacity.
This flexibility can suit service providers, government environments and enterprises that cannot place all control in a public cloud service. It can also create more design and operational responsibility. Decide who supplies the infrastructure, who patches the control plane, where telemetry is stored and which party supports the underlay.
Rank #4
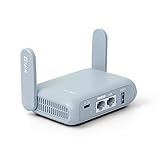
- 【DUAL BAND AX TRAVEL ROUTER】Products with US, UK, EU Plug; Dual band network with wireless speed 574Mbps (2.4G)+2402Mbps (5G); 2.5G Multi-gigabit WAN port and a 1G gigabit LAN port; USB 3.0 port; Wi-Fi 6 offers more than double the total Wi-Fi speed with the MT3000 VPN Router.
- 【VPN CLIENT & SERVER】OpenVPN and WireGuard are pre-installed, compatible with 30+ VPN service providers (active subscription required). Simply log in to your existing VPN account with our portable wifi device, and Beryl AX automatically encrypts all network traffic within the connected network. Max. VPN speed of 150 Mbps (OpenVPN); 300 Mbps (WireGuard). *Speed tests are conducted on a local network. Real-world speeds may differ depending on your network configuration.*
- 【OpenWrt 21.02 FIRMWARE】The Beryl AX is a portable wifi box and mini router that runs on OpenWrt 21.02 firmware. It supports more than 5,000 ready-made plug-ins for customization. Simply browse, install, and manage packages with our no-code interface within Beryl AX's Admin Panel.
- 【PROTECT YOUR NETWORK SECURITY】Our pocket wifi, unlike other vulnerable portable wifi hotspot for travel purposes supports WPA3 protocol–Preventive measures against password brute-force attacks; DNS over HTTPS & DNS over TLS–Protecting domain name system traffic and preventing data eavesdropping from malicious parties; IPv6–Built-in authentication for privacy protection, eliminating the need for network address translation.
- 【VPN CASCADING AT EASE】Surpassing the mediocre performance of most VPN routers for home usage, the Beryl AX is capable of hosting a VPN server and VPN client at the same time within the same device, enabling users to remote access local network resources like Wi-Fi printers or local web servers, and accessing the public internet as a VPN client simultaneously.
Request a complete bill of materials for your chosen deployment mode. A private or sovereign design may change hardware, staffing, support and lifecycle costs even when the software feature list looks similar to a hosted option. Versa should be evaluated as a platform and operating model together.
Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Repair Windows errors before they cause bigger problems3Scan for outdated or missing drivers - takes under a minuteWhen is Cato a better architectural change than a direct replacement?
Cato is an alternative for organizations that would rather consume a cloud-native SASE backbone than deploy and operate many customer-managed edge devices.
CIOPages describes a subscription combining site sockets and per-user security services. That model can simplify branch connectivity and shift backbone operations to the provider. It also changes the dependency profile: internet access, provider points of presence, identity integration and exit planning become central design concerns.
Use Cato as a separate architecture track in the evaluation. Compare the cost and operational effort of provider connectivity with your current circuits, edge hardware, security appliances and support teams. Verify regional coverage, application paths, data-residency requirements and the process for exporting policy and traffic data if you later change providers.
How do pricing and three-year costs differ?
Public list prices are uncommon for these platforms, so a credible comparison requires a workload-based model rather than a price-per-site guess. CIOPages identifies the main cost drivers as edge count and throughput, subscription tier, security or SSE seats, optional WAN optimization, support, professional services and whether the platform is managed, self-hosted, cloud-delivered or sovereign.
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →| Cost category | What to measure | Why it changes the decision |
|---|---|---|
| Edge infrastructure | Appliance count, models, spares and refresh timing | Hardware-heavy designs have different capital and replacement profiles from cloud-delivered services |
| Subscriptions | Edge tier, throughput, site sockets, users and security services | Per-site, per-user and capacity pricing scale differently as branches and employees grow |
| WAN optimization | Sites and applications requiring an optimization add-on | Applying an optional feature everywhere can inflate recurring cost without improving every path |
| Underlay and overlap | Broadband, MPLS, cellular and months of parallel service | Migration often requires overlapping circuits before the old WAN can be retired |
| Implementation | Professional services, testing, training and internal engineering hours | A simpler control plane may reduce labor; a sovereign or highly customized design may increase it |
| Risk and resilience | Avoided outage costs, spare capacity and recovery requirements | The lowest subscription price is not the lowest business cost if failover is inadequate |
Build a 36-month view that includes hardware, subscriptions, underlay circuits, MPLS overlap during migration, professional services, internal labor and avoided outage costs. Show one-time and recurring amounts separately, and model growth in sites, bandwidth, users and security seats. Require each bidder to identify which capabilities are included, which require an add-on and which are delivered by a separate service.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.How do you select a platform for common scenarios?
Use the following as a starting decision tree, then validate the choice with a pilot that represents your most difficult site.
Best Value

- License‑Free Cloud Management Access and manage the network remotely through the Omada Cloud portal. With the built‑in controller, all features — including advanced capabilities — are fully available from day one.
- Simplified Setup for Faster Deployment Easily set up the Fusion Gateway via Bluetooth using the Omada App. Automatically discover and batch adopt all other Omada networking devices at once, saving time and simplifying IT deployment."
- High-Performance Quad-Core CPU Ensures lightning-fast processing to overpower lag. "
- Five 2.5G Ports Delivers outstanding speed and rock-solid connectivity with up to 4-WAN load balancing and auto multi-WAN failover."
- Touchscreen-Based Quick On-Site Troubleshooting The 2.51"" touchscreen provides instant on‑site insights — including health scores, speed tests, alerts, and real‑time traffic — enabling quick troubleshooting without a laptop. Reduce on‑site work and save time with direct, on‑device monitoring"
- Traditional routing and scale dominate: start with Cisco Catalyst SD-WAN and compare its routing, segmentation and multiregion behavior against your current design.
- A small team needs guided cloud management: evaluate Cisco Meraki, while testing the routing exceptions and rollback controls that a simple branch template may not cover.
- Firewall consolidation is the business case: evaluate Fortinet Secure SD-WAN with realistic IPS, SSL inspection, application-control and URL-filtering loads.
- WAN optimization is a specific requirement: evaluate HPE Aruba EdgeConnect and price the Boost add-on only for qualifying applications and sites.
- Application identity and zero trust lead: evaluate Prisma SD-WAN with App-ID, ZTNA, Prisma Access and ADEM requirements mapped end to end.
- Private, cloud or sovereign deployment is mandatory: evaluate Versa and document who operates every control-plane and data-plane component.
- You prefer a provider-operated backbone: evaluate Cato as a SASE architecture, not merely as another edge appliance.
How should a migration from VeloCloud be staged?
A staged migration limits the risk created by routing changes, security policy conversion and circuit overlap. Keep the existing environment available until the replacement has passed application, failover and rollback tests.
- Freeze the baseline: export inventories, topology, route tables, segmentation, QoS classes, business-critical applications, security rules and current circuit performance.
- Classify dependencies: separate internet, MPLS, cellular, cloud, data-center and SaaS paths, and record which teams own each policy.
- Choose a representative pilot: include a standard branch, a high-bandwidth site, a site with legacy routing and a site with cellular or difficult underlay conditions.
- Build policy translations: map application steering, business priorities, security inspection, NAT, segmentation and management roles before touching production.
- Test adverse conditions: inject loss, latency and jitter; disconnect each circuit; test brownouts; verify convergence, voice and video quality, SaaS sessions and security logging.
- Run in parallel: retain the old overlay and circuits for the agreed rollback window. Track MPLS overlap and temporary licensing as explicit costs.
- Migrate in waves: schedule sites by risk, not geography alone, and keep a documented backout procedure for each wave.
- Decommission deliberately: remove old circuits, licenses and hardware only after monitoring confirms stable traffic, complete logs and accepted support handoff.
What should a proof of concept measure?
A useful proof of concept measures the traffic and failure modes that drive your purchase. Record baseline and replacement results under the same circuits, applications and security settings.
- Application response and packet loss while steering between links with different latency and jitter.
- Time to detect a failed link, select a new path and restore sessions where the application permits it.
- Throughput and latency with firewall, IPS/IDS, SSL inspection or URL filtering enabled.
- Route convergence, segmentation enforcement and reachability for legacy networks.
- Cloud and SaaS path quality, including regional variations and private-application access.
- Zero-touch deployment time, template reuse, API behavior and administrator rollback.
- Observability: whether operators can explain a path decision, identify an anomaly and export evidence for an incident.
- Operational workload: number of consoles, approvals, policy translations and recurring tasks required per site.
There is no authoritative independent benchmark covering all of these alternatives under identical conditions, so treat vendor demonstrations as hypotheses. Your own traffic, security policy and underlay determine the result.
What are the most common selection mistakes?
- Choosing by brand familiarity alone: an existing firewall or routing relationship may not satisfy cloud, identity or sovereignty requirements.
- Comparing appliance throughput without inspection: encrypted traffic and security services can change usable capacity.
- Ignoring brownouts: a link that is technically up can still damage voice, video and transactional applications.
- Underestimating policy conversion: application names, route priorities, NAT and segmentation rarely map one-for-one between orchestrators.
- Mixing SD-WAN and SASE requirements: a platform can steer paths well while requiring a separate SSE or firewall service.
- Leaving the operating model undefined: managed, self-hosted, cloud-delivered and sovereign designs assign patching, monitoring and incident duties differently.
- Omitting exit planning: document configuration export, circuit ownership, identity dependencies and data-retention requirements before signing a long subscription.
What is the practical shortlist?
For complex routing and multiregion Cisco environments, begin with Catalyst. For guided cloud operations, begin with Meraki. For branch firewall consolidation, begin with Fortinet. For WAN optimization and HPE Aruba alignment, test EdgeConnect. For App-ID, ZTNA and Prisma security integration, test Prisma SD-WAN. For private, cloud or sovereign control, test Versa. For a provider-operated SASE backbone, evaluate Cato as a different architecture.
Do not name a final winner until the supplier has demonstrated your route exceptions, security inspection load, circuit failures, cloud and SaaS paths, administrative workflow and three-year cost model. The July 2026 policy change makes that validation and timing exercise especially important for any organization still expanding a VMware-branded deployment.
Frequently Asked Questions
Can an existing VMware SD-WAN deployment keep running after July 2026?
Microsoft Azure documentation says existing deployments continue to work even though new deployments on the older VMware SD-WAN branding will be blocked in July 2026. Confirm the exact eligibility and support terms for your tenant, edge software and marketplace channel before planning an expansion.
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Is replacing SD-WAN the same as adopting SASE?
No. SD-WAN handles overlay connectivity and path policy, while SASE commonly adds cloud-delivered security and identity controls. A replacement project should document which SSE, firewall and zero-trust functions are included and which remain separate.
How many sites should be included in an SD-WAN pilot?
Use several site types rather than a single average branch: a standard location, a high-bandwidth site, a legacy-routing site and one with cellular or difficult underlay conditions. This exposes policy and failover problems that a uniform pilot can miss.
What information should I request in an SD-WAN quote?
Request itemized edge hardware, throughput tiers, site or user subscriptions, security services, optional optimization, support, implementation and training. Also ask the supplier to identify recurring charges during circuit overlap and the assumptions behind any managed, private-cloud or sovereign deployment.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.

