What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
Strengthening Active Directory security requires evidence before enforcement. Build an inventory of NTLM use, enable targeted Advanced Audit Policy logging, review the enhanced NTLM Operational channel, fix legacy dependencies, and only then apply restrictions to a pilot group before expanding them. This sequence exposes who is authenticating, which systems are involved, and why NTLM was selected without causing an avoidable outage.
The most useful baseline combines successful and failed logon events, explicit-credential events, policy-change and directory-service auditing, and NTLM-specific telemetry. It also treats domain controllers, member servers, workstations, trusts, service accounts, and privileged administration as separate risk areas. Continuous central collection and alerting are needed after the initial migration because new applications and devices can reintroduce weak authentication.
As an Amazon Associate I earn from qualifying purchases.
What does strengthening Active Directory with NTLM controls involve?
A defensible program has four phases: discover, audit, remediate, and enforce. Discovery maps domain controllers, member servers, workstations, trusts, business-critical applications, appliances, and service accounts. Auditing then records normal and abnormal authentication so you can identify NTLMv1, unexpected source hosts, and repeated failures. Remediation moves compatible workloads to Kerberos or modern application authentication and replaces clients that cannot meet current requirements. Enforcement blocks defined legacy paths in stages, with an owner and rollback plan for every exception.
Do not treat “disable NTLM” as a single switch. Authentication can occur between users and domain controllers, between services, or directly between workstations. A restriction that is safe for one organizational unit may break an old scanner, scheduled task, file transfer, or appliance elsewhere.
#1 Best Overall

- Ultra-Compact FIDO2 Security Key - Plug-and-stay or carry on a keychain. This USB-A hardware security key offers portable, always-on protection for desktop and mobile use. (Item Size: 0.75 X 0.74 IN x 0.25 IN)
- USB-A Hardware Key for All Devices - Works with USB-A ports on PC, Mac, Android, and other laptop/notebook device. Enables secure, cross-platform login with FIDO2.0 passkey support.
- FIDO Certified Security Key - Meets FIDO and FIDO2 standards. Works with Google, Microsoft, GitHub, Dropbox, and more. Please check service compatibility before purchase.
- Passwordless Login with Passkey - Supports passkey login via WebAuthn and CTAP2. Enjoy password-free sign-ins where supported. Not all websites or services currently support passkeys.
- Advanced Multi-Factor Authentication - Offers 200 FIDO2 passkey slots and 50 OATH-TOTP slots. Strong, flexible 2FA/MFA support across various apps and authentication platforms.
How should I inventory Active Directory before changing NTLM settings?
Start with a role-based map rather than one undifferentiated domain list. Record the operating-system version, application owner, authentication protocol, source and destination, account type, and business impact for each dependency.
Separate the systems that create different evidence
- Domain controllers: capture authentication decisions, account activity, policy changes, and directory-object access.
- Member servers: identify services accepting network logons, scheduled tasks, file shares, and local applications that may fall back to NTLM.
- Workstations: look for workstation-to-workstation authentication, mapped drives, scripts, and unmanaged software that uses stored credentials.
- Trusts and external connections: document forest, domain, and application trusts, including which side owns the account and which side receives the logon.
Capture ownership and business context
For each NTLM observation, record the user or service account, source host, destination host, process or service when available, reason selected by Windows, first and last occurrence, and application owner. Mark privileged accounts, non-expiring passwords, interactive use by service identities, and systems that cannot be patched. An exception without an owner and an expiration date becomes a permanent bypass.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →How do I enable the right Windows audit policies?
Use Advanced Audit Policy through Group Policy for managed fleets, or auditpol.exe for a controlled local or scripted test. Apply settings to a pilot organizational unit first, confirm that the resulting policy is actually applied, and verify event arrival on the intended computers.
- In Group Policy Management, create or select a policy linked to the pilot OU.
- Open
Computer Configuration > Policies > Windows Settings > Security Settings > Advanced Audit Policy Configuration > System Audit Policies. - Enable the logon, account-management, policy-change, and selected directory-service subcategories. Where the Microsoft baseline calls for both, enable success and failure auditing.
- Update a pilot computer with
gpupdate /force, then check the effective settings withauditpol /get /category:*. - For a narrowly scoped test, use a command such as
auditpol /set /subcategory:"Logon" /success:enable /failure:enable; keep scripted changes documented so Group Policy does not silently overwrite them. - Generate known test activity, confirm the expected records, and measure event volume before linking the policy more broadly.
Microsoft cautions that production audit policies should be reviewed, tested, and validated against security and operational requirements before deployment. Object-access and process-tracking categories can create substantial noise, so enable them only for a defined investigative purpose and turn them down when that purpose ends.
Which Windows events reveal suspicious Active Directory logons?
Use successful events to establish normal behavior and failures or credential-use events to find deviations. Correlation is more valuable than any single record: connect the account, source address, destination computer, logon type, process, and time window.
Rank #2

- USB-C or tap via NFC for easy authentication on any compatible device. No drivers needed; optional Kensington software available for advanced management features.
- Works across Windows, macOS, iOS, Android, ChromeOS, and supports Passkeys and Apple ID.
- Slim, keychain-ready form for easy carry and on-the-go authentication
- IP68-rated for dependable performance
- FIDO CTAP 2.1 for enhanced security features (e.g. resident credentials, Passkey support) and backwards compatibility with CTAP 2. FIDO2 L2 certified security for phishing resistant protection against identity theft and unauthorized access.
| Event or channel | What it contributes | Practical use |
|---|---|---|
| 4624 | Successful logon | Build a baseline of normal users, service accounts, source hosts, logon types, and destinations. |
| 4625 | Failed logon | Investigate bursts, a new source, a changed service account, or failures that begin immediately after a restriction. |
| 4648 | Logon attempt using explicit credentials | Examine runas, scheduled tasks, scripts, and tools that supply a username and password directly. |
| 4675 | Filtered SIDs during logon | Review token construction and constrained or filtered administrative access in the surrounding session. |
| Microsoft-Windows-NTLM/Operational | Enhanced NTLM records on supported releases | Answer who used NTLM, why it was selected, and where the authentication occurred; correlate account, process, source, and destination fields. |
| 4024 | NTLMv1-derived credential use identified during the transition | Find clients or services still relying on NTLMv1 as the new enforcement behavior is introduced. |
Event 4625 is not automatically an attack: a mistyped password, expired task credential, or disconnected drive can produce it. Suspicion rises when failures are repeated, distributed across many accounts, tied to a new source host, or followed by a successful logon from the same origin.
What is enhanced NTLM auditing and which Windows versions support it?
Enhanced NTLM auditing adds context that ordinary logon records often lack. On Windows 11 version 24H2 and later, and Windows Server 2019, 2022, and 2025, the NTLM Operational channel can identify the account, the reason NTLM was chosen, and the locations involved. Use that channel to find dependencies before changing a blocking policy.
Collect the channel from domain controllers and selected clients, not just from one central server. A domain controller may show the receiving side of an authentication while the client log contains the process that initiated it. Correlating both sides helps distinguish a user action from a service, script, or embedded appliance.
Fields worth preserving
- Account name, domain, and whether the identity is privileged or a service account.
- Source and destination computer names and addresses.
- Process, service, or application details supplied by the event.
- The stated reason for NTLM selection, including compatibility or protocol negotiation clues.
- Timestamp, logon type, and related 4624, 4625, or 4648 records.
How do I investigate suspicious NTLM and logon patterns?
Prioritize observations that combine weak protocol use with unusual identity or location. A repeatable investigation prevents analysts from disabling a legitimate service based on one noisy event.
Start with high-risk combinations
- NTLMv1 use, especially from a device that otherwise supports modern authentication.
- A privileged account authenticating from a workstation, server, or geographic source it has never used.
- Workstation-to-workstation NTLM where a server-mediated Kerberos path should exist.
- Repeated 4625 failures for a service account, followed by a successful 4624 from a different host.
- 4648 events from scripts or scheduled tasks that are not documented for the account.
- Authentication beginning immediately after a policy change, software deployment, or password rotation.
Correlate before escalating
Group events by account and source, then compare the destination and process. Check whether the source computer was recently reimaged, whether a task runs under saved credentials, and whether DNS or time synchronization problems forced a protocol fallback. Confirm the owner of the application before changing its account or authentication method, and preserve the relevant records for incident response if the activity cannot be explained.
Rank #3
- Tamper Resistant Star Key Set Crafted with premium chrome vanadium steel, and each star tool folds neatly into the handle for quick, easy access.
- Details - The handle is engraved with size for quick identification with drilled tips to allow use.
- Portable - Keys fold compact for easy storage, Drilled tips allow use on tamper resistant security screws.
- Size:Full Size T-6, T-7, T-8, T-9, T-10, T-15 T-20, T-25, T-27 and T-30.
- And with 10 total star sizes able to match nearly all standard tamper resistant security screws on the market.
How can I block NTLMv1 without breaking legacy applications?
Use an audit-to-enforce transition. First identify every NTLMv1-dependent client or service, then update the software, change its authentication configuration, or replace the device. Test the replacement in a production-like environment before applying a restriction to business systems.
Stage the change
- Observe: collect NTLM Operational records and 4024-related evidence while the current behavior remains allowed.
- Classify: separate confirmed NTLMv1 use from NTLM versions that are not yet proven to be v1, and rank dependencies by business criticality.
- Remediate: prefer Kerberos for domain-integrated services and modern application authentication where available. Update legacy clients, firmware, drivers, and appliances; do not merely rename an exception.
- Pilot: apply the restriction to a dedicated OU or controlled server group. Watch 4625 failures, service health, task history, and application logs.
- Expand: move one business group or server tier at a time after the pilot remains stable through normal operating cycles.
- Enforce: document the final setting, affected systems, test evidence, owner, and rollback procedure.
Microsoft’s stated transition changes the default for an unset BlockNtlmv1SSO value to Enforce mode after the October 13, 2026 Windows security update. That behavior blocks NTLMv1-derived Single Sign-On credentials, so systems that have not been inventoried can fail when the update is installed. Treat the update date as a change-management milestone, not as a reason to skip testing.
Which NTLM-control approach fits my environment?
There is no universal best setting. Compare approaches by visibility, enforcement, compatibility, event volume, correlation quality, rollback, and who will investigate alerts.
| Approach | Visibility | Enforcement | Compatibility impact | When it fits |
|---|---|---|---|---|
| Baseline auditing only | Good for logon and policy activity; limited NTLM-specific context if enhanced logging is unavailable | None | Low | Initial discovery or environments with unknown dependencies |
| Enhanced NTLM auditing | Client, server, and domain-controller context when supported | None | Low, but storage and triage needs rise | Building an evidence-backed migration list |
| Pilot restriction | High for affected systems because failures are observable in a bounded group | Targeted block | Manageable if owners test first | Validating fixes before broad deployment |
| Domain-wide enforcement | Depends on central collection and alerting | Strongest | Highest for undocumented legacy clients | Only after pilots, remediation, and rollback checks succeed |
Event storage and alert-triage capacity are part of the decision. A policy that produces more records than the security team can retain, search, and investigate does not create useful control. Keep high-volume categories scoped to a question you are actively answering.
Recommended Free Tools
What should I monitor after restrictions are enabled?
Continuous monitoring detects both attacks and operational regressions. Send Windows Security and NTLM Operational events to a protected central system, restrict access to the logs, and alert on patterns rather than isolated records.
Rank #4
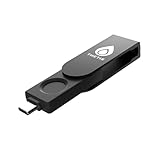
- FIDO2 Certified Passkey Authentication: Officially FIDO2 certified for secure, passwordless login on supported platforms. Use modern passkeys with hardware-backed protection. Please verify your intended service supports FIDO2 hardware keys before purchase.
- Precision Fingerprint Sensor: Built-in high-accuracy biometric fingerprint sensor ensures fast, convenient authentication while preventing unauthorized access. No PIN reuse, no shared secrets—only your fingerprint unlocks the key.
- Strong Hardware 2FA/MFA Security: Enhances account protection with physical-presence and biometric verification, helping defend against phishing, credential theft, and account takeovers.
- USB-C Wired Compatibility (No NFC): Designed for stable USB-C authentication on desktops and laptops, including Windows, macOS, and Linux systems. Ideal for users and enterprises that prefer wired-only security keys.
- Durable Aluminum Shield, Portable Design: Features the same precision aluminum protective shield for long-term durability. Compact, lightweight, battery-free, and network-free-built for everyday carry and professional environments.
- New source hosts or unusual geography for privileged accounts.
- Authentication from a workstation where the identity normally uses a secured administrative host.
- Sudden increases in 4625 failures after a policy, patch, password, or network change.
- 4624 successes that follow a series of failures or originate from a never-seen device.
- 4648 use by scripts, scheduled tasks, or processes outside their documented maintenance window.
- Changes to audit policy, authentication policy, group membership, or sensitive directory objects.
- New or modified service accounts, non-expiring passwords, and unexpected delegation settings.
Pair protocol controls with least privilege, temporary privileged access, monitored changes to sensitive directory objects, and hardened administrative hosts. NTLM restrictions reduce one attack surface but cannot compensate for excessive permissions or unmonitored directory changes.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What are the common failure modes and recovery steps?
A legacy application stops authenticating
Use the failure timestamp to find the destination, source, account, and process in 4625 and NTLM records. Restore only the smallest pilot scope if business continuity requires it, assign an owner, and set a short expiration while the application is upgraded or replaced.
Auditing creates too much noise
Remove broad object-access or process-tracking settings that are not tied to an investigation. Filter collection by computer group, account, event, or time window, and retain a documented reason for every high-volume subcategory.
Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Repair Windows errors before they cause bigger problems3Fix the driver behind crashes, sound loss and screen glitchesExpected events do not appear
Check the effective policy with auditpol /get /category:*, confirm that the policy is linked to the computer’s OU, verify that another policy is not overriding it, and inspect the correct Security or NTLM Operational channel. Also confirm that the operating system supports the enhanced channel and that the log has not overwritten records due to insufficient size.
Service-account failures are intermittent
Compare task schedules, password-rotation times, DNS resolution, clock synchronization, and the account’s allowed logon locations. A restriction may expose a latent configuration problem rather than create a new one; fix the dependency instead of granting a permanent broad exception.
Best Value

- FIDO2 & Passkey Ready: Business-ready and FIDO2 L1 certified. This key is supported by major management suites and is ideal for both individual and enterprise deployment. Works seamlessly with Gmail, Facebook, GitHub, Dropbox, Coinbase, and more.
- Universal Connectivity (USB-A ): Features a built-in USB-A connector—simply unfold the key and plug it into your compatible PC or laptop for seamless authentication on the go.
- Dedicated Manager App: Use the Thetis Manager App for the initial hardware PIN setup. Setting the PIN on the device first ensures a smooth registration process. Once the PIN is configured, you can begin registering the key across your favorite FIDO2-compatible online services.
- Ultra-Durable & Portable: Featuring a rotating metal cover, this key is water, crush, and tamper-resistant. It fits easily on a keychain and requires no batteries or network connectivity.
- Check FIDO2 compatibility before purchase - Known limitations: ID Austria is not supported (requires FIDO2 Level 2). Windows Hello login only works with Windows Enterprise editions that support Entra ID, and NFC is NOT supported.
What should a practical rollout checklist contain?
- Inventory domain controllers, member servers, workstations, trusts, applications, appliances, and service accounts.
- Define the pilot OU, business owner, maintenance window, success criteria, and rollback authority.
- Enable the required Advanced Audit Policy subcategories and confirm effective settings.
- Collect 4624, 4625, 4648, 4675, NTLM Operational, and relevant 4024 records centrally.
- Investigate NTLMv1, privileged-account anomalies, workstation-to-workstation use, and repeated failures.
- Remediate clients and services toward Kerberos or modern application authentication.
- Test restrictions against production-like workloads and document every remaining exception.
- Expand enforcement in controlled groups while watching service health and failure alerts.
- Review policy changes, directory modifications, privileged activity, and source-host patterns continuously.
- Reassess exceptions on a fixed date and remove them when the dependency is gone.
Frequently Asked Questions
Does disabling NTLM also disable Kerberos?
No. Kerberos remains the normal domain authentication protocol when a client can locate a domain controller, resolve the service name, and maintain acceptable clock synchronization. NTLM restrictions mainly remove fallback paths, so DNS, time, and service-principal-name health become more important during testing.
Can local Windows accounts still authenticate after NTLM restrictions?
Local-account logons on the same computer are a different path from domain authentication. A network connection that uses a local account can still be affected by separate policy settings, so test local administration, remote management, and service credentials independently rather than assuming one result covers all three.
How should I handle an exception for an unpatchable appliance?
Place the appliance in a segmented network, limit its destination servers and account permissions, and monitor every authentication from it. Record the technical owner, compensating controls, review date, and replacement plan; an exception should be a dated risk decision, not a global allow rule.
What is the safest way to test a restriction outside production?
Clone the relevant Group Policy settings into a test OU and use representative accounts, scheduled tasks, file shares, and application transactions. Capture both client and server logs, run through a normal operating cycle, and rehearse rollback before moving the same policy to a production pilot.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

