Free tools Windows power users keep installed
One-click scans. No signup required.
Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
The safest way to enable workplace AI is a staged rollout, not a single privacy switch. First inventory every assistant, connector and agent. Classify information into allowed, restricted and prohibited categories; enforce single sign-on (SSO), multifactor authentication (MFA) and least-privilege access; remove unnecessary connectors and external sharing; set retention, deletion and legal-hold rules; verify each vendor’s model-training terms; then pilot with synthetic or low-sensitivity data. Review audit logs and permissions on a scheduled basis, and preserve screenshots or configuration exports so every change is reviewable.
This approach matters because an assistant can retrieve whatever the signed-in employee can already access. Privacy therefore depends on identity, repository permissions, connector scope, data use, retention and monitoring together—not only on whether a vendor trains a model on prompts.
As an Amazon Associate I earn from qualifying purchases.
What exactly must a workplace AI privacy program control?
A complete program covers six separate questions: what the assistant can reach, how submitted data is used, how long interactions remain available, which connectors and agents can act, what administrators can observe, and how the service is introduced. Treating these as separate control planes exposes gaps that a “no training” setting cannot fix.
- Access scope: Which identity is signed in, and which files, mailboxes, chats, calendars or systems can that identity access?
- Data use: Are prompts, responses, uploads or connector results used to train models, improve services or support human review?
- Retention and deletion: How long are conversations stored, can users delete them, and can administrators place or honor a legal hold?
- Connectors and agents: What permissions do add-ons have, where do they send data, and can they perform actions rather than only answer questions?
- Auditability: Are prompts, responses, file access, policy changes and sharing events logged and searchable?
- Rollout: Which employees receive access first, and what evidence is required before expansion?
Document each control in one register. A vendor can offer strong model-training protections while an over-broad connector, stale group or public link still exposes confidential information.
#1 Best Overall
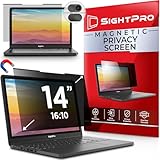
- 【Instant Snap-on Magnetic Attachment】- The Patented Magnetic Privacy Screen – Protected by U.S. Patents 9,829,669 and D844,012. Simply place the privacy screen along the top of your MacBook and let the magnets attach along the top. No need for tricky placement, messy tape, or damaging adhesive. Easily remove and reattach when you need it.
- 【Filter Dimensions】: Width: 11 15/16" (304 mm), Height: 7 1/2" (190 mm), Diagonal: 14.1" (358.14 mm) - SightPro Blackout Privacy Filter is engineered to be compatible with Lenovo, HP, Dell, Acer, Asus, Samsung, and other laptop brands. Please verify your screen's width and height measurements before ordering. It's not recommended to make your selection based solely on your screen's diagonal size. [Not optimized for touchscreens.]
- 【Superior Privacy】- Our advanced multi-layered film filter blacks out your screen when viewing from the side, while maintaining a crystal clear screen straight-on. It also protects your eyes from harmful UV and blue light. [Note: It does not block visibility directly behind you, regardless of the distance.]
- 【Perfect for Travel and Open Workspaces】- The Laptop Privacy Screen Filter is the ideal solution for healthcare providers, mobile workers, commuters, students, and business travelers. Now you can stay compliant and safeguard sensitive corporate information while working in airplanes, subways, airports, and public areas.
- 【Package Contents】- Each package includes a magnetic privacy screen filter, magnetic stickers, a webcam privacy cover, a storage folder, and a cleaning cloth. Buy with confidence – located in the US, Sight Pro specializes in providing best-in-class privacy solutions to individuals, small businesses, corporations, government, and educational institutions. Our privacy screens are Section 889 and TAA compliant.
How do I inventory every assistant, connector and agent?
Start with an inventory that includes sanctioned and unsanctioned tools. Ask procurement, identity, endpoint, collaboration and security teams for separate lists; employees often install browser extensions, desktop clients or marketplace agents that never appear in the central software catalog.
- List the service and edition. Record the vendor, product name, plan or license, deployment region, tenant or workspace, administrator URL and policy version.
- Map identities. Note whether access uses corporate SSO, a personal account, a service account or an invitation-based account. Require MFA for every administrative and user path that supports it.
- Enumerate data paths. Record native mail, document, chat and meeting access plus every plug-in, API, browser extension, upload destination and external action.
- Identify agents separately. An agent that can send mail, edit a record, create a ticket or call an API needs an action owner, approval boundary and rollback plan; do not classify it as a passive chatbot.
- Assign an owner and review date. The owner should be able to disable the integration, answer privacy questions and provide a current configuration export.
| Inventory field | Why it matters | Minimum record |
|---|---|---|
| Vendor and product | Identifies the governing terms and administrator surface | Name, edition, region and tenant |
| Identity and groups | Determines who can invoke or administer the tool | SSO method, MFA status, user and admin groups |
| Repositories and scopes | Shows what content can be retrieved | Sites, drives, mailboxes, calendars, APIs and permission model |
| Connectors and agents | Reveals extra destinations and write actions | Permission scopes, owner, action list and disable path |
| Data-use statement | Captures training and service-improvement terms | Exact statement, policy version and capture date |
| Retention and audit | Supports deletion, legal hold and investigations | Retention rule, export method, logs and alert coverage |
How should we classify information before enabling AI?
Use three classes that employees can apply quickly, then map them to existing information-governance labels. A classification is useful only if it changes what users may submit or what the assistant may retrieve.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Fix the driver behind crashes, sound loss and screen glitches3Repair Windows errors before they cause bigger problems| Class | Typical examples | Default AI treatment |
|---|---|---|
| Allowed | Published product documentation, public web copy, synthetic records and non-confidential drafts | Permitted in approved tools and pilot tenants, subject to normal access controls |
| Restricted | Internal roadmaps, customer support records, employee information, unreleased financial material and source code | Use only in an approved workspace with verified permissions, logging, retention and connector scope |
| Prohibited | Credentials, private keys, regulated data without an approved processing path, data under a contractual no-disclosure restriction and material covered by an active legal hold unless counsel approves the workflow | Do not paste, upload, retrieve through an unapproved connector or send to an external agent |
Put the classification in the prompt guidance, upload warnings and data-loss-prevention (DLP) rules. Tell users what to do when a request mixes classes—for example, replace real customer identifiers with synthetic values or ask the data owner for an approved extract.
What do Copilot, Gemini and ChatGPT disclose about training and retention?
The vendors describe different controls, so record each statement rather than assuming one product’s policy applies to another. The table below reflects the cited vendor documentation and the dates available in that documentation.
| Workplace tool | Model-training statement | Retention and administration |
|---|---|---|
| Microsoft Copilot | Microsoft says prompts, responses and data accessed through Microsoft Graph are not used to train foundation language models, including those used by Microsoft Copilot. | Copilot can use organizational email, documents, chats, meetings and contacts through Microsoft Graph, but it surfaces only content the signed-in user is permitted to view. Interaction content is stored and can be managed with Microsoft search, Purview retention and audit tools. |
| Google Workspace Gemini | The reviewed Google Workspace material does not provide a single universal retention period that applies to every tenant; administrators determine the setting. | Google Workspace Help (2026) lists prompt and response retention as 90 days to indefinite, determined by administrators. Users may delete conversations unless an administrator prohibits deletion. |
| ChatGPT Business and Enterprise | OpenAI says content from Business, Enterprise, Edu and ChatGPT for Healthcare workspaces is not used to train its models by default. | Managed workspaces can apply organization-level retention, memory, compliance and access controls. Confirm the settings for your specific plan and workspace before enabling uploads or connectors. |
Save the exact current wording, plan name, region and capture date in your register. A “not used for training” statement does not answer how long chats are stored, who can search them, whether a connector sends data elsewhere or what happens under a legal hold.
Rank #2

- Filter Dimensions: Width: 11 15/16" (304 mm), Height: 7 1/2" (190 mm), Diagonal: 14.1" (358.14 mm) - SightPro Blackout Privacy Filter is engineered to be compatible with Lenovo, HP, Dell, Acer, Asus, Samsung, and other laptop brands. Please verify your screen's width and height measurements before ordering. It's not recommended to make your selection based solely on your screen's diagonal size. [Not optimized for touchscreens.]
- Two Attachment Options - Installs in minutes. Option 1 uses clear adhesive strips that securely attach to any screen. Option 2 uses slide mount tabs that easily stick to the display frame, allowing you to slide the filter on and off the screen as needed.
- Superior Privacy and Anti Glare - Our advanced multi-layered film filter blacks out your screen when viewing from the side, while maintaining a crystal clear screen straight-on. It also protects your eyes from harmful glare, UV, and blue light. [Note: It does not block visibility directly behind you, regardless of the distance.]
- Perfect for Travel and Open Workspaces - Our computer screen privacy filter is the ideal solution for healthcare providers, mobile workers, commuters, students, and business travelers. Now you can stay compliant and safeguard sensitive corporate information while working in airplanes, subways, airports and public areas.
- Package Contents - Each package includes one privacy screen shield filter, two sets of clear adhesive strips, two sets of slide mount tabs, and a microfiber cleaning cloth. Buy with confidence – located in the US, Sight Pro specializes in providing best-in-class privacy solutions to individuals, small businesses, corporations, government, and educational institutions. Our privacy screens are Section 889 and TAA compliant.
How do permissions determine what an assistant can reveal?
Most workplace assistants inherit the user’s existing repository permissions. That is safer than a shared superuser account, but it also means an assistant can expose an overlooked file to anyone who already has access to it.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →- Review inherited access. Export group membership and repository ACLs for the pilot users. Look for nested groups, departed employees, shared mailboxes, anonymous links and broad “everyone in the company” grants.
- Remove stale access before the pilot. Have data owners approve exceptions, then wait for directory and repository synchronization to complete.
- Separate administration from use. Give administrators configuration rights without granting them unnecessary access to business content, and use dedicated break-glass accounts with monitored access.
- Test a restricted file. With an authorized pilot account, ask the assistant to find a deliberately restricted document. With an unauthorized account, verify that the same request returns no content, no extract and no revealing metadata.
- Recheck after role changes. Test a user who changes departments, loses a group and is later deprovisioned. Confirm that access follows the directory change rather than a cached assistant permission.
Do not “fix” an access problem by disabling permission checks. Correct the underlying repository ACL, group or sharing link and then repeat the test.
Which connectors and agents should we disable first?
Disable anything that is not required for the pilot, especially integrations with write access, external destinations or broad scopes. Re-enable one connector at a time after its owner documents the data path.
- Public or anonymous links: Remove them from repositories used by the assistant unless a named business owner has approved the exposure.
- Unbounded search connectors: Narrow them to approved sites, projects or labels instead of an entire tenant.
- Write-capable agents: Start in read-only mode. Require human approval before sending messages, changing records, publishing content or triggering payments.
- Marketplace plug-ins and browser extensions: Check permission scopes, terms of use, storage location and deletion process. Remove extensions that cannot provide those details.
- Personal-account bridges: Block forwarding or synchronization from a managed workspace to consumer accounts unless legal and security owners approve it.
For each enabled integration, record the data source, destination, fields transferred, action permissions, owner, user population, logging coverage and emergency-disable procedure.
How should we configure retention, deletion and legal holds?
Set retention before users create production conversations. The correct period depends on regulatory, contractual, litigation and operational needs; it is not automatically the shortest available option.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Rank #3

- 【Filter Dimensions】: Width: 13 9/16" (345 mm), Height: 7 5/8" (194 mm), Diagonal: 15.6" (396.24 mm) - SightPro Blackout Privacy Filter is engineered to be compatible with Lenovo, HP, Dell, Acer, Asus, Samsung, and other laptop brands. Please verify your screen's width and height measurements before ordering. It's not recommended to make your selection based solely on your screen's diagonal size. [Not optimized for touchscreens.]
- 【Two Attachment Options】- Installs in minutes. Option 1 uses clear adhesive strips that securely attach to any screen. Option 2 uses slide mount tabs that easily stick to the display frame, allowing you to slide the filter on and off the screen as needed.
- 【Superior Privacy and Reduce Glare】- Our advanced multi-layered film filter blacks out your screen when viewing from the side, while maintaining a crystal clear screen straight-on. It also protects your eyes from harmful glare, UV, and blue light. [Note: It does not block visibility directly behind you, regardless of the distance.]
- 【Perfect for Travel and Open Workspaces】- Our computer screen privacy filter is the ideal solution for healthcare providers, mobile workers, commuters, students, and business travelers. Now you can stay compliant and safeguard sensitive corporate information while working in airplanes, subways, airports and public areas.
- 【Package Contents】- Each package includes one privacy screen shield filter, two sets of clear adhesive strips, two sets of slide mount tabs, and a microfiber cleaning cloth. Buy with confidence – located in the US, Sight Pro specializes in providing best-in-class privacy solutions to individuals, small businesses, corporations, government, and educational institutions. Our privacy screens are Section 889 and TAA compliant.
- Define the record. Decide whether prompts, responses, uploaded files, tool results, feedback, logs and generated artifacts are separate records or one conversation record.
- Choose an administrator-controlled period. Document the period, whether it applies to new and existing data, and whether users can delete their own conversations.
- Map legal holds. Specify which system places a hold, whether held content remains searchable, who can release it and how a hold overrides ordinary deletion.
- Test deletion. Delete a pilot conversation as a user, then verify the administrator, export and audit views show the behavior your policy promises.
- Test export and termination. Confirm that you can retrieve required records in a usable format and that departing users lose access without destroying records subject to retention or hold.
For Google Workspace Gemini, the documented administrator-controlled range is 90 days to indefinite (Google Workspace Help, 2026). Do not assume a user’s delete button shortens that period when an administrator prohibits deletion or a legal hold applies.
How can we prevent external sharing and accidental disclosure?
Combine technical restrictions with simple user prompts. Users should see a clear warning at the moment they paste, upload or invoke an external action.
- Restrict sharing of AI conversations and generated files to named internal recipients by default.
- Block external recipients for restricted and prohibited labels, and require an approved exception workflow for business-critical cases.
- Apply DLP rules to prompts, uploads, responses and connector traffic where the platform supports those inspection points.
- Disable automatic publishing, public links and cross-tenant sharing during the pilot.
- Mask customer identifiers, employee identifiers and secrets before using data for demonstrations or testing.
- Train users to treat generated text as a new copy of the source data: a response can repeat a confidential value even if the original file is not attached.
Shoulder-surfing and local downloads remain separate risks. Use device lock timers, managed storage and appropriate screen privacy in shared offices; these measures do not replace tenant-level data controls.
What is the safest pilot and rollout sequence?
Use a small, reversible pilot and require evidence at each gate. Synthetic data is preferable; if real data is necessary, begin with low-sensitivity material owned by the pilot team.
- Prepare: Approve the inventory, classifications, identity controls, connector list, retention rule, support process and rollback owner.
- Configure: Enable SSO and MFA, remove unnecessary integrations, restrict external sharing, apply DLP and turn on audit logging.
- Test: Run authorized and unauthorized prompts, restricted-file retrieval tests, deletion and export tests, connector action tests and deprovisioning tests.
- Pilot: Enroll a limited group from different roles. Prohibit prohibited data and require incident reporting for unexpected retrieval, sharing or retention.
- Review: Examine logs, DLP alerts, user feedback, false positives and permission changes. Fix issues before adding another connector or user group.
- Expand gradually: Increase the population in defined waves, preserving the same controls and a documented stop condition.
Keep a versioned change record with configuration exports, screenshots, test prompts, expected results, actual results, approvers and dates. This evidence makes later audits and incident investigations faster.
Rank #4

- Compatible Models: Width: 13 9/16" (13.5 inch/344 mm), Height: 7 5/8" (7.6 inch/194 mm), Diagonal: 15.6" (396.24 mm) widescreen laptops which have a 16:9 aspect ratio. Not touchscreen compatible !!! Not fit for 16:10.Do NOT rely solely on your laptop’s diagonal size when ordering. Use a ruler to measure your screen’s visible area (excluding the black bezels). If the width reads 344mm and height reads 194mm, this filter is a perfect match for your device.
- Keep Information Privacy: Effective "black out" privacy from side views outside the 60-degree viewing angle. Designed for optical clarity when viewing from the front, a person not at the front of the screen can only see the dark side of the screen, so it protects buisness secrets and personal privacy
- Eye and Screen Protection: Privacy filter does not only protect your private life but also protects your eyes by blocking 30% of blue light , blocking the harmful blue light between 380 - 495nm, it filters out the blue light and relieves eye strain. Our laptop privacy screen also helps keep your screen safe from dust and scratches
- Perfect For Open Workspaces: Great for maintaining screen privacy in high traffic areas such as open work spaces, airports, airplanes, commuter trains, coffee shops and other public places, etc
- Easy Installation: Choose between 2 simple Options; Slide-On/Off or Mounted. Not touchscreen compatible
How do we verify that the controls actually work?
Verification must test outcomes, not merely show that a checkbox is enabled. Use a repeatable test script and retain the results.
| Test | Expected result | Evidence to keep |
|---|---|---|
| Unauthorized user requests a restricted file | No content, extract or sensitive metadata is returned | Prompt, account, timestamp and response capture |
| Authorized user asks about an approved file | Only permitted content is retrieved and citations or source links follow policy | Prompt, source identifier and response |
| Prompt contains a prohibited secret | Upload or submission is blocked, masked or routed to the approved exception process | DLP event and user notification |
| Agent attempts an external write action | Action is blocked or requires the configured human approval | Agent log, approval record and final state |
| User deletes a conversation | Behavior matches the administrator retention and hold policy | User view, administrator view and export result |
| User loses a group or is deprovisioned | Access disappears after the documented synchronization interval | Directory event, assistant test and audit entry |
Enable alerts for unusual downloads, repeated blocked prompts, new external sharing, connector-scope changes, privilege escalation and disabled logging. Assign an owner and response time to each alert; an unread log is not an effective control.
How often should access and vendor settings be reviewed?
Use both a calendar schedule and event-triggered reviews. A quarterly review is a practical baseline for ordinary access; higher-risk agents and regulated data may require monthly or continuous monitoring.
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Scan for outdated or missing drivers - takes under a minuteDriver Scan →| Trigger | Required review |
|---|---|
| Monthly | Review privileged administrators, agent owners, failed DLP events and unresolved sharing alerts. |
| Quarterly | Reconcile users and groups, sample repository permissions, confirm connector scopes and retest deletion and deprovisioning. |
| Vendor release or policy change | Re-read model-training, retention, memory, connector and subprocessors language; rerun high-risk tests. |
| New connector, agent or data source | Complete a new scope, destination, action and legal review before activation. |
| Incident or unexpected output | Freeze the affected integration, preserve logs, investigate source permissions and approve a documented recovery. |
Keep the previous configuration and policy version. Comparing versions is often the quickest way to identify an accidental scope expansion.
What are the most common implementation failures?
Most failures come from treating a vendor promise as a complete governance program. Use the symptom and fix below as a troubleshooting checklist.
Best Value

- 【Instant Snap-on Magnetic Attachment】- The Patented Magnetic Privacy Screen – Protected by U.S. Patents 9,829,669 and D844,012. Simply place the privacy screen along the top of your MacBook and let the magnets attach along the top. No need for tricky placement, messy tape, or damaging adhesive. Easily remove and reattach when you need it.
- 【Filter Dimensions】: Width: 12 3/16" (310 mm), Height: 6 7/8" (175 mm), Diagonal: 14" (355.6 mm) - There are two different 14 inch screen sizes, please select the correct one. SightPro Blackout Privacy Filter is engineered to be compatible with Lenovo, HP, Dell, Acer, Asus, Samsung, and other laptop brands. Please verify your screen's width and height measurements before ordering. It's not recommended to make your selection based solely on your screen's diagonal size. [Not optimized for touchscreens.]
- 【Superior Privacy】- Our advanced multi-layered film filter blacks out your screen when viewing from the side, while maintaining a crystal clear screen straight-on. It also protects your eyes from harmful UV and blue light. [Note: It does not block visibility directly behind you, regardless of the distance.]
- 【Perfect for Travel and Open Workspaces】- The Laptop Privacy Screen Filter is the ideal solution for healthcare providers, mobile workers, commuters, students, and business travelers. Now you can stay compliant and safeguard sensitive corporate information while working in airplanes, subways, airports, and public areas.
- 【Package Contents】- Each package includes a magnetic privacy screen filter, magnetic stickers, a webcam privacy cover, a storage folder, and a cleaning cloth. Buy with confidence – located in the US, Sight Pro specializes in providing best-in-class privacy solutions to individuals, small businesses, corporations, government, and educational institutions. Our privacy screens are Section 889 and TAA compliant.
- “The tool does not train on our data, so we are done.” Check retention, user deletion, legal holds, connectors, external sharing and repository permissions separately.
- An assistant reveals a confidential document. Inspect the user’s inherited groups, stale links and shared drives; correct the source permission rather than weakening retrieval controls.
- Users cannot delete conversations. Review the administrator retention setting and any legal hold. This may be intentional policy behavior, not a broken button.
- A connector returns more data than expected. Narrow its scope, remove write permissions, rotate credentials if needed and retest with an unauthorized account.
- Logs exist but nobody reviews them. Assign an owner, alert thresholds and a response deadline, then record review completion.
- Policy differs between regions or plans. Record the exact edition, tenant region and policy version; do not copy settings from another workspace without verification.
- Employees paste real secrets during testing. Stop the test, preserve the event, rotate exposed credentials and switch future tests to synthetic values.
What should the written workplace AI policy contain?
A short policy is easier to follow when it points to enforceable settings and named owners. Include these elements:
- Approved assistants, editions, regions and administrator contacts
- Allowed, restricted and prohibited data examples
- Rules for prompts, uploads, generated files, memory and feedback
- Permitted connectors and agents, including action-approval requirements
- SSO, MFA, device and session requirements
- External-sharing, public-link and personal-account restrictions
- Retention, user deletion, export and legal-hold procedures
- Logging, DLP, alert ownership and review cadence
- Incident reporting, emergency disablement and credential-rotation steps
- Training requirements and an acknowledgement process
Publish the policy with a one-page prompt checklist and a link to the current configuration register. Update both when a vendor changes a material setting or a new agent is approved.
Frequently Asked Questions
Can employees delete workplace AI conversations themselves?
Sometimes. Administrator retention settings can allow, limit or prohibit user deletion, and a legal hold can preserve records even after a user requests deletion. Test the user, administrator and export views in the specific tenant rather than relying on the interface label.
Should a company ban all file uploads to workplace AI?
A total ban is usually less useful than a data-classification rule. Permit synthetic and approved low-sensitivity files, require an approved workspace for restricted material, and prohibit secrets or data lacking a lawful processing path.
What happens to AI access when an employee changes departments?
Access should change when directory groups and repository permissions change, but synchronization can take time. Include role-change and deprovisioning tests in every rollout and investigate any result that contradicts the identity system.
How can we prove an AI connector did not send data outside the company?
Document its destination, fields, permission scopes and subprocessors, then correlate connector logs with network, DLP and audit records during a controlled test. If the service cannot provide sufficient logs or a clear destination, keep the connector disabled.
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallCrashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteQuick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

