Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
A reliable website maintenance plan is a recurring operating routine, not a reminder to click “Update.” It names owners, inventories every dependency, sets risk-based patch windows, creates verified backups of both files and the database, protects administrator access, monitors changes, and provides a tested rollback and restore procedure. Use daily or continuous monitoring for critical sites, weekly update and backup checks, a planned monthly maintenance window, quarterly reviews, and immediate out-of-band response for critical vulnerabilities or signs of compromise. Adjust those intervals to your site’s business impact and acceptable data loss rather than treating them as universal deadlines.
What should a website maintenance plan include?
A complete plan connects prevention, change control, and recovery. It should say what is maintained, who is responsible, how often work happens, what evidence proves it worked, and what happens when an update fails.
As an Amazon Associate I earn from qualifying purchases.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Fix the driver behind crashes, sound loss and screen glitches3Repair Windows errors before they cause bigger problems- Scope and inventory: production and staging sites, CMS core, plugins or packages, themes, custom code, hosting, DNS, certificates, domains, analytics, payment integrations, email services, and backup destinations.
- Ownership: an owner for each asset, an approver for high-risk changes, and a person with authority and access to recover the site.
- Support status: vendor support dates, end-of-life versions, renewal dates, and dependencies that could make an update unsafe.
- Maintenance calendar: routine checks, update windows, backup schedules, restore tests, quarterly reviews, and emergency triggers.
- Backup design: complete file-and-database copies, retention, separate storage, encryption, access controls, failed-job alerts, and restore evidence.
- Safe change process: advisory review, staging test, pre-change backup, implementation, verification, monitoring, and rollback criteria.
- Access and monitoring: multifactor authentication (MFA), least privilege, HTTPS, account reviews, audit logs, and alerts for suspicious changes.
- Recovery runbook: contacts, credentials or access paths, restore steps, DNS and certificate actions, communications, evidence preservation, and post-incident review.
Write the plan so another person can execute it during an incident. If a step depends on one employee’s memory, it is not yet an operational control.
How often should a website be updated?
Apply security fixes according to risk, exploitability, exposure, and business impact—not a single calendar interval. NIST defines patch management as identifying, prioritizing, acquiring, installing, and verifying patches, while the UK National Cyber Security Centre (NCSC) advises urgent out-of-band fixes for critical vulnerabilities and thorough testing of updates. NIST’s SP 800-40 Rev. 4 was published in April 2022.
#1 Best Overall

- Slim durable design to help take your important files with you
- Vast capacities up to 6TB[1] to store your photos, videos, music, important documents and more
- Back up smarter with included device management software[2] with defense against ransomware
- Help secure your important files with password protection and hardware encryption
- 3-year limited warranty
| Cadence | What to do | When to accelerate |
|---|---|---|
| Daily or continuous | Watch uptime, backup-job failures, security alerts, administrator logins, and suspicious file or content changes on business-critical sites. | Any alert indicating compromise, active exploitation, or a failed recovery safeguard. |
| Weekly | Review available security updates, confirm backup completion, and inspect high-value flows such as login, forms, checkout, and contact submissions. | A vulnerability is being exploited, a vendor issues an emergency notice, or monitoring shows abnormal behavior. |
| Monthly | Apply routine updates in a planned window, review administrator accounts and installed components, check storage capacity, and perform a restore test when feasible. | An update fixes a high-severity issue or a dependency reaches end of support. |
| Quarterly | Recheck the asset inventory, vendor support status, disaster-recovery contacts, retention rules, and lessons from incidents or failed changes. | Major architecture, ownership, hosting, or business changes. |
| Out of band | Assess and respond immediately to critical vulnerabilities, active exploitation, compromise indicators, or emergency vendor instructions. | Do not wait for the next scheduled window. |
These intervals are an operating baseline, not a universal standard. A brochure site with little change may tolerate a different routine from a busy store or membership service. Record the rationale for your chosen targets and revisit it after an incident or major change.
How do I decide which security updates to install first?
Prioritize the combination of technical risk and business exposure. A remotely exploitable flaw in an internet-facing login, payment integration, or administrator component generally outranks a low-impact issue in an isolated feature, but the decision should be recorded rather than assumed.
- Read the advisory: identify the affected component, versions, severity, exploitability, available fix, and any temporary mitigation.
- Map exposure: note whether the component is public-facing, reachable only by administrators, disabled, or present on multiple sites.
- Assess impact: consider account takeover, data loss, defacement, payment interruption, privacy obligations, and downtime costs.
- Check compatibility: review required runtime, database, theme, plugin, package, or hosting changes and whether the vendor still supports your version.
- Set a target: define the response time for your site and document who can authorize an emergency change.
- Verify after installation: confirm the expected version, review logs, and test important user journeys.
The NCSC’s secure deployment and maintenance guidance, published and reviewed 7 May 2025, says updates should be signed and thoroughly tested. It also states that updates and patches should not be a premium feature of software.
How often should I back up my website?
Choose frequency from how much data you can afford to lose and how quickly the site changes. WordPress guidance says smaller sites may back up weekly, while high-activity sites may need daily backups. Those are examples to adapt to your recovery objectives, not rules for every platform.
- Low-change informational site: a weekly schedule may be suitable if you can recreate the small amount of intervening content.
- Frequently edited, membership, or commerce site: daily backups, or more frequent database protection, reduce the amount of lost orders, accounts, or posts.
- Before every consequential change: create a current, functional backup immediately before patching, configuration changes, migrations, or theme work.
CISA’s patch-management guidance requires a current, functional backup or archive before deployment and says a plan should define frequency, verification, retention, and storage locations. Treat a successful job notification as a starting point: periodically prove that the files can be read and the database can be restored.
What exactly must a website backup contain?
A complete recovery copy includes both the site files and the database. WordPress explains that a typical site needs both to be fully restored; downloading only the site directory omits database content such as posts, users, settings, and orders.
Rank #2
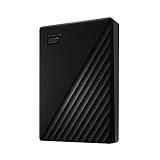
- Slim durable design to help take your important files with you
- Vast capacities up to 6TB[1] to store your photos, videos, music, important documents and more
- Back up smarter with included device management software[2] with defense against ransomware
- Help secure your important files with password protection and hardware encryption
- 3-year limited warranty
Files to include
- Uploaded media and other user-generated files.
- CMS core files, themes, plugins, packages, and custom code.
- Configuration files, environment settings, and web-server rules needed to rebuild the application.
- Certificates, deployment manifests, and documentation required to reconnect external services, where policy permits storing them.
Database and service information
- The complete production database, with a consistent snapshot rather than an incomplete file copy.
- Database credentials or a secure method to retrieve them during recovery.
- Details for DNS, domains, email, analytics, payments, and other integrations that must be reconnected.
Keep at least three to five recent copies in different locations as an example starting point from WordPress backup guidance. Separate locations can include the host, a cloud account, and a local computer. Adapt the number to your recovery objectives, storage risk, and retention requirements.
Where should I store website backups?
Use more than one location and separate backup access from production access. A useful design combines an automated copy for quick recovery with a separately stored or offline copy that is less exposed to a compromised hosting account.
- Primary backup destination: an automated repository monitored for completion and capacity.
- Separate account or region: a copy protected from a single hosting-account failure or accidental deletion.
- Offline or removable copy: an external hard drive can add a disconnected copy, but it must be protected from loss, theft, ransomware, and hardware failure and must not be the only backup.
The Australian Cyber Security Centre’s website guidance, published 1 July 2020 and reviewed 29 July 2024, lists cloud storage or an external hard drive as possible destinations. Encrypt backups where appropriate, restrict who can delete them, and monitor for failed jobs. Record geographic or account separation, retention periods, and how a potentially compromised backup is quarantined.
How do I create a maintenance calendar?
Turn the cadence into named tasks with an owner, expected evidence, and an escalation path. A calendar entry should answer what is checked, where it is recorded, and what happens if it fails.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
- List recurring checks: uptime, alerts, backup jobs, updates, administrator accounts, storage, certificates, domains, and key user journeys.
- Assign an owner and backup owner: include an approver for high-risk changes and a recovery executor.
- Choose a maintenance window: select a low-traffic period, publish internal notification requirements, and confirm how to contact decision-makers.
- Define evidence: save update versions, backup timestamps, test results, screenshots or logs, and any exceptions.
- Define escalation: specify when a failed check blocks release, who is paged, and when to invoke the recovery runbook.
WordPress recommends frequent maintenance, update checks, backups, and site checks; its sample calendar includes monthly statistics checks and periodic backup and validation work. Use that pattern as a prompt, then tune it to traffic, data volatility, and acceptable downtime.
How do I safely update WordPress plugins and other components?
Use a repeatable release workflow that creates a recovery point before touching production and verifies the site afterward. The same method applies to CMS core, themes, extensions, server packages, and custom code.
Rank #3
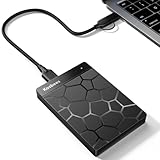
- 【Plug-and-Play Expandability】 With no software to install, just plug it in and the drive is ready to use in Windows(For Mac,first format the drive and select the ExFat format.
- 【Fast Data Transfers 】The external hard drives with the USB 3.0 cable to provide super fast transfer speed. The theoretical read speed is as high as 110MB/s-133MB/s, and the write speed is as high as 103MB/s.
- 【High capacity in a small enclosure 】The small, lightweight design offers up to 500GB capacity, offering ample space for storing large files, multimedia content, and backups with ease. Weighing only 0.35 Lbs, it's easy to carry "
- 【Wide Compatibility】Supports PS4 5/xbox one/Windows/Linux/Mac and other operating systems, ensuring seamless integration with game consoles,various laptops and desktops .
- Important Notes for PS/Xbox Gaming Devices: You can play last-gen games (PS4 / Xbox One) directly from an external hard drive. However, to play current-gen games (PS5 / Xbox Series X|S), you must copy them to the console's internal SSD first. The external drive is great for keeping your library on hand, but it can't run the new games.
- Review the change: read the vendor advisory, affected versions, severity, exploitability, compatibility notes, and required prerequisites.
- Confirm inventory: verify the component is actually installed, identify dependencies, and note whether it is exposed or business-critical.
- Check the backup: confirm a recent functional file-and-database backup, record its timestamp and location, and ensure the restore owner can access it.
- Prepare the window: verify monitoring, maintenance communication, rollback access, and a way to pause automated deployments or traffic if needed.
- Test first: apply the update in staging or a representative test environment when practical. Exercise authentication, forms, checkout, integrations, and scheduled jobs.
- Deploy in priority order: install the highest-risk available fix first, following the platform’s supported procedure. Avoid bundling unrelated changes when isolating a failure matters.
- Verify installation: check the reported version, deployment logs, error logs, page rendering, permissions, and configuration.
- Run user-journey checks: test login, password reset, forms, payments, email delivery, search, uploads, and any workflow that earns or protects revenue.
- Monitor after release: watch uptime, performance, logs, administrator activity, redirects, unexpected content, and security alerts for a defined observation period.
- Record the result: document versions, timestamps, test evidence, exceptions, and follow-up actions.
For a WordPress-specific operation, take the backup before updating core, plugins, or themes; do not rely on a plugin update screen as your recovery plan. If a component cannot be tested safely, document the risk, consider a temporary mitigation, and obtain the required approval rather than silently postponing it.
What should I verify after an update?
Verification should cover both technical health and the actions visitors perform. A green deployment message does not prove that a payment callback, form email, or administrator login still works.
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →- Confirm the expected component version and that no dependency was left in an unsupported state.
- Check HTTP status, page rendering, assets, redirects, caching, and server and application error logs.
- Sign in and out, test password reset and MFA, and confirm role permissions.
- Submit representative contact or registration forms and verify delivery and storage.
- Run checkout, payment, subscription, or other revenue workflows in a safe test mode where available.
- Check integrations, webhooks, scheduled jobs, search, uploads, and email notifications.
- Review administrator logins, file changes, DNS and certificate records, and unexpected content or redirects.
- Keep monitoring active after the window and record the evidence and any residual risk.
What access controls and monitoring belong in the plan?
Administrator access is a primary maintenance risk because a stolen account can bypass otherwise careful patching and backups. The Australian guidance recommends MFA, HTTPS, strong passwords, access controls, current software, backups, and review for suspicious activity.
- Require MFA for administrator, hosting, DNS, domain, backup, and recovery accounts where supported.
- Use unique strong passwords and a managed method for storing them; never share a personal administrator account.
- Apply least privilege and remove unused accounts promptly after staff or vendor changes.
- Review access regularly and after every ownership, contractor, or hosting change.
- Monitor administrator logins, file and database changes, plugin or package changes, DNS and certificate changes, and backup failures.
- Alert on unexpected redirects, new administrator accounts, suspicious content, repeated login failures, or disabled monitoring.
- Keep HTTPS current and verify certificate renewal ownership and notification paths.
Record who can approve a high-risk change and who can execute recovery. Those roles may be held by different people, but both must be reachable during the maintenance window.
How do I restore a website after an update breaks it?
Stop making additional changes, preserve evidence, and choose the least disruptive recovery path. A rollback to the previous component may be enough for a known isolated failure; a full restore is safer when files, database state, or security integrity are uncertain.
- Declare the incident: note the time, symptoms, affected journeys, recent changes, and incident owner.
- Reduce impact: place the site in maintenance mode, disable the failing component, or route traffic to a safe page if that protects users and data.
- Preserve evidence: retain logs, error messages, deployment records, suspicious files, and the failed version before cleanup.
- Check the recovery point: identify the last known-good file-and-database backup and confirm it predates the failure.
- Attempt a targeted rollback: if the cause is known and the database is compatible, revert the changed component using the documented procedure.
- Restore when needed: restore both files and database to a clean environment or production according to the runbook. Reconnect DNS, certificates, integrations, and secrets carefully.
- Validate: test authentication, forms, payments, content, integrations, permissions, and security indicators before reopening the site.
- Monitor and communicate: watch errors and suspicious activity, tell affected stakeholders what changed, and record recovery time and data loss.
- Prevent recurrence: identify the triggering dependency, improve staging coverage or rollback automation, and update the inventory and runbook.
Never overwrite the only copy of a failed system before preserving it. If compromise is suspected, quarantine the affected backup and investigate before restoring it; otherwise, the recovery operation can reintroduce the attacker.
Rank #4

- Slim durable design to help take your important files with you
- Back up smarter with included device management software[2] with defense against ransomware
- Help secure your important files with password protection and hardware encryption
- 3-year limited warranty
How do I test whether a backup really works?
Perform a restore test on a representative backup, preferably in an isolated environment, and record the result. The test should demonstrate that the files and database can be combined into a functioning site, not merely that an archive exists.
- Choose a backup that matches the retention and recovery objectives you advertise.
- Restore files and database into an isolated environment with documented versions and configuration.
- Verify media, themes, plugins, custom code, users, settings, forms, integrations, and permissions.
- Measure the elapsed time and note any manual steps, missing secrets, broken links, or version incompatibilities.
- Record the tester, date, backup identifier, result, recovery time, data-loss window, and corrective actions.
A backup that has never been restored is an assumption rather than demonstrated recovery capability. Repeat the test after major hosting, CMS, database, or backup-process changes.
What should the recovery runbook contain?
Keep a concise first-response page and link it to detailed procedures. It should remain usable when the normal website, ticketing system, or a key employee is unavailable.
- Incident criteria, severity levels, and the person who can declare an incident.
- Emergency contacts for hosting, DNS, domain registration, certificates, payment, email, and key vendors.
- Secure access paths to production, staging, backup repositories, and monitoring; do not print unprotected secrets.
- Backup locations, identifiers, retention rules, restore order, and rollback decision points.
- Commands or UI paths for maintenance mode, traffic control, restore, cache clearing, and verification.
- Evidence-preservation requirements and a process for quarantining a compromised backup.
- Customer, staff, partner, or regulator communication responsibilities where applicable.
- Post-incident review questions, owner assignments, and deadlines for corrective work.
Test the runbook and record whether the stated contacts, permissions, backups, and recovery-time target actually worked.
Free tools Windows power users keep installed
One-click scans. No signup required.
Should maintenance be managed or self-managed?
Compare operating models by responsibilities and recovery capability rather than by marketing labels. The right choice depends on who can safely perform updates, monitor failures, and restore the site outside normal business hours.
| Decision area | Questions to answer |
|---|---|
| Managed versus self-managed | Who applies patches, watches failures, approves risky changes, and performs recovery? |
| Automation versus manual control | Does automation improve speed and consistency while preserving review, staging, alerts, and rollback? |
| Backup design | Are files and database complete, retained, separated, encrypted, access-controlled, and restore-tested? |
| Recovery objectives | How much data loss is acceptable, and how quickly must the site return to service? |
| Compatibility and testing | Is staging available, are integrations covered, and can a failed release be reversed? |
| Access and monitoring | Are MFA, role controls, alerting, audit logs, and incident response in place? |
| Provider assurance | What are the support lifecycle, security practices, data location, and contractual responsibilities? |
Automation is valuable for repeatability, but an automated backup or update that nobody monitors can fail silently. A managed arrangement still needs clearly assigned ownership, evidence of restore tests, and a way to obtain the backups and logs if the provider is unavailable.
Best Value

- World’s First 6TB 2.5” Portable Hard Drive
- Slim durable design to help take your important files with you
- Vast capacities up to 6TB[1] to store your photos, videos, music, important documents and more
- Back up smarter with included device management software[2] with defense against ransomware
- Help secure your important files with password protection and hardware encryption
What are the most common maintenance-plan failures?
Most failures are process gaps rather than a lack of available update buttons. Design controls for these predictable mistakes.
- Files-only backups: add database exports and test a combined restore.
- One storage location: add a separate account, location, or offline copy and restrict deletion.
- Blind automatic updates: require advisory review, staging where practical, pre-change backups, and post-release checks.
- No owner: assign primary and backup owners for every asset and recovery action.
- Stale inventory: review components, domains, certificates, integrations, and support dates quarterly and after changes.
- Unprotected administrator access: enforce MFA, least privilege, HTTPS, unique credentials, and prompt account removal.
- Untested recovery: schedule restore exercises and capture elapsed time, missing steps, and data-loss results.
- Ignoring emergency advisories: define out-of-band authority and a communication path that does not depend on the normal calendar.
How do I document targets without inventing universal deadlines?
Write targets that reflect the site’s risk and business requirements. State the maximum acceptable data loss, target restoration time, critical-component response target, backup retention, and verification frequency, then document who approved them.
Official guidance does not establish one patch deadline or backup frequency that fits every website. NIST and NCSC support risk-based prioritization; WordPress provides weekly and daily backup examples for different activity levels. Review your targets after incidents, major traffic or data changes, hosting migrations, or new regulatory obligations.
Which official guidance supports this approach?
Use primary guidance to keep the plan current:
- WordPress Developer Resources: Backups explains why both files and database are required, gives weekly and daily examples, and suggests three to five recent copies in different locations.
- CISA patch-management guidance calls for a current, functional backup before deployment and defined frequency, verification, retention, and storage locations.
- NIST SP 800-40 Rev. 4 defines the patch-management lifecycle of identifying, prioritizing, acquiring, installing, and verifying updates.
- NCSC secure deployment and maintenance guidance addresses signed, thoroughly tested updates and urgent response to critical vulnerabilities.
- Australian Cyber Security Centre: Secure your website recommends MFA, HTTPS, strong passwords, access controls, regular updates, backups, and suspicious-activity review.
What is a practical first week for building the plan?
Start with controls that reduce the largest recovery and exposure risks, then add detail as you learn how the site behaves.
- Day 1: inventory the production site, dependencies, accounts, domains, certificates, integrations, and existing backup destinations.
- Day 2: assign owners, recovery authority, emergency contacts, and a maintenance window.
- Day 3: create a complete file-and-database backup, place a copy in a separate location, and verify that the recovery owner can access it.
- Day 4: enable MFA, remove unused accounts, confirm HTTPS, and turn on alerts for backup failures and administrator changes.
- Day 5: test a representative update in staging or a safe test environment and document the verification checklist.
- Day 6: perform an isolated restore test, measure recovery time, and fix missing credentials, configuration, or integration steps.
- Day 7: publish the calendar and runbook, record targets for data loss and restoration time, and schedule the first quarterly review.
After that baseline is working, refine automation, expand test coverage, and tune frequencies from observed failures, traffic, data changes, and incident history.
Frequently Asked Questions
Can I rely on my hosting provider’s automatic backups?
Only if you can verify what they include, how long they are retained, where they are stored, who can delete them, and how to restore them independently. Confirm that both files and the database are covered and perform a test restore rather than relying on a dashboard status.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Should I update all website plugins at once?
Bundling unrelated updates makes a failure harder to isolate. Group changes only when compatibility testing covers them; otherwise, prioritize the highest-risk fix, verify it, and keep a clear rollback point before moving to the next change.
What should I do if a critical vulnerability appears outside my maintenance window?
Use the out-of-band procedure: assess exposure, notify the authorized approver, create or confirm a functional backup, test a mitigation or fix as quickly as practical, and monitor closely after deployment. Do not defer an actively exploited issue solely to preserve the calendar.
How do I know whether my recovery target is realistic?
Measure it during a restore exercise, including access approvals, downloading backups, rebuilding the database, reconnecting integrations, clearing caches, and validating user journeys. The elapsed test time and any manual blockers provide a more useful target than an unsupported promise.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.
Recommended Free Tools

