Free tools Windows power users keep installed
One-click scans. No signup required.
Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
No—Microsoft Entra ID SAML does not directly sign a user into the SAP GUI desktop connection. SAP GUI single sign-on uses SAP Secure Network Communications (SNC), with Kerberos tickets or X.509 certificates as the credential options. SAML belongs to browser-facing SAP applications and federation with SAP BTP or SAP Identity Authentication Service (IAS). Entra ID can be part of both architectures, but the protocols and configuration paths are different.
Why can Entra ID be the identity provider but still not sign SAP GUI in with SAML?
An identity provider establishes or verifies a user’s identity; a client and service still need a compatible protocol to exchange that identity. Microsoft’s SAP identity guidance draws the practical boundary this way: browser-based clients use SAML or OIDC, while SAP GUI uses X.509 or Kerberos tickets. Entra ID can therefore be central to an organization’s SAP identity architecture without a SAML assertion being the credential SAP GUI presents to an ABAP application server.
As an Amazon Associate I earn from qualifying purchases.
For desktop SSO, the SAP GUI connection uses SNC, SAP’s security layer between the client and the ABAP server. In a Kerberos design, the client obtains a Kerberos ticket and SNC presents it to SAP. In a certificate design, SNC uses an X.509 credential. In either case, the GUI logon path depends on SNC configuration and the selected credential—not on the browser SAML exchange.
This is a protocol boundary, not a claim that the systems cannot work together. An organization can use Entra ID for browser-based SAP sign-in and maintain a separate SNC-based design for SAP GUI. The two paths may share identity governance or organizational processes, but success on one path does not establish that the other is configured.
#1 Best Overall

- 4 PROFESSIONAL MECHANICAL KEYBOARD - The thinnest mechanical keyboard in the world! The combination of tactile feel, the psycho-acoustic experience and incredible craftsmanship all deliver an unmatched typing experience that only Das Keyboard 4 offers. With a Das Keyboard 4, you'll type faster and longer. It feels so good, you won't want to stop.
- PREMIUM TACTILE EXPERIENCE - Best-in-class Cherry MX Blue mechanical key switches provide tactile and audio feedback so accurate it allows you to execute every keystroke with lightning-fast precision. Factory lubricated stabilizers on large keys for smooth typing with bumps on the F and J keys. Enjoy the tactile experience you love from a mechanical keyboard, with just enough sound to satisfy you - and not annoy your coworkers!
- UP TO 50 MILLION KEYSTROKES - Laser-etched keycaps for maximum durability are paired with Cherry MX Blue switches, giving your new mechanical keyboard life up to 50 million keystrokes. High-performance, gold-plated switches provide the best contact and typing experience because, unlike other metals, gold does not rust, increasing the lifespan of the switch.
- FULL N-KEY ROLLOVER - Fast typists, productive professionals and gamers will appreciate that Das Keyboard 4 supports full NKRO over USB. No need to use a PS2 adapter anymore. Just press shift + mute to toggle to NKRO (works with both Windows and Linux).
- 2 PORT USB 3.0 HUB & MORE - The convenience to charge USB devices & simultaneously upload content through USB is right at your fingertips. A blazing fast 2- port USB 3.0 hub to transfer music, high resolution pics & large videos at up to 5Gb/second. That’s 10x faster than USB 2.0. Extra long 6.5ft(201cm) USB cable w/ single USB A connector. Dedicated media controls w/ LARGE VOLUME KNOB & instant sleep button. Magnetically detachable footbar ruler to raise the keyboard to an optimal 4-degrees.
What does SNC do in an SAP GUI connection?
SNC provides the security mechanism SAP GUI uses to communicate securely with an SAP application server and, in an SSO design, to present a supported credential. It is the relevant layer to investigate when the desktop client cannot complete its SAP logon, even if the user has already signed in successfully to a browser-based SAP application.
The main design choice described for SAP GUI is Kerberos ticket-based SNC or X.509 certificate-based SNC. The credential type changes the dependencies and the likely failure points. Neither option turns the GUI connection into a SAML connection.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Kerberos over SNC
In a Kerberos design, the client obtains a ticket and the SAP service accepts it through SNC. Microsoft’s documented Kerberos procedure calls for Active Directory Domain Services (AD DS), an SAP service account, a service principal name (SPN) in the SAP/<SID> format, and SAP Basis configuration through SNCWIZARD, including Kerberos credentials and SPNEGO.
For the documented gateway scenario, prerequisites also include a Windows server with AD DS and an on-premises data gateway version of October 2024 or newer. That version requirement is specific to the gateway scenario in Microsoft’s procedure; it should not be generalized to every SAP GUI SNC deployment. The work also spans Microsoft Entra administration, SAP Basis, and Power Platform administration.
X.509 over SNC
With certificate-based SNC, the credential is an X.509 certificate rather than a Kerberos ticket. The implementation depends on certificate issuance and trust, certificate-to-user handling, and SNC client and server configuration. The available Microsoft guidance identifies X.509 as a supported SAP GUI credential option, but does not establish a universal certificate-enrollment method or a single certificate mapping procedure for every SAP landscape. Those details must be set for the organization’s SAP and certificate infrastructure.
Where does SAML fit in an SAP identity architecture?
SAML 2.0 is used for browser-facing SAP applications and federation configurations involving SAP BTP and IAS. Microsoft describes two common patterns: trust BTP directly with Entra ID, or use IAS as a SAML proxy between Entra ID and BTP or other SAP applications. IAS is a cloud authentication service that can proxy Entra sign-in to SAP cloud and on-premises applications.
Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Clear out junk files and repair common Windows errors3Fix the driver behind crashes, sound loss and screen glitchesIn these flows, the parties exchange SAML metadata and assertions. Configuration concerns include the identity provider and service provider trust, issuer and audience values, NameID and other claims, and the application’s role mapping. Microsoft describes Entra groups being asserted into IAS or BTP role collections. Use immutable group IDs rather than display names when designing claims and role mappings: display names can change, while the identifier is intended to remain stable.
Microsoft also notes that OIDC is a newer solution than SAML, which is a well-established industry standard. That observation does not make OIDC a drop-in option for SAP GUI. Select a federation protocol according to the supported client and service flow; the SAP GUI desktop path described here remains an SNC path using Kerberos or X.509.
How do Kerberos, X.509, and SAML compare?
Choose by the client and connection being secured, not by which protocol is most familiar to the identity team. The table summarizes the roles and dependencies Microsoft’s guidance establishes.
| Design | Primary client or use | Credential | Core dependencies | Typical failure domain | Admin teams |
|---|---|---|---|---|---|
| Kerberos over SNC | SAP GUI and other ticket-capable clients | Kerberos ticket | AD DS, service account, SPN, SNC and Kerberos configuration | DNS or SPN resolution, ticket issuance, SNC names, time synchronization | AD and SAP Basis |
| X.509 over SNC | SAP GUI with Secure Login components | X.509 certificate | Certificate issuance and trust, plus SNC client and server configuration | Certificate chain, user mapping, expiration, SNC configuration | PKI and SAP Basis |
| SAML federation | Browser, BTP, IAS, and web applications | Signed SAML assertion | Entra enterprise application, metadata, IAS or BTP trust, claims | Issuer or audience mismatch, NameID or claim mapping, metadata, role assignment | Entra, IAS/BTP, and application teams |
The “primary client” column is the key distinction: SAML is not an alternative row for desktop SNC. A browser application can use SAML while a user connecting through SAP GUI uses Kerberos or a certificate. The choice between those SNC credentials is an architecture decision driven by the organization’s directory, PKI, client, and SAP Basis arrangements; the available guidance does not establish one as universally preferable.
In practice, Kerberos and X.509 put operational weight in different places. Kerberos centers on directory and service identity: the SAP service account and SPN must correspond to the service users are reaching, and the ticket must be usable by the client and accepted by the SAP-side configuration. Certificate-based SNC shifts more of the lifecycle to issuance, trust distribution, certificate-to-user mapping, and renewal. Neither is automatically simpler; compare the expertise and infrastructure already available to the teams that will own the deployment.
SAML is different in kind, not merely a third credential choice. It carries a signed assertion in a federation flow between browser-oriented parties. Its metadata and claims do not configure an SNC connection, and a certificate used to sign SAML assertions is not interchangeable with an X.509 user credential used for SNC. The word “certificate” can appear in both architectures, but the certificate’s purpose and relying parties differ.
How should an organization separate the two SSO implementation paths?
Keep independent design records and operational runbooks for GUI SNC and browser federation. This makes ownership clear and prevents a successful test of one route from being treated as proof that the other is complete.
For SAP GUI, document SNC and the credential path
- Identify the client SNC library and the SNC name used for the connection.
- Record whether the design uses Kerberos/SPN or X.509 trust, including the relevant credential and user-mapping arrangements.
- Track the SAP profile parameters and SAP Basis configuration associated with the connection.
- For the Kerberos procedure described by Microsoft, document the AD DS environment, SAP service account,
SAP/<SID>SPN, and the Basis steps performed throughSNCWIZARD, including Kerberos credentials and SPNEGO.
For browser, BTP, or IAS, document federation and authorization
- Keep the SAML metadata and record the issuer, audience, NameID format, and claims expected by each relying party.
- Document whether BTP trusts Entra ID directly or uses IAS as a SAML proxy, and record the trust relationships on the involved systems.
- Specify how Entra groups map to IAS or BTP role collections. Prefer immutable group IDs in the claim and mapping design.
- Record the role assignment and Conditional Access arrangements that apply to the browser sign-in path.
These lists describe different protocol responsibilities, not a required product sequence. For the gateway-based Kerberos procedure, Microsoft specifically lists Entra ID, SAP Basis, and Power Platform administrators among the roles needed to implement it. Assign clear owners for each dependency before troubleshooting a cross-team failure.
Recommended Free Tools
A practical planning sequence is to name the user experience first, then the client, then the credential path. For example, “SAP GUI desktop access to an ABAP server” leads to SNC and a decision between Kerberos and X.509. “Browser access to a BTP application” leads to federation design, trust metadata, claims, and role collections. This small distinction helps prevent a project from treating one broad goal—single sign-on—as if it implied one protocol for every SAP client.
Before implementation, agree on who owns each identity object and change. The directory team may own the AD DS service-account and SPN work; SAP Basis owns SNC settings and SAP-side configuration; PKI owners handle certificate issuance and trust for an X.509 design; Entra, IAS/BTP, and application owners handle SAML trust, claims, and authorization. The documented gateway scenario adds Power Platform administration. Put handoffs and test responsibilities in the runbook so that a failure is routed to the team responsible for the failing layer.
How do you troubleshoot SAP GUI SSO when browser SAML works?
Treat the browser result as evidence only about the browser federation route. It does not confirm that the GUI has an SNC library, that the correct SNC name is used, or that Kerberos or certificate trust is working. Diagnose the failing route from the client toward the SAP service, then check its credential-specific dependencies.
- Confirm which client and route failed. Establish whether the user is signing in through a browser-based SAP application or through SAP GUI to an ABAP application server. Record the client, target connection, time, and exact error rather than treating every SAP SSO failure as a SAML problem.
- Check the GUI SNC configuration. Review the SNC library, configured SNC name, SAP profile settings, and the SAP Basis configuration for the affected connection. A mismatch or missing configuration in this layer can prevent GUI SSO regardless of a successful browser sign-in.
- Follow the credential branch in use. For Kerberos, verify the AD DS and service-account/SPN design, including the expected
SAP/<SID>SPN and the Kerberos/SPNEGO setup. Check the ticket and name-resolution path, since DNS/SPN issues and time synchronization are identified failure areas. For X.509, check the certificate chain, trust, expiry, user mapping, and SNC setup. - Check team ownership and recent changes. Kerberos issues may require both directory and SAP Basis administrators; certificate issues may involve PKI and SAP Basis. Use the runbook to identify whether a credential, name, trust, or profile change occurred, rather than editing the browser SAML configuration as a first response.
- Test browser federation separately if that path is also affected. For a browser or BTP issue, inspect SAML metadata, issuer and audience, NameID and claims, IAS trust, role collections, and Conditional Access. Do not infer from a GUI result that these SAML values are correct—or vice versa.
Keep the two test outcomes separate in incident notes: “browser SAML succeeds” and “GUI SNC succeeds” are distinct results. If one succeeds and the other does not, investigate the path that failed instead of changing a working protocol configuration without evidence.
Rank #2
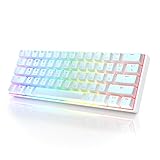
- ✅ PREMIUM OPTICAL SWITCHES: The GK61 comes equipped with Optical mechanical switches that deliver ultimate performance and reliability, designed for enduring and intense usage.
- ✅ CUSTOMIZABLE RGB LIGHTING: Experience a vivid spectrum of 16.8 million colors with twenty adjustable backlight patterns using the included software, letting you tailor the multicolor RGB system to your preference.
- ✅ TACTILE: Offers tactile responsive feel for both typing and gaming; utilized by some of the world's elite gamers for optimal performance.
- ✅ REMOVABLE TYPE-C CABLE: Features a 5FT/1.5M Type-C to Type-A USB cable that can be detached for your convenience, providing a consistent connection with your devices.
- ✅ SMOOTH STABILIZERS: With pre-lubricated stabilizers, enjoy solid gaming without wire rattle, for a seamless experience.
When the failure is limited to Kerberos, narrow the investigation to ticket acquisition and service identification before changing federation settings. Confirm that the user is reaching the intended SAP service name, that the expected SAP/<SID> SPN is associated with the service account, and that the SNC names and Kerberos/SPNEGO configuration agree across client and server. DNS/SPN resolution and time synchronization are relevant checks because errors in either can disrupt ticket use. If the failure is limited to certificate-based SNC, check whether the certificate is valid and trusted, whether the intended SAP user mapping is in place, and whether client and server SNC settings align.
For a browser-only failure, reverse the logic: validate the federation trust and the authorization path rather than the SAP GUI SNC library. An accepted SAML assertion is not by itself proof that the user has the intended application role. Check the assertion’s issuer, audience, NameID and group claims, then verify that the group-to-role collection mapping and assignment are correct. This distinction is especially useful when sign-in succeeds but the user still cannot access a BTP application.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What should administrators plan for when SAML certificates expire?
Certificate rollover is a lifecycle task for SAML federation and should be tracked separately from day-to-day user provisioning. Microsoft says the initial Entra enterprise-application certificate used to sign SAML assertions has a default validity period of three years. That is the stated default for the initial signing certificate, not a guarantee about every certificate or renewal schedule.
Microsoft’s guidance says the replacement certificate must be updated in each relying party before expiry. For IAS, the metadata is imported rather than dynamically retrieved, so a new signing certificate is not automatically reflected in dependent systems through a live metadata lookup. Maintain an owner, a renewal date, a list of relying parties, and an update-and-validation procedure for each dependent trust. Certificate maintenance for this browser federation path is distinct from certificate-based SNC used for SAP GUI: a SAML signing certificate does not by itself configure the GUI’s X.509 credential path.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →For a SAML certificate rotation, the operational sequence is to identify the relying parties that trust the current signing certificate, coordinate the replacement before it expires, update imported metadata or certificate configuration where required, and validate the affected browser sign-in and role mapping. Avoid assuming that updating Entra alone completes a rollover when a relying party uses imported metadata.
Do not merge certificate inventories just because both paths may involve X.509 material. The SAML signing certificate is trusted by federation relying parties to validate signed assertions; an SNC client certificate serves a different authentication path and has its own trust and mapping requirements. Give each certificate a recorded purpose, owner, dependent systems, expiry date, and validation test. A rollover plan that checks only the Entra signing certificate will not renew or validate a separate certificate-based GUI credential.
What should you decide before starting?
Start with the target client and the sign-in experience users need. If the target is desktop SAP GUI, plan an SNC design and select Kerberos or X.509 based on the available directory, PKI, client, and SAP Basis capabilities. If the target is browser-based SAP, BTP, or IAS federation, design the SAML or supported browser protocol trust, claims, and authorization mapping.
- Do not design SAML assertion handling as a substitute for SNC in the SAP GUI connection.
- Do not use a successful browser sign-in as the acceptance test for SAP GUI SSO.
- Do not use a working GUI Kerberos logon as proof that SAML metadata or BTP role mapping is valid.
- Plan certificate expiry and rollover for SAML trusts and for any separate certificate-based SNC arrangement according to their own owners and dependencies.
Frequently Asked Questions
Can I use Microsoft Entra SAML directly with SAP GUI?
No. Microsoft’s SAP identity guidance identifies SAP GUI as using X.509 or Kerberos tickets. SAML is for browser-facing federation flows such as BTP and IAS; it does not replace SNC in the GUI connection.
Why does SAP GUI need SNC if Entra ID is already my identity provider?
An identity provider and a client connection protocol serve different roles. SAP GUI needs a supported credential and security layer for its connection to the ABAP server; SNC provides that layer, using Kerberos tickets or X.509 credentials in the documented options.
Should SAP GUI SSO use Kerberos or an X.509 certificate?
There is no universally preferable choice established here. Kerberos depends on AD DS, service-account and SPN design, and SAP Basis SNC configuration. X.509 depends on certificate issuance and trust, user mapping, and SNC client/server configuration. Choose based on the directory, PKI, client, and SAP Basis capabilities your organization can support.
Is SAML only for Fiori, BTP, and browser logons?
The relevant distinction is client type: Microsoft describes SAML or OIDC for browser-based clients and X.509 or Kerberos tickets for SAP GUI. SAML is used in browser-facing SAP federation, including BTP and IAS patterns, rather than as a direct SAP GUI SNC credential.
How do I troubleshoot an SAP GUI SSO failure when browser SAML works?
Treat the browser success as evidence about the browser route only. Check the GUI SNC library, SNC name, SAP profile and Basis configuration, then investigate the selected credential: AD DS, SPN, ticket/name resolution and time for Kerberos; certificate chain, trust, expiry and user mapping for X.509.
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchDoes Entra ID replace Active Directory for Kerberos SAP GUI SSO?
Not in the Kerberos procedure described by Microsoft: it lists Active Directory Domain Services as a prerequisite. Entra ID may participate in the broader identity architecture, but the procedure still requires the AD DS and SAP service-account/SPN elements for the Kerberos path.
Can I use OIDC instead of SAML for SAP GUI?
OIDC is a browser-facing federation option, not an SAP GUI SNC credential. Microsoft distinguishes browser clients, which can use SAML or OIDC, from SAP GUI, which uses Kerberos tickets or X.509.
Do SAML group claims automatically give SAP users access to every BTP role?
No. Claims carry identity or group information; the application-side role collection mapping and assignment determine what access follows. Verify the group-to-role mapping for the target BTP or IAS configuration rather than assuming that a group claim alone grants a role.
Does the October 2024 gateway version requirement apply to every SAP GUI SNC setup?
No. Microsoft lists an on-premises data gateway version of October 2024 or newer for the documented gateway scenario. That specific prerequisite should not be generalized to every SAP GUI SNC deployment.
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Repair Windows errors before they cause bigger problemsFix Now →Does updating the Entra SAML certificate automatically update IAS?
Not when IAS relies on imported metadata as described in Microsoft’s guidance. Plan to update the dependent trust before expiry and validate the affected browser sign-in; do not assume a live metadata refresh.
The Bottom Line
Bottom line: Microsoft Entra ID can support both SAP browser federation and broader identity management, but SAP GUI desktop SSO uses SNC with Kerberos or X.509—not a direct SAML assertion. Design, assign owners, and troubleshoot those paths separately.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

