Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallWhen you proxy a website hostname through Cloudflare, visitors connect to Cloudflare first, and Cloudflare forwards their requests to your host. That changes the DNS answer, what your origin server sees as the network connection, and how HTTPS is handled. Cloudflare can also apply caching and security rules on the route, depending on your configuration.
1. DNS points visitors to Cloudflare, not directly to your host
For a proxied A, AAAA, or CNAME record, DNS returns Cloudflare anycast addresses instead of the origin server’s address. The visitor’s web request then passes through Cloudflare before it reaches the origin. With a DNS-only record, DNS returns the underlying target and the HTTP proxy is bypassed. See Cloudflare’s proxy-status documentation.
As an Amazon Associate I earn from qualifying purchases.
This distinction applies to supported web traffic, not every DNS record: MX and TXT records cannot be proxied. Cloudflare’s standard proxy handles HTTP and HTTPS, so records for mail and services such as SSH, FTP, RDP, or game servers should remain DNS-only unless you use a separately suitable service. Cloudflare’s use-case guidance explains the supported and unsupported cases.
2. Your origin sees Cloudflare as the network peer
A proxied request reaches your origin from a Cloudflare IP address, rather than directly from the visitor’s source address. Cloudflare supplies the visitor IP in headers including CF-Connecting-IP and X-Forwarded-For. If your application, logs, geolocation, authentication, or rate limits need the visitor’s address, configure them to use forwarded information safely. See Cloudflare’s HTTP header reference and its guidance on proxy use cases.
#1 Best Overall

- VLAN Network Segregation: This router includes five preconfigured VLANs that isolate IoT devices, guest users, and work systems into separate, secure networks. Each LAN port and every WiFi SSID can be assigned to a VLAN, giving you complete control over how traffic flows inside your home.
- Dual VPN Client and Server Support: The router works as both a VPN client and a VPN server, supporting OpenVPN, IPsec, and WireGuard. You can route selected VLANs through a VPN while keeping others on your regular ISP connection, giving each device group the exact level of privacy it needs.
- Full WiFi 6 on Both Bands: With dual-band WiFi 6 support, the router delivers modern wireless performance across 2.4GHz b/g/n/ax and 5GHz a/n/ac/ax. It improves capacity, stability, and speed while remaining compatible with older devices, making it ideal for busy homes with many connections. Wi-Fi Mesh is available after firmware update.
- High-Performance Hardware Architecture: Powered by the IPQ6000 quad-core ARM processor at 1.2GHz, along with 128MB flash, 256MB RAM, and hardware NAT acceleration, the router handles multitasking, streaming, VPN traffic, and VLAN isolation smoothly without slowing your network.
- Flexible and Powerful Parental Controls: You can use trusted services like OpenDNS, CleanBrowsing, and Cloudflare for filtering, then add custom block lists, allow lists, and schedules. The router includes defenses against common bypass attempts, letting families create rules that match each user. Best of all, it's subscription free!
Your origin firewall also needs to allow Cloudflare’s published IP ranges; otherwise it may block requests arriving through the proxy. Cloudflare publishes those ranges at Cloudflare IP addresses. If a third-party API or webhook integration checks the apparent source IP and requires the origin address, it may stop working when requests arrive through Cloudflare instead.
3. HTTPS ends at Cloudflare and starts again to the origin
Cloudflare terminates the visitor’s TLS connection, then establishes a separate connection to the origin. The origin therefore does not receive the visitor’s client certificate as part of its own TLS handshake. If your application relies on client certificates, account for this separate TLS boundary in its design. Cloudflare also adds or changes request headers, so the proxy is an active request-processing hop—not merely a DNS lookup change. Details are in Cloudflare’s proxy use-case documentation and its HTTP header reference.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What the proxy can—and cannot—do
Cloudflare says proxying can hide the origin address from ordinary DNS answers and allows configured features such as DDoS protection, caching, and a web application firewall to act on traffic. In its origin-protection documentation, last updated October 2, 2026, Cloudflare says: “Proxy records (when possible): Set up proxied (orange-clouded) DNS records to hide your origin IP addresses and provide DDoS protection.” Read Cloudflare’s origin-protection guidance.
Free tools Windows power users keep installed
One-click scans. No signup required.
Rank #2
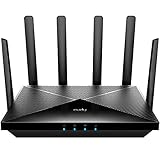
- Lightning-fast Qualcomm Snapdragon SDX62 5G NR SA / NSA Modem Inside . The Cudy P5 supports 5G NR downlink speeds of up to 2.5 Gbps and 4G LTE downlink speeds of up to 1 Gbps. Wide spectrum bandwidth accelerates internet speed and reduces network latency for premium and time-sensitive mobile broadband services.
- Qualcomm IPQ5018 WiFi 6 SoC. 1 GHz Dual-core ARM Cortex-A53 CPU High Capacity 802.11ax SoC, delivers super fast dual band Wi-Fi with speeds of up to 2402 Mbps on the 5 GHz band and 574 Mbps on the 2.4 GHz band. Exceptional wireless performance enables online gaming and HD video streaming at the same time, while large files can be shared with multiple devices.
- Dual SIM and WAN Failover Keep You Always On-internet. Dual SIM slots provide redundancy and keep the device always online. Both SIM slots can be filled, you can choose whether to use SIM card 1 or SIM card 2, or auto select by Cudy. Set WAN/LAN port as WAN to enable Cudy use the landline internet from WAN, and 3G/4G connection works as a backup to provide a sustained and reliable internet connection for you.
- The replaceable cellular antenna interface provides a variety of installation possibilities. 4 x 5dBi cellular antenna and 2x5dBi WiFi antenna enhance the sensitivity of the router and improve the signal quality of 5G NR and Wi-Fi. At the same time, the cellular antenna is a detachable design. If you want to use an outdoor cellular antenna, the SMA connector also provides the possibility of an external cellular antenna.
- Multiple VPN Clients. With built-in PPTP/ L2TP / OpenVPN / WireGuard /IPsec/ Zerotier VPN, this 4G router can easily establish a connection to the VPN server to transport all your online data and traffic, securing it with its encryption at the same time. Compatible with 20 more DDNS providers, convenient to manage your remote cameras.
That DNS answer does not prove the origin is undiscoverable. A DNS-only record or another disclosure may reveal its address. Review records that point directly to the origin, and configure the origin firewall to accept Cloudflare traffic while restricting unwanted direct access where appropriate. Cloudflare’s published IP ranges are relevant to that firewall configuration.
Proxying does not mean every request or asset will be cached. What Cloudflare caches depends on the resource, response headers, and configuration. Origin Cache-Control directives can govern caching, while Cache Rules can augment or override origin directives or defaults. See How Cloudflare DNS works and Origin Cache Control.
Quick Recap
Before you proxy a hostname
- Confirm that the hostname serves HTTP or HTTPS and that Cloudflare should process its traffic.
- Check whether an application or third party needs to see the origin IP rather than Cloudflare’s address.
- Allow Cloudflare’s published IP ranges through the origin firewall, and configure the application to trust forwarded visitor-IP headers appropriately.
- Review TLS settings, especially if the origin expects a client certificate from the visitor.
- Keep mail and non-HTTP service records DNS-only unless you have a separately suitable service for them.
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




