The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →SIFT Workstation is a SANS-maintained collection of free, open-source incident response and forensic tools. You get started in one of three ways documented by SANS: download the prebuilt virtual machine (OVA), install SIFT on native Ubuntu 22.04, or install it in Ubuntu 22.04 under Windows Subsystem for Linux (WSL). After that, you use SANS’s cheat sheet and how-to guides to pick the right tool for your evidence. SIFT is a toolkit, not a one-click workflow. Protocol SIFT, an AI-related project, is separate experimental research and not part of the validated core.
What SIFT Workstation is
The SANS Institute describes it this way: “The SIFT Workstation is a collection of free and open-source incident response and forensic tools designed to perform detailed digital forensic examinations in a variety of settings.” Per the official SIFT Workstation page, it supports filesystem, network-evidence and memory analysis. Listed evidence formats include raw, AFF, EWF, split images, VMDK, VHD/VHDX and QCOW.
As an Amazon Associate I earn from qualifying purchases.
Named examples include Plaso/log2timeline (timelines), Volatility (memory), bulk_extractor, afflib, ClamAV and The Sleuth Kit, plus hundreds of additional tools. Not every tool suits every case, and the workstation does not validate your conclusions. You choose tools based on the evidence and the question you are answering.
Step 1: Choose how to run it
| Route | Best when | What SANS documents |
|---|---|---|
| VM appliance (OVA) | You can run a virtual machine and want an isolated, prebuilt environment | 8.81 GB download, shown as last updated 24 April 2026 when checked; requires logging in to or creating a SANS Portal account |
| Native Ubuntu | You already run, or want to dedicate, an Ubuntu 22.04 machine | Install Cast, then run the SIFT installer |
| Ubuntu on WSL | You work on Windows and want a Linux shell without a separate VM | Works on WSL 1 or WSL 2 per SANS; Ubuntu 22.04; elevated shell for installation |
SANS’s page does not give a CPU, RAM, disk or hypervisor compatibility matrix, and the 8.81 GB OVA size is a download size, not installed storage. Check current SANS guidance and your virtualization software’s documentation, and leave generous disk headroom because evidence images are large. The page also does not rank the routes or promise that every function behaves identically on each, including WSL 1 versus WSL 2.
#1 Best Overall

- Includes Tableau T356789iu Forensic Universal bridge, TC2-8-R2, TC4-8-R2, TC6-8, TC-USB3, TC7-9-9 and USB B Male to USB 19 Pin Header Cable
- The Tableau Forensic Universal Bridge is an integrated write-blocker that mounts in a drive bay of a forensic workstation and supports forensic acquisitions of SATA, USB 3.0, PCIe, SAS, FireWire 800, and IDE.
- Mounts in one 5.25” half-height drive bay
- Color LED indicators for “Write Block” or “Read/Write” mode visibility
- USB 3.0 host computer connection, Two SATA power connectors
Step 2: Install
Option A: the virtual machine
- Open the SIFT Workstation page and log in or create a SANS Portal account.
- Download the OVA.
- Import it into your hypervisor using that product’s OVA/OVF import function.
- Boot it and sign in with the default credentials shown on the SANS page. These are page-specific defaults; change them before exposing the VM to any network.
Option B: native Ubuntu 22.04
- Install Ubuntu 22.04.
- Download the latest Cast binary as directed on the SANS page.
- Run:
sudo cast install teamdfir/sift
Option C: Ubuntu 22.04 under WSL
- Install WSL on Windows and choose Ubuntu 22.04 as the distribution.
- Open the Ubuntu shell with elevated privileges for the installation.
- Install Cast as directed on the SANS page.
- Run:
sudo cast install --mode=server teamdfir/sift-saltstack
Installer instructions change over time, so compare these commands with the SANS page before running them.
Step 3: Use the cheat sheet as your task index
The SIFT Cheat Sheet (published 23 October 2025) is meant to help analysts find tools and techniques in the SIFT Workstation. Its subjects make a good beginner’s map:
Rank #2

- Backlit Interface - Device status, device information, logical unit (LUN) select, and bridge information are easily accessible
- Supports USB 1.0/2.0/3.0, Flash Drives, Mass Storage Drives, and any "bulk storage" drive
- Kit Includes - TP2 Power Supply with US-Style power cord, TC-USB3 USB 3.0 (A to B) cable, 6 foot length, Soft-Sided bag and Quick Start Guide
- Hardware-Based USB 3.0 Write Blocker
- Mounting evidence
- Recovering data
- Creating timelines
- Filesystem analysis
Start with the question (“What ran on this system, and when?” or “What is in this memory capture?”), find the matching section, then open the relevant tool’s documentation.
Free tools Windows power users keep installed
One-click scans. No signup required.
Step 4: Handle a disk image
For a disk image, begin with SANS’s article on mounting evidence image files. It describes mounting an image to reach the raw data without converting it first, and it covers read-only access. The SIFT page also links how-to guides titled “How To Mount a Disk Image In Read-Only Mode” and “How To Create a Filesystem and Registry Timeline.”
Rank #3

- TX2 Forensic Imager Kit Includes: TX2 Forensic Imager, TP8 Power Supply, US Power Cord, (x4) TC4-8-R4 Unified SATA/SAS Signal and Power Cable (Molex), (x2) TC-PCIE4-8 PCIe Adapter Cable, 8", (x2) TCA-USB3-AC USB 3.0-A to USB 3.1-C Cable Adapter, Velcro Cable Ties (TPKG-VCT-5), Microfiber Cloth (TPKG-CLOTH), Quick Ref Guide
- LIGHTNING-FAST PROCESSING AND IMAGING: Powered by parallel hash verification and concurrent imaging, the TX2 is up to 3.8x faster than its predecessor. Capture and verify evidence in record time across multiple jobs.
- STREAMLINED RECONFIGURATION PROCESS: The TX2 makes it easy to pivot between tasks with a simplified reconfiguration process. Wipe, format, or encrypt all in one.
- UNLIMITED CONCURRENT OR CONSECUTIVE QUEUEING: The TX2's architecture is built for multitasking, allowing for unlimited concurrent or consecutive queueing. Stack jobs back-to-back or run several at once.
- OPTIMAL POWER ALLOCATION: The TX2 intelligently allocates power with dynamic resource assessment to maintain peak performance during heavy workloads. Its dynamic power management evaluates task demands in real time, ensuring every imaging job runs at optimal speed.
Keep the original evidence untouched and work on copies where your procedures require it. These are documented techniques, not proof that your handling meets any legal standard; that depends on your jurisdiction and organization’s procedures.
Step 5: Match the tool to the evidence
| Evidence or goal | Tools SANS names |
|---|---|
| Timeline of activity | Plaso/log2timeline |
| Memory capture | Volatility |
| Disk and filesystem structures | The Sleuth Kit |
| Carving strings, emails, and other artifacts from raw data | bulk_extractor |
| Malware scanning | ClamAV |
| Forensic image formats | afflib and related format support |
The table maps tools to the roles SANS lists them under; it is not a complete workflow for any case.
Rank #4
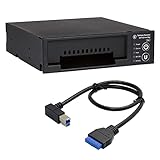
- Includes: Tableau T3iu Forensic SATA Drive Bay and 17" USB B to USB 19 Pin Header Cable
- The Tableau Forensic SATA Drive Bay is an integrated write-blocker that mounts in a drive bay of a forensic workstation and supports forensic acquisitions of 3.5” and 2.5” SATA hard drives.
- Mounts in one 5.25” half-height drive bay
- USB 3.0 host computer connection
- Read/write mode capability via internal DIP switch
Protocol SIFT is not core SIFT
SANS’s Protocol SIFT overview calls it an experimental research initiative exploring AI-assisted orchestration in the SIFT environment. It is separate and does not modify or replace the core workstation. SANS states: “Protocol SIFT has not been validated for forensic soundness or evidentiary reliability,” and it is not intended for evidentiary use in legal proceedings. Do not rely on its output in casework that may be tested in court.
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallOutdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchOptional: acquisition hardware
If you acquire evidence from physical drives, a USB forensic write blocker is a common accessory. It is not a SIFT component, SANS does not require or recommend a model, and this is a workflow suggestion rather than SANS guidance. Verify connector and drive compatibility before buying.
Quick Recap
Best Value
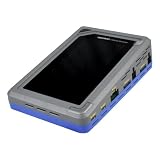
- TD4 Forensic Duplicator Kit includes: TD4 Forensic Duplicator, TP6 Power Supply, US Power Cord, (x3) TC4-8-R4 Unified SATA/SAS Signal and Power Cable (Molex), TC-PCIE4-8 PCIe Adapter Cable, 8" (Gen3 x4), TA-PCIE-PCIE4 Adapter (adapts between PCIe Gen2 and Gen3+), (x2) TCA-USB3-AC USB 3.0-A to USB 3.1-C Cable Adapter, Velcro Cable Ties (TPKG-VCT-5), Microfiber Cloth (TPKG-CLOTH), Quick Reference Guide
- Image data anywhere—native support for SATA, SAS,PCIe, and USB-C.
- Intuitive, seamless workflows—custom-built UI on color, touchscreen interface.
- Fast, efficient targeted acquisitions with local imaging capability.
- Wipe, format, and encrypt options for destination media.
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




