Recommended Free Tools
A password manager protects you mainly by making every account use a different, hard-to-guess password and by encrypting the vault that stores those credentials. With a well-designed cloud service, the vault can be encrypted on your device before syncing, limiting what the provider or a network observer can read. That protection has boundaries: phishing can still trick you, malware can capture secrets from an unlocked device, and weaknesses in the manager or its recovery process can still matter.
The right way to judge a password manager is therefore not “Is it safe?” in isolation. Ask which threats its encryption addresses, what happens when the vault is unlocked, how the account is recovered, and which protections you add around the manager and each important account.
As an Amazon Associate I earn from qualifying purchases.
What a password manager protects
A password manager gives you one primary vault to protect while it generates and stores separate credentials for your other services. Instead of inventing one memorable password and reusing it, you can create a long random password for every account and let the manager fill it when needed.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Scan for outdated or missing drivers - takes under a minute3Repair Windows errors before they cause bigger problemsThat separation limits the damage from a single website breach. If a password used on one shopping site is exposed, it should not also unlock your email, banking, or work account. The manager also removes the temptation to keep credentials in unsecured notes, documents, screenshots, or browser tabs.
#1 Best Overall

- Requires 3 "AAA" batteries (included)
- Unit auto-locks for 30 minutes after 5 consecutive incorrect PINs
The National Institute of Standards and Technology (NIST) recommends password managers for generating and storing long, complex passwords. Its consumer guidance quotes Digital Identity Program lead Ryan Galluzzo: “The worst password I can think of is ‘password’ or ‘12345.’”
A manager does not make the destination service secure. It improves the credentials you choose and the way you handle them. The website still needs to store passwords safely, offer multifactor authentication (MFA), and respond appropriately when accounts are attacked.
How vault encryption and syncing work
Encryption at rest
Your vault is normally stored as ciphertext rather than readable text. An attacker who obtains only that encrypted file must guess or otherwise obtain the key before seeing the entries. The primary password, device key, or both may be involved in deriving that key, depending on the product’s design.
Encryption at rest is most useful when an attacker steals a database, backup, lost phone, or cloud copy without controlling an active device. It does not mean the entries are encrypted at every moment. When you unlock the manager, the device must decrypt enough data to display and fill credentials.
End-to-end encryption and zero-knowledge designs
For a cloud-synced manager, end-to-end encryption aims to encrypt sensitive data on your device before it travels to the provider. A zero-knowledge design aims to ensure that the provider’s systems do not receive your primary password or a plaintext copy of the vault. In that model, the service can store and synchronize encrypted data without being able to routinely read the entries.
“Zero knowledge” describes a threat boundary and design goal, not a guarantee that every implementation is flawless. Bugs, weak key handling, compromised endpoints, unsafe recovery procedures, or a malicious update can create paths around the intended boundary. Check how a particular service documents encryption, key derivation, device authorization, and recovery rather than treating a label as proof.
Rank #2
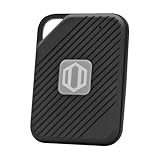
- Auto-Fill Feature: Say goodbye to the hassle of manually entering passwords! PasswordPocket automatically fills in your credentials with just a single click.
- Internet-Free Data Protection: Use Bluetooth as the communication medium with your device. Eliminating the need to access the internet and reducing the risk of unauthorized access.
- Military-Grade Encryption: Utilizes advanced encryption techniques to safeguard your sensitive information, providing you with enhanced privacy and security.
- Offline Account Management: Store up to 1,000 sets of account credentials in PasswordPocket.
- Support for Multiple Platforms: PasswordPocket works seamlessly across multiple platforms, including iOS and Android mobile phones and tablets.
Cloud convenience versus local-only storage
| Storage model | What it helps with | Trade-offs to plan for |
|---|---|---|
| Cloud-synced vault | Access across phones and computers; encrypted copies can be restored when a device is lost. | There are provider-held encrypted copies and possibly cached local copies. Account takeover, service outages, or a flawed implementation remain concerns. |
| Local-only database | Avoids routine provider-side storage and reduces dependence on a sync service. | You must synchronize devices yourself and maintain reliable, protected backups. Losing the database or its key can mean losing access. |
Cloud sync is not automatically less secure, and local storage is not automatically safer. The deciding details are the encryption design, the security of each endpoint, the quality of your backups, and whether you can recover without handing a human support agent excessive power.
What a password manager cannot protect against
Phishing and look-alike websites
A convincing fake login page can persuade you to enter a valid password or approve a sign-in. NIST notes that password length and complexity do not stop an attacker who tricks the user into sending the secret. A manager may refuse to autofill when the domain does not match, but that signal is not a substitute for checking the address and the context of the request.
Before entering a credential, open the service from a bookmark or a known app rather than a link in an unexpected message. Verify the domain, watch for unusual redirects, and treat urgent requests for a password, one-time code, or recovery action as suspicious. For compatible accounts, a passkey can provide phishing resistance because the cryptographic response is bound to the legitimate site; it still depends on a secure device and sound recovery process.
Malware, keyloggers, and malicious browser extensions
Malicious software on an endpoint can record keystrokes, read data exposed to other processes, alter a page, or operate the browser while you are signed in. A keylogger may capture your primary password as you type it. A compromised browser extension can potentially observe page content or interfere with autofill.
Vault encryption cannot make an infected operating system trustworthy. Keep the operating system, browser, manager, and security software updated; remove extensions you do not need; install applications only from trusted sources; and avoid unlocking the vault on a computer you do not control.
An unlocked or fully compromised device
Encryption mainly protects stored ciphertext. Once the vault is unlocked, the device has access to the information required to display or fill entries. An attacker who controls that device may use an existing session, capture a copied credential, or proxy actions through the endpoint without decrypting the stored file independently.
Rank #3

- NEVER FORGET A PASSWORD AGAIN: Almost every App. has a password, it is almost impossible to remember all the password log in details. This password book is specifically designed to help you create secure passwords and store all your passwords safely in one place. You will never forget your password log-in details again with this password keeper.
- ALPHABETICAL A-Z TABS FOR QUICK ACCESS: Alphabetical tabs design allows you to store your passwords alphabetically so you can find what you want faster, no more annoying searches!
- ANONYMOUS WITHOUT ANY TITLE: On the outside, this password notebook organizer looks just like those writing journals, there is no title listed on the cover, so no one would know it's a password book. But we still recommend keeping the internet password logbook in a safe place such as a locked drawer or a shelf full of books.
- THICK NO-BLEED PAPER: This 5.2" x 7.6" password book contains 74 sheets of thick 120gsm paper that resists ink smearing, say goodbye to those cheap password books that bleed ink!
- PREMIUM QUALITY & PERFECT MEDIUM SIZE: This password journal comes with a high-quality leatherette hardcover, an elastic band, pen holder, ribbon bookmarker, and inner accordion pocket. It measures 5.2 inches wide and 7.6 inches long, which is the perfect size for your needs.
Use an automatic lock timeout, require the device’s screen lock, and lock the vault before leaving a workstation. On a shared or borrowed computer, use a separate trusted device instead of installing or opening your vault there.
Social engineering and weak recovery processes
An attacker may impersonate you to support staff, persuade you to reveal a recovery code, or exploit a process designed to restore access after a lost primary password. NIST identifies social engineering and recovery procedures as security risks. A convenient reset that bypasses the primary secret can become the easiest route into the vault.
Read the recovery policy before you need it. Identify which recovery keys, devices, contacts, or support steps can restore access; store emergency material offline and separately from the vault; and do not disclose a recovery code in response to an unsolicited call or message.
Free tools Windows power users keep installed
One-click scans. No signup required.
Vulnerabilities in the manager itself
No product is immune to implementation mistakes. NIST includes exploitation of a vulnerability in an insufficiently secure password manager among authenticator threats. A flaw could affect the desktop app, mobile app, browser extension, synchronization service, update mechanism, or export function.
Updates are therefore a security control, not merely a feature upgrade. Prefer a manager with a documented vulnerability-response process, timely patches, transparent security documentation, and a way to revoke or review trusted devices.
Stolen credentials at the destination account
A manager can fill the right password into the right site, but it cannot stop a breach of that site’s database or an attacker who has already obtained the credential. Add MFA to email, financial, work, and administrator accounts. NIST recommends MFA and notes that some methods, including text-message codes, are more vulnerable than stronger alternatives.
Rank #4

- NEVER FORGET A PASSWORD AGAIN - Clever Fox password journal will help you create secure passwords and keep them safe and organized. This password book allows you to store all your passwords and other computer information in one place to find it easily.
- ALPHABETICAL A-Z TABS - Alphabetic tab system makes it easy to find any password you need. The book also has sections for most important passwords, wireless & email settings, software license information & additional notes.
- ELEGANT, SMART, PRACTICAL & SECURE PASSWORD ORGANIZATION - This password keeper book has been designed to be anonymous without an obvious title on the cover. For added security there is space to write hints instead of the password itself.
- POCKET SIZE & PREMIUM QUALITY - This internet address and password logbook with tabs comes in pocket size (4.0x5.5 inches). The password notebook has an eco-leahter hardcover, elastic band, pen loop, bookmark, pocket for notes, and thick 120gsm paper.
- 60-DAY MONEY-BACK GUARANTEE - We will exchange or refund your password organizer if you aren’t satisfied with your password organization for any reason. Reach out to us via message to refund your internet password logbook.
What different attacks look like
| Attacker’s position | What the manager’s encryption can do | What you must still control |
|---|---|---|
| Sees network traffic while you sync | End-to-end encryption can prevent credentials being sent in plaintext. | Use the current app, protect the account, and verify that the service really encrypts before upload. |
| Steals an encrypted cloud or backup file | Encryption can prevent immediate reading of the vault. | Use a strong primary secret, keep software patched, and monitor for provider or account incidents. |
| Gets your primary password through phishing | Vault encryption cannot distinguish a genuine sign-in from a user-entered secret. | Check domains, reject unexpected prompts, and use phishing-resistant authentication where supported. |
| Controls a device while the vault is unlocked | Stored ciphertext protection may no longer be relevant to the active session. | Secure the endpoint, use short lock timeouts, and remove malware. |
| Abuses support or account recovery | Encryption does not fix an overly permissive reset process. | Understand recovery, protect recovery material, and verify support requests independently. |
Set up a password manager with sensible protections
- Create a unique primary secret. Use a long passphrase that you have not used anywhere else. It protects the manager account and may be part of the vault-encryption key.
- Turn on MFA in the manager’s account settings. Look for a path such as Settings → Security → Multifactor authentication. Enroll more than one approved method only if you can protect the backups; save recovery codes offline.
- Generate a new password for every important account. Use the manager’s generator rather than modifying an old password. Change reused passwords first, prioritizing email, financial, work, administrator, and recovery accounts.
- Review autofill behavior. Require a domain match where the product offers that control, and disable automatic filling on pages or fields where it creates unnecessary exposure.
- Enable automatic locking. Set a short idle timeout and require the device lock or primary secret after the timeout. Lock manually before leaving the device.
- Update every component. Keep the manager app, browser extension, browser, operating system, and mobile platform current. Remove obsolete extensions and apps that can read page content.
- Plan recovery before an emergency. Record where recovery codes, emergency kits, or an encrypted export are stored. Test that you understand the process without weakening it.
- Protect the devices that can unlock the vault. Use full-disk encryption where available, a strong screen lock, reputable security updates, and separate user accounts on shared computers.
MFA, security keys, and passkeys
MFA protects the manager account even if its primary password is exposed. A second factor does not encrypt an already unlocked vault, but it can stop an attacker from signing in from a new device with only the password.
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallCrashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteA FIDO2/WebAuthn security key is an optional hardware factor for services that support those protocols. Some keys also support FIDO U2F and connect over USB or NFC. Confirm that the specific manager, operating system, and device connector support the key before buying it. Keep a second enrolled key or another approved recovery method in a secure location if losing the only key would lock you out.
Passkeys can resist many phishing attacks on compatible services because the device creates a cryptographic response for the legitimate origin. They do not remove the need to secure the device, protect the account used to synchronize passkeys, or maintain a safe recovery route.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.How to compare password managers
There is no evidence here that all managers are equally safe, and no universal product ranking. Compare the properties that define the threat boundary:
| Question | Why it matters |
|---|---|
| When and where is the vault encrypted? | Local encryption before sync limits what a provider or network observer can read. |
| What does “zero knowledge” mean in the implementation? | Look for details on key derivation, plaintext handling, logs, and administrative access rather than relying on the phrase alone. |
| Which MFA methods are supported? | FIDO2/WebAuthn or an authenticator app can provide stronger protection than a text message, depending on the service. |
| How does recovery work? | A recovery path that bypasses the primary secret may be convenient but can add a high-value attack target. |
| How are devices and sessions controlled? | Trusted-device lists, remote sign-out, automatic locking, and alerts help contain a lost or compromised endpoint. |
| Can you export or back up safely? | Exports support recovery and migration, but an unencrypted export becomes a concentrated credential file. |
| How are vulnerabilities handled? | Patch speed, security advisories, and a clear reporting process affect the risk after a flaw is discovered. |
| What works offline? | Offline access can be useful during outages but creates cached copies that need device protection. |
Backups, exports, and account recovery
A local-only vault requires dependable backups, while a cloud vault still benefits from a recovery plan for lost devices, outages, or account lockout. Store an encrypted backup on media that is not permanently connected to your computer. Protect the backup password or key separately; placing both in the same unprotected location defeats much of the benefit.
Be deliberate about exports. A CSV or other plain-text export may contain every credential in readable form. Create it only when needed, keep it offline during the task, delete temporary copies securely, and verify that the import succeeded before removing the original vault. Never email an unencrypted export to yourself.
Best Value
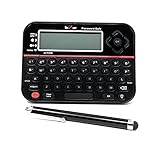
- Securely Remember All Your Passwords, Log-in's, User Names, ATM PIN Numbers and More
- Large Back-lit LCD Screen, QWERTY Keyboard - So Easy to Use
- Enter one PIN number and have access to 400 accounts. Search function included.
- Unit auto locks for 30 minutes after 5 consecutive incorrect PIN attempts
- Includes mini stylus for easier keypad entry
Recovery instructions differ by service. Before relying on a manager for all accounts, confirm whether losing the primary password is recoverable, which emergency contacts or devices are accepted, how long a recovery hold lasts, and whether support personnel can reset access. A design that cannot recover a forgotten primary secret may be safer against impersonation but less forgiving of user error.
What password strength can and cannot achieve
NIST’s 2025 consumer password page gives an illustrative estimate that a modern PC can attempt to decrypt 100 billion passwords per second. That is not a universal benchmark: the result depends on hardware, the password-hashing method, rate limits, and the attack conditions. It does show why short or common passwords are unsuitable for protecting a vault or an online account.
NIST’s Digital Identity Guidelines, SP 800-63B-4, state that “Many attacks associated with passwords are not affected by password complexity and length.” Phishing, keylogging, malware, and social engineering fall into that category. A unique random password remains valuable, but it is one layer rather than a complete defense.
Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Clear out junk files and repair common Windows errorsFree Scan →The scale of the surrounding problem is also broader than any one manager. NIST cites the Identity Theft Resource Center’s report of more than 3,000 data breaches in 2024, potentially exposing hundreds of millions of online accounts. That figure describes breaches generally, not breaches of password-manager providers.
What to do after a suspected compromise
- Use a clean, trusted device. If malware is possible, do not change credentials from the suspected endpoint until it has been assessed and updated.
- Secure the manager account first. Change the primary secret, revoke unfamiliar sessions or devices, and review MFA and recovery settings.
- Change the highest-impact passwords. Start with the email account that receives resets, then financial, work, administrator, and other accounts that can affect many services.
- Revoke active sessions and tokens. Password changes may not invalidate existing browser sessions, API keys, app passwords, or recovery links.
- Check for tampering. Review vault history, browser extensions, forwarding rules, payment details, and account notifications for changes you did not make.
- Preserve evidence and report appropriately. Record dates and alerts, contact the affected service through its official channel, and follow its breach or identity-theft guidance.
A password manager is most effective as part of a layered setup: unique generated credentials, encrypted storage, a protected manager account, patched and trustworthy devices, phishing-resistant options where available, and a recovery plan that you can execute without exposing the vault.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

