Free tools Windows power users keep installed
One-click scans. No signup required.
Start with your installed antivirus, then use Microsoft Defender Offline when you suspect persistence or rootkit behavior, and finish with an updated on-demand second-opinion scanner such as Malwarebytes or ESET. No product can promise detection of every remote-access trojan (RAT), and a clean quick scan is not proof that a machine is clean. RATs can install additional malware, steal keystrokes and browser data, send device information to an attacker, and maintain remote control while trying to evade security software.
What a RAT is and why a normal antivirus scan can miss it
A remote-access trojan is malware that gives an attacker some form of remote control over a device. Microsoft’s definitions describe trojans as programs that can download and install other malware, record keystrokes and websites visited, send device information to an attacker, and enable further compromise. Microsoft defines a backdoor as malware that provides malicious hackers with remote access and control. Some malware also includes evasion software that actively attempts to avoid security products.
As an Amazon Associate I earn from qualifying purchases.
That combination creates a practical problem: the scanner is looking at a moving target. A RAT may launch through a scheduled task, service, startup entry, stolen legitimate tool, or a component injected into another process. It may contact a command-and-control server only at certain times, encrypt its traffic, or disable a security process briefly while it runs. A quick scan examines fewer files and locations than a full scan, and a scan performed inside a running Windows session is operating in the same environment the malware is trying to influence.
For that reason, “my antivirus found nothing” answers only a narrow question: the product did not identify a threat with the signatures, reputation data, behavior rules, and scan scope available at that moment. It does not establish that there is no unauthorized account, persistence mechanism, altered system file, or attacker-controlled session.
#1 Best Overall
- [Package Offer]: 1 Pack USB Flash Drive 8GB Available in black.
- [Plug and Play]: No need to install any software, Just plug in and use it. The metal clip rotates 360° round the ABS plastic body which. The capless design can avoid lossing of cap, and providing efficient protection to the USB port.
- [Compatibilty and Interface]: Supports Windows 7 / 8 / 10 / Vista / XP / 2000 / ME / NT Linux and Mac OS. Compatible with USB 2.0 and below. High speed USB 2.0, LED Indicator - Transfer status at a glance.
- [Suitable for All Uses and Data]: Suitable for storing digital data for school, business or daily usage. Apply to data storage of music, photos, movies, software, and other files.
- [Warranty Policy]: 12-month warranty, our products are of good quality and we promise that any problem about the product within one year since you buy, it will be guaranteed for free.
The safest scanner sequence when you suspect a RAT
Use a layered process rather than repeatedly running quick scans. The order below moves from the least disruptive check to a scan that runs outside the ordinary Windows kernel, then adds an independent second opinion.
- Disconnect if active compromise is plausible. Unplug Ethernet and disable Wi-Fi or Bluetooth on the affected computer if you see unknown remote-control sessions, unexplained cursor movement, new accounts, or files being opened by someone else. Disconnecting limits what an operator can do while you investigate. Do not reconnect merely to download a scanner; use a known-clean device to obtain instructions or transfer trusted tools when possible.
- Update the resident antivirus. Install the latest engine and definitions, then run a full scan rather than a quick scan. Microsoft lists Defender Antivirus and Microsoft Safety Scanner among tools for detecting and removing trojans. A full scan takes longer because it checks substantially more locations and files.
- Run Microsoft Defender Offline for persistence or rootkit concerns. This is the key step when malware may hide from a running Windows session, has altered the shell, or survives ordinary restarts.
- Review the result after Windows starts again. Open Windows Security, choose Virus & threat protection, and open Protection history. Record the threat name, affected path, action taken, and whether a restart or manual remediation is requested.
- Run one updated on-demand second opinion. Malwarebytes or ESET can provide an independent detection engine and different cloud or behavioral reputation data. Update the scanner immediately before the scan and choose its deepest available scan mode.
- Contain accounts and evidence if access was unauthorized. From a known-clean device, change email, banking, password-manager, VPN, and administrator credentials. Revoke active sessions and rotate multi-factor authentication recovery codes where applicable. Preserve logs and suspicious files if an incident-response professional may need them.
CISA’s guidance on remote-access security is useful when an attacker may have obtained interactive access. A scanner can remove a file; it cannot tell you with certainty which credentials were copied before removal.
Microsoft Defender Offline: when and how to use it
Why an offline scan helps
Microsoft says that Defender Offline runs “from outside the normal Windows kernel so it can target malware that attempts to bypass the Windows shell.” Microsoft Support explains that the computer restarts into a scanning environment “without loading Windows, so any persistent malware has a more difficult time hiding or defending itself.” In practical terms, ordinary startup programs, user-session processes, and many persistence components are not running in their usual form while the scan examines the disk.
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Offline scanning is especially appropriate when a threat returns after removal, Windows Security cannot start normally, a rootkit is suspected, or the Windows shell behaves as if another person is controlling it. It is not a guarantee against every bootkit or firmware-level attack, and it does not replace credential containment or a full incident response.
Rank #2

- 10 Pack USB Sticks: 10 pieces of USB flash drives are fit for a variety of scenarios. Whether the flash drives USB are used as school supplies for high school students to backup data storaged in USB jump drives or music USB flash drive for car, zip drive can meet the basic storage needs. USB drive pack of 10 has a higher cost performance. USB flash drive pack of 10 is suitable for ordinary users with appropriate needs, but also for special groups such as companies, schools or other organizations that need a large number of U disks. In short, thumb drives can meet the needs of different customers.
- Swivel Design: With the 360° swivel design, all the ports of the thumb drives 10 pack can be hidden inside the metal casing. When needed, simply swivel the casing gently and the ports will automatically expose, making it convenient for you to insert and remove. This design is not only fashionable and beautiful but also more user-friendly, whether you'd like your flash drive for photos, flash drive for video storage, or memory sticks for computers. In addition, the swivel design can effectively protect the interface from damage and pollution, increasing the service life of the flash USB drive.
- Portability: The small hole on the thumbdrive USB is designed for lanyards, which is convenient to carry. Besides, the USB flash drive keychain can also be tied through the small hole to prevent loss. This design is very thoughtful and reflects the humanized design concept of the memorias USB flash drive.
- Plug and Play: You can use the computer storage flash drive immediately for data storage or backup without any additional installation after inserting it into the computer. This plug and play feature makes the laptop storage drive a very convenient external ssd. You can copy the required data files to the external drive at any time without worrying about computer system compatibility issues. In addition, the design of the external flash drive enables it to be quickly recognized by the system after being inserted into the computer. (NOTE: Please check if your device has a USB-A port before purchasing. If not, a USB-C hub is needed.)
- FAT32 format: The default system format for 8GB flash drive is FAT32. FAT32 USB flash drive is widely applicable, such as in televisions, DVD players, vehicles, printers, embroidery machines, etc. Be patient if you have problems with system recognition. It may take some time for initial recognition, but it will happen.
Start it from Windows Security
- Save open work and connect the computer to AC power. The process restarts the machine and can take longer than a normal scan.
- Open Windows Security.
- Select Virus & threat protection, then Scan options.
- Choose Microsoft Defender Antivirus (offline scan) and select Scan now.
- Approve the restart. Windows loads the Windows Recovery Environment and runs the scan before ordinary Windows starts.
- After the computer returns to Windows, open Virus & threat protection and Protection history to see detections, quarantine actions, and any remediation that failed.
If the offline option is missing, update Windows and Defender, verify that another security product has not disabled Defender, and check that you have administrator rights. On managed work or school computers, policy may hide the setting; contact the administrator rather than attempting to bypass that policy.
Create removable offline media when Windows cannot launch normally
Microsoft’s offline-media instructions specify a blank CD, DVD, or USB flash drive with at least 250 MB of free space. Creating the media can reformat the drive, so copy anything important from it first. An 8 GB USB flash drive is a practical search phrase when buying a small drive, but capacity alone does not guarantee that a particular computer will boot from it. Firmware settings, Secure Boot support, USB port behavior, and the drive’s partition layout also matter.
- Use a known-clean Windows computer to prepare the media.
- Insert a blank optical disc or an empty USB flash drive with at least 250 MB free.
- Follow Microsoft’s Defender Offline media-creation instructions and select the removable drive only after verifying its contents are backed up.
- On the suspect computer, open the one-time boot menu (the key varies by manufacturer) and choose the removable media.
- Allow the offline scan to complete, then remove the media before the next normal startup.
If the system refuses to boot the media, try another USB port, confirm that the media was created successfully, and check the manufacturer’s documented boot-menu and Secure Boot settings. Do not repeatedly change firmware settings on a business computer without approval; preserve its current configuration for the administrator or responder.
Recommended Free Tools
Choosing a second-opinion scanner
Malwarebytes
Malwarebytes is useful as an on-demand second opinion after the resident antivirus and, when indicated, Defender Offline. Its role is not to replace a maintained, real-time security product during normal use. Update its components, select the most comprehensive threat scan available, and review detections rather than automatically deleting every unfamiliar file. A legitimate remote-administration utility can be flagged as a potentially unwanted or dual-use program; verify ownership and business purpose before removal.
Rank #3
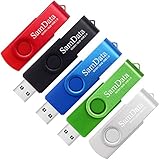
- [Package Offer]: 5 Pack USB 2.0 Flash Drive 8GB Available in 5 different colors - Black Blue Green Red Silver. The different colors can help you to store different content.
- [Plug and Play]: No need to install any software, Just plug in and use it. The metal clip rotates 360° round the ABS plastic body which. The capless design can avoid lossing of cap, and providing efficient protection to the USB port.
- [Compatibilty and Interface]: Supports Windows 7 / 8 / 10 / Vista / XP / 2000 / ME / NT Linux and Mac OS. Compatible with USB 2.0 and below. High speed USB 2.0, LED Indicator - Transfer status at a glance.
- [Suitable for All Uses and Data]: Suitable for storing digital data for school, business or daily usage. Apply to data storage of music, photos, movies, software, and other files.
- [Warranty Policy]: 12-month warranty, our products are of good quality and we promise that any problem about the product within one year since you buy, it will be guaranteed for free.
ESET
ESET is another independent on-demand option. It is valuable when you want a different vendor’s signatures, reputation service, and behavioral analysis after the first scanner reports a clean result. Run it with current updates and allow the scan to inspect archives and potentially unwanted applications if those choices are offered. As with any scanner, a clean result means only that no matching evidence was found in the examined scope.
Microsoft Safety Scanner
Microsoft Safety Scanner is a portable diagnostic tool that Microsoft lists for trojan detection and removal. Download a fresh copy for each investigation because its security intelligence is not a permanent replacement for Defender’s regularly updated protection. Run it with administrator privileges and note that the utility expires after a limited period, so an old copy should not be treated as current.
What independent test results actually tell you
AV-Comparatives’ Malware Protection Test 2026 reports separate offline detection, online detection, online protection, and false-alarm measures. The figures below are general malware-protection results, not a RAT-only leaderboard. They indicate how products performed across the test’s malware set and phases; they do not guarantee that a particular RAT family will be detected on your computer.
| Product | Offline detection | Online protection | How to interpret it |
|---|---|---|---|
| F-Secure | 98.6% | 99.98% | Highest offline and online figures among the products listed here in the 2026 report; still a general malware test. |
| Bitdefender | 97.6% | 99.94% | Strong results in both phases; not evidence of universal RAT coverage. |
| ESET | 96.4% | 99.93% | High general protection in the cited test and a reasonable independent second opinion. |
| Malwarebytes | 92.4% | 99.59% | Lower offline detection than the other listed products in this test, with high online protection. |
| Microsoft | 89.2% | 99.93% | Lower offline detection in this report but nearly the same online-protection result as ESET. |
The test also includes false-alarm measurements. A product that detects more samples but blocks legitimate software can create operational problems, so detection percentage should not be the only selection criterion. The report’s online and offline phases measure different conditions: an offline result reflects what the product recognized without the benefit of live cloud interaction, while online protection can use current reputation and network intelligence.
Rank #4

- Ultra-compact and portable contoured styling
- Share your photos, videos, songs and other files between computers with ease
- Protect your private files with included SanDisk SecureAccess software (Password protection uses 128-bit AES encryption and is supported by Windows Vista, Windows 7, Windows 8, Windows 10 and Mac OS X v10.6+ (Software download required for Mac, see official SanDisk Secure Access website for more details.))
- Store more with capacities up to 8GB (1 gigabyte (GB) = 1 billion bytes. Some capacity not available for data storage.)
These numbers should therefore shape, not replace, your workflow. Defender Offline is valuable because it changes the execution environment. A second-opinion scanner is valuable because it changes the detection engine. Neither role is captured by a single percentage.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Decision framework: which scan should you run?
| Situation | Best next action | Reason |
|---|---|---|
| No symptoms, routine check | Update the resident antivirus and run a full scan | Lowest disruption and appropriate for ordinary maintenance. |
| Repeated reinfection, altered browser or shell, suspected rootkit | Microsoft Defender Offline, then Protection history review | Runs outside the normal Windows kernel and startup session. |
| Resident antivirus is clean but suspicion remains | Updated Malwarebytes or ESET on-demand scan | Adds an independent engine and reputation data. |
| Windows will not start or cannot be trusted | Offline removable media from a known-clean computer | Allows scanning without relying on the installed Windows session. |
| Evidence of an active unauthorized operator | Disconnect networks, preserve evidence, change credentials from a clean device | Scanning alone cannot stop ongoing access or undo stolen credentials. |
Common failure modes and fixes
A quick scan is clean, but suspicious behavior continues
Run a full scan and then Defender Offline. Check Protection history, installed remote-administration software, startup entries, scheduled tasks, browser extensions, and new local accounts. A RAT may not be active during a short scan, so correlate scanner results with Windows event logs and account activity.
Defender Offline restarts but reports no result
Boot back into Windows, install pending Defender and Windows updates, and check Protection history. If the device is managed, ask the administrator whether policy or another endpoint product controls offline scans. Repeat from removable media if Windows itself remains untrusted.
A second-opinion scanner flags a legitimate tool
Do not whitelist it reflexively. Confirm the file’s publisher, installation source, digital signature, hash from a trusted inventory, and whether anyone authorized its use. Quarantine first when the tool is unexpected; restore only after verification.
Best Value

- 【What You Get】 1 pieces 8 GB small capicity bulk usb flash drives,which allow you to classify your files, music, pictures etc. Great choice for enhancing your Name's visibility as the pen drives can be printed on
The scanner cannot update
Do not reconnect a potentially controlled computer just to make an update work. Download the current tool or definitions on a known-clean device using the vendor’s official distribution method, transfer them with trusted removable media, and scan that media before use. If a corporate proxy blocks updates, involve the security administrator.
Malware is removed but accounts are still being accessed
Assume credentials may have been exposed. From a known-clean device, change passwords beginning with email and password-manager accounts, revoke sessions and application tokens, rotate recovery codes, and contact financial institutions if relevant. Review sign-in history for unfamiliar locations and devices.
The same RAT returns after cleanup
Look for persistence outside the obvious executable: scheduled tasks, services, startup folders, registry run keys, browser extensions, compromised administrator accounts, and vulnerable remote-access software. If you cannot establish a trusted state, back up only necessary personal documents, erase and reinstall Windows from trusted media, fully patch it, and restore data selectively. For business systems, involve incident response before wiping because destruction of evidence can hinder attribution and recovery.
How to improve the odds of detection
- Keep Windows, browsers, drivers, and security engines current before scanning.
- Use a standard account for daily work and reserve administrator access for deliberate tasks.
- Enable multi-factor authentication on email, cloud storage, and remote-access services.
- Review remote-desktop and remote-support software regularly; remove tools no one can explain.
- Keep offline or immutable backups so a cleanup decision does not become a data-loss emergency.
- Record scan dates, engines, detection names, file paths, and remediation actions. A timeline helps distinguish a one-time false positive from recurring persistence.
- Do not run several real-time antivirus products simultaneously. Use one resident product and add on-demand scanners only when needed.
When scanning is not enough
Escalate to a qualified incident-response professional when the computer stores regulated information, an attacker had administrator access, a business account was used, a firmware or boot compromise is suspected, or the RAT repeatedly reappears. Preserve the machine’s state where possible, document times and symptoms, and avoid logging into sensitive services from it. A professional can collect memory and disk evidence, identify lateral movement, and determine whether reimaging every related device is necessary.
For a personal computer with no sensitive data, a clean reinstall is often more reliable than endless scanning when you cannot explain the persistence. Use installation media created on a trusted machine, apply updates before restoring applications, and change passwords from another clean device. Restore documents only after checking them with updated security tools.
Bottom line for RAT detection
There is no universal “best RAT scanner” established by the available evidence. The most defensible approach is layered: full scan with an updated resident antivirus, Microsoft Defender Offline when persistence or rootkit behavior is possible, and one updated second-opinion scanner such as Malwarebytes or ESET. The AV-Comparatives 2026 figures provide useful general malware context, but they are not a promise of RAT-family detection. Treat continued unauthorized access as a security incident, not merely a failed scan, and contain networks and credentials before attempting repeated cleanup.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.
Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Repair Windows errors before they cause bigger problems3Scan for outdated or missing drivers - takes under a minute
