Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →The most direct alternative is a VPN server that you control at home. Run WireGuard on your home router or another always-on host, then connect your phone, laptop, or travel router as a client. Use a full-tunnel route (AllowedIPs = 0.0.0.0/0,::/0) when every internet connection should leave through home, or advertise only your home subnet for split tunneling. OpenVPN provides the same home-server model with a more traditional configuration. A travel router is the practical choice when several devices, including televisions or game consoles, must share the tunnel. ZeroTier can also act as a full-tunnel gateway, but you must configure default-route advertisement and NAT yourself.
These designs make websites see the public IP of your home connection rather than the network you are visiting. They do not create extra bandwidth: download speed and responsiveness remain limited by your home connection’s upload capacity, the distance between you and home, and the reliability of the local network.
As an Amazon Associate I earn from qualifying purchases.
What a Tailscale exit node does
An exit node is an internet gateway on your private network. When a traveling device selects it, traffic that is not destined for the private mesh is sent to that device first and then out through its local internet connection. Tailscale describes the feature as routing all traffic through a specific device on your network. That is useful on untrusted café or hotel Wi-Fi and when you need services that are available only from your home country.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
The same result can be built without Tailscale’s control plane. The essential pieces are a reachable server at home, a VPN client at your current location, a route that determines which traffic enters the tunnel, and firewall/NAT rules that let the home server forward that traffic to the internet. A full tunnel changes the apparent public address for every application. A split tunnel sends only selected home networks through the VPN while ordinary web traffic uses the local connection.
#1 Best Overall
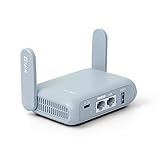
- 【DUAL BAND AX TRAVEL ROUTER】Products with US, UK, EU Plug; Dual band network with wireless speed 574Mbps (2.4G)+2402Mbps (5G); 2.5G Multi-gigabit WAN port and a 1G gigabit LAN port; USB 3.0 port; Wi-Fi 6 offers more than double the total Wi-Fi speed with the MT3000 VPN Router.
- 【VPN CLIENT & SERVER】OpenVPN and WireGuard are pre-installed, compatible with 30+ VPN service providers (active subscription required). Simply log in to your existing VPN account with our portable wifi device, and Beryl AX automatically encrypts all network traffic within the connected network. Max. VPN speed of 150 Mbps (OpenVPN); 300 Mbps (WireGuard). *Speed tests are conducted on a local network. Real-world speeds may differ depending on your network configuration.*
- 【OpenWrt 21.02 FIRMWARE】The Beryl AX is a portable wifi box and mini router that runs on OpenWrt 21.02 firmware. It supports more than 5,000 ready-made plug-ins for customization. Simply browse, install, and manage packages with our no-code interface within Beryl AX's Admin Panel.
- 【PROTECT YOUR NETWORK SECURITY】Our pocket wifi, unlike other vulnerable portable wifi hotspot for travel purposes supports WPA3 protocol–Preventive measures against password brute-force attacks; DNS over HTTPS & DNS over TLS–Protecting domain name system traffic and preventing data eavesdropping from malicious parties; IPv6–Built-in authentication for privacy protection, eliminating the need for network address translation.
- 【VPN CASCADING AT EASE】Surpassing the mediocre performance of most VPN routers for home usage, the Beryl AX is capable of hosting a VPN server and VPN client at the same time within the same device, enabling users to remote access local network resources like Wi-Fi printers or local web servers, and accessing the public internet as a VPN client simultaneously.
Compare the practical alternatives
| Approach | Devices covered | Routing choices | Home reachability | Administrative work | Best fit |
|---|---|---|---|---|---|
| WireGuard server at home | Each device with a WireGuard client, or every device behind a VPN travel router | Full tunnel or selected home prefixes | Usually a public IP; port forwarding is needed when the server sits behind another router | Key management, routes, firewall and NAT | People who want a lean, standards-based tunnel and control of the endpoint |
| OpenVPN server at home | Per-device clients or a travel router running the client | Full tunnel or split tunnel, depending on server and client configuration | Public IP and, in common home-router layouts, port forwarding | Certificate/profile distribution plus firewall and NAT | Networks that already use OpenVPN or need its broad client support |
| VPN client on a travel router | Phones, laptops, streaming boxes and other devices connected behind that router | One tunnel for the router’s downstream network; policy-based exceptions depend on firmware | Uses whichever home server you choose; the travel router itself must reach the VPN endpoint | Configure once on the router instead of every downstream device | Families, work trips or hotel rooms with several devices, including devices that cannot install a VPN app |
| ZeroTier full-tunnel gateway | ZeroTier members, or devices behind a gateway configured to route for them | Advertised default route or narrower private routes | The gateway can be a home host, Raspberry Pi or small VPS; internet forwarding and NAT are your responsibility | Route advertisement, gateway forwarding, NAT and member authorization | Administrators who already operate ZeroTier and are comfortable managing the gateway |
No authoritative comparison in the available documentation establishes a universal throughput or latency winner among these options. The architecture and your two internet connections matter more than a product label.
Option 1: Run WireGuard directly at home
WireGuard is usually the simplest direct replacement when you control the home router or an always-on computer. The home device terminates encrypted sessions, forwards permitted traffic, and performs NAT so replies return through the tunnel.
Check the home connection first
- Public reachability: The home-side WireGuard server generally needs a public IP address. If your internet provider uses carrier-grade NAT, inbound connections may not reach your router.
- Forwarding: If the server is behind an upstream modem/router, forward the WireGuard UDP port to the server and permit it in the home firewall.
- Stable endpoint: A changing public address requires a hostname or another way to update the client’s endpoint. Confirm that your router firmware supports this before relying on the setup.
- Upstream capacity: Every byte downloaded while traveling must first be uploaded from home. A slow or heavily used home uplink will be the bottleneck.
Create the home server
- Install the WireGuard server package on a supported home router or an always-on host. GL.iNet documents routers with pre-installed WireGuard Server and Client functions; other platforms expose equivalent server settings.
- Create a private key for the server and a separate key pair for each traveling client. Never reuse one client’s private key on several devices.
- Assign an internal tunnel address to the server and to each peer. Keep this tunnel network separate from your home LAN subnet.
- Add the server’s listening UDP port to the home firewall and forward that port from the upstream router when necessary.
- Enable forwarding from the WireGuard interface to the home WAN interface and add a masquerade/NAT rule. Without NAT, the remote device may connect to the server but internet replies will not know how to return.
- For private-resource access, permit only the home LAN prefixes you actually need. For internet egress, permit forwarding from the tunnel to the WAN while retaining normal firewall protections for the rest of the home network.
Configure a phone or laptop for a full tunnel
Import a peer profile into the WireGuard application on the traveling device. The important route setting is:
AllowedIPs = 0.0.0.0/0,::/0This tells the client to send both IPv4 and IPv6 traffic through the tunnel. Include an endpoint hostname or address and the server’s UDP port, a client private key, the server public key, and a persistent keepalive if the local network drops idle UDP mappings. The exact field names vary by client, but the values have the same meaning.
When only home resources should use the VPN, replace the default route with your actual home prefixes, such as your LAN subnet and the WireGuard tunnel subnet. GL.iNet’s documentation illustrates this distinction: a default route sends all traffic through the tunnel, while a LAN-only prefix implements restricted access.
Rank #2
- 【DUAL BAND WIFI 7 TRAVEL ROUTER】Products with US, UK, EU, AU Plug; Dual band network with wireless speed 688Mbps (2.4G)+2882Mbps (5G); Dual 2.5G Ethernet Ports (1x WAN and 1x LAN Port); USB 3.0 port. Enjoy gaming and streaming across up to 120 devices.
- 【HIGH SPEED VPN CLIENT & SERVER】Max. VPN speed of 1100 Mbps (WireGuard); 1000 Mbps (OpenVPN-DCO). OpenVPN and WireGuard are pre-installed, compatible with 30+ VPN service providers (active subscription required). Simply log in to your existing account with our portable wifi device, and Beryl 7 automatically encrypts all network traffic within the connected network. *Speed tests are conducted on a local network. Real-world speeds may differ depending on your network configuration.*
- 【OpenWrt 21.02 FIRMWARE】The Beryl 7 (GL-MT3600BE) is a high-performance Wi-Fi 7 travel router, built with OpenWrt 21.02 (Kernel 5.4.281) for maximum customization and advanced networking capabilities. With 512MB storage, total customization with open-source freedom and flexible installation of OpenWrt plugins.
- 【PERFECT PORTABLE WIFI ROUTER FOR TRAVEL】The Beryl 7 is an ideal international wireless portable wifi travel router. With its mini size and travel-friendly features, the pocket Wi-Fi router is the perfect companion for travelers in need of a secure internet connectivity on the go. portable wi-fi for traveling, hotels or cruise ships.
- 【PROTECT YOUR NETWORK SECURITY】Our pocket wifi, unlike other vulnerable portable wifi hotspot devices for travel purposes supports WPA3 protocol–Preventive measures against password brute-force attacks; DNS over HTTPS & DNS over TLS–Protecting domain name system traffic and preventing data eavesdropping from malicious parties; IPv6–Built-in authentication for privacy protection, eliminating the need for network address translation.
Use a WireGuard travel router
Install the WireGuard client profile on the travel router rather than on every downstream device. Connect the router to the hotel or café Wi-Fi, tether it to a phone, or use its WAN port, then connect your devices to the router’s private Wi-Fi or Ethernet network. The router performs the tunnel, routing and NAT for those devices.
Keep the travel router’s management network separate from the home tunnel network. If both networks use the same private subnet, routes can overlap and devices may try to reach the wrong gateway. Choose a distinct downstream subnet before importing the profile.
Verify that the tunnel is doing what you expect
- Connect the client while using the local network.
- Confirm that the WireGuard handshake timestamp updates on the home server.
- Check a public-IP service and verify that it reports the home connection’s address and country, not the hotel or café’s address.
- Test a home-LAN resource separately; internet egress and private-resource access are different forwarding paths.
- Temporarily disable the tunnel and confirm that ordinary local internet access returns. This distinguishes a routing problem from a home-server problem.
Option 2: Run an OpenVPN server at home
OpenVPN uses the same overall topology but relies on server certificates, client profiles and a mature collection of clients. It can be a sensible choice when your existing router, operating system or travel router already supports OpenVPN better than WireGuard.
Requirements and topology
The home server must be reachable from the public internet. GL.iNet’s OpenVPN-server guidance describes a router providing secure remote access to a home or office network and calls out port forwarding in a typical installation. Its travel-router example is the Beryl AX (GL-MT3000), a compact router that can run a client for devices connected behind it.
Deployment sequence
- Enable the OpenVPN server on the home router or host and generate the server certificate authority, server certificate and key.
- Create a unique client profile for each phone, laptop or travel router. Protect the embedded private key as carefully as the device itself.
- Choose whether the server should push a default route for full tunneling or only routes for home subnets. Do not assume that connecting to the VPN automatically changes the public IP; the server must be configured to forward and NAT client internet traffic.
- Open the selected OpenVPN port on the home firewall and forward it through any upstream router.
- Import the profile into the client application or travel-router firmware, connect, and perform the same handshake, public-IP and home-resource checks used for WireGuard.
OpenVPN profiles can be larger and involve more certificate material than WireGuard profiles. That is an operational difference, not a guarantee of slower or faster service; no supplied evidence provides a benchmark ranking.
Rank #3
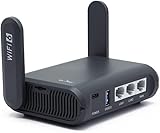
- 【AXT1800 WiFi 6 Wireless Router】Slate AX offers powerful Wi-Fi 6 network connection with a dual-band combined Wi-Fi speed of 1800 Mbps (600 Mbps for 2.4GHz and 1200 Mbps for 5GHz). Enhance Wi-Fi performance with MU-MIMO, OFDMA, BSS color and able to connect to up to 120 devices simultaneously.
- 【Fast and Secure Browsing】IPv6 supported; OpenVPN & WireGuard pre-installed, compatible with 30+ VPN service providers, OpenVPN speed up to 500 Mbps; WireGuard speed up to 550 Mbps. Cloudflare encryption supported to protect the privacy.
- 【Easy File Sharing】Our NAS feature supports SAMBA and WebDav protocol. By plugging an external USB hard disc into the router, you can create a private network to store and share your documents.
- 【Runs on OpenWrt 21.02】Slate AX runs on the latest OpenWrt 21.02 operating system (Kernel version 4.4.60), with mass device connection capabilities, and significantly reduced signal interference. You can customize the router and install applications based on your preferences.
- 【Repeater for Public, Hotel WiFi】Convert a public network(wired/wireless) to a private network(wired/wireless) for secure surfing. Work with Captive Portal. (Note: Most of the Free Public Wi-Fi hotspot set a time limit for users, which will disconnect your devices once the time is over. To deal with this situation, please reconnect your router to the wifi.)
Option 3: Put the VPN client on a travel router
A travel router solves the device-coverage problem. Instead of installing a VPN application on every phone, computer, streaming stick or console, you configure one gateway and connect everything to it. The travel router’s public-facing side joins the hotel or café network; its private side serves your devices; its VPN client sends selected or all traffic to the home server.
When this design is worth carrying
- You travel with several devices and do not want separate profiles or applications on each one.
- A device cannot install WireGuard or OpenVPN, but it can connect to Wi-Fi or Ethernet.
- You want one place to switch the home tunnel on or off.
- You need consistent DNS and routing behavior across a group of devices.
Hardware and setup considerations
The clearest product phrase for this use is GL.iNet Beryl AX GL-MT3000 travel router; GL.iNet’s OpenVPN-server guide uses the Beryl AX as its travel-router example. A compatible router must support the client protocol you choose, have enough memory for its firmware, and provide a way to join networks that require a captive-portal login.
- Connect the router to the hotel or café network without enabling the home VPN yet.
- Complete any captive-portal acceptance from a device connected to the router. Captive portals often block VPN traffic until the local terms page has been accepted.
- Import the home WireGuard or OpenVPN profile into the router’s VPN-client function.
- Select full-tunnel routing when all downstream devices should appear at home. Select split routing when local breakout is needed for ordinary browsing or location-sensitive services.
- Connect your devices to the router’s private SSID and test the public address from one of them.
Remember that the router adds another failure point. Its battery, power adapter, Wi-Fi radio and firmware all matter during travel. Carry a way to reach its administration interface locally if the tunnel fails, and keep a copy of the original profile so you can recreate the configuration.
Option 4: Build a ZeroTier full-tunnel gateway
ZeroTier documents a design in which a node advertises a default route and becomes the gateway for internet traffic. The gateway can be a home machine, a Raspberry Pi or a small VPS. This is a flexible mesh approach, but it is not automatic: route advertisement, IP forwarding, firewall policy and NAT must all be configured.
How the traffic path works
- Join the traveling device and the gateway to the same authorized ZeroTier network.
- Configure the gateway to advertise a default route (
0.0.0.0/0, and an IPv6 default if you intend to carry IPv6). - Enable forwarding between the ZeroTier interface and the gateway’s internet-facing interface.
- Add a masquerade/NAT rule so return traffic from the internet is translated back to the ZeroTier network.
- Authorize the member and test the public IP from the traveling device.
ZeroTier’s documented tutorial explicitly notes that a Raspberry Pi can serve as the exit-node host. The same tutorial also makes clear that the operator must configure gateway and NAT behavior; merely joining the virtual network does not route all internet traffic.
Free tools Windows power users keep installed
One-click scans. No signup required.
Rank #4
- The information below is per-pack only
- 【DUAL BAND AX TRAVEL ROUTER】Products with US, UK, EU Plug; Dual band network with wireless speed 574Mbps (2.4G)+2402Mbps (5G); 2.5G Multi-gigabit WAN port and a 1G gigabit LAN port; USB 3.0 port; Wi-Fi 6 offers more than double the total Wi-Fi speed with the MT3000 VPN Router.
- 【VPN CLIENT & SERVER】OpenVPN and WireGuard are pre-installed, compatible with 30+ VPN service providers (active subscription required). Simply log in to your existing VPN account with our portable wifi device, and Beryl AX automatically encrypts all network traffic within the connected network. Max. VPN speed of 150 Mbps (OpenVPN); 300 Mbps (WireGuard). *Speed tests are conducted on a local network. Real-world speeds may differ depending on your network configuration.*
- 【OpenWrt 21.02 FIRMWARE】The Beryl AX is a portable wifi box and mini router that runs on OpenWrt 21.02 firmware. It supports more than 5,000 ready-made plug-ins for customization. Simply browse, install, and manage packages with our no-code interface within Beryl AX's Admin Panel.
- 【PROTECT YOUR NETWORK SECURITY】Our pocket wifi, unlike other vulnerable portable wifi hotspot for travel purposes supports WPA3 protocol–Preventive measures against password brute-force attacks; DNS over HTTPS & DNS over TLS–Protecting domain name system traffic and preventing data eavesdropping from malicious parties; IPv6–Built-in authentication for privacy protection, eliminating the need for network address translation.
When ZeroTier is the better fit
Choose this route when you already manage ZeroTier nodes, want mesh connectivity in addition to internet egress, or prefer placing the gateway on a small Linux computer. Choose a conventional WireGuard or OpenVPN server when you want a single-purpose VPN endpoint with fewer mesh-specific route controls.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Public IP, CGNAT and captive-portal checks
Most failed home-VPN projects fail before encryption is involved. Determine whether the home router’s WAN address is globally reachable. If the router displays a private or carrier-grade address, inbound port forwarding may not work; ask the provider for a public address or choose a gateway that can make an outbound connection to a reachable host.
At the travel location, hotel and airport networks may require browser authentication, block UDP temporarily, isolate clients, or rate-limit long-lived connections. Join the local network and complete its sign-in page before troubleshooting the VPN. If the network blocks your chosen transport, a different protocol or an outbound relay may be required, but that changes the architecture and may add latency.
Full tunnel versus split tunnel
Use a full tunnel when
- You want public websites to see the home connection’s address.
- You are protecting traffic on an untrusted local network.
- You need country-specific services that permit access from the home connection.
- You are willing to consume home upload capacity for all browsing, updates and streaming.
Use a split tunnel when
- Only files, cameras or applications on the home LAN need remote access.
- Local services work better when they use the hotel or mobile connection directly.
- The home uplink is limited and should not carry general browsing.
- You need local access to a printer, casting device or captive portal while maintaining a private route home.
Document the prefixes you intend to route before creating client profiles. A mistaken default route can make local administration difficult, while an overly narrow route can leave the public IP unchanged even though the VPN reports connected.
Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Clear out junk files and repair common Windows errors3Fix the driver behind crashes, sound loss and screen glitchesSecurity and maintenance checklist
- Use a separate key or certificate for every client and revoke it when a device is lost.
- Keep the home router, server operating system and travel-router firmware updated.
- Expose only the VPN service port to the internet; do not publish the router’s administration interface.
- Restrict access from the VPN to the home subnets and services that travelers actually need.
- Back up server configuration and a recovery profile offline, but protect private keys from casual access.
- Decide how IPv6 should behave. A full IPv4 route without an IPv6 route can allow applications to use the local network’s IPv6 path instead of home.
- Monitor handshake times, assigned addresses and server logs so you can tell whether a failure is authentication, routing, NAT or local-network access.
Performance and cost expectations
Routing through home cannot exceed the home internet connection’s upstream capacity. If several travelers share one home uplink, they compete for that upload bandwidth. Latency is determined largely by the distance and peering between the travel network and home, so a geographically distant home may feel slower even when the tunnel is technically healthy.
Best Value

- 【AC1200 Dual-band Wireless Router】Simultaneous dual-band with wireless speed up to 300 Mbps (2.4GHz) + 867 Mbps (5GHz). 2.4GHz band can handles some simple tasks like emails or web browsing while bandwidth intensive tasks such as gaming or 4K video streaming can be handled by the 5GHz band.*Speed tests are conducted on a local network. Real-world speeds may differ depending on your network configuration.*
- 【Easy Setup】Please refer to the User Manual and the Unboxing & Setup video guide on Amazon for detailed setup instructions and methods for connecting to the Internet.
- 【Pocket-friendly】Lightweight design(145g) which designed for your next trip or adventure. Alongside its portable, compact design makes it easy to take with you on the go.
- 【Full Gigabit Ports】Gigabit Wireless Internet Router with 2 Gigabit LAN ports and 1 Gigabit WAN ports, ideal for lots of internet plan and allow you to connect your wired devices directly.
- 【Keep your Internet Safe】IPv6 supported. OpenVPN & WireGuard pre-installed, compatible with 30+ VPN service providers. Cloudflare encryption supported to protect the privacy.
The documented options do not establish a laboratory speed or latency ranking. Select based on reachability, client coverage and the amount of routing administration you are prepared to perform, not on an assumed protocol winner.
Which alternative should you choose?
- Choose direct WireGuard if you can obtain a public home endpoint and want the smallest, clearest configuration. It is the default recommendation for a technically comfortable household.
- Choose OpenVPN if your existing router or client ecosystem already relies on OpenVPN profiles and certificates, or if that is the protocol your travel hardware supports most reliably.
- Choose a travel router when the requirement is “every device in the room,” especially for devices that cannot run a VPN application. Put WireGuard or OpenVPN on the router and let it provide the downstream gateway.
- Choose a ZeroTier gateway if you already operate ZeroTier and are comfortable implementing default-route advertisement, forwarding and NAT on a Linux host or similar gateway.
Troubleshooting by symptom
The client never handshakes
Check the home WAN address, upstream port forwarding, firewall rules, endpoint hostname and UDP reachability. A carrier-grade NAT address or a captive portal can prevent the first packet from reaching the server.
The handshake works but the public IP is still local
Inspect the client’s allowed routes. A split-tunnel profile will intentionally leave ordinary internet traffic local. For a full tunnel, confirm the IPv4 and IPv6 default routes, then verify that the home server forwards and NATs traffic from the tunnel interface to its WAN interface.
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minutePC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Home devices are reachable but internet access fails
The encrypted path is working; forwarding or NAT toward the home WAN is not. Review the home firewall’s forwarding policy and masquerade rule, and confirm that the server’s own internet connection works.
Internet works but home-LAN devices do not
Check that the client profile includes the home LAN prefix, that the home firewall permits traffic from the VPN subnet, and that the LAN devices use the home router as their return gateway. Overlapping subnets at the hotel and home can also send packets to the wrong interface.
The travel router works for one device but not another
Confirm that both devices are connected to the router’s private network and that neither has a separately enabled VPN or proxy. Check the router’s downstream DHCP settings and whether policy rules exclude a particular address or protocol.
Bottom-line decision
For most travelers who want their traffic to look as though it comes from home, a home WireGuard server is the strongest Tailscale exit-node alternative: it provides full- or split-tunnel routing with a small client profile and no mesh control plane. Add a travel router when you need to cover several devices at once. Use OpenVPN for compatibility with an existing deployment, and use ZeroTier when its mesh model and a self-managed gateway fit your network. Validate public-IP reachability, CGNAT status, port forwarding and captive-portal behavior before buying hardware or depending on the setup for a trip.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.

