Freedom251 › Static Application Security Testing Software
Skylos
What Skylos is
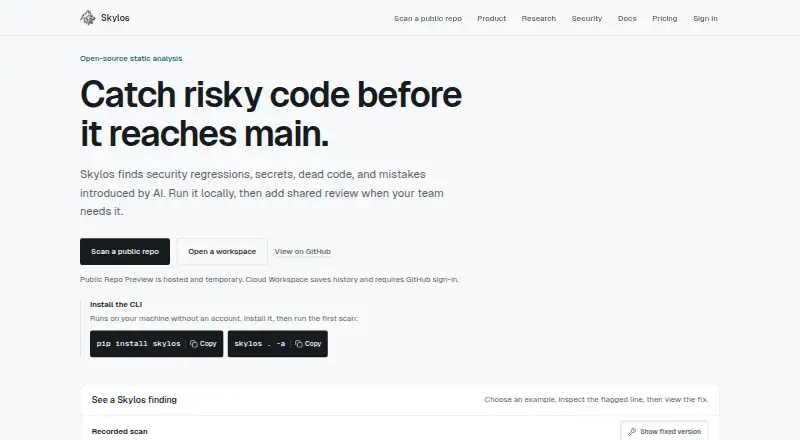
Skylos is an open-source static analysis tool for finding security regressions, exposed secrets, dead code, quality issues, and mistakes introduced by AI. It analyzes Python, JavaScript and TypeScript, Go, Java, Kotlin, PHP, Rust, Dart, C#, Shell, and deployment configuration, though analysis depth varies by language. Its CLI runs locally without an account and supports local scans and CI checks. A free VS Code extension provides inline diagnostics and optional AI verification using OpenAI or Anthropic API keys. Cloud features include GitHub pull request workflows, OIDC identity, and optional Slack or Discord notifications. A normal CLI scan stays on your machine; Cloud receives scan data when you upload a report, trigger a cloud action, or use the public scan endpoint. Uploaded reports may include findings, file paths, line numbers, snippets, and scan metadata. The free tier includes one cloud project, 10 stored scans, and seven days of history. One-time credit packs start at 9.00 USD and include Pro access for a stated period. Skylos says it does not currently claim SOC 2, ISO 27001, or CSA STAR certification.
Who it suits
Skylos suits developers and teams that want local static analysis, CI checks, or inline diagnostics in VS Code. Its VS Code page describes the extension for Python teams already using Ruff, Pylint, or Mypy.
What it does well
- CLI scans run locally without an account.
- Supports local scans and CI checks.
- Free VS Code extension offers inline diagnostics.
- Normal CLI scans stay on the user's machine.
What to know first
- Analysis depth varies by language.
- Free cloud tier has one project and 10 stored scans.
- Skylos does not claim SOC 2, ISO 27001, or CSA STAR certification.
Limits
The Free plan includes one cloud project, 10 stored scans, and seven-day history. The listed Workspace tier includes 10 projects, 500 stored scans per project, and 90-day history; Enterprise lists 9,999 projects, 10,000 stored scans, and 365-day history.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Free | Local CLI scans without login · Cloud: 1 project · 10 stored scans · 7-day history | Free |
| Team credit pack | 10,000 credits; one-time purchase; credits do not expire; Pro access for 180 days · 10,000 credits · 180 days Pro access | $129, paid once |
| Builder credit pack | 2,500 credits; one-time purchase; credits do not expire; Pro access for 90 days · 2,500 credits · 90 days Pro access | $39, paid once |
| Scale credit pack | 50,000 credits; one-time purchase; credits do not expire; Pro access for 365 days · 50,000 credits · 365 days Pro access | $499, paid once |
| Starter credit pack | 500 credits; one-time purchase; credits do not expire; Pro access for 30 days · 500 credits · 30 days Pro access | $9, paid once |
| Enterprise | Custom pricing · Unlimited credits · 365-day retention · Priority support and SLA | On request |
As skylos.dev lists them, read 30 Sept 2026. The maker's own page has the final word.
Getting started
- Open skylos.dev.
- Run the CLI locally without creating an account, or use it for CI checks.
- Install the free VS Code extension for inline diagnostics.
- Use optional OpenAI or Anthropic API keys for AI verification.
- Use Cloud features for GitHub pull request workflows or optional Slack and Discord notifications.
- Choose the Free plan or buy a one-time credit pack for Pro access.
Skylos is an open-source static analysis tool for security, secrets, dead code, quality issues and AI-introduced mistakes. It best suits teams that want local scanning and CI checks, particularly Python teams using Ruff, Pylint or Mypy. Its local CLI is the strongest reason to choose it; cloud workflows add collaboration but bring report-upload and retention considerations.
Overview
Skylos can run locally without an account, which makes it a practical fit for developers who want checks in their existing workflow without committing every scan to a hosted service. It also offers cloud workflows for pull requests and stored scan history. That split gives teams a choice, but cloud use is not equivalent to local-only analysis: uploads can include code snippets and other repository context.
Key features
The tool targets security regressions, exposed secrets, dead code, quality issues and mistakes introduced by AI. It analyzes Python, JavaScript and TypeScript, Go, Java, Kotlin, PHP, Rust, Dart, C#, Shell and deployment configuration. This is useful for mixed-language repositories, though analysis depth varies by language, so broad language support should not be mistaken for uniform coverage.
The free VS Code extension supplies inline diagnostics, with optional AI verification using an OpenAI or Anthropic API key. Its stated audience is Python teams already using Ruff, Pylint or Mypy, making it a more natural companion to established Python linting than a replacement for those tools. GitHub pull request workflows and OIDC identity are cloud features; Slack and Discord notifications are optional.
Local MCP tools cover analysis, security scanning, quality checks and secret scanning. The remediation tool consumes credits, so teams that rely on it should account for usage rather than treat it as an unlimited part of the workflow.
A normal CLI scan remains on the user's machine. Data is sent to Cloud when a user or workflow uploads a report, triggers a cloud action or uses the public scan endpoint. Uploaded reports may contain findings, severity, rule IDs, file paths, line numbers, snippets, attribution, scan metadata and optional provenance or defense evidence. Skylos describes role-based permissions, hashed project API keys, restricted GitHub OIDC uploads, bounded report ingestion and security headers. It does not claim SOC 2, ISO 27001 or CSA STAR certification, a material consideration for organizations with those requirements. Vulnerability reports are acknowledged within two business days, with an initial triage update within five; there is no paid bug bounty program.
Pricing
The Free plan costs nothing. Local CLI scans need no login; Cloud is limited to one project, 10 stored scans and seven days of history. It is a sensible way to begin with local analysis, but the small cloud allowance limits its usefulness for teams that want ongoing shared history.
Paid access is sold as one-time credit packs rather than a stated monthly subscription. The Starter credit pack is $9, paid once for 500 credits and 30 days of Pro access; the Builder credit pack is $39, paid once for 2,500 credits and 90 days; the Team credit pack is $129, paid once for 10,000 credits and 180 days; and the Scale credit pack is $499, paid once for 50,000 credits and 365 days. Credits do not expire, while the included Pro access does. Smaller packs suit occasional use; teams needing longer access or greater credit capacity can choose larger packs, but should distinguish the fixed access period from the non-expiring balance.
Enterprise has custom pricing, unlimited credits, 365-day retention, priority support and an SLA. Workspace includes 10 projects, 500 stored scans per project and 90-day history; Enterprise lists 9,999 projects, 10,000 stored scans and 365-day history. A seven-day trial is offered. Those quotas make the cloud tiers easier to assess for teams managing multiple projects, while Free remains much tighter on project count and retained scans.
Platforms
Skylos is available through its API, extension, Linux and macOS, self-hosted deployment, web and Windows. It supports IDE use and CI/CD, with a hybrid deployment model. That combination lets teams keep CLI scanning local while adopting cloud workflows selectively.
Who it's for
Skylos is best for developers and teams that want source analysis close to their code, CI checks, and the option to add cloud-based pull request workflows. Python teams already using Ruff, Pylint or Mypy have a particularly clear fit with the VS Code extension. Teams that need uniform analysis depth across languages, strict certified compliance, or substantial free cloud history should weigh those needs carefully before adopting it.
Pros and cons
- Pro: The CLI runs locally without an account, supporting code checks without routine report uploads.
- Pro: Broad language coverage and CI/CD support make it relevant to mixed-language repositories and automated checks.
- Pro: Cloud workflows, OIDC identity and optional notifications add collaboration paths for teams that want them.
- Con: Analysis depth varies by language, so coverage may not be equally useful across a repository.
- Con: Cloud reports may include snippets, paths and line numbers, requiring care around uploads and retention.
- Con: Free Cloud is capped at one project and 10 scans, and the tool does not claim major security certifications.
Alternatives
Snyk Open Source is a better fit when software composition analysis is the priority: its free monthly plan covers five projects with access to Snyk Open Source (SCA), while Skylos emphasizes broader static analysis and local CLI use. Horusec is worth considering for teams seeking a free, Apache License 2.0 option with CLI and platform components. Puma Scan is an alternative for readers who prefer its open-source Community edition or an annual End User license.
Semgrep Code may suit teams wanting code and supply-chain coverage in a free edition, with a cap of 10 repositories, 10 contributors and 60 AI credits. OpenGrep is a free CLI option for those who want an open-source static analysis engine on Linux, macOS or Windows. PVS-Studio, Bandit and Bearer are also alternatives to compare.
Browse more options in Static Application Security Testing Software.
Verdict
Choose Skylos if local-first scanning, CI checks and optional cloud collaboration matter more than uniform analysis depth or generous free cloud history. Its strongest advantage is the ability to keep ordinary CLI scans on the developer's machine while expanding into cloud workflows as needed. Look elsewhere if certified compliance is essential or if a small free cloud allowance cannot support your team's project and retention needs.
Verdict
Skylos offers local analysis alongside cloud workflows, with clear distinctions about when scan data is uploaded. Review language coverage and cloud limits to see whether they fit your workflow.
Questions
Is Skylos free?
Yes. The Free plan is 0.00 USD and includes local CLI scans without login, plus one cloud project, 10 stored scans, and seven-day history.
What do the paid plans cost?
One-time credit packs cost 9.00 USD, 39.00 USD, 129.00 USD, and 499.00 USD. They provide 500, 2,500, 10,000, and 50,000 credits respectively, with Pro access periods ranging from 30 to 365 days.
Which languages does Skylos analyze?
It supports Python, JavaScript and TypeScript, Go, Java, Kotlin, PHP, Rust, Dart, C#, Shell, and deployment configuration. Analysis depth varies by language.
Does Skylos work locally?
Yes. The CLI runs locally without an account, and a normal CLI scan stays on the user’s machine.
What happens to data sent to Skylos Cloud?
Cloud receives scan data when a report is uploaded, a cloud action is triggered, or the public scan endpoint is used. Reports may contain findings, severity, rule IDs, file paths, line numbers, snippets, attribution, metadata, and optional evidence.
Is Skylos certified for SOC 2 or ISO 27001?
Skylos says it does not currently claim SOC 2, ISO 27001, or CSA STAR certification.
Facts from Skylos's own pages
- Cloud data
- Uploaded reports may include findings, severity, rule IDs, file paths, line numbers, snippets, attribution, scan metadata, and optional provenance or defense evidence. · skylos.dev, 30 Sept 2026
- Cloud integrations
- Cloud features include GitHub pull request workflows and OIDC identity, plus optional Slack and Discord notifications. · skylos.dev, 30 Sept 2026
- Compliance
- Skylos says it does not currently claim SOC 2, ISO 27001, or CSA STAR certification. · skylos.dev, 30 Sept 2026
- IDE integration
- The free VS Code extension provides inline diagnostics and optional AI verification using OpenAI or Anthropic API keys. · skylos.dev, 30 Sept 2026
- Local and CI use
- The CLI runs locally without an account and supports local scanning and CI checks. · docs.skylos.dev, 30 Sept 2026
- Local data handling
- A normal CLI scan stays on the user's machine; Cloud receives scan data when a user or workflow uploads a report, triggers a cloud action, or uses the public scan endpoint. · skylos.dev, 30 Sept 2026
- MCP support
- The docs list local MCP tools for analysis, security scanning, quality checks, and secret scanning, and a credit-charged remediation tool. · docs.skylos.dev, 30 Sept 2026
- Plan limits
- The Workspace tier includes 10 projects, 500 stored scans per project, and 90-day history; Enterprise lists 9,999 projects, 10,000 stored scans, and 365-day history. · skylos.dev, 30 Sept 2026
- Security controls
- The Trust Center describes role-based permissions, hashed project API keys, restricted GitHub OIDC uploads, bounded report ingestion, and security headers. · skylos.dev, 30 Sept 2026
- Support
- The security page says vulnerability reports are acknowledged within 2 business days with an initial triage update within 5 business days, and that there is no paid bug bounty program. · skylos.dev, 30 Sept 2026
- Supported languages
- It analyzes Python, JavaScript and TypeScript, Go, Java, Kotlin, PHP, Rust, Dart, C#, Shell, and deployment configuration, with analysis depth varying by language. · skylos.dev, 30 Sept 2026
- What it does
- Skylos is an open-source static analysis tool that finds security regressions, secrets, dead code, quality issues, and mistakes introduced by AI. · skylos.dev, 30 Sept 2026
- Who it is for
- The VS Code page describes the extension for Python teams already using Ruff, Pylint, or Mypy. · skylos.dev, 30 Sept 2026