Freedom251 › UML Modeling Software
Horusec
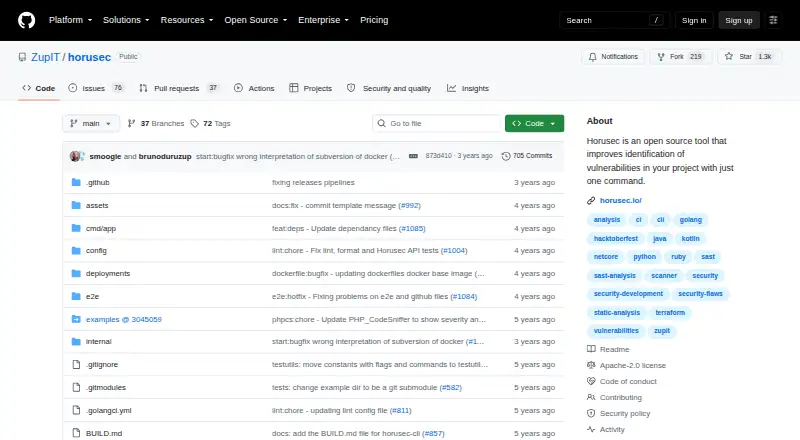
What Horusec is
Horusec is a free, open-source static code analysis tool for identifying security flaws during development. It scans source code and can search project files and Git history for leaked keys and other security issues. The project describes analysis across 18 languages with 20 security tools; listed language coverage includes C#, Java, Kotlin, Python, Ruby, Golang, Terraform, JavaScript, TypeScript, Kubernetes, PHP, C, HTML, JSON, Dart, Elixir, Shell, and Nginx. Analysis can be configured through CLI resources. Developers can run Horusec from the command line, while DevSecOps teams can use it in CI/CD pipelines, and a Visual Studio Code extension is available. Horusec-Web provides vulnerability dashboards, false-positive controls, authorization tokens, and vulnerability updates. The platform integrates with the CLI to visualize and manage findings and supports native Horusec, LDAP, and Keycloak authentication. The platform repository was archived by its owner on March 19, 2025 and is read-only. Running Horusec with all its tools requires Docker; disabling Docker reduces its analysis capabilities. The platform requires RabbitMQ and PostgreSQL.
Who it suits
Horusec suits developers and DevSecOps teams seeking code analysis in development or CI/CD workflows. Its web platform may suit teams that need to visualize and manage findings, provided they account for its dependencies and archived status.
What it does well
- Free and open-source under Apache License 2.0.
- Scans source code and searches Git history for leaked keys.
- Can run in CI/CD pipelines.
- Includes a Visual Studio Code extension.
- Offers vulnerability dashboards and false-positive controls.
What to know first
- Full tool use requires Docker.
- Disabling Docker reduces analysis capabilities.
- The platform repository is archived and read-only.
- The platform requires RabbitMQ and PostgreSQL.
Limits
The plan is free, with no free-plan quota stated in the facts. Running Horusec without Docker reduces its analysis capabilities; the Platform also requires RabbitMQ and PostgreSQL.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Open source | Apache License 2.0 · CLI and platform components | Free |
As github.com lists them, read 1 Oct 2026. The maker's own page has the final word.
Getting started
- Visit the Horusec GitHub repository.
- Choose the CLI, Visual Studio Code extension, or self-hosted platform route.
- Install Docker to run Horusec with all its tools.
- Configure analysis through CLI resources.
- For Horusec Platform, provide RabbitMQ and PostgreSQL.
Overview
Horusec is an open-source static code analysis tool for finding security flaws during development. It suits development and DevSecOps teams that want configurable checks across a broad set of languages and workflows. Its strongest case is the combination of CLI and CI/CD use with secret scanning; its web platform is a less secure long-term bet because its repository is archived.
Horusec analyzes source code and searches project files and Git history for leaked keys and other security issues. It combines 20 security tools across 18 languages, with analysis configurable through CLI resources. SCA and fix guidance are included, though the project details do not describe the form that guidance takes.
For more options, see Static Application Security Testing Software.
Key features
Configurable analysis and secret detection
Coverage spans C#, Java, Kotlin, Python, Ruby, Golang, Terraform, JavaScript, TypeScript, Kubernetes, PHP, C, HTML, JSON, Dart, Elixir, Shell and Nginx. Scanning Git history as well as current project files can help teams catch exposed keys that are no longer present in the working tree. The breadth is useful across mixed-language projects, while the requirement for Docker to run all tools is a meaningful operational cost: disabling Docker removes much of the analysis power.
Developer workflows
The CLI supports local use and CI/CD integration, and a Visual Studio Code extension adds an editor workflow. That range gives teams options for bringing checks into development without relying on the web platform. The analysis is configurable through CLI resources, which is useful for teams that need control over checks rather than a fixed scan.
Web vulnerability management
Horusec-Web provides vulnerability metrics dashboards, false-positive control, authorization tokens and vulnerability updates. Horusec Platform connects the CLI to web services for visualizing and managing vulnerabilities, with native Horusec, LDAP and Keycloak authentication. However, the platform repository was archived by its owner on March 19, 2025 and is read-only. It also requires RabbitMQ and PostgreSQL, so teams should weigh both the maintenance status and deployment dependencies before making it central to their workflow.
Pricing
Horusec is free. Its Open source plan costs nothing and is licensed under Apache License 2.0, covering CLI and platform components. There are no paid tiers or seat limits described, making it a low-cost option for teams able to operate the tooling themselves. The trade-off is that self-hosting and, for the web platform, RabbitMQ and PostgreSQL are part of the deployment burden; there is no hosted paid tier described to avoid that work.
Platforms
Horusec supports API, extension, Linux, macOS, self-hosted, web and Windows. It targets source analysis, includes IDE and CI/CD support, and is deployed self-hosted. Docker is required to run the full set of analysis tools.
Who it's for
Horusec is a strong fit for teams seeking a free, self-hosted scanner that can run in a CLI or CI/CD workflow and cover multiple languages, including secret checks in Git history. It is less suited to organizations that need a maintained web platform with minimal infrastructure work, or that want a hosted service rather than managing deployment requirements themselves.
Pros and cons
- Pros: Broad language coverage and 20 security tools give mixed-language teams a single analysis workflow.
- Pros: CLI, CI/CD and Visual Studio Code options let teams place checks in different stages of development.
- Pros: Git-history secret scanning can surface exposed keys beyond the current project files.
- Cons: Docker is needed for the full toolset, and disabling it substantially reduces analysis capability.
- Cons: The web platform is read-only at its archived repository and depends on RabbitMQ and PostgreSQL, complicating its use as a core managed service.
Alternatives
For a different balance of scan scope, cost and deployment, consider these alternatives:
- Skylos may suit teams wanting local CLI scans without login alongside a cloud option capped at one project, 10 stored scans and seven days of history.
- Snyk Open Source is worth considering when SCA is the priority: its free plan covers five projects and Snyk Open Source access, while its Team plan is $25 a month, billed monthly, for up to 10 developers.
- MobSF is another free, open-source option, with Android and iOS among its supported platforms.
- Puma Scan offers a free Community plan and a $299 a year End User plan with an annual subscription.
- Semgrep Code may appeal to teams seeking a paid product with a free edition that includes Code and Supply Chain for up to 10 repositories and 10 contributors, plus 60 AI credits.
- Flawfinder is a free GPL-2.0+ open-source option for Linux, macOS, self-hosted and Windows environments.
- OpenGrep offers a free open-source static analysis engine with a CLI for Linux, macOS and Windows.
- Bandit is a free Apache License 2.0 alternative for Linux, macOS and self-hosted use.
Verdict
Choose Horusec if your team wants a free, self-hosted analyzer with configurable CLI checks, CI/CD support and broad language coverage, including Git-history secret detection. Look elsewhere if you need a maintained web vulnerability platform or want to avoid Docker and the infrastructure demands of self-hosting.
Verdict
Horusec combines configurable static analysis with CLI, editor, and CI/CD workflows. Teams considering its web platform should note that its repository is read-only and that it requires RabbitMQ and PostgreSQL.
Questions
How much does Horusec cost?
The open-source plan is free under Apache License 2.0.
What platforms are listed?
Horusec is listed for API, extension, Linux, macOS, self-hosted, web, and Windows.
Does it support CI/CD and IDE workflows?
Yes. DevSecOps teams can use Horusec in CI/CD pipelines, and the project provides a Visual Studio Code extension.
What does Horusec analyze?
It performs static analysis on source code and searches project files and Git history for leaked keys and other security flaws.
Does it require Docker?
Docker is required to run Horusec with all its tools. Disabling Docker reduces its analysis capabilities.
Is Horusec Platform still maintained?
Its repository was archived by its owner on March 19, 2025 and is read-only. The Platform requires RabbitMQ and PostgreSQL.
Facts from Horusec's own pages
- Configurable analysis
- The analysis is fully configurable through CLI resources. · github.com, 1 Oct 2026
- Developer workflow
- Developers can use Horusec through its CLI, while DevSecOps teams can use it in CI/CD pipelines. · github.com, 1 Oct 2026
- Docker requirement
- Docker is required to run Horusec with all its tools; disabling Docker loses much of the analysis power. · github.com, 1 Oct 2026
- Editor integration
- The project provides a Visual Studio Code extension for analyzing projects. · github.com, 1 Oct 2026
- Languages
- It analyzes C#, Java, Kotlin, Python, Ruby, Golang, Terraform, JavaScript, TypeScript, Kubernetes, PHP, C, HTML, JSON, Dart, Elixir, Shell and Nginx. · github.com, 1 Oct 2026
- Platform authentication
- Horusec Platform supports native Horusec, LDAP and Keycloak authentication. · github.com, 1 Oct 2026
- Platform dependencies
- Horusec Platform requires RabbitMQ and PostgreSQL. · github.com, 1 Oct 2026
- Platform integration
- Horusec Platform is a set of web services integrating with Horusec CLI to visualize and manage vulnerabilities. · github.com, 1 Oct 2026
- Platform status
- The Horusec Platform repository was archived by its owner on March 19, 2025 and is read-only. · github.com, 1 Oct 2026
- Purpose
- Horusec performs static code analysis to identify security flaws during development. · github.com, 1 Oct 2026
- Secret detection
- It searches project files and Git history for key leaks and other security flaws. · github.com, 1 Oct 2026
- Security policy
- Zup's open-source projects adopt OpenSSF Security Scorecard and OpenSSF Best Practices Badge recommendations. · github.com, 1 Oct 2026
- Security tools
- Horusec analyzes 18 languages with 20 different security tools simultaneously. · github.com, 1 Oct 2026
- Support
- Questions and ideas are handled through GitHub Issues and the Zup Open Source Forum. · github.com, 1 Oct 2026
- Web application
- Horusec-Web provides vulnerability metrics dashboards, false-positive control, authorization tokens and vulnerability updates. · github.com, 1 Oct 2026