PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchIf a mail-server vulnerability may have exposed accounts or messages, start your organization’s incident-response process, contain further access without destroying evidence, and investigate what the attacker could actually access. An “exposure” does not by itself prove that anyone read messages, stole credentials, or that every recipient was affected. Individuals should secure their email accounts if those accounts were compromised; organizations should base notices and other protective advice on what the investigation establishes.
What should an organization do first?
Activate the incident plan and involve the people who can make security, operational, legal, and communications decisions. The FTC recommends a coordinated response that may include information security, IT, forensics, legal, operations, communications, and management. Bring in privacy counsel promptly: legal duties depend on the organization, the information involved, and the jurisdictions and rules that apply. If the organization lacks the necessary expertise, consider an independent forensic investigator. See the FTC’s business data-breach guide and NIST SP 800-45 Version 2.
As an Amazon Associate I earn from qualifying purchases.
Assign someone to keep a timeline of discoveries and decisions. Record when the vulnerability was found, which systems and accounts may be involved, and what response actions were taken. That record supports the investigation and helps counsel assess reporting and notification obligations.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
How can you contain the incident without losing evidence?
Reduce the chance of further access or data loss, but do not assume that powering down, rebooting, or reimaging is always the right first move. Those actions can destroy useful evidence. The FTC advises taking affected equipment offline but cautions against turning machines off before forensic experts arrive. NIST describes careful isolation through upstream network equipment as one possible approach. The right action depends on the threat, the system, and the evidence responders need to preserve.
#1 Best Overall

- Ultra-Compact FIDO2 Security Key - Plug-and-stay or carry on a keychain. This USB-A hardware security key offers portable, always-on protection for desktop and mobile use. (Item Size: 0.75 X 0.74 IN x 0.25 IN)
- USB-A Hardware Key for All Devices - Works with USB-A ports on PC, Mac, Android, and other laptop/notebook device. Enables secure, cross-platform login with FIDO2.0 passkey support.
- FIDO Certified Security Key - Meets FIDO and FIDO2 standards. Works with Google, Microsoft, GitHub, Dropbox, and more. Please check service compatibility before purchase.
- Passwordless Login with Passkey - Supports passkey login via WebAuthn and CTAP2. Enjoy password-free sign-ins where supported. Not all websites or services currently support passkeys.
- Advanced Multi-Factor Authentication - Offers 200 FIDO2 passkey slots and 50 OATH-TOTP slots. Strong, flexible 2FA/MFA support across various apps and authentication platforms.
Use qualified forensic advice and the organization’s incident plan to weigh the immediate risk of ongoing access against the evidentiary value of system state. Preserve relevant logs and, where responders can do so safely, volatile information before actions that could erase it. Do not destroy evidence.
What should the investigation establish?
Determine the scope and consequences rather than treating the presence of a vulnerability as proof of a specific breach. Review mail-server and identity-provider activity, look for attacker changes or tools, and check whether connected hosts, service accounts, or user accounts were also affected. Preserve the evidence used to reach conclusions.
Rank #2

- FIDO2 & Passkey Ready: Business-ready and FIDO2 L1 certified. This key is supported by major management suites and is ideal for both individual and enterprise deployment. Works seamlessly with Gmail, Facebook, GitHub, Dropbox, Coinbase, and more.
- Universal Connectivity (USB-A ): Features a built-in USB-A connector—simply unfold the key and plug it into your compatible PC or laptop for seamless authentication on the go.
- Dedicated Manager App: Use the Thetis Manager App for the initial hardware PIN setup. Setting the PIN on the device first ensures a smooth registration process. Once the PIN is configured, you can begin registering the key across your favorite FIDO2-compatible online services.
- Ultra-Durable & Portable: Featuring a rotating metal cover, this key is water, crush, and tamper-resistant. It fits easily on a keychain and requires no batteries or network connectivity.
- Check FIDO2 compatibility before purchase - Known limitations: ID Austria is not supported (requires FIDO2 Level 2). Windows Hello login only works with Windows Enterprise editions that support Entra ID, and NFC is NOT supported.
- Was information merely accessible, or does evidence show that messages or other data were accessed or acquired?
- What types of information were in the potentially affected accounts or messages, and how many people or business customers could be affected?
- Were credentials, password-reset links, financial information, identity numbers, or other sensitive details exposed?
- Did encryption meaningfully protect the information, and is there evidence of unauthorized changes or continued access?
Where facts remain uncertain, distinguish what is confirmed from what is still being investigated. That distinction matters both for containment and for deciding what recipients need to know.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Scan for outdated or missing drivers - takes under a minute3Repair Windows errors before they cause bigger problemsHow should you remove access and recover the service?
Use the investigation to set the reset scope and recovery plan. Revoke or reset credentials and secrets that may have been exposed, including relevant user and service accounts. Patch the vulnerable software or configuration, disable services that are not needed, and review provider privileges and network segmentation. A patch alone does not establish that an attacker has lost access.
Rank #3

- A FIDO security key with PUF technology provides a unique, hardware-rooted trust anchor that resists tampering and cyber attacks, offering stronger security than conventional designs.
- FIDO2 Certified Protection – Enjoy phishing-resistant security with FIDO2 certification, ensuring top-tier account safety across Windows, macOS, Linux, iOS iOS, Android and more.
- Easy to use & Portable – Designed with a compact USB-C interface, Clife key fits easily on your keychain for secure access anywhere. Simply plug in and authenticate with ease.
- Universal Compatibility – Works seamlessly with hundreds of FIDO2/U2F compliant services, including popular cloud, email, and social platforms.
- Backup recommended – To ensure continuous access, register a backup Clife security key as a spare in case your primary key is lost.
Choose a recovery method based on evidence and operational risk. NIST’s 2007 publication discusses sequencing, testing, and monitoring, and warns that restoring from a backup made after compromise can preserve attacker access. It is legacy guidance, not a current product-specific procedure; apply it alongside your incident plan and qualified technical advice.
| Choice | What to weigh |
|---|---|
| Isolate the affected system while retaining power | May limit network access while preserving volatile evidence, but the appropriate isolation method depends on the architecture and whether it actually stops the threat. NIST describes upstream isolation as one possible method. |
| Power down or reboot | May be considered in some circumstances, but can erase volatile evidence. Consult forensic responders before taking this step when feasible. |
| Repair the existing system | Can be appropriate if responders can identify and remove the cause and verify the system’s integrity. Patch and configuration changes alone do not prove that persistence or unauthorized access has been removed. |
| Restore or rebuild from a clean state | Assess whether the backup predates the compromise and is itself trustworthy. Test the restored system before reconnecting it, then monitor for renewed access. |
These are not universal prescriptions. Consider ongoing attacker access and potential data loss, evidence volatility, backup integrity, downtime and safety impacts, available forensic expertise, and what the incident plan and provider architecture permit. Follow the response with monitoring for renewed access and document the recovery decisions.
Rank #4

- Manufactured by Hirsch Secure, Inc. — formerly Identiv. PHISHING-RESISTANT SECURITY: FIDO Alliance-certified SecureKey stores site-specific cryptographic credentials on-device to help defend against phishing, password theft and replay attacks. PASSWORDLESS + MFA: Supports FIDO2, U2F and WebAuthn for passwordless sign-in, 2FA and MFA. USB-C + NFC: Works with compatible laptops, desktops and mobile devices across Windows, macOS, Linux, ChromeOS, Android and iOS. MULTI-PROTOCOL: Supports HOTP and PIV, with SecureKey Manager for FIDO2 PIN and device management. TAA COMPLIANT: Built for personal, business, enterprise and government use. Register a second key as backup.
Who must be notified, and when?
Ask privacy counsel to determine which laws, contracts, sector rules, and regulator requirements apply. The FTC says all U.S. states, the District of Columbia, Puerto Rico, and the Virgin Islands have laws requiring notification of security breaches involving personal information. Requirements and deadlines vary; the FTC’s guide is not a complete state-by-state deadline chart, and it does not establish a universal deadline for every incident. Health-information rules, contractual duties, and requirements outside the United States may also matter.
Recommended Free Tools
One narrower federal requirement illustrates why applicability matters: under the FTC Safeguards Rule guidance, a covered financial institution must report a defined notification event involving at least 500 consumers’ unencrypted information to the FTC as soon as possible and no later than 30 days after discovery. This is a rule for covered financial institutions and qualifying events, not a general deadline for every mail-server breach. Review the FTC Safeguards Rule guidance with counsel before deciding whether it applies.
Best Value
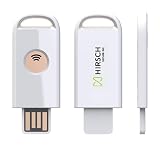
- Manufacturer Information: Manufactured by Hirsch Secure, Inc. - formerly Identiv
- Phishing-Resistant Security: FIDO Alliance-certified SecureKey stores site-specific cryptographic credentials on-device to help defend against phishing, password theft and replay attacks
- Passwordless and Multi-Factor Authentication: Supports FIDO2, U2F and WebAuthn for passwordless sign-in, 2FA and MFA
- USB-A and NFC Connectivity: Works with compatible laptops, desktops and mobile devices across Windows, macOS, Linux, ChromeOS, Android and iOS
- Multi-Protocol Support: Supports HOTP and PIV, with SecureKey Manager for FIDO2 PIN and device management
If the organization held information for business customers, notify those customers as required and coordinate with them. Prepare recipient notices that accurately explain what happened, what information was involved, what the organization has done, and what useful steps people can take. Provide a reliable contact route, and coordinate timing with law enforcement where relevant. Avoid sharing operational details that could create additional risk or make a notice easier to imitate in a phishing message.
For each proposed notice or protective recommendation, weigh the information involved, the likelihood and potential harm of misuse, any applicable legal deadline, and whether the advice is actionable. For example, contact the relevant financial institution if financial account credentials were exposed. Do not advise everyone to freeze credit unless the exposed information makes that step appropriate.
What should an individual do after an email account was hacked?
If your own mailbox was taken over, secure it and check for changes the intruder may have made. The FTC’s hacked-email recovery guide, marked August 2023, recommends these steps:
Free tools Windows power users keep installed
One-click scans. No signup required.
- Change the email password to a new, unique password.
- Sign out other devices or sessions and enable two-factor authentication.
- Check that recovery email addresses and phone numbers are yours.
- Remove unauthorized forwarding rules.
- Review sent and deleted folders for unfamiliar messages or signs of tampering.
- Warn contacts if suspicious messages may have been sent from your account.
Email can be used to reset passwords for other accounts. If the mailbox or its messages contained password-reset links or credentials, change the passwords for affected linked accounts as well. If financial credentials or identity numbers may have been exposed, contact the relevant financial institution or use authoritative identity-recovery resources appropriate to the information involved.
What should happen after recovery?
Once services are stable, document lessons from the incident, update the response plan, and confirm that providers have fixed the vulnerability. Use the investigation’s findings to improve access controls, segmentation, and monitoring where weaknesses were identified. NIST SP 800-45 Version 2 was published in 2007; its mail-security response concepts can be useful, but it should not be treated as a current product-specific playbook.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




