Banks should evaluate e-signature software as a third-party service that may maintain, process or access customer information. Require controls proportionate to the bank’s risks, plus an audit trail that connects the signer and signing events to the executed document and can be retrieved for review. The precise requirements depend on the bank, transaction, jurisdiction and retention rules; there is no single feature set or log-retention period established for every bank.
Start with the bank’s risk and regulatory scope
Before comparing platforms, identify the workflows the service will support: which products and transactions, what customer information is involved, who will use the system, where the parties are located, and what access the provider and its subprocessors may have. Map those facts to the bank’s information-security and third-party risk assessments.
As an Amazon Associate I earn from qualifying purchases.
For national banks and federal savings associations, the interagency information-security guidelines in 12 CFR Appendix B to Part 30 call for a written security program with safeguards suited to the institution’s size, complexity, activities and identified risks. The guidelines address customer information maintained by or on behalf of covered institutions. Banks should confirm the current official rule and the parallel requirements of their own regulator before applying it to a procurement.
Recommended Free Tools
These rules set a risk-based oversight framework, not a universal e-signature product specification. A vendor’s certification or audit report can inform the bank’s assessment, but does not replace the bank’s own judgment about whether the service and its controls are appropriate for a particular use.
#1 Best Overall

- Instant E-Signatures, One Click Away – Seamlessly send your handwritten signature to your computer with just one tap. Fully compatible with PDF, Word, Excel, JPG, PNG, and TIFF formats.
- Your Paperless Office Hero – Sign quotes, contracts, insurance forms, and internal approvals without ever printing a page. Complete documents quickly and securely—100% digitally.
- Built-in Timestamp & Printed Name – Every signature includes a timestamp and your printed name for enhanced credibility and traceability—ideal for business and legal use.
- Smart Sticky Notes, Digitally Delivered – Jot down memos and upload them instantly to your Outlook Calendar or desktop. Your personal assistant for smart, organized scheduling.
- Effortless Visual Collaboration – Sketch workflows, wireframes, or brainstorm ideas in real time. Perfect for teams that move fast and think visually.
Evaluate identity, authentication and access controls
Ask how the platform establishes signer identity, authenticates the person at signing, confirms that person is authorized for the transaction, and limits access to documents and account functions. Review controls for both customers and bank personnel, including privileged administrators and support staff.
- Request a description of available authentication methods and the circumstances in which each is used.
- Determine how the workflow handles failed authentication, repeated attempts, access recovery and changes to signer details.
- Review role-based permissions, privileged access, administrator activity and restrictions on viewing or disclosing customer information.
- Match controls to the transaction’s risk, value and customer type rather than assuming one authentication factor is appropriate for every workflow.
The FFIEC’s Authentication and Access guidance provides context for evaluating services used by financial institutions, including electronic agreements. It does not mean every signature workflow must use one specific factor.
Protect customer information throughout the service
Review how information is protected in transit and in storage, who can access it, where it is handled, and which subprocessors are involved. The interagency guidelines identify encryption of electronic customer information in transit and storage as a safeguard to consider where appropriate to risk; they do not make one blanket technical configuration the answer for every deployment.
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Rank #2
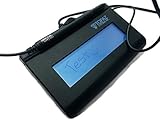
- Virtual Serial via USB Interface
- Rugged signing area for long life
- LCD display for customizability
- Small size and weight for portability
- High-quality biometric and forensic capture
Establish how the bank can restrict provider access, and what happens to records when the contract ends. The bank should understand the provider’s data return, deletion and subprocessor arrangements, including how those commitments apply to retained copies and backups under the contract.
Require an audit trail that can support review
U.S. bank guidance establishes risk-based security and oversight duties, but the cited guideline does not prescribe a universal e-signature log schema. Treat the following as procurement questions: can the platform produce usable evidence that links the signing activity to the transaction and the specific executed document?
- Attribution: Can the record identify the signer and connect the authentication event to that signer?
- Event sequence: Does it show relevant workflow events and timestamps, including completion, refusal or other outcomes?
- Document linkage: Does the evidence identify the version signed and preserve an integrity reference or equivalent means of relating the record to the executed document?
- Administrative activity: Can reviewers see relevant administrative changes and access to the workflow or records?
- Retrieval: Can the bank export evidence in a readable, durable form and reconcile it to the completed document?
Ask for sample exports and test whether bank staff can interpret them and connect them to the executed document. Exercise realistic cases such as normal completion, authentication failure, refusal, document correction or replacement, delegated or administrative action, and incident investigation. These are practical evaluation and testing measures, not a claim that any particular vendor has been tested.
Rank #3
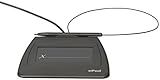
- EPADLINK VP9801 EPADLINK SIG PAD USB WITH
- The package length is 4.064 centimeters
- The package height is 23.114 centimeters
- The package width is 16.51 centimeters
An older European Commission eIDAS-Node manual offers additional engineering ideas for audit logs: synchronized time sources, protections against alteration or deletion, limits on administrators’ ability to erase or disable records, suitable archiving, avoidance of unnecessary sensitive data in logs, and simple standard formats. It also discusses monitoring and SIEM. Treat this as dated technical guidance, not a bank-specific legal mandate.
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallMake provider safeguards and incident cooperation enforceable
For covered U.S. institutions, the interagency guidelines anchor provider oversight in appropriate selection due diligence, contractual safeguards and risk-based monitoring. Build the review and contract around the service’s actual access to customer information and the bank’s ability to oversee it.
- Define permitted provider use and access to customer information, including relevant subprocessor controls.
- Specify the safeguards the provider must maintain and the audit, test or equivalent assurance evidence it will make available.
- Set responsibilities for records access and export, retention, deletion or return, and service continuity.
- Require prompt notice to the bank of relevant security incidents, access to investigation records, cooperation with containment and notification, and preservation of relevant logs.
The bank needs a workable response path when provider-held customer information is involved. Vendor notification or assistance does not by itself discharge the bank’s own regulatory responsibilities.
Rank #4

- 【Signature tool 1】: SMAJAYU electronic signature pad works with “SMAJAYU document(s) Signer” a Sign Tool for pdf,word,excel documents digital signature. Pdf,Excel,word documents will be save as pdf after signature on sign tool.
- 【Signature tool 2】: Second sign tool named “demo tool” which is for getting signature picture to past on excel,word.edited files.
- 【Signature tool 3】: 430S SDK is available to integrate with programmable flatform, like website, app. Contact SMAJAYU support team for support.
- 【Apply Windows OS】SMAJAYU Signature pad and Signer tool only compatible with Windows OS, Windows 7,8,10,11, don’t support apple PC.
- 【How to sign documents】Install “ SMAJAYU document(s) Signer” on computer, run this app and create certification for first installation which for signature encryption and safety. Then insert Signature pad by USB and open files to start sign.
Review independent assurance and test key controls
Request independent audits, test summaries or equivalent evaluations, then assess their scope, dates, exceptions and remediation rather than relying on a label alone. The U.S. guidelines call for regular testing of key controls, systems and procedures, with frequency based on risk; testing should be conducted or reviewed independently of staff who develop or maintain the security program. Consider how the bank can independently test the parts of the signing workflow on which it relies.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.For EU workflows, separate qualification from acceptance
For transactions involving the EU, first determine the signature or trust-service level the workflow requires. The European Commission’s eIDAS Dashboard describes the framework for creating, validating and preserving electronic signatures and timestamps. Qualified status is reflected in national Trusted Lists and relates to a particular provider or service, so verify the relevant service entry at procurement and renewal. A listing alone does not establish commercial availability or fitness for the bank’s workflow.
Free tools Windows power users keep installed
One-click scans. No signup required.
If the objective is to create qualified signatures, the Commission’s qualified-certificate guidance says the certificate’s private key must be protected by a qualified signature creation device. The Commission’s validation material explains that technical validation depends on a validation policy and trust anchors, and that technical validation must be completed by business validation. Accordingly, define both the technical signature status the bank will accept and the business rules for accepting the signed transaction.
Best Value
- Item Package Dimension: 9.099999990718L X 6.49999999337W X 1.599999998368H Inches
- Real-Time Signature Display – LCD screen shows the signature as it’s being written, providing instant visual confirmation and accuracy.
- Easy USB Connectivity – Simple plug-and-play setup with any standard USB port, no complicated installation required.
- Durable and Compact Design – Built for daily use in professional environments, with a small footprint to save desk space.
- Secure and Legally Binding – Works seamlessly with signature software to capture secure, tamper-proof electronic signatures.
Use one evidence request to compare providers
Give each candidate the same workflow description and evidence request. Compare its demonstrated capabilities against the bank’s requirements, not its marketing terminology.
| Evaluation area | Evidence or question for each provider |
|---|---|
| Identity and access | Authentication options, signer identity evidence, authorization, privileged access and controls against unauthorized disclosure. |
| Data protection | Safeguards for information in transit and storage, access restrictions, data handling locations and subprocessors, and return or deletion arrangements. |
| Audit evidence | Sample event records and completed-document package showing attribution, timestamps, event outcomes, document linkage, administrative activity and exportability. |
| Incident response | Notification commitments, investigation-record access, cooperation with containment and notification, and log preservation. |
| Assurance and testing | Independent audit or equivalent evidence, test scope and date, exceptions and remediation, plus the bank’s ability to test key controls. |
| Operations and jurisdiction | Service-continuity arrangements, applicable retention support and, where relevant, the specific EU trust-service status and validation support. |
Set retention and signature-acceptance rules for each transaction and jurisdiction. The cited sources do not establish one global retention duration for e-signature logs.
Sources and currency
The U.S. regulatory discussion above draws on 12 CFR Appendix B to Part 30 as reproduced by Cornell Legal Information Institute and on FFIEC Authentication and Access guidance. Confirm the official current CFR text, the rules applicable to the bank’s regulator, and the exact FFIEC guidance version used in procurement. The European Commission eIDAS Dashboard displayed version 2.32.0 dated 2026-05-27 when consulted; Trusted List entries and provider controls can change, so check the relevant service again during selection and renewal. The eIDAS-Node manual is older material used here only for general log-design considerations.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




