Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallCrashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteBefore asking an AI agent to assess a code change, ask a narrower question: What can this code do now that it could not do before? Sentinel MR Report 0.2.0 is presented by its author as a JavaScript-focused GitLab CI job that answers part of that question by comparing changed files and reporting capability differences. Its design illustrates a useful boundary for AI-assisted development: let deterministic tools establish observable facts, then use human or AI judgment to interpret them.
What Sentinel MR Report 0.2.0 is designed to do
Project author jackymenCZ describes Sentinel MR Report as a small CI job for JavaScript repositories. It compares old and new versions of changed .js files using Git objects available to the runner, parses the code with Tree-sitter, extracts structured facts, and reports changes in capabilities and risk. The output can be machine-readable, and configured policy can make the GitLab pipeline fail.
As an Amazon Associate I earn from qualifying purchases.
The author says this analysis runs in CI without an LLM, account, telemetry, API key, external analysis service, or remote source-code analysis. These are descriptions of version 0.2.0 in the author’s October 1, 2026 article, not findings from an independent audit of the implementation. Read the author’s description of Sentinel MR Report 0.2.0.
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Why a capability change can matter more than a risk score
A risk label compresses information. If a file is already rated critical, adding another dangerous capability may not raise its score. The capability surface has still changed: the code can now do something it could not do before.
#1 Best Overall
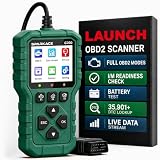
- 【PLUG IN AND START DIAGNOSING】 Connect the G700 directly to your vehicle’s OBD2 port and start scanning. No app, Bluetooth, Wi-Fi, account, charging or internal battery required—ideal for beginners and everyday car owners.
- 【READ AND CLEAR CHECK ENGINE CODES】 Read stored, pending and permanent engine fault codes, view code definitions and clear codes after the underlying problem has been repaired. Know what is happening before visiting a repair shop.
- 【FASTER DIAGNOSTICS WITH F1/F2/F3】 Press F1 to read codes, F2 to erase codes and F3 to check I/M readiness. Access frequently used functions instantly without navigating through multiple menus.
- 【COMPLETE OBD2 DIAGNOSTIC FUNCTIONS】 Access read/clear codes, live data, freeze frame, I/M readiness, vehicle information, O2 sensor data, Mode 6, Mode 8 and other standard OBD2 functions for everyday engine diagnostics.
- 【VIEW LIVE DATA AND REAL-TIME CURVES】 View live engine data, select important parameters and display two data items as real-time curves. Review changing values and identify abnormal trends more easily than reading numbers alone.
According to the author, version 0.2.0 can gate on a newly added dangerous fact as well as on a raised risk level, subject to the configured threshold. A rename or other edit that adds no dangerous fact does not meet that capability-change condition. That distinction makes the report a way to direct review toward new behavior rather than treating every file-level score as the whole story.
How to read a reported capability
A capability is an observation about what code can access or invoke, not proof of intent. Process execution, file-system access, environment reads, and network use can be legitimate parts of an application. A report that identifies a new capability supplies a review question; it does not answer whether the change is malicious, necessary, or safe.
Rank #2

- Instant Review Access: Visitors can access your review us sign instantly with a simple NFC tap or QR code scan. Functions as a Review Stand or NFC Tag, compatible with all smartphones
- Enhance Online Presence with Analysis Dashboard: Designed as a review us sign or business sign, it provides an analysis dashboard to monitor visitor engagement and interaction insights
- Simple Setup, No Apps or Subscription: Link your Review page once with this NFC & QR Code Stand. No apps, subscriptions, or technical setup needed. Update the link anytime without replacing the display
- Acrylic Counter Display: Made from clear acrylic, measuring approximately 4.45 × 6.30 in, with a stable insertable base. Sleek and professional design fits perfectly on counters, reception desks, or event table
- Compact & Versatile for Any Business: Perfect for restaurants, cafés, salons, boutiques, hotels, trade shows, or pop-up events. Keeps your review link visible and accessible, helping small businesses enhance credibility, SEO, and customer interaction
That distinction is relevant when reviewing AI-generated changes. A model can explain code, but a separate deterministic check may be better suited to establishing whether a concrete capability appeared in the diff. The project author summed up the architecture as: “Don’t make the AI rediscover facts that a deterministic program can establish reliably.” That is the author’s design principle, not a general technical standard.
What acknowledgements and thresholds change
Fact-level acknowledgements
The author says acknowledgements can identify accepted facts, such as child_process and process_spawn, rather than waiving an entire file by path. This is narrower: a reviewer can acknowledge a known capability without automatically accepting every future capability added to that file. The older string acknowledgement format remains supported, but the author says reports make its broader scope visible.
Rank #3
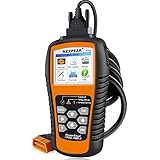
- 【Professional Car Code Reader】 NEXPEAK NX501 obd2 scanner is an enhanced auto scanner that you can not only check all engine related fault codes, find out what caused the check engine light comes on, turn-off Malfunction Indicator Lamp (MIL), locate bad O2 sensor, but also can monitor car battery health status, remind you when the battery need to be replaced. It’s a perfect scan tool helps you to determine if your car need to be repaired and avoid blind maintenance, saves your time and money.
- 【Wide Array of Compatibility】 Accurately read and erase error codes on all OBD2 protocol vehicles with a 16 PIN interface (KWP2000, ISO9141, J1850 VPW, J1850 PWM and CAN). The NEXPEAK NX501 automobile diagnostic is compatible with most US vehicles that are model year 1996 or later – including sedans, SUVs, light trucks, and 12V diesels. This is a plug-and-play engine diagnostic code reader (both generic and manufacturer specific codes) – no extra batteries or apps required.
- 【Not Only Full OBD2 Function】 All 10 modes OBD2 diagnostic function including: read and erase fault codes, retrieve I/M readiness and freeze frame data. Unique graphical forms to display live sensor data, Auto VIN acquisition, O2 Sensor and EVAP Test (Mode 8), Advanced On-board Monitoring (Mode 6). This auto code reader can not only reveal what error codes your car is producing, but also monitor the battery voltage at all time during OBD car diagnostic, reminds you when having an aging battery.
- 【BEST Stability and Performance】This NX501 OBD2 car computer reader does all diagnosis via 2.8’’ color LCD screen, features with user-friendly UI design and STM-32 main chip, this diagnostic code scanner can access OBDII car diagnostics, DTC Lookup and Review 2-3 times faster than other car diagnostic scanners. With patented design soft silicone keypad and Red-Yellow-Green LEDs indicators, you don’t even need to read the manual and will enjoy the car diagnostics just as the professionals.
- 【Warranty & Update】 The NX501 OBD2 code scanner supports life-time free smart update service, Built-in memory card allows you to store diagnostic data and upload to computers for printing (for Windows ONLY). The NX501 package comes with a free carry case It’s a must have tool for you and your family.
Thresholds and gradual risk changes
Policy configuration affects what blocks a pipeline. For example, with a critical threshold, risk can rise from low to medium to high across separate changes without triggering a block. Teams should therefore understand both the risk threshold and the separate new-capability condition before interpreting a passing pipeline as evidence that no meaningful change occurred.
What Sentinel does not establish
- It is described as JavaScript-only and per-file. It does not perform complete cross-file call-graph reasoning.
- Unsupported syntax is not safely inferred. Files using TypeScript or Flow syntax the current parser cannot handle are reported rather than guessed at.
- A capability delta is not a vulnerability verdict. It does not establish intent, exploitability, or whether a capability is appropriate in context.
- It is not presented as a replacement for mature security scanners. Its stated role is narrower: observe changes in capability surface.
Why capability visibility matters in CI
Socket Threat Research describes the SANDWORM_MODE supply-chain campaign as involving credential theft in developer and CI environments, exfiltration, repository and workflow modification, and targeting of AI development tooling. Its report identifies at least 19 malicious npm packages and discusses a weaponized GitHub Action. Socket also says public propagation through that Action had not been confirmed at the time of its investigation. These findings illustrate why reviewers may care about secret access, network communication, process execution, and workflow changes; they do not show that Sentinel detects or stops this campaign. Socket’s SANDWORM_MODE report recommends treating affected developer or CI environments as potentially exposed, rotating tokens and secrets, and checking repository metadata and workflow files.
Rank #4

- Upgraded AD310 with Bluetooth — Want the trusted AD310 with more flexibility? AD310BT combines the familiar handheld OBD2 scanner with Bluetooth connectivity, so you don't have to choose between the two. Whether you use the handheld or connect to your phone, you get the core OBD2 diagnostic functions for everyday engine and emissions checks. Use it the way that fits the moment—a simple handheld check with a car code reader, or connected diagnostics from your phone
- Check Engine Light & Smog Check — Check Engine Light on or getting ready for a smog check? Use this car check engine code reader to read engine trouble codes, understand what they mean, and clear codes after the problem is repaired. I/M Readiness shows whether required emissions monitors are ready, helping you check the issue before repairs and your readiness before heading to the test station
- Understand More Than the Code — Got a trouble code but still not sure what happened? Built-in DTC definitions explain the code, Freeze Frame shows key engine data recorded when the fault was detected, and Live Data lets you watch supported readings while the engine is running. See what happened then and what is happening now, so you have more information before deciding what to check next with this code reader for cars and trucks
- See More with the ANCEL App — Want an easier way to view and track vehicle data? The ANCEL App displays Live Data in clear graphs and a customizable Dashboard, making trends easier to follow on your phone. Connect this OBD2 scanner Bluetooth to view trip, performance and vehicle-voltage information, save diagnostic reports for later review, and use the app with no ads, no subscription fees and lifetime free updates
- Know What It Covers Before You Buy — AD310BT works with most 1996+ U.S. OBD2-compliant cars, SUVs and light trucks with a standard 16-pin port, making it a versatile Bluetooth code reader for compatible vehicles. It is designed for engine and emissions diagnostics and does not support ABS, SRS, transmission, TPMS or service-reset functions. Backed by a 2-year w-arranty and ANCEL customer support for added confidence after purchase
A separate 2026 paper by Wenyuan Xu and Anders Møller reports that 72.9% of its benign npm-package dataset used no security-sensitive capabilities after deduplication; its corresponding pre-deduplication figure is 59.4%. These are dataset-specific results under the paper’s capability definitions, not a claim that those percentages of npm are safe. The paper studies a separate defensive analysis system and does not validate Sentinel. Its proceedings are scheduled for ASE 2026 on October 12–16, 2026, so the conference had not yet taken place as of October 7, 2026. The 2026 paper by Xu and Møller.
Free tools Windows power users keep installed
One-click scans. No signup required.
How Sentinel’s role differs from general CI findings
Sentinel’s stated focus is a capability delta between versions of changed JavaScript files. Semgrep documents a broader policy-based model for findings: configured policies can use Block, Monitor, Comment, or Disabled modes, and blocking findings return an exit code that CI can use to stop a merge. Its documentation states, “The existence of any findings means that Semgrep returns an exit code of 1, which you can use to block your PRs or MRs.” Semgrep documentation: Handling blocking findings and errors.
Best Value

- NFC Review Tap Stand with QR Code
- Boost Reviews & Online Presence: a stylish review us sign. Provides visitor insights to monitor how often your review link is accessed, helping small businesses understand engagement and improve local SEO
- Insertable Base for Easy Setup;No Apps, Subscriptions: The stand comes with a separate small base, allowing quick assembly. Simply insert the acrylic display into the base, link your review page once, and it’s ready to use. No apps, subscriptions, or technical setup required
- Counter & Table Display: Made from premium acrylic, measuring approximately 4.45 × 6.30 in, with a transparent top for maximum visibility. Compact yet stable, perfect for counters, reception desks, or event tables.
- Compact & Versatile for Any Business: Ideal for cafés, restaurants, salons, boutiques, hotels, trade shows, or pop-up events. Keeps your review page accessible while enhancing credibility, customer interaction, and online presence
These approaches answer different questions. A capability-delta report asks what observable abilities changed; rule- or vulnerability-focused scanning asks whether findings match configured checks. The available sources do not establish a performance comparison, nor do they show that Sentinel has Semgrep’s language coverage or breadth. Choose based on the review question and treat the tools as potentially complementary rather than interchangeable.
Quick Recap
A cautious way to evaluate it in a repository
- Start with report-only observation. Run it against a repository the team understands before making reports merge-blocking, as the author recommends.
- Compare reports with human review. Check whether the reported facts match the actual changes and whether legitimate changes produce understandable results.
- Set policy deliberately. Decide which risk threshold should block, whether new dangerous facts should block, and whether acknowledgements should name specific accepted facts or use a broader legacy path-level waiver.
- Only then consider enforcement. A pipeline failure is a policy outcome, not a complete security verdict; preserve human review for intent, context, and cross-file behavior.
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




