Free tools Windows power users keep installed
One-click scans. No signup required.
Some recent attempts to exploit a years-old vulnerability in Realtek Jungle SDK devices have delivered Cling malware, but the observed activity does not mean every vulnerable device was infected—or that every exploit attempt succeeded. The analyzed Cling sample uses STUN-like network traffic to register and receive commands, while also installing persistence and attempting to spread to other devices.
What happened in the 2026 campaign
Nozomi Networks Labs reported on October 1, 2026, that anonymized customer telemetry showed a spike in attempts to exploit CVE-2021-35394. The Hacker News reported on October 5 that the spike began around September 5. The activity included opportunistic probing; in a subset of cases, attackers retrieved and executed a Cling sample.
As an Amazon Associate I earn from qualifying purchases.
CVE-2021-35394 affects the diagnostic component of Realtek Jungle SDK, commonly compiled as UDPServer. It was disclosed in 2021, but remains relevant because the SDK is embedded in products from multiple manufacturers, and some devices may still be unpatched. The National Vulnerability Database assigns the flaw a CVSS base score of 9.8. That is a severity rating for the vulnerability, not a measure of the campaign’s scale or the number of infections.
The 2026 reporting does not give a campaign-wide infection count or establish an actor identity. Its technical findings center on one analyzed MIPS sample, alongside supporting observations from related samples; details should not automatically be assumed to apply to every Cling variant.
#1 Best Overall
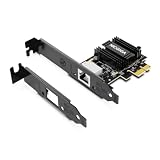
- ⭐【Next-Gen 10Gbe Performance】:Adopting the latest Realtek RTL8127 controller, this 10Gb PCIe network card delivers blazing-fast speeds up to 10Gbps. It provides extreme stability for local data transmission and internet access, effectively preventing packet loss. Perfect for NAS storage, home labs, gaming, and 4K video editing. Supports Wake-on-LAN (WOL).
- ⭐【Multi-Gig Auto-Negotiation】:Seamlessly backward compatible with 10Gbps, 5Gbps, 2.5Gbps, 1Gbps, and 100Mbps. It automatically negotiates the optimal speed to match your routers, switches, or NAS systems. Supports standard Cat6a/Cat7 or high-quality Cat6 cabling for cost-effective 10GbE network upgrades.
- ⭐【PCIe 4.0 x1 for Compact Systems】:Features a high-bandwidth PCIe 4.0 x1 interface that easily converts a standard x1 slot into a 10G RJ45 Ethernet port. Universally fits into PCIe x1, x4, x8, and x16 slots without occupying your GPU's lanes, making it ideal for Mini PCs, ITX builds, and compact workstations (Note: Not for PCI slots).
- ⭐【Broad OS & Advanced Linux Support】:Fully compatible with Windows 11/10 and Windows Server 2019/2022. Native plug-and-play for modern Linux distributions with Kernel 6.x and above (Ubuntu, Debian, Fedora), while older kernels (5.x) can be easily driven via Realtek official source code. Ready for mainstream virtualization and DIY NAS platforms.
- ⭐【Cool Running & Easy Installation】:Thanks to the ultra-efficient Realtek RTL8127 chipset, this 10G NIC consumes minimal power and generates significantly less heat than older 10G chips, ensuring non-stop stability. Includes both standard full-height and low-profile brackets to perfectly fit into slim or full-size desktop towers.
How Cling gets onto a device and persists
Exploit attempts and propagation
Nozomi describes exploit traffic as UDP datagrams beginning with orf; followed by shell commands. In one captured attempt, BusyBox wget fetched a binary, made it executable, and ran it with an infection-method tag such as realtek.selfrep. This is an example of a successful delivery path in the observed activity, not evidence that every probe delivered malware.
The analyzed MIPS sample also contained exploit logic for seven other command-injection vulnerabilities affecting devices associated with Realtek, Eir, MVPower, LB-LINK, FiberHome/China Mobile, TBK, and Linksys. That indicates capabilities built into the sample; it does not prove that all seven vulnerabilities were exploited during every infection.
Persistence mechanisms
The sample checks whether another instance is running by attempting to bind a socket on port 33957. It copies itself to /root/.cling and /usr/local/bin/.cling, and adds startup references to /etc/inittab, /etc/init.d/rcS, and /etc/rc.d/rc.boot on systems using SysV- or BusyBox-style startup.
Rank #2

- Coverage up to 2,000 sq. ft. for up to 25 devices
- Ultrafast AX3000 speeds up to 3Gbps with WiFi 6 technology for uninterrupted streaming, HD video gaming, and web conferencing
- This router does not include a built-in cable modem. A separate cable modem (with coax inputs) is required for internet service.
- Connects to your existing cable modem and replaces your WiFi router. Compatible with any internet service provider up to 1Gbps including cable, satellite, fiber, and DSL
- Plug in computers, game consoles, streaming players, and more with 4 x 1G Ethernet ports
Another method tampers with wget: the malware moves the legitimate executable to wget.r, records its location in wget.p, and replaces the original command. Later calls to wget can then launch the malware again.
How Cling uses STUN for command and control
STUN, or Session Traversal Utilities for NAT, normally helps an endpoint discover its public IP address and the port mapped by its network address translation (NAT) device. It is commonly used in real-time communications. In the analyzed Cling sample, STUN-like exchanges are repurposed for bot registration and command delivery.
- Probe STUN endpoints. The bot sends Binding Requests to a hard-coded list of 13 servers about every five seconds. The requests use an all-zero transaction ID, rather than the random ID expected by the protocol.
- Collect mapped ports. The bot records the externally observed ports associated with its connections.
- Register with a custom datagram. It sends those ports and an infection tag in a custom UDP datagram. This registration packet is not a conforming STUN message, so compliant STUN servers ignore it.
- Wait for encoded commands. The bot listens on the mapped ports for UDP packets whose 12-byte STUN transaction ID field encodes operator commands.
Nozomi identified 145.249.115[.]184 as suspicious after it responded to controlled Binding Requests with an all-zero transaction ID instead of echoing the request’s ID. In a validation test, researchers sent different port sets to that server and to other listed STUN endpoints. Several hours later, they received commands on a port advertised only to the suspected server. Nozomi assessed that the server was controlled by or colluding with the operator.
Command packets appeared to originate from 74.125.250[.]129, an address to which stun.l.google.com resolves. Nozomi assessed that the operator most likely spoofed that source IP address, citing consistent TTL differences between legitimate STUN responses and the command packets. The observed address is not evidence that Google operated the botnet or knowingly relayed its commands.
Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Clear out junk files and repair common Windows errors3Scan for outdated or missing drivers - takes under a minuteWhat commands the sample supports
The analyzed sample supports payload execution, scanning and exploitation, stopping its scanner, starting or stopping a TCP tunnel, starting or stopping a proxy relay, and flooding a specified target for a specified time. Nozomi observed commands to self-propagate and flood several targets. These findings describe behavior in the observed sample; they do not establish a botnet-wide infection count or the identity of the operator.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.“Cling is notable not because it introduces a new propagation technique, but because it repurposes ordinary STUN behavior into a practical command-and-control channel.”
Rank #4
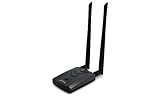 【New Version Type-C WiFi USB】 ALFA AWUS036ACH AC1200 WiFi 5 USB Adapter for Desktop PC, Wireless Network Card, Long-Range Dual-Band High-Gain Antenna System
- Wireless Standards IEEE 802.11ac/a/b/g/n
- Wireless Frequency: 2.4 GHz / 5 GHz; Wireless Data Rate: 2.4 GHz-up to 300 Mbps, 5 GHz-up to 867 Mbps.
- Interface: USB-C (includes cable); Antenna Type: 2 x Dual-Band High-gain detachable antenna.
- Wireless Security: WEP, WPA, WPA2, WPA3 WPA/PSK, WPA2-PSK
- Operating System: Windows Vista 32/64bit; Windows 7 32/64bit; Windows 8/8.1 32/64bit; Windows10 32/64bit; Linux kernel 4.19 or later.
Nozomi Networks Labs
How defenders can detect and respond
No single network indicator or file check is enough to establish that a device is infected. Combine device inventory, traffic monitoring, and host-artifact checks, then follow the device maker’s remediation guidance if you find suspicious activity.
1. Find exposed and potentially affected equipment
- Inventory internet-facing routers, access points, DVRs, and embedded appliances that may include Realtek Jungle SDK components.
- Include equipment from the other manufacturers and product categories implicated by exploit logic in the sample, without assuming every listed device or vulnerability was targeted.
- Confirm the exact model and firmware with the device vendor; the Nozomi report does not provide a universal affected-device list or firmware fix version covering every OEM.
2. Reduce exposure and remediate
- Apply the vendor’s firmware update for the affected device, where one is available.
- Restrict unnecessary internet exposure and inbound access, especially for devices that cannot yet be updated.
- Segment IoT and edge equipment from higher-value systems so a compromised appliance has fewer paths to other assets.
- Consider replacing unsupported devices for which the vendor provides no suitable remediation.
3. Monitor for protocol and host indicators
- Look for repeated STUN Binding Requests with all-zero transaction IDs, custom non-STUN UDP datagrams sent to STUN endpoints, and other traffic that differs from an asset’s normal baseline.
- Do not rely on destination reputation alone: the report’s analysis says command packets may have used a spoofed source address.
- On a suspected device, check for
.clingcopies, unexpected startup entries in/etc/inittab,/etc/init.d/rcS, or/etc/rc.d/rc.boot, and thewget.randwget.pfiles associated with a replacedwgetbinary.
4. Preserve evidence and follow vendor guidance
If a device may be affected, preserve relevant network and host evidence and use the device vendor’s remediation guidance. There is no single recovery procedure or firmware version that can safely be prescribed across the different manufacturers and models involved.
How to interpret the historical exploitation figure
Palo Alto Networks Unit 42 reported 134 million exploit attempts against CVE-2021-35394 between August and December 2022. That figure describes historical exploitation activity in that period, before the reported 2026 Cling campaign. It is not a count of Cling infections and should not be read as a current 2026 total.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




