Your encrypted data has not necessarily been hacked or decrypted. The concern is that an attacker could copy encrypted information now and keep it in case a sufficiently capable quantum computer can decrypt it in the future. That strategy is called “harvest now, decrypt later” (HNDL). It makes long-lived secrets a planning concern today—not proof that quantum computers can break ordinary encryption today.
What does “harvest now, decrypt later” mean?
An attacker using HNDL collects encrypted communications or stored data while it is protected by today’s cryptography, then retains those copies for possible decryption later. The attacker does not need a quantum computer to collect the data; the strategy depends on the possibility that future technology could make some current cryptographic protections vulnerable.
As an Amazon Associate I earn from qualifying purchases.
That possibility matters most when information must stay confidential for years or decades. NIST identifies health records, financial data, intellectual property, and national-security information as examples of data that could have long confidentiality lifetimes. The useful question is not simply whether information is encrypted, but how long it must remain secret and what harm disclosure would cause. NIST explains the HNDL risk and the value of protecting long-lived information.
Can quantum computers break encryption today?
No. NIST says current quantum computers are much too small and unstable to threaten the cryptography protecting ordinary communications. There is no settled date for when a cryptographically relevant quantum computer might exist; NIST says no one knows how long development will take, or even whether it will happen. Treat predictions of a precise “quantum deadline” as uncertain, not as an established countdown.
#1 Best Overall

- POWERFUL SECURITY KEY: The YubiKey 5 NFC is the most versatile physical passkey, protecting your digital life from phishing attacks. It ensures only you can access your accounts
- WORKS WITH 1000+ ACCOUNTS: Compatible with popular accounts like Google, Microsoft, and Apple. A single YubiKey 5 NFC secures 100+ of your favorite accounts, including email, password managers, and more
- FAST & CONVENIENT LOGIN: Plug in your YubiKey 5 NFC via USB and tap it, or tap it against your phone (NFC), to authenticate. No batteries, no internet connection, and no extra fees required
- MOST SECURE PASSKEY: Supports FIDO2/WebAuthn, FIDO U2F, Yubico OTP, OATH-TOTP/HOTP, Smart card (PIV), and OpenPGP. That means it’s versatile, working almost anywhere you need it
- PRIMARY & SPARE KEYS: Just like having a spare house key, we recommend buying two YubiKeys - one for daily use and one as a spare. That way you’ll never get locked out of your accounts
“Already compromised” is therefore a warning about potential future exposure, not a claim that every encrypted account has been breached, that an attacker has decrypted your data, or that every person is known to be under HNDL surveillance. The strategy is a reason to plan around sensitive information that needs protection far into the future.
Which cryptography is at risk, and what is post-quantum cryptography?
The main concern is widely used public-key cryptography, which supports tasks such as establishing encryption keys and creating digital signatures. A sufficiently powerful quantum computer running relevant algorithms could undermine some of those protections. That does not mean all encryption is already broken.
Rank #2

- Protect accounts with USB-C & NFC 2FA security key. Hardware-based authentication blocks phishing, credential theft & unauthorized access across cloud, enterprise & personal platforms.
- FIDO2 Level 2 certified Security Key. Works with Apple ID, Microsoft Azure/Entra ID, AWS, Google, Facebook, Salesforce, DUO & more. Compatible with Chrome, Safari & Edge on all major OS.
- Plug & play USB-C Security Key with NFC tap login. No software, drivers or batteries required. Works with Windows PC, MacBook, iPhone, Android & Chromebook for fast, secure authentication.
- Built with FIPS 140-2 Level 3 secure element for advanced encryption. Trusted by IT teams, healthcare, education & government for secure authentication & identity protection.
- IP68 waterproof, dustproof & crush-resistant design. Supports FIDO2, U2F, OTP, PIV, Mini Driver & smart card login. Durable USB security key for long-term enterprise & daily use.
Post-quantum cryptography (PQC) refers to algorithms designed to resist attacks by both conventional computers and future quantum computers. It is different from quantum cryptography, which is based on quantum physics. PQC aims to replace vulnerable cryptographic methods through software and protocol changes; it is not a special consumer device. NIST’s overview explains the distinction and the purpose of PQC.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Which post-quantum standards are available?
In August 2024, NIST finalized three PQC standards. They address key establishment and digital signatures, two different cryptographic jobs; one standard does not replace the others for every use. NIST says the standards can be put into use now and form the foundation for most deployments.
Rank #3

- Protect accounts with USB-A & NFC 2FA security key. Hardware-based authentication blocks phishing, credential theft & unauthorized access across cloud, enterprise & personal platforms.
- FIDO2 Level 2 certified Security Key. TAA compliant and supports Apple ID, Microsoft Azure/Entra ID, AWS, Google, Facebook, Salesforce, DUO & more. Works with Chrome, Safari & Edge across major OS.
- Plug & play USB-A Security Key with NFC tap login. No software, drivers or batteries required. Works with Windows PC, MacBook, iPhone, Android & Chromebook for fast, secure authentication.
- Built with FIPS 140-2 Level 3 secure element for advanced encryption. Trusted by IT teams, healthcare, education & government for secure authentication and identity protection.
- IP68 waterproof, dustproof & crush-resistant design. Supports FIDO2, U2F, OTP, PIV, Mini Driver & smart card login. Durable USB security key for long-term enterprise and daily use.
| Standard | Algorithm | Purpose |
|---|---|---|
| FIPS 203 | ML-KEM | Key encapsulation and key establishment |
| FIPS 204 | ML-DSA | Digital signatures |
| FIPS 205 | SLH-DSA | Digital signatures |
Additional algorithms, including Falcon and HQC, remain in standardization. Their mention is not a reason to delay planning around the three finalized standards. See NIST’s post-quantum cryptography project page for the standards and ongoing work.
What should individuals do now?
For most people, the practical response is to keep the software and services that handle their information current and ask providers about their PQC plans. The protection depends on adoption by the operating systems, applications, protocols, and service providers involved—not on buying a generic privacy gadget.
Rank #4

- FIDO2 & Passkey Ready: Business-ready and FIDO2 L1 certified. This key is supported by major management suites and is ideal for both individual and enterprise deployment. Works seamlessly with Gmail, Facebook, GitHub, Dropbox, Coinbase, and more.
- Universal Connectivity (USB-A ): Features a built-in USB-A connector—simply unfold the key and plug it into your compatible PC or laptop for seamless authentication on the go.
- Dedicated Manager App: Use the Thetis Manager App for the initial hardware PIN setup. Setting the PIN on the device first ensures a smooth registration process. Once the PIN is configured, you can begin registering the key across your favorite FIDO2-compatible online services.
- Ultra-Durable & Portable: Featuring a rotating metal cover, this key is water, crush, and tamper-resistant. It fits easily on a keychain and requires no batteries or network connectivity.
- Check FIDO2 compatibility before purchase - Known limitations: ID Austria is not supported (requires FIDO2 Level 2). Windows Hello login only works with Windows Enterprise editions that support Entra ID, and NFC is NOT supported.
- Install operating-system, browser, and application security updates as they become available.
- Use service providers that maintain their security, and ask whether and when the services you rely on plan to support post-quantum standards.
- Be especially attentive to services holding information whose exposure would still matter years from now.
NIST mathematician Andrew Regenscheid puts the immediate user action plainly: “The most effective thing you can do as a user is to ensure that your systems are updated.” NIST’s guidance for users does not prescribe a special consumer purchase as a solution.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Fix the driver behind crashes, sound loss and screen glitches3Clear out junk files and repair common Windows errorsWhat should organizations do to prepare?
Organizations need a migration plan because cryptography can be embedded across applications, infrastructure, suppliers, and older systems. The joint CISA, NIST, and NSA guidance recommends creating a roadmap, engaging vendors, identifying where cryptography is used, and prioritizing sensitive and critical assets.
Best Value
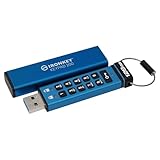
- FIPS 140-3 Level 3 (Pending) Certified Military-Grade Security
- OS/Device Independent
- XTS-AES Hardware Encryption
- Enforced Alphanumeric PIN
- Multi-PIN (Admin and User) Option
- Inventory cryptographic use. Identify systems, applications, data flows, and suppliers that rely on cryptography, including where quantum-vulnerable algorithms are used.
- Prioritize by confidentiality lifetime and impact. Find sensitive information that must remain secret for years, then assess the consequences of its future disclosure. Include critical systems in migration priorities.
- Ask vendors for specifics. Request their PQC plans, standards coverage, migration sequencing, legacy-system support, and interoperability or validation evidence. A broad promise of “quantum readiness” is less useful than a clear account of which functions and systems will change.
- Plan and sequence migration. Establish ownership, timelines, and procurement requirements, and include PQC in system modernization rather than waiting for a single deadline.
The joint agencies’ preparation guidance says to begin this work now. As Rob Joyce, then Director of NSA Cybersecurity, said: “The key is to be on this journey today and not wait until the last minute.” Read the joint CISA, NIST, and NSA recommendations.
What do the 2035, 2030, and 2027 dates actually mean?
These dates refer to different transition programs and should not be treated as universal deadlines for every consumer or business.
| Date | What it applies to | What it does not mean |
|---|---|---|
| 2035 | NIST’s plan to deprecate and ultimately remove quantum-vulnerable algorithms from its standards; NIST says high-risk systems should transition much earlier. | It is not a guarantee that every product or organization will be migrated by 2035. |
| 2027 | NSA’s CNSA 2.0 schedule: new commercial National Security Systems (NSS) must support the quantum-resistant algorithms by this year. | It is not a deadline for all commercial products, businesses, or consumers. |
| 2030 | NSA’s CNSA 2.0 schedule to phase out legacy systems in scope of that National Security Systems program. | It is not a general phase-out date for legacy systems everywhere. |
NIST’s date is part of its standards transition plan, while the 2027 and 2030 dates belong to NSA’s CNSA 2.0 requirements for National Security Systems. Check the scope before applying any of these dates to a particular organization. NIST describes its standards transition; NSA describes the CNSA 2.0 milestones.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




