The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Continuous secure delivery for infrastructure as code (IaC) means governing the full path from a proposed infrastructure change through review, testing, authorization, deployment, and monitoring—not relying on a one-time file scan. Treat IaC, policy code, and configuration code as parts of the software supply chain, and apply security controls to both the code and the systems that deliver it.
What continuous secure delivery means for IaC
Infrastructure code defines details of the platform on which software will run. A change to that code can therefore affect the environment that applications depend on, as well as its security settings and operating behavior.
As an Amazon Associate I earn from qualifying purchases.
NIST Special Publication 800-204D, issued in February 2024, says pipeline activities and security requirements should cover application code, infrastructure as code, and policy or configuration code that specifies runtime settings. Its guidance concerns software supply-chain security in DevSecOps pipelines; it does not prescribe one universal pipeline architecture or approval model.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Continuous delivery is the controlled, repeatable path that makes a change deployable. Continuous deployment goes further by deploying changes automatically under the organization’s chosen conditions. A team can use automated delivery checks and still require a person to authorize a production deployment; the sources do not require one approval approach for every organization.
#1 Best Overall

- Ultra-Compact FIDO2 Security Key - Plug-and-stay or carry on a keychain. This USB-A hardware security key offers portable, always-on protection for desktop and mobile use. (Item Size: 0.75 X 0.74 IN x 0.25 IN)
- USB-A Hardware Key for All Devices - Works with USB-A ports on PC, Mac, Android, and other laptop/notebook device. Enables secure, cross-platform login with FIDO2.0 passkey support.
- FIDO Certified Security Key - Meets FIDO and FIDO2 standards. Works with Google, Microsoft, GitHub, Dropbox, and more. Please check service compatibility before purchase.
- Passwordless Login with Passkey - Supports passkey login via WebAuthn and CTAP2. Enjoy password-free sign-ins where supported. Not all websites or services currently support passkeys.
- Advanced Multi-Factor Authentication - Offers 200 FIDO2 passkey slots and 50 OATH-TOTP slots. Strong, flexible 2FA/MFA support across various apps and authentication platforms.
What a secure IaC delivery path needs to control
Map the actual workflow before choosing individual controls. The sequence below is a practical planning framework based on NIST guidance, not a mandatory stage list.
- Source and review: Identify where infrastructure, policy, and configuration changes are proposed and reviewed, and define who can commit or approve them.
- Validate and test: Run repeatable checks appropriate to the change. Decide which findings block progress, which can be accepted as exceptions, and who is authorized to make that decision.
- Build or prepare the change: Control who or what can generate builds, packages, plans, or other delivery artifacts, and protect the environment where those operations run.
- Authorize and deploy: Restrict deployment authority to the identities and roles that need it. Make any human approval or automated authorization rule explicit.
- Record evidence and observe results: Connect the delivered change to relevant review, checks, build context, and deployment evidence, then monitor the environment and feed findings into remediation.
Protect the pipeline as infrastructure
Pipeline runners, build agents, and deployment stages can hold access to source, artifacts, or cloud environments. NIST recommends hardening the CI/CD execution environment, using a secure and isolated build platform, hardening build servers, and controlling authentication and authorization for build participants. In practice, that means treating the systems that execute delivery as sensitive infrastructure rather than as neutral plumbing.
Define roles for pipeline actors and grant granular permissions for tasks such as committing source, generating builds or packages, and checking artifacts into or out of repositories. A pipeline identity should have only the authority its task requires; privileged deployment permissions deserve particular care. These are least-privilege applications of the guidance, not a mandate for a particular credential pattern, approval gate, or identity product.
Recommended Free Tools
Rank #2

- FIDO2 & Passkey Ready: Business-ready and FIDO2 L1 certified. This key is supported by major management suites and is ideal for both individual and enterprise deployment. Works seamlessly with Gmail, Facebook, GitHub, Dropbox, Coinbase, and more.
- Universal Connectivity (USB-A ): Features a built-in USB-A connector—simply unfold the key and plug it into your compatible PC or laptop for seamless authentication on the go.
- Dedicated Manager App: Use the Thetis Manager App for the initial hardware PIN setup. Setting the PIN on the device first ensures a smooth registration process. Once the PIN is configured, you can begin registering the key across your favorite FIDO2-compatible online services.
- Ultra-Durable & Portable: Featuring a rotating metal cover, this key is water, crush, and tamper-resistant. It fits easily on a keychain and requires no batteries or network connectivity.
- Check FIDO2 compatibility before purchase - Known limitations: ID Austria is not supported (requires FIDO2 Level 2). Windows Hello login only works with Windows Enterprise editions that support Entra ID, and NFC is NOT supported.
Isolation and access control address different risks: permissions limit what an actor can do, while a hardened, isolated execution environment helps protect the machinery performing the work. Both matter because a compromised delivery system may be able to affect downstream deployments even when the infrastructure code itself has been reviewed.
Build checks into the change workflow
Apply security requirements to infrastructure, policy, and configuration changes as well as application source. NIST’s broader CI/CD guidance discusses security testing tools such as static and dynamic application security testing and software composition analysis. Those categories do not, by themselves, establish which IaC checks a team must use or how a particular scanner behaves.
For IaC workflows, teams can define checks around static configuration review, policy-as-code rules, and examination of proposed changes. These are useful categories for designing the workflow, not a product recommendation or a claim that one check is sufficient. The important operational choice is to make checks repeatable and connect their results to a defined decision: proceed, remediate, or handle an authorized exception.
Rank #3

- A FIDO security key with PUF technology provides a unique, hardware-rooted trust anchor that resists tampering and cyber attacks, offering stronger security than conventional designs.
- FIDO2 Certified Protection – Enjoy phishing-resistant security with FIDO2 certification, ensuring top-tier account safety across Windows, macOS, Linux, iOS iOS, Android and more.
- Easy to use & Portable – Designed with a compact USB-C interface, Clife key fits easily on your keychain for secure access anywhere. Simply plug in and authenticate with ease.
- Universal Compatibility – Works seamlessly with hundreds of FIDO2/U2F compliant services, including popular cloud, email, and social platforms.
- Backup recommended – To ensure continuous access, register a backup Clife security key as a spare in case your primary key is lost.
NIST’s NCCoE DevSecOps guidance describes security checks integrated into CI/CD, security configurations and policies managed as code, vulnerability management, and continuous monitoring. It also frames zero trust around consistent, policy-driven authentication, authorization, and least privilege. These practices support making security checks part of the ordinary change path rather than an occasional activity detached from delivery.
Make authorization meaningful
Automated checks do not settle every deployment decision. Teams need to decide which changes can proceed automatically, which need additional authorization, and who may grant it. NIST calls for defined pipeline roles and granular authorization; NSA and CISA also identify authentication and access control as areas to address when defending CI/CD environments.
Keep the authorization decision tied to the change and the authority being exercised. For example, permission to propose or validate infrastructure code need not automatically include permission to deploy it. The appropriate separation depends on the organization’s workflow and risk; the cited guidance does not prescribe a single approval design.
Rank #4

- Manufactured by Hirsch Secure, Inc. — formerly Identiv. PHISHING-RESISTANT SECURITY: FIDO Alliance-certified SecureKey stores site-specific cryptographic credentials on-device to help defend against phishing, password theft and replay attacks. PASSWORDLESS + MFA: Supports FIDO2, U2F and WebAuthn for passwordless sign-in, 2FA and MFA. USB-C + NFC: Works with compatible laptops, desktops and mobile devices across Windows, macOS, Linux, ChromeOS, Android and iOS. MULTI-PROTOCOL: Supports HOTP and PIV, with SecureKey Manager for FIDO2 PIN and device management. TAA COMPLIANT: Built for personal, business, enterprise and government use. Register a second key as backup.
Keep evidence with the delivered change
NIST recommends generating build-attestation evidence concurrently with software delivery to demonstrate compliance with secure build processes. The NCCoE DevSecOps guidance also includes artifact integrity and verification of code commits and signatures among practices for strengthening DevSecOps.
For an infrastructure change, useful evidence should let the team relate the delivered result to its source change, review, checks, build context, and deployment. This is a practical synthesis of the guidance: evidence is most useful when it travels with delivery and can support investigation or audit, rather than being reconstructed later from disconnected records.
Continue security work after deployment
A successful deployment is not the end of the security process. The NCCoE guidance includes continuous monitoring, vulnerability management, and feedback. Teams should use operational findings to inform remediation and future changes, closing the loop between what the pipeline delivered and what the running environment reveals.
Best Value
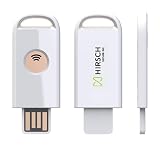
- Manufacturer Information: Manufactured by Hirsch Secure, Inc. - formerly Identiv
- Phishing-Resistant Security: FIDO Alliance-certified SecureKey stores site-specific cryptographic credentials on-device to help defend against phishing, password theft and replay attacks
- Passwordless and Multi-Factor Authentication: Supports FIDO2, U2F and WebAuthn for passwordless sign-in, 2FA and MFA
- USB-A and NFC Connectivity: Works with compatible laptops, desktops and mobile devices across Windows, macOS, Linux, ChromeOS, Android and iOS
- Multi-Protocol Support: Supports HOTP and PIV, with SecureKey Manager for FIDO2 PIN and device management
Manual, ad hoc evidence production can become inconsistent or risky, so make evidence generation and review part of the workflow where feasible. Monitoring and remediation should connect back to the people and processes that can correct infrastructure, policy, or configuration code.
Why the pipeline itself is a security target
In a June 28, 2023 announcement, NSA and CISA warned that attackers can use CI/CD environments to compromise cloud deployments. The agencies identified risks including introducing malicious code, stealing intellectual property or trade secrets, and causing denial of service. They emphasized defenses involving authentication and access control, development environments and tools, and the development process.
NSA Technical Director for Critical & Emerging Technologies Dr. Ethan Givens summarized the concern: “Failure to effectively defend the CI/CD pipeline can provide an attack vector that circumvents security policies and products.” The implication for IaC is that securing the configuration is not enough if an attacker can manipulate the process that validates, packages, or deploys it.
Quick Recap
A practical starting checklist
- Inventory the pipeline stages and the identities, systems, and repositories involved.
- Include IaC, policy code, and configuration code in the defined security requirements.
- Harden and isolate execution and build environments, and control access to them.
- Assign granular roles for source changes, builds, artifact handling, and deployment.
- Make relevant security checks repeatable and define how findings and exceptions are handled.
- Generate build and artifact evidence alongside delivery and retain a connection to the change.
- Monitor deployed environments and feed vulnerability and operational findings back into remediation.
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




