Secure access across global data centers requires a policy for each person, device, workload, application, and data resource—not simply a VPN or a trusted internal network. Authenticate and authorize before granting access, limit each session to its approved resources, and combine identity controls with network restrictions, monitoring, and recovery planning.
What secure access means in a distributed environment
A global data-center environment can include on-premises facilities, cloud infrastructure, SaaS, and cloud-native services running across providers. Its access paths include more than employee logins: administrators connect to management interfaces, workloads call other services, and applications reach data stores. Each path needs an identified owner, a business purpose, and controls suited to the resource.
NIST’s Zero Trust Architecture, SP 800-207, centers protection on resources rather than network segments. It says that a user’s or asset’s physical or network location, or ownership, is not by itself a reason to trust it. Authentication and authorization of both subject and device occur before an enterprise-resource session is established. In practical terms, being in a corporate office, on a private network, or connected through a VPN does not settle whether a particular request should be allowed.
Use the requested resource, the identity making the request, relevant device or workload context, and policy to make an access decision. This is a design principle, not a claim that every platform exposes the same context signals or implements them in the same way.
#1 Best Overall

- AI Motion Detection 2.0 – Driving AI to the next level, human&vehicle detection and flexible detection area are more accurate than before. For quicker locating in crucial moments, human&vehicle smart searching in recordings offers you great help.
- Tried-and-True Safe Guard – This one-stop security solution can work with TVI, AHD, CVI, CVBS & IP cameras, the kit includes 1080P cams. The 8CH 3K lite DVR can hook up with 1080P@30fps or 3K/5MP@20fps cams. Therefore, you can also DIY it with other cameras in your home.
- Reliable 24/7 Continuous Recording – With a pre-installed 1TB HDD(Support up to 10TB HDD), providing 24/7 surveillance recording for you. Upgraded H.265+ saves more storage space and uses less bandwidth, recording videos longer and smoother viewing.
- Smart Dual-Light Effectively Guard Your Home – This newly upgraded security system offers you a crisp full color night vision, IR mode and color night vision switch flexibly. Once detect intruders, immediate pushes pop up on your phone, securing your peace of mind day&night.
- Color Night Vision & IP67 Weatherproof – Built-in IR lights and white lights, these cameras can see up to 100ft in B&W night vision, full-color night vision up to 66ft. Rated IP67, these wired cameras can brave all weather, and stand from cold to hot.
How to secure access across global data centers
- Inventory important resources and paths. Identify administrative interfaces, workloads, applications, data stores, service-to-service calls, and remote operations. Record who owns each resource, which identities need access, and why. CISA’s cloud architecture guidance treats asset management and visibility as integrated security capabilities.
- Establish identities for people and workloads. Govern human accounts centrally where feasible, and give application services distinct identities rather than treating service traffic as anonymous or implicitly trusted. NIST SP 800-207A addresses identities for application services as well as users in hybrid and multi-cloud environments.
- Set explicit access rules. Define which identity may reach which resource, for what purpose, and under what relevant conditions. Evaluate device state or workload identity when the platform and policy can reliably use those signals. Microsoft’s Azure zero-trust guidance describes user, device, location, and workload as contextual inputs in its own implementation; those inputs should not be assumed to be available identically in other environments.
- Reduce privilege and access duration. Grant only the roles required for the task and, where operations allow, avoid standing administrative privilege. Make exceptions explicit, owned, and reviewable rather than allowing them to become untracked permanent access.
- Constrain paths between services and locations. Use network segmentation alongside application-level policy so that one compromised system cannot automatically reach every other system. For distributed applications, NIST SP 800-207A describes combining identity-tier and network-tier policies, including gateways and service-identity infrastructure.
- Secure remote administration. Require phishing-resistant MFA for VPNs and accounts that access critical systems where supported. CISA’s StopRansomware guidance recommends this protection for critical access. A compatible FIDO2 security key is one possible way to implement phishing-resistant or passwordless MFA; confirm identity-provider compatibility and organizational policy before choosing a device.
- Log decisions and rehearse recovery. Retain enough access and activity information to investigate denied or suspicious requests, identity compromise, and lateral movement. Test incident response and recovery, including recovery of critical services and data. Microsoft’s Azure examples include monitoring and immutable backups; the particular implementation depends on the environment.
Is a VPN enough for data-center access?
A VPN can provide a remote connection, but it does not by itself establish that a user or device should access every resource reachable from the resulting network. Its security depends on configuration, identity controls, scope, and how access is monitored. CISA and partner agencies’ June 18, 2024 guidance on modern network access security discusses vulnerabilities and threats associated with traditional remote access and VPN deployments, including business risk from misconfiguration.
Assess VPN, zero-trust network access (ZTNA), secure access service edge (SASE), and security service edge (SSE) approaches against the workloads and risks in your environment. These labels describe different architectural approaches, not a universal ranking. The joint CISA guidance advises organizations to assess their needs and security posture and make an informed decision based on comprehensive analysis before selecting a solution.
Rank #2
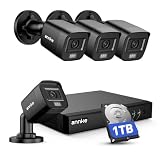
- 【AI Motion Detection 2.0】Driving AI to the next level, human&vehicle detection and flexible detection area are more accurate than before. For quicker locating in crucial moments, human&vehicle smart searching in recordings offers you great help.
- 【Tried-and-True Safe Guard】This one-stop security solution can work with TVI, AHD, CVI, CVBS & IP cameras, the kit includes 1080P cams. The 8CH 3K lite DVR can hook up with 1080P@30fps or 3K/5MP@20fps cams. Therefore, you can also DIY it with other cameras in your home.
- 【Reliable 24/7 Continuous Recording】With a pre-installed 1TB HDD(Support up to 10TB HDD), providing 24/7 surveillance recording for you. Upgraded H.265+ saves more storage space and uses less bandwidth, recording videos longer and smoother viewing.
- 【Smart Dual-Light Effectively Guard Your Home】This newly upgraded security system offers you a crisp full color night vision, IR mode and color night vision switch flexibly. Once detect intruders, immediate pushes pop up on your phone, securing your peace of mind day&night.
- 【Color Night Vision & IP67 Weatherproof】Built-in IR lights and white lights, these cameras can see up to 100ft in B&W night vision, full-color night vision up to 66ft. Rated IP67, these wired cameras can brave all weather, and stand from cold to hot.
How to compare access architecture choices
Compare designs by how they control access and how they behave operationally, rather than by acronym alone.
| Decision area | Questions to ask | Why it matters |
|---|---|---|
| Access scope | Does a connection provide broad network reach, or access to named applications and resources? | Narrower resource-specific access can limit what a compromised account or device can reach. |
| Policy inputs | Does a decision consider only user identity, or also device state, workload identity, resource sensitivity, and relevant risk context? | Identity is essential, but different requests and resources may warrant different conditions. |
| Enforcement placement | Are rules enforced through an identity provider, gateway or proxy, workload, service mesh, network segmentation, or a combination? | Distributed applications may need both identity-tier and network-tier enforcement, as described in NIST SP 800-207A. |
| Environment coverage | Can the design cover legacy data-center systems, cloud infrastructure, SaaS, and cloud-native services across providers? | A policy that only reaches one part of the estate leaves other access paths to be governed separately. |
| Operations | Who owns policies and exceptions? How will teams troubleshoot access, handle migrations, and maintain logging? | A control that cannot be operated consistently can produce unmanaged exceptions or blind spots. |
| Failure behavior | What happens when the identity provider, policy service, network, or telemetry is unavailable? | Define which actions must fail closed, what emergency access is permitted, and how that access is recorded and reviewed. |
Layer controls around the access decision
Identity policy is only one part of the design. Combine it with segmentation, encryption, monitoring, and recovery controls appropriate to the systems involved. CISA’s cloud architecture guidance emphasizes integrated identity, asset, network, application, and data protections, together with automation, governance, and visibility. Microsoft’s Azure guidance offers implementation examples such as segmentation, encryption, monitoring, and immutable backups; these are vendor-specific examples rather than a vendor-neutral certification checklist.
Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Repair Windows errors before they cause bigger problemsFix Now →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Rank #3
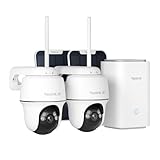
- 4K 8MP FULL-COLOR FOOTAGE DAY & NIGHT: Experience the ultimate clarity in the 4K 8MP footage. From day till night, the system captures every detail in vivid color, ensuring unparalleled visibility around the clock thanks to the spotlight color night vision.
- 100% WIRE-FREE + 2.4/5GHZ WI-FI: With the flexibility of both 2.4GHz for extended coverage and 5GHz for faster data rates, the home hub and the included cameras provide a more reliable connection. Made 100% wire-free, they save you from wiring hassles.
- 360° COVERAGE + MONITOR POINT: With 355° pan and 140° tilt capabilities, the cameras included rotate their eyes to monitor every corner. Besides, you can set your own monitor Point, the camera will return to that point automatically after deviating according to the time set.
- Up to 8 Cameras Centralized Management: The Home Hub supports up to two 512GB microSD cards, enabling connection of up to 8 cameras for comprehensive surveillance. Enjoy centralized camera management without subscriptions.(microSD card NOT included)
- Security Summaries & Smart Alarm Center: Stay on top of what's happening around your home with daily, weekly, and monthly event summaries. Easily track motion-triggered events and quickly access video footage through the app. Plus, siren alerts help deter intruders with immediate, loud notifications when suspicious activity is detected. Whether you’re at home enjoying family time or traveling for work, you’ll always be in the know.
- Identity: Authenticate people and services, use strong MFA for critical access, and constrain roles and duration.
- Network and application paths: Restrict east-west traffic and apply policy at the resource or application level where feasible.
- Data: Apply encryption and access policy suited to the data and its storage or transmission context.
- Detection and recovery: Monitor access and activity, investigate suspicious behavior, and test recovery procedures.
- Governance: Assign policy and resource owners, review exceptions, and maintain visibility across locations.
Plan for outages and exceptions
Global systems depend on identity, policy, network, and monitoring components that may not always be available. Decide in advance how access behaves during an outage: which work can stop safely, which narrowly scoped emergency actions are essential, and how emergency access will be authorized, logged, and reviewed afterward. Avoid letting a temporary exception silently become a permanent alternate route.
Keep the design specific to the organization’s systems and operating constraints. NIST SP 800-207 and SP 800-207A provide vendor-neutral architecture guidance; Microsoft’s examples are Azure-specific. CISA’s joint network-access guidance was released June 18, 2024, and NIST SP 800-207A was finalized in September 2023. Consult the current source publications and relevant local requirements when applying the guidance; this article does not establish country-specific regulatory obligations.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




