Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Fix the driver behind crashes, sound loss and screen glitches3Clear out junk files and repair common Windows errorsTrivy can scan Java dependency inputs—including a built JAR, a Maven POM, or supported Gradle and SBT lockfiles—and can separately scan the files and configuration in a container image. Those inputs do not produce identical results. Choose the one that matches what you want to check, and treat a clean scan as evidence only about the artifacts and checks Trivy detected, not proof that the application is secure.
Choose the Java input that matches your question
Trivy documents four Java input groups: JAR/WAR/PAR/EAR, pom.xml, *gradle.lockfile, and *.sbt.lock. The Java coverage page marks SBOM and vulnerability scanning as available for each. License detection is marked for POM and Gradle lockfiles, but not for JAR/WAR/PAR/EAR or SBT lockfiles in the documented coverage table. Check the Trivy Java coverage documentation for current release-specific coverage.


As an Amazon Associate I earn from qualifying purchases.
| Input | SBOM | Vulnerabilities | Licenses | Input-specific behavior |
|---|---|---|---|---|
| JAR, WAR, PAR, or EAR | Supported | Supported | Not marked in Trivy’s coverage table | Includes dependencies, including development dependencies; metadata is gathered from pom.properties and MANIFEST.MF. |
pom.xml |
Supported | Supported | Supported | Uses Maven repositories for package information; development dependencies are excluded by default. |
*gradle.lockfile |
Supported | Supported | Supported | Read locally; internet access is not required to read the lockfile. Development dependencies are excluded by default. |
*.sbt.lock |
Supported | Supported | Not marked in Trivy’s coverage table | Local input that must be generated with the sbt-dependency-lock plugin. |
Dependency-graph and source-position information are not established in the documented coverage details summarized here, so do not assume those capabilities from the file type alone.
Scan the built artifact to inspect what you package
A JAR or other supported archive is useful when you want Trivy to inspect the assembled artifact rather than infer its contents from a build declaration. The Java documentation says archive scans include dependencies. It also identifies metadata sources as pom.properties and MANIFEST.MF, so the result depends on metadata available in the artifact.
#1 Best Overall
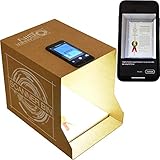
- Flatbed scanners simply cannot compete with your smartphone and a Scanner Bin. Improved resolution and color rendering compared to popular flatbed scanners. Compare to 1200 DPI. Takes a fraction of the time to scan at a fraction of the cost. Not to mention that flatbed scanners end up adding a lot of hazardous e-waste to your local landfill.
- Solve the common issues with smartphone scanning. Provides a contrasting background for consistent edge-detection and auto-cropping. Controls the lighting and provides stability and proper positioning while you scan with your smartphone.
- Scan photographs, receipts, letters, notes, artwork, fragile documents, etc. Also used as an aid for the blind or visually impaired or as a document camera for remote learning. When you aren't scanning, turn on its side to use as a desk-side bin to toss in the items you want to scan later.
- This version is the lowest cost option for a scanner solution. It is also simplified for set up and use, and therefore is recommended for those who are blind, visually impaired or have movement disorders.
- Use with popular FREE APPS for document scanning like Adobe Scan, Scanbot, Evernote Scannable, CamScanner, and Prizmo Go
Scan a POM to analyze Maven declarations
A POM scan is not simply a local parse of a completed dependency lock. Trivy uses repositories declared in the POM under its documented repository-selection rules, with Maven Central also used for applicable release artifacts. Snapshot artifacts use configured snapshot repositories when present; other artifacts use configured release repositories when present and Maven Central. Repository lookup supplies package information; it is distinct from the vulnerability database used to identify known issues.
Use lockfiles for resolved build inputs
Gradle lockfiles are read locally, as are SBT lockfiles. This avoids the need to contact a package repository just to read those files, but it does not mean Trivy’s vulnerability database is unnecessary. For SBT, the lockfile must be produced with the sbt-dependency-lock plugin.
Account for Maven scopes and development dependencies
Trivy’s Java documentation says POM analysis includes Maven scopes import, compile, runtime, and an empty scope. Other scopes and optional dependencies are not currently analyzed. These are implementation details that can change between Trivy releases, so verify them against the version used in your workflow.
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minute- For POM and Gradle lockfile scans, development dependencies are excluded by default. Add
--include-dev-depswhen you want them included. - JAR/WAR/PAR/EAR scanning is documented as including development dependencies.
- A Maven dependency may be missed or lack a usable version if its parent POM cannot be reached, a hard requirement specifies more than one version, or a dependency has no version; the Java documentation notes that child dependencies are not detected in the last case.
These differences mean that a POM, lockfile, built archive, and packaged image can produce different dependency inventories. For repeatable checks, scan the artifact relevant to the question and record the Trivy version and input used.
Scan the final container image as a separate check
Image scanning covers more than the Java dependency files. Trivy distinguishes files inside the image from image configuration metadata. For image files, vulnerability and secret scanning are enabled by default. License scanning is disabled by default; cryptographic-asset scanning is experimental, disabled by default, and uses CycloneDX output. See the container-image documentation for the current options.
Image configuration checks are a separate target. To enable misconfiguration scanning of image metadata, use --image-config-scanners misconfig. To enable metadata secret checks, the documentation shows --image-config-scanners secret. These options concern image configuration, not the files within the image.
Rank #4

- TRAVEL-READY FILM CONTAINER – Carry up to nine 35 mm film cassettes with confidence through airport security and customs checks. This lead-lined film container helps reduce the risk of X-ray-related fogging and streaking from low-dose carry-on screening, helping preserve unprocessed film before development
- CARRY-ON SAFE TRAVEL USE ONLY: Always pack this lead film bag for airport xray screening inside your cabin luggage, as this protective film case is engineered for low-dose scanners only and cannot shield film from the intense, repeated X-ray exposure commonly used on checked baggage, helping serious film shooters avoid hidden damage on long trips.
- TRIPLE-SHIELD DURABLE PROTECTION: Engineered as a rugged film case with a tough ballistic nylon exterior, dense lead‑impregnated vinyl core, and smooth snag free inner lining, this xray proof bag keeps each roll securely cushioned and easy to access, delivering dependable film storage for photographers who refuse to risk their images in transit.
- ORGANIZED STORAGE WITH QUICK ACCESS – Keep film rolls neatly contained and ready for your next shoot with this film case's full-length hook-and-loop closure that helps block dirt, dust, and light moisture. A practical travel accessory for film photographers, analog hobbyists, and creative professionals.
- SMALL SIZE, EVERYDAY CONVENIENCE – Measuring 5.25 x 8 in. (13 x 20 cm), this compact film container fits easily inside camera bags, backpacks, and carry-on luggage while providing dedicated storage for up to nine 35 mm film cassettes or a small camera, making it a practical travel accessory for film photography.
Misconfiguration scanning is not enabled by default for the image, fs, and repo commands. It can be combined with vulnerability and secret scanning, and is intended for configuration and infrastructure-as-code files such as Docker, Kubernetes, Terraform, and CloudFormation. The misconfiguration-scanning documentation explains the scanner’s scope.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Separate package access from vulnerability database access
For Java vulnerability findings, Trivy documents the GitHub Advisory Database for Maven. Trivy automatically fetches and caches relevant vulnerability databases during vulnerability scans; the vulnerability-scanning documentation describes the data sources and database behavior.
Best Value

- 【RFID Signal Protection】RFID blocking sleeve is engineered with aluminum foil coating that blocks all 13.56MHz frequency signals used by skimmers. Creates a Faraday cage effect to prevent unauthorized scanning, skimming, or digital theft of your card information.
- 【Universal Card Fit】Credit card protector holders are precisely sized at 8.7x5.8cm (3.43x2.28in) with ultra-slim 0.3mm profile to accommodate credit cards, IDs, and passports. The dimensional accuracy ensures complete coverage without bulk, seamlessly integrating into any wallet.
- 【Durable Waterproof Composite Material】RFID wallet women card sleeves are constructed with rigid aluminum foil layered between tear-resistant polymer sheets. Provides scratch protection, water resistance, and structural integrity while maintaining flexibility for easy card insertion/removal.
- 【Effortless Daily-Use Design】RFID identity card protector features smooth inner lining for frictionless card access and snug fit without adhesive or modifications. The minimalist design works equally well for travel security and everyday wallet organization without inconvenience.
- 【Comprehensive Financial Document Protection】RFID card holder safeguards credit/debit cards, IDs, passports, and access cards from both electronic theft and physical damage. Essential for urban commuting, international travel, and protecting sensitive personal information.
The Java option --offline-scan affects Maven repository access, not Trivy’s vulnerability database download. Trivy still downloads its database, and dependencies unavailable locally may be skipped. Therefore, an offline Maven repository lookup is not the same as a fully network-isolated vulnerability scan: package availability and database availability are separate concerns.
Quick Recap
Build a scan sequence around the deliverable
- Check the Java dependency view. Scan the POM, lockfile, or built archive that answers your question. Use a lockfile when you want to analyze that resolved input; use the built artifact when you want to inspect the assembled package.
- Decide whether development dependencies belong in scope. For POM and Gradle lockfile inputs, add
--include-dev-depsif your policy requires them. Do not assume that the default inventory includes them. - Scan the image you intend to ship. Run an image scan after packaging so findings reflect the container’s files, not only the source build declaration.
- Enable non-default checks deliberately. Choose license scanning or image metadata misconfiguration/secret checks when they are needed; their defaults differ from vulnerability and secret checks on image files.
- Review findings in context. Interpret results against the scanned input, enabled scanners, available repositories, and vulnerability database. A clean result cannot establish coverage of unsupported or unavailable dependencies.
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




