Reduce the risk of remote compromise by prioritizing vulnerabilities that are both exploitable and reachable, applying security updates through your distribution’s supported process, limiting network exposure, hardening SSH without locking out administrators, and verifying the result with suitable scans. The commands and procedures below are explicitly for Red Hat Enterprise Linux (RHEL) 8 or 9 where noted; package management and security tooling differ across Linux distributions.
Start with an inventory and a baseline
Before changing a server, establish what it runs and what can reach it. Record its distribution and release, support status, installed packages, enabled services, listening ports, SSH policy, maintenance constraints, and the clients or networks that need access. For each security advisory, verify that the affected product, release, architecture, and package stream match the host. Red Hat advisories identify affected products, severity, fixed issues, and associated CVEs.
This baseline separates a package finding from a practical exposure. A vulnerable component may be installed but not reachable in the current configuration; a later configuration or software change can create an exposure path, so that condition still needs remediation or tracking.
Decide what to fix first
Prioritize exploitation and reachability
Raise the priority of a vulnerability when there is known exploitation and the affected service or code is reachable under the host’s current configuration. Red Hat Lightspeed describes an open path in terms of a port or operating-system version that permits an impact on confidentiality, integrity, or availability. Its “Known exploits” label reflects public exploit code or known public exploitation; it does not show that a particular server has been compromised.
#1 Best Overall

- equipped with celeron n2940 processor, compatible with many freebsd based router systems, linux distros, or win.os supported, easy configuration and management
- Onboard Intel Celeron N2940 Processor, FCBGA1170 quad-core four-thread,1.83 GHz base frequency, 2 MB L2 cache, TDP 7.5 W processor
- Please note, this is a barebone only. A system memory, a storage drive and an operating system are needed to complete this system
- Compact aluminum, 12v3a power supply, with power cord, make sure to use a big brand memory and ssd/hdd with quality assurance
- designed with power on/off, hdmi, 2 x usb3.0, vga, rst, 4 x lan, dc-in, size at 126 x 134 x 40.6mm Quiet, fanless design silent 100%, 0.00db noise makes an ideal deployment in small offices
Use exploitation catalogs as an urgency signal
Check CISA’s Known Exploited Vulnerabilities Catalog as one input to triage, then confirm the product and version against the distribution vendor’s advisory. A generic upstream version comparison can mislead because distributions may backport fixes while retaining an older-looking version string. The catalog changes over time, so consult its current entries rather than relying on a copied count or deadline.
Choose between patching and temporary mitigation
Where a fix is available, plan to install it through the vendor-supported update process. A temporary mitigation may reduce urgency if it closes the exposure path, but it is not a substitute for eventual patching. Weigh known exploitation, actual reachability, patch availability, and the downtime or service impact of applying the fix.
Apply security updates through the distribution’s process
RHEL 8: review advisories and manage updates
For RHEL 8, review Red Hat Security Advisories and use the RHEL-supported package update workflow. Red Hat documents an automatic security-only option using dnf-automatic: set upgrade_type = security in /etc/dnf/automatic.conf, then enable the dnf-automatic-install.timer. This is a RHEL 8 approach, not a universal Linux command or configuration.
Rank #2
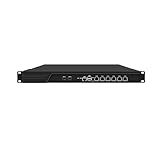
- HUNSN RJ16 equipped with 3th gen core i5 3320m, 3340m processor, compatible with many freebsd based router systems, linux distros, or win.os supported, easy configuration and management, support aes new instructions
- Please note, this is a barebone only. A system memory, a storage drive and an operating system are needed to complete this system
- Standard 1u, atx power, with power cord, make sure to use a big brand memory and ssd with quality assurance, ready to run straight out of the box
- Designed with rst, gpio, console, 2 x usb2.0, 6 x lan, 2 x sfp+, vga, power switch, ac socket, size at 440 x 255 x 45mm
- Original industry network motherboard, low power consumption, low heat, use dedicated turbo silent cooling fan to ensure long-term operation
Automatic installation can reduce the chance that a security update is missed, while manual review gives administrators more control over timing and change approval. Either approach needs a tested schedule, staged deployment where appropriate, a recovery plan, and procedures for service restarts and downtime. Confirm how kernel updates and other process restarts will be handled in your environment.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Confirm that changes are active
After an update, verify that the fixed package or advisory is installed and check whether a reboot or process restart is required. Red Hat documents tooling for identifying processes that need restarting. A completed package transaction alone does not prove that every change is active.
Keep a closeout record for each finding: the advisory or CVE, affected host, package version before and after, patch or mitigation applied, required restart or reboot, verification result, and any accepted exception with its owner and expiry date.
Rank #3

- ✅【Professional Firewall PC MGCN51N】MOGINSOK Fanless Firewall Mini PC- MGCN51N, a fanless & silent professional firewall router pc bring you a secured and encrypted network environment.Multi-functional support AES-NI, ESXI, Watchdog, Auto power on, RTC, PXE boot, Wake-on-LAN.
- ✅【CPU&Ports】MOGINSOK Firewall PC MGCN51N onboard with Jasper Lake 11th Gen Intel Celeron 5105 Quad cores Four threads 2.0GHz up to 2.9GHz 4MB cache with Intel UHD Graphics ,supported AES-NI . With HDMI 2.0+DP 1.4+ Type C(support display&Data only)Support [email protected] also with Dual DDR4 RAM slot support 2x16GB DDR4 non-ecc Ram Maximum 3200Mhz and 1xM.2 NVMe/PCIe 3.0x1 2280 SSD slot and 1x2.5Inch SATA SSD/HDD(Maximum 9mm) slot.
- ✅【DDR4 Ram & 3x SSD slots】MOGINSOK Micro Firewall Appliance MGCN51N installed with 8G RAM 128GB NVMe SSD (2xDDR4 slot support maximum 32GB DDR4 ) and 1*M.2 PICE 3.0 slot, also has a M.2 2230 support WIFI or transfer to NVMe SSD slot and 1*2.5INCH SATA HDD/SSD) configurations, you can install your own ram and ssd for DIY depends on your application.
- ✅【Professional OS Supported】This Firewall Route with 4*Intel i226 network card speed maximum up to 2.5GbE(need other device like router, cables etc. also support 2.5Gb) bring you more faster and professional network usage(some system suppliers maybe have not released compatible driver to match yet, suggest to install newest version of following systems: compatiable pf-Sense plus 23.0X or CE 2.7.x, OPNsense 22.1, OpenWrt, ROS7, ESXI , Proxmox, CentOS etc).
- ✅【Quality With Warranty】If you have any questions on MOGINSOK Firewall Appliance MGCN51N, feel free to contact us(if you want to get the latest bios update, you can send us message via Amazon). We offered 12 Months warranty for it and WE'LL REPLY YOUR Questions within 12 hours(during Workdays).
Reduce the services and network paths exposed to the internet
Remove services the server does not need
Disable unused daemons and update the packages for network services that must remain. Red Hat’s RHEL 7 Security Guide warns, “Potentially, any network service is insecure.” Treat that as a reason to minimize reachable services, not as a claim that every service has the same risk. Red Hat specifically advises against legacy remote shells such as rlogin, rsh, and telnet; use SSH instead.
Restrict necessary services to their intended clients
Use host and perimeter firewall rules to allow a service only from the clients or networks that need it. Services such as NFS and Samba require careful implementation and firewall protection. Do not expose an internal-only service to the public internet simply because it is installed or convenient to reach.
The Tool Desk
Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Do not confuse a changed SSH port with access control
Moving SSH off its standard port may reduce automated scanning against the default port, but Red Hat characterizes this as security through obscurity. It does not replace patching, strong authentication, access restrictions, or network controls.
Rank #4

- Powerful 12th Gen N150 Processor: Glovary Firewall Box Computer with Twin Lake 12th Gen N150 Processor, 4 Cores 4 Threads, 6M Cache, up to 3.6 GHz, TDP 6W. Supports OPNsense, Linux, Openwrt, etc
- 6 x i226V 2.5GbE Lan: Firewall router with 6 x i226-V network card, 2.5x faster than common Gigabit Ethernet. Soft Router can monitor network data, improve network security, powerful and widely used
- DDR5 RAM 2 x M.2 NVMe Slot: Micro firewall appliance with 1 x DDR5 SO-DIMM, 2 x M.2 2280 NVMe SSD slot, 1 x SATA 3.0 for 2.5" SSD/HDD (SATA 3.0 Cable Included)
- UHD Graphics & Triple Display: Mini PC Firewall with 2HD+Type-C triple display interfaces support 4K@60Hz, N150 processor integrated UHD Graphics. Fanless design with aluminium alloy body, quiet running without noise. Supports 12V 4 Pin 80 x 10mm small fan (Package includes 4Pin fan cable)
- Package Contents: 1 xGlovary firewall appliance, 1 xPower adapter, 1 xSATA 3.0 cable, 1 x4pin fan cable, 1 xVESA bracket. Rich interfaces: 6 x2.5G i226V-LAN, 2 xHD, 1 xType-C, 1 xUSB3.2, 4 xUSB2.0, 1 xTF Card slot supports data storage and system boot
Harden SSH without creating a lockout
Restrict administrative access
On RHEL 8, consider setting PermitRootLogin no if direct root login is not needed. Use individual administrative accounts with controlled privilege escalation instead. Where it fits your account-management model, limit SSH access with AllowUsers or AllowGroups in the SSH daemon configuration.
After changing the configuration, reload sshd for the changes to take effect. Keep an existing administrative session open and verify that a second session can connect under the new policy before closing the first. This precaution helps reduce the risk of losing remote access through a configuration mistake.
Balance stricter algorithms with compatibility and compliance
Restrictive SSH settings can prevent older clients from connecting. Red Hat’s RHEL 8 network-security guidance cautions that most hardening changes reduce compatibility with clients that do not support current algorithms or cipher suites. For example, Ed25519 host keys are not FIPS-140-compliant and do not work with Ed25519 in FIPS mode. Choose authentication and algorithm settings based on the client fleet and applicable compliance requirements.
Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Repair Windows errors before they cause bigger problems3Scan for outdated or missing drivers - takes under a minuteBest Value

- CPU:Intel Core i3-N305 Processor,8 cores , 8 threads,6M Cache, up to 3.80 GHz,15W
- Configuration:8G DDR4 Ram 128G M.2 SSD NO WIFI
- 196 x 122 x 47mm ,Low Power,Aluminum alloy case ,24/7/365 ,Perfect fit for a LAN or WAN router, firewall, proxy, WiFi access point, VPN appliance, DHCP Server, DNS Server, etc.
- 2 x Marvell AQC113 10 Gigabit LAN,4 x Intel I226-V 2.5 Gigabit LAN,3 x USB 3.0, 1 x USB 2.0,1 x Type C,1 x Nano SIM Slot,1 x HD Video, 1 x Display Port
- Supports Windows and Linux kernels, such as Windows, OpenWrt, Linux, iKuai, etc, Does not support Unix kernels, such as pfsense, OPNsense, etc.Pre-install windows 10(Unactivated)Please reinstall OS by yourself.
Scan and verify the repaired system
RHEL 9: assess vulnerabilities with matching OVAL definitions
Red Hat’s RHEL 9 documentation describes downloading the OVAL definitions that match the release, then evaluating them with:
oscap oval eval --report vulnerability.html rhel-9.oval.xml
Review vulnerability.html and investigate the findings. Remote assessment is also available with oscap-ssh over SSH, using the scanner and utilities installed as documented for the environment.
Assess configuration against a chosen baseline
SCAP Security Guide content can assess a system against a selected hardening or compliance profile. Match the content and profile to the distribution release and the policy you actually need to meet. Scanner coverage depends on the definitions’ applicability and freshness; a clean report is not proof that unknown vulnerabilities are absent or that the host has never been compromised.
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallClose findings and track exceptions
Re-scan after changes and track any residual findings to resolution. For an exception, document why it is accepted, who owns it, and when it expires so a temporary risk decision does not become an unreviewed permanent state.
Choose an update and verification approach that fits the service
| Approach | Best fit | Trade-off and checks |
|---|---|---|
| Manual security updates | Environments that require explicit review, approval, or maintenance-window coordination. | Offers more control over timing, but depends on a reliable review cadence. Plan for downtime, service restarts, and reboot requirements. |
| Automatic security updates | Environments where reducing missed-patch risk is a priority and the update schedule has been tested. | RHEL 8 documents dnf-automatic with upgrade_type = security and dnf-automatic-install.timer. Validate timing, service impact, and restart or reboot handling before relying on it. |
| Local vulnerability scan | Checking a server using definitions appropriate to its distribution release. | Review definition applicability and freshness, and investigate reported findings. A scan does not establish that unknown flaws or compromise are absent. |
| Remote vulnerability scan | Assessing a remote host through SSH where supported and configured. | RHEL 9 documentation describes oscap-ssh. Confirm the required scanner utilities, access, and matching definitions. |
These procedures use Red Hat documentation for RHEL 8 update management and SSH, RHEL 9 vulnerability scanning, and RHEL 7 service-reduction guidance. They should not be treated as identical instructions for Ubuntu, Debian, SUSE, or other distributions; use the relevant vendor’s current guidance for those systems.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




