What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Limit an AI assistant by restricting its tools, data, and credentials; enforce permissions in the connected systems rather than trusting the model to obey instructions; and require approval before high-impact actions such as sending, deleting, spending, or changing access. A prompt that says “do not send email” is not a security boundary if the assistant still has a tool that can send it.
Start with the smallest set of permissions
Give an assistant only the access its task requires. Begin with a deny-by-default policy, then explicitly allow the necessary tools, resources, and operations. Remove unneeded functionality instead of leaving broad tools enabled and relying on instructions to limit their use. OWASP recommends this least-agency approach in its guidance on excessive agency and AI agent and MCP security guidance.
As an Amazon Associate I earn from qualifying purchases.
Inventory what the assistant can reach
Before enabling proactive actions, list every connected app, tool, credential, filesystem location, and network destination. For each, identify whether the assistant needs to read, write, send, delete, or administer. Remove integrations that do not serve the task, and split broad tools into narrower operations where possible.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Fix the driver behind crashes, sound loss and screen glitches3Repair Windows errors before they cause bigger problemsFor example, an assistant that summarizes a mailbox may need permission to read messages but not to send or delete them. These are separate capabilities; granting one should not imply the others.
#1 Best Overall

- [AI Smart Speaker] You can use tozo pm1 speaker to AI Chat by connect with TOZO APP, you can literally Talk to it like a real person, rather than just typing and reading on a screen. It’s perfect for hands-free assistance, learning, and entertainment.
- [Intelligent Meeting Assistant] Recording + real-time transcription: one-click recording, stopping as you go, AI real-time conversion of voice messages into text recordings, and automatically analyzing the recording/text content, intelligently refining the key points, action items, and conclusions, and also translating into multiple languages with one click.
- [Excellent Sound Quality] Experience studio-grade clarity with our precision-engineered 28mm dynamic driver. Delivering 30% louder output and deeper bass resonance, it captures every nuance—from crisp highs to rich mid-ranges, ensuring vibrant, distortion-free sound whether you’re streaming music, or voice call.
- [Up to 20H Playtime] Bluetooth speaker has a built-in robust rechargeable battery. Up to 20 hours playtime, ensuring continuous, uninterrupted playback, whether you use the speaker for lectures, work conversations, or listening to music while running outdoors, etc.
- [Unleash Your Hands] Clip-On Convenience make it secure the rugged built-in clip to jackets, backpacks, or belts, room-filling music or take calls hands-free, perfect for hiking, cycling, or busy workdays.
Use explicit allowlists
Allow only named tools and appropriate argument ranges. Avoid unrestricted shell access, broad network access, secret locations, and unreviewed integrations unless a specific task requires them. Keep permission settings in reviewable, version-controlled configuration where the product supports it, and apply organizational policy to approved tools. Exact controls and labels vary by product, so check that product’s current permission documentation.
Make the connected system enforce authorization
The assistant should propose actions, not decide whether it is authorized to carry them out. A policy gateway or the downstream service should check every tool request using the agent identity, the user’s authorization context, the target resource, the operation, and the arguments. OWASP’s excessive-agency guidance recommends placing authorization in downstream systems rather than relying on model reasoning.
Keep credentials and identity narrow
Use credentials scoped to the task. A read-only document assistant should use an identity that cannot write or delete. When an assistant acts for an individual, preserve that person’s authorization context instead of using a generic privileged identity that can access everyone’s data. This makes permissions attributable and reduces the damage a mistaken or manipulated request can cause.
Recommended Free Tools
Rank #2

- Your favorite music and content – Play music, audiobooks, and podcasts from Amazon Music, Apple Music, Spotify and others or via Bluetooth throughout your home.
- Alexa is happy to help – Ask Alexa for weather updates and to set hands-free timers, get answers to your questions and even hear jokes. Need a few extra minutes in the morning? Just tap your Echo Dot to snooze your alarm.
- Keep your home comfortable – Control compatible smart home devices with your voice and routines triggered by built-in motion or indoor temperature sensors. Create routines to automatically turn on lights when you walk into a room, or start a fan if the inside temperature goes above your comfort zone.
- Do more with device pairing – Fill your home with music using compatible Echo devices in different rooms, or create a home theatre system with Fire TV.
- Say goodbye to drop-offs and buffering - With eero Built-in, Echo Dot doubles as a mesh wifi extender, adding up to 1,000 sq. ft. of wifi coverage to your existing eero network.
For sensitive API workflows, OpenAI’s cybersecurity checks documentation advises reviewing proposed tool calls against approved scope, denying unauthorized actions, pausing ambiguous or high-risk changes for human approval, enforcing independent filesystem and network boundaries, keeping audit logs, and failing closed if review is unavailable.
Require approval for actions with serious consequences
Decide which operations need a person’s review based on the harm they could cause and how difficult they are to undo. OWASP gives reading documents as a low-risk example and sending email, executing code, deleting a database, and transferring funds as higher-risk examples. Those examples are illustrative; classify actions for your own environment, and do not silently treat unknown operations as low risk. See the OWASP AI Agent Security Cheat Sheet.
Make approval specific and hard to replay
A vague “Are you sure?” prompt gives a reviewer little to assess. Show the exact action, target, and parameters before approval. Bind approval to the actor, tool, target, normalized parameters, time, and expiry so it cannot be reused for a different action or replayed later. For critical operations, use step-up authentication and fail closed if policy or approval validation is unavailable.
Rank #3
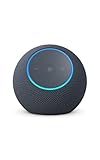
- Meet Echo Dot Max: Experience rich room-filling sound that automatically adapts to your space and fine-tunes playback. Features a built-in smart home hub and Omnisense technology for highly personalized experiences.
- Music to your ears: With nearly 3x the bass versus Echo Dot (2022 release), it fits beautifully in any space, delivering your personal sound stage with deep bass and enhanced clarity. Listen to streaming services, such as Amazon Music, Apple Music, Spotify, and SiriusXM. Encore!
- Do more with device pairing: Connect compatible Echo smart speakers and smart displays in different rooms, or pair with a second Echo Dot Max to enjoy even richer sound
- Simple smart home control: Set routines, pair and control lights, locks, and thousands of smart home devices that work with Alexa without needing a separate smart home hub. With Omnisense technology, you can activate routines via temperature or presence detection.
- Say goodbye to drop-offs and buffering - With eero Built-in, Echo Dot Max doubles as a mesh wifi extender, adding up to 1,000 sq. ft. of wifi coverage to your existing eero network.
To avoid approval fatigue, safely allowlist and sandbox routine low-risk actions while keeping human review for actions where harm is difficult to reverse. OWASP discusses this balance in its DevSecOps guidance.
Limit the damage from untrusted content and integrations
Emails, websites, documents, and tool descriptions may contain instructions aimed at the assistant. Treat that content as data, not as authorization to expand the assistant’s powers. OWASP describes a malicious email manipulating an assistant with mailbox access into scanning and forwarding messages; read-only mail access and user approval before sending reduce the available path to harm. The example appears in OWASP’s excessive-agency guidance.
Vet extensions and MCP servers
Before connecting an extension or MCP server, establish what code or service will run and what it can access. OWASP recommends using an approved server registry, vetting maintainers and requested permissions, pinning versions, granting minimal scopes, and sandboxing local servers with restricted filesystem and network access. A trusted-looking description is not a substitute for checking the server’s actual access.
Rank #4
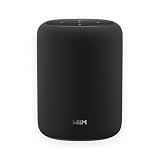
- Hi‑Res Audio, Expertly Tuned – Enjoy up to 24‑bit/192 kHz Hi‑Res streaming, powered by a 100W peak amplifier, 4″ paper‑cone woofer and dual 1″ silk‑dome tweeters for natural mids, smooth highs, and room‑filling clarity.
- Smarter in Any Room - AI RoomFit technology optimizes the sound to your specific space and placement—balanced bass, clean vocals, and engaging detail wherever you place it.
- Open by Design - Stream in the WiiM Home App or cast directly via Google Cast, Spotify/TIDAL/Qobuz Connect, Alexa Cast, DLNA, Roon/LMS; join WiiM, Google Cast, Alexa multi‑room groups.
- Stereo & Cinema‑Ready - Pair two for true L/R stereo; add WiiM Sub Pro for deeper, tighter bass or combine with compatible WiiM components as center/surround for an immersive home‑theater setup.
- Control made simple – Manage playback and settings easily through the WiiM Home App, voice control via Alexa or Google Assistant (with compatible devices), and physical buttons on the speaker—streamlined design, no screen or remote needed.
Log actions and contain runaway behavior
Record tool calls, commands, writes, network requests, initiating identity, session, and outcomes or diffs. Keep logs outside the assistant’s control where feasible, and do not record secret values. Alert on unusual credential access, unexpected destinations, bulk reads, new servers, and changes to instruction or CI files. OWASP’s AI agent and MCP guidance covers these monitoring controls.
Set limits on retries, tokens, cost, recursion, and tool chains. These caps do not replace authorization, but they can constrain runaway behavior and give people time to detect it. Maintain an interruption and recovery path appropriate to the system; a log is useful for investigation, but it does not by itself undo a completed action.
Test the boundaries before and after changes
Treat permission rules and approval checks as software controls. Test them before production and after material changes to prompts, tools, memory, retrieval, policies, or providers. Keep regression cases for past failures, and do not release high-risk permission or approval changes without updated tests.
Best Value

- Powered by a 47% faster processor, the next-gen dual-tweeter acoustic architecture produces detailed stereo separation while a 25% larger midwoofer deepens the bass.¹
- Place this speaker anywhere and everywhere you want to listen. The compact design fits beautifully on your bookshelf, kitchen counter, desk, or nightstand.
- Stream from all your favorite services over WiFi. Pair a Bluetooth device with the press of a button. Connect a turntable or other audio source using an auxiliary cable and the Sonos Line-In Adapter.²
- Go from unboxing to unbelievable sound in just a few minutes. Simply plug in the power cable, connect your phone or tablet to WiFi, and open the Sonos app.
- With a tap in the Sonos app, Trueplay tuning technology analyzes the unique acoustics of your space and optimizes the speaker’s EQ. So all your content sounds just the way it should.
- Try prompt overrides and requests to use unauthorized tools.
- Test privilege escalation, memory poisoning, and data exfiltration attempts.
- Check recursive tool abuse, approval bypass, and multi-agent chaining.
- Verify that denied requests stay denied when policy review is unavailable.
These abuse cases and testing recommendations are described in the OWASP AI Agent Security Cheat Sheet.
Compare assistant setups by their controls
When choosing an assistant or reviewing its configuration, assess the security boundaries rather than relying on a general claim that it is “safe.” Look for permission granularity at the tool, operation, resource, and argument levels; authorization enforced by a gateway or downstream system; scoped and attributable identities; and approvals that preview and bind to the exact action.
Also check filesystem, network, and code-execution isolation; audit logs and alerts; interruption and recovery options; rate and loop limits; and whether policies and abuse cases can be versioned and regression-tested. NIST NCCoE’s Agentic AI Identity and Authorization project hub describes ongoing work on practical resources in this area. NIST’s February 5, 2026 announcement of a concept paper describes a proposed project, not a finalized agent-specific implementation standard.
Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




