Recommended Free Tools
Protecting data in the cloud takes coordinated controls: manage who can reach it, choose encryption and key practices that fit your services, and make backups that you can restore. The right setup depends on whether you use infrastructure, platform, or software services—and on how quickly your organization needs to recover.
Start with the cloud service model
Cloud providers and customers share security responsibilities, but the division changes by service. NIST SP 800-210 explains that access controls must account for the components exposed by infrastructure as a service (IaaS), platform as a service (PaaS), and software as a service (SaaS). A control that is available to configure in an IaaS environment may not be exposed in the same way in a SaaS product. Identify the service model and the controls you can actually manage before designing policy. NIST SP 800-210 (2020)
As an Amazon Associate I earn from qualifying purchases.
- IaaS: Determine which infrastructure and access components your team administers and which remain with the provider.
- PaaS: Focus on the platform, application, identity, and data controls exposed to you.
- SaaS: Work within the provider’s available identity, role, sharing, and data settings; do not assume control over underlying infrastructure.
Shape access around identity and context
Grant only the access people and services need, and review permissions as roles change. Context can also inform decisions: CISA’s federal cloud-use-case guidance describes policy inputs such as the service being accessed, identity, device, and data labels. This is an approach in that federal guidance, not a universal mandate for every organization. CISA TIC 3.0 Security Capabilities Catalog
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minute- Use distinct identities and roles rather than shared accounts where the service supports them.
- Limit permissions to the data and actions required for each role.
- Consider device, service, and data sensitivity when deciding whether to allow access.
- Review access when users, workloads, or business needs change.
Choose encryption and key custody deliberately
Encryption can protect data at different points, but the location of encryption and custody of keys affect what the customer can control. CISA distinguishes client-side encryption, in which an agency-created key is not shared with the cloud provider, from server-side encryption performed at the cloud destination. Neither description alone establishes which choice is best for every workload. Consider where keys are stored, who can use them, how access is controlled, and how keys are retained, rotated, or recovered. CISA TIC 3.0 Security Capabilities Catalog CISA TIC 3.0 Cloud Use Case
#1 Best Overall

- Massive capacity, up to 18TB capacity (1 1TB = one trillion bytes. Actual user capacity may be less depending on operating environment.).Specific uses: Business, personal
- Includes software for device management and backup with password protection (Download and installation required. Terms and conditions apply. User account registration may be required.)
- 256-bit AES hardware encryption
- SuperSpeed USB (5 Gbps); USB 2.0 compatible
- Client-side encryption: The customer controls the key described in CISA’s guidance. This can increase control, while making key protection and availability the customer’s operational responsibility.
- Server-side encryption: Encryption is applied at the cloud destination. Confirm the service’s available key options and responsibilities in current provider documentation.
Encryption is not a substitute for access control or recovery planning: someone still needs authorized access to keys, and encrypted backups must remain restorable.
Plan backups around recovery needs
A backup is useful only if its design and retention support the recovery the organization requires. NIST SP 800-209 recommends specifying backup tiers, frequency, number of copies, media types, encryption, and key-retention or rotation considerations. It does not prescribe a universal backup schedule. Set these choices against the data’s importance and the time and amount of data the organization can afford to lose. NIST SP 800-209 (2020)
Rank #2

- Easy-to-use desktop hard drive—simply plug in the power adapter and USB cable
- Fast file transfers with USB 3.3
- Drag-and-drop file saving right out of the box
- Automatic recognition of Windows and Mac computers for simple setup (Reformatting required for use with Time Machine)
- Enjoy peace of mind with the included limited warranty and Rescue Data Recovery Services
- Frequency: Set how often backups run based on acceptable data loss, rather than adopting an unsupported one-size-fits-all interval.
- Tiers and copies: Decide what is backed up, how many copies are maintained, and how each copy supports recovery.
- Media: Specify the storage media used. Physical media can be one option in a broader plan, but NIST does not specifically endorse external hard drives.
- Encryption and keys: Protect backup data and ensure the necessary keys will be available for restoration.
- Retention and rotation: Define how long copies remain available and how key lifecycle choices affect older backups.
Test restoration and protect data in transit
Backup creation does not prove that recovery will work. CISA’s cloud architecture guidance identifies regular and frequent backup testing as a data-protection consideration. Test restoration in a way that confirms the organization can retrieve usable data and access any required keys. CISA TIC 3.0 Cloud Use Case
Also map where data moves between cloud services, workloads, and environments. Cloud-native, service-mesh, multi-cloud, and hybrid architectures can create communication paths that need explicit in-transit protection. NIST IR 8505 addresses data-protection approaches for these architectures; the relevant controls depend on the design and data flows in use. NIST IR 8505 (September 2024)
Rank #3

- Slim durable design to help take your important files with you
- Back up smarter with included device management software[2] with defense against ransomware
- Help secure your important files with password protection and hardware encryption
- 3-year limited warranty
Turn the strategy into an operating plan
- Inventory sensitive data and identify which cloud services and service models handle it.
- Map who or what can access each service and data set; align permissions with roles and relevant context.
- Choose encryption placement and key custody, then document key access, storage, lifecycle, and recovery responsibilities.
- Define backup scope, tiers, frequency, copy count, media, encryption, and retention against recovery needs.
- Exercise restoration and review data flows to identify unprotected paths between cloud components or environments.
- Recheck the plan when services, provider capabilities, data classifications, or organizational recovery needs change.
Provider features, terms, and regional availability can change. Verify service-specific capabilities and responsibilities against the provider’s current documentation before relying on them.
Quick Recap
Best Value

- World’s First 6TB 2.5” Portable Hard Drive
- Slim durable design to help take your important files with you
- Vast capacities up to 6TB[1] to store your photos, videos, music, important documents and more
- Back up smarter with included device management software[2] with defense against ransomware
- Help secure your important files with password protection and hardware encryption
Rank #4
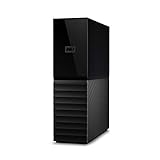
- Massive capacity, up to 18TB capacity (1 1TB = one trillion bytes. Actual user capacity may be less depending on operating environment.).Specific uses: Business, personal
- Includes software for device management and backup with password protection (Download and installation required. Terms and conditions apply. User account registration may be required.)
- 256-bit AES hardware encryption
- SuperSpeed USB (5 Gbps); USB 2.0 compatible
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




