There is no universally best fine-grained authorization tool. Relationship-based systems, policy engines and managed services solve different parts of the authorization problem. For a relationship-heavy application you might start with OpenFGA or SpiceDB; for managed authorization in an AWS environment, consider Amazon Verified Permissions; for policy-as-code across domains, look at OPA or Cedar. The rankings below are editorial fit scores based on documented capabilities—not hands-on tests or independent performance benchmarks—and should be read alongside each tool’s intended use.
How the ranking works
The score is an editorial assessment of fit and documented scope, not a measurement of product quality or speed. It weights authorization-model fit (30 points), deployment and operational choices (20), authoring and developer workflow (20), validation, testing and lifecycle evidence (20), and clarity of product boundaries and available evidence (10). A lower score can reflect limited evidence for this comparison, not a finding that the product itself is inferior. Documentation reviewed for this article was accessed in October 2026; product features, versions, regions and plan terms can change.
As an Amazon Associate I earn from qualifying purchases.
These entries include authorization languages and engines, hosted services, and a data-governance platform. They are not interchangeable. In particular, a language or engine does not automatically include managed hosting, policy distribution, or application enforcement.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Fix the driver behind crashes, sound loss and screen glitches3Repair Windows errors before they cause bigger problems| Rank | Tool | Score | Best starting point | Key qualification |
|---|---|---|---|---|
| 1 | OpenFGA | 92/100 | Open-source relationship-based authorization | Plan to operate the service and storage. |
| 2 | SpiceDB / AuthZed | 91/100 | Zanzibar-style authorization database, self-managed or managed | Compare consistency, operations and managed terms for your workload. |
| 3 | Auth0 Fine-Grained Authorization (FGA) | 89/100 | Managed relationship-based authorization | Production use requires a subscription; confirm current terms and locality coverage. |
| 4 | Cedar | 86/100 | Typed authorization policies and policy analysis | Cedar is a language and engine ecosystem, not a hosted service by itself. |
| 5 | Amazon Verified Permissions | 85/100 | Managed Cedar-based authorization for custom applications | AWS service behavior and requirements are not identical to every native Cedar implementation. |
| 6 | Cerbos | 84/100 | Policy-file-based application authorization with self-hosting | Optional commercial components add lifecycle management or enrichment. |
| 7 | Open Policy Agent (OPA) | 82/100 | Policy-as-code across multiple domains | Teams must integrate enforcement and plan policy and data distribution. |
| 8 | Permit.io | 79/100 | Authorization platform with hosted control-plane workflows | Some feature descriptions in available comparisons are competitor-authored; verify them with current product documentation. |
| 9 | Immuta | 74/100 | Fine-grained authorization and governance for data | Data authorization is a different scope from a general application authorization service. |
| 10 | Oso | Evidence-limited | Worth evaluating if it matches your authorization model | Available official documentation did not establish enough current detail for a defensible product score. |
The numeric scores are comparative editorial judgments within this shortlist, not objective ratings. Oso is marked evidence-limited rather than assigned a misleading number; its placement at the end is not a verdict on the product.
#1 Best Overall

- Access control keypad is sturdy rugged keypad; with zinc alloy electroplated technology;The circuit board is completely encapsulated in epoxy to be weatherproof; keyboard is waterproof so you can use it outdoor or indoor
- Key backlight function; the keys light will stay on in dark places or at night; indicator light; Red light stands for enter into programming mode; Yellow light for in the programming mode;Green light for operation successful mode
- Wiegand access control keypad can be as a standalone reader or keypad;0-99s adjustable door relay time; It is a relay output to open the door; so that you could connect this to a powered device without the use of some computing intermediate
- Easy to use;full programming from the keypad;support 3 access ways for card;PIN or card with PIN;you can set the public password or private password and the password can be changed which is more secure and personalized
- You can use the access control keypad to add and delete 2000 user information; set the door open delay time; it is suitable for garages; shops; homes; warehouses; laboratories; it has short circuit protection
Choose by the shape of your permissions
When access follows relationships
If permissions depend on connections such as a user belonging to a group, a group owning a folder, or a document being shared with a person, evaluate a relationship-based authorization model. OpenFGA, SpiceDB and Auth0 FGA document this approach. The central design work is defining relationships and keeping relationship data accurate as users, groups and resources change.
When rules depend on attributes or policy conditions
If decisions hinge on attributes and context—such as a resource’s classification, an actor’s role, or request-time conditions—evaluate policy-centric options. Cedar, Cerbos and OPA are relevant to this style, though their deployment and management models differ. Confirm how each policy receives trusted attributes and how changes are validated before they affect decisions.
When authorization applies to governed data
Immuta belongs in the comparison when the problem is controlling access to analytics or other governed data. It should not be treated as a direct substitute for a general application policy decision point unless its supported platforms and enforcement path meet that application’s requirements.
Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Clear out junk files and repair common Windows errorsFree Scan →Scan for outdated or missing drivers - takes under a minuteDriver Scan →1. OpenFGA — 92/100
Why it ranks first
OpenFGA is an open-source authorization solution with a modeling language and APIs. Its project documentation says it draws on ideas from Google’s Zanzibar paper, supports relationship-based authorization, and can also address role- and attribute-based use cases. A Docker-based local quick start makes it possible to explore a model without first adopting a hosted service.
Rank #2
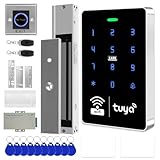
- All-in-one kit: Your full access control kit is a complete access control system that provides everything you need in one kit (including WiFi access control host, power supply, 280kg magnetic lock + ZL bracket, sensor switch, doorbell, remote control, IC keychain)
- The wiring is super simple and the installation is more convenient: just connect the 6 terminals to the corresponding numbers to complete the wiring, which is a step faster and solves the wiring pain points. It is really great.
- WiFi access control keypad: supports 1000 users, IP68 outdoor waterproof, supports five ways to open the door: WiFi Tuya APP/temporary password/RFID card/password/RFID card + password, remote door opening , touch blue backlit keyboard, supports always-on mode, can set to add and delete cards
- Sturdy 280kg Magnetic Lock - This magnetic lock has a powerful 600-pound holding force, ensuring your door stays securely locked. It features a fail-safe feature and comes with both Z- and L-shaped brackets to fit a wider range of door types. Easy installation. [Note: For single-door wooden doors, iron doors, and UPVC doors (inward opening), you can purchase the ZL bracket set.]
- The power supply has been upgraded for super-easy installation: 1. The power input cable is pre-connected; simply plug it into an outlet (eliminating the hassle of wiring and increasing safety). The cable is available in 2-meter lengths to accommodate various installation scenarios. 2. The power output cable is pre-connected (the cable closest to the power supply is tightened before shipment; please do not loosen it). Simply plug the corresponding digital terminals into the connectors to easily complete the wiring.
What to verify before choosing it
OpenFGA is a strong fit when an engineering team wants an open-source relationship model and is prepared to operate the service and its storage. A local quick start is not a production topology: validate database operations, deployment design, backups, upgrades and the current release against project documentation. Also test whether your chosen model supports the resource queries your application needs, not only single-object permission checks.
2. SpiceDB / AuthZed — 91/100
Why it ranks highly
AuthZed documentation describes SpiceDB as an open-source, Zanzibar-style authorization database: define a schema, write relationships, and call permission checks from application code. The documentation also describes managed SpiceDB offerings, so teams can investigate both self-managed and hosted operating models.
What to compare
Compare its schema semantics and consistency behavior with the relationship model you would use in OpenFGA. Then assess availability, operational responsibilities and the terms of any managed offering against your own requirements. The documentation index listed releases through September 2026 and updates in October 2026; those dates establish recent documentation activity, not a performance advantage. No cross-product performance comparison is established here.
3. Auth0 Fine-Grained Authorization (FGA) — 89/100
Why it ranks highly
Auth0 FGA is a managed relationship-based authorization service based on OpenFGA. Its documentation covers stores, authorization models, tuples, contextual and conditional tuples, APIs, SDKs, IDE and command-line workflows, and model testing. That combination suits teams seeking hosted operations alongside tools for developing and testing a relationship model.
Rank #3

- ✅ 【Wireless Access Control System】Integrated wireless access control keypad allows you to control the keypad share, modify and delete passwords/ID cards, remote Unlock doors/gates, view access logs, manage users, and assign temporary or permanent access from your phone, anytime and anywhere
- ✅ 【Multiple Access Options】Come with 5PCS ID key fobs, support 2000 users capacity. Swipe card or password or TUYA APP multiple unlocking methods to open the door. Equipped with doorbell button, compatible with all electric locks.
- ✅ 【Reliable and Practical】The access control keypad with strong zinc alloy electroplated technology, epoxy to completely encapsulated, anti-prying hexagonal star screw, anti-vandal and weatherproof. Suitable for mounting either indoor or outdoor. Backlight design(non-turn-off), in dark locations or night you can read numbers.
- ✅ 【Widely Used】Wiegand access control keypad system can prevent unauthorized personnel from entering. Built in buzzer and light dependent resistor (LDR) for anti tamper. Can be as a standalone reader or keypad. Very suitable for garage, hotel, shops, warehouses, laboratories, other private spaces. Note: Models whose connection protocol is Wi-Fi, learn buttons, safety sensors, rolling code are not currently supported! Keypad uses 2-wire connection directly to the opener's push button switch terminals.
- ✅ 【Simple Setup for Use】Connect the access controller to the power supply and the electric lock, Keypad enter "*master code#73#" code, turn on wireless pairing, add the keypad to the TUYA APP, you can remotely manage the access control system. Attention: The password keypad working on 2.4 GHz network, when adding keypad, make sure the keypad must be connected to the same Wi-Fi network as your smartphone. Powered by 12V DC power supply (not included)
Plan and availability checks
Auth0 documentation describes a free evaluation tier and says production use requires a subscription. It also describes active-active availability across two AWS regions for each listed locality, as well as a private-cloud option. Check current plan terms, region coverage, service requirements and the fit of those deployment choices before committing; the documented availability description is not a guarantee for every geography or plan.
4. Cedar — 86/100
What it is
Cedar is an open-source authorization policy language and engine ecosystem. It is relevant when typed policies, schema validation and policy analysis matter to the design. The language and engine should be evaluated separately from any service that hosts policies or makes authorization decisions for an application.
Keep the service boundary clear
Amazon Verified Permissions uses Cedar, but it is a distinct managed product with service-specific behavior and lifecycle. Native Cedar implementations and a hosted service can differ in integrations, operations and constraints. The Cedar material available for this comparison did not establish enough detail to rate particular implementation features beyond this boundary, so verify the current language and engine documentation before selecting an implementation.
Free tools Windows power users keep installed
One-click scans. No signup required.
5. Amazon Verified Permissions — 85/100
How it makes decisions
AWS describes Verified Permissions as a fine-grained authorization service for custom applications. Policies use Cedar; the service evaluates a principal, action, resource and context against policy stores and schemas. Application code calls the authorization API and remains responsible for enforcing the returned decision.
Rank #4

- 【Multiple users, Multiple Access Ways】Come with 5PCS ID key fobs, Support 2000 user capacity, support open the door for ID key cards, password, ID key card+password options.
- 【Heavy-Duty Zinc Alloy Case】The access control keypad with strong zinc alloy wlectroplated anti-vandal and weatherproof. Epoxy to completely encapsulated, suitable for mounting either indoor or outdoor.
- 【Simple Set-ups and Easy Installation】The access control is multifunction standalone access controller, full programming from the keypad, don't need to connect to computer. Working with DC12V power supply.
- 【Bright Backlight Keypad】Access control keypad with blue backlight features keys, you cansee the keypad numbers at night or in the dark outside the office. In addition, provided with a WG26 interface and door bell button.
- 【High Security and Widely Used】Access control system able to deterring unauthorized personnel, built in buzzer and light dependent resistor (LDR) for anti tamper. Suitable for apartment, office, access control, garage door/sliding door openers, off-limit area, hotel locks, school campus access, identification, parking lot entry, etc.
Version and service-specific checks
AWS documentation accessed in 2026 states, “Verified Permissions currently uses Cedar version 4.7.” Treat that as the documented service version at that time, not as a claim about every Cedar implementation or a guarantee of the current version. AWS also documents differences between its service implementation and native Cedar. Validate language compatibility, service dependency, available regions, pricing and policy lifecycle for your intended application.
6. Cerbos — 84/100
Policy files and deployment
Cerbos describes an application-focused authorization policy decision point (PDP). Its comparison documentation says the standalone open-source PDP can run from hand-authored YAML or JSON policies with CEL, without a control plane on the decision path. That may suit teams that want to self-host a policy decision service and keep its decision path separate from management tooling.
Optional components and protocol details
Cerbos Hub and Cerbos Synapse add commercial policy-lifecycle and decision-time-enrichment capabilities. Cerbos identifies its PDP API with the AuthZEN Authorization API, while its comparison page describes the implementation as partial. Confirm current deployment and protocol details in primary documentation; do not assume that an API association means complete protocol compatibility.
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minutePC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 117. Open Policy Agent (OPA) — 82/100
Where it fits
OPA is a general-purpose policy engine that uses Rego. It is relevant when a team wants policy-as-code across multiple domains rather than a turnkey managed application authorization product. The comparison material reviewed describes self-hosted service or sidecar deployment and notes an open-source control-plane option.
Best Value

- Multiple Access Options - This access control system offers a variety of ways to enter and exit a secure area including password input, card swiping and remote control.
- Enhanced Security - The 600LBS electromagnetic lock ensures that the door is tightly secured, enhancing the safety and security of the premises.
- Visitor Management - Visitors can easily press the doorbell on the access keypad, letting those indoors know when someone has arrived. The indoor unit comes with a remote control that allows easy entry for visitors without the need to go outside.
- Easy Installation - The system is user-friendly and can be installed with ease, requiring minimal time and effort.
What the team must provide
OPA’s fit depends on how the application integrates enforcement, distributes policy and data, tests changes and operates the runtime. Those choices are part of the solution design; the engine alone does not settle them. Evaluate representative policies and operational failure behavior before using it as the authorization layer for critical requests.
8. Permit.io — 79/100
Platform approach
A Cerbos-authored product comparison describes Permit.io as pairing a managed control plane with an open-source PDP in its standard hosted model. It also describes a low-code editor, embeddable access-workflow components, OPAL-based policy and data distribution, local or self-hosted operating models, and multiple authoring workflows.
Verify claims with current product documentation
Those descriptions come from a competitor’s comparison, so they are useful as leads, not independent confirmation. Before scoring Permit for a real deployment, verify each required feature, deployment option, distribution path and support commitment in Permit’s own current documentation. In particular, establish where policy and authorization data live, how quickly updates propagate, and how the system behaves if a control plane or network connection is unavailable.
9. Immuta — 74/100
Data-focused authorization
Immuta’s official materials frame its offering around data access authorization and governance. That makes it a candidate when the access problem concerns analytics or governed data, rather than a generic application check such as whether a user can edit a project record.
Scope your evaluation
Confirm current connectors, supported data platforms, deployment choices, governance capabilities and pricing with Immuta’s product documentation. Include it in a general authorization shortlist only if its data-focused enforcement path covers the reader’s actual use case; otherwise compare it within a data-governance evaluation.
10. Oso — evidence-limited
Oso belongs on a broad candidate list for authorization software, but the official documentation page available for this comparison did not provide enough substantive detail to establish its current product lineup, policy model, deployment choices or product availability. That is an evidence gap, not a negative product assessment. Verify those points with Oso’s current official documentation before deciding whether it belongs in a scored shortlist.
A practical selection process
- Write down the decision being made. Specify the principal, action, resource and any request context. Add representative cases for a single resource and for lists or searches if the application needs both.
- Choose the model that matches the policy shape. Use relationships as the starting point for sharing and membership graphs; use a policy-centric approach when decisions depend on attributes and conditions. If authorization concerns governed data, define that scope before comparing general application engines.
- Map the components. Identify the decision engine, policy or relationship store, management interface, distribution path and enforcement point. Establish which components are self-hosted, managed or embedded, and which remain your team’s responsibility.
- Test updates and failure behavior. Measure policy and relationship freshness under your own workload. Decide what happens when a service, control plane or network path is unavailable, and test the chosen behavior rather than assuming a default.
- Evaluate the developer and governance workflow. Test model or schema validation, policy tests, audit records, explainability and change review. Check whether the system supports the resource listing and filtering operations your product needs; a successful single-resource check does not prove it can safely filter a large result set.
- Compare operational and commercial fit. Confirm language and SDK support, cloud dependencies, regional availability, support terms and current pricing for the intended workload. Do not treat vendor performance claims as independent benchmarks; use representative policies and production-shaped data for your own evaluation.
Common comparison mistakes
- Equating an allow/deny API with a complete authorization system. Application enforcement, trusted context, policy distribution and data freshness still need an owner.
- Comparing unlike categories as if they were the same product. A policy language, a self-hosted engine, a managed service and a data-governance platform offer different boundaries and operational work.
- Assuming a management plane is always on the decision path. Confirm which components are required at request time and what happens during an outage.
- Using advertised speed as a ranking shortcut. No independently published cross-vendor performance statistic was established for these options. Benchmark the policies, data volume and deployment pattern that match your application.
Final verdict
Start with OpenFGA or SpiceDB when the core challenge is modeling relationships and you can own the operating model. Put Auth0 FGA on the shortlist if you prefer a managed relationship-based service. Evaluate Cedar or Amazon Verified Permissions for typed policy-based authorization, keeping the language distinct from the AWS service; consider Cerbos for a self-hosted application PDP and OPA for broader policy-as-code. Use Immuta for data-governance needs, and verify current product details before assigning Oso a comparative score. The right choice depends on the authorization model, deployment boundary and operational responsibilities your application can support.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




