In one home SOC, a local 27B model found problems in a Splunk-and-Sysmon setup and helped fix some of them—but it also made false-positive claims, consumed nearly its full context window during a misdirected investigation, and did not resolve every issue. The account is a useful example of AI-assisted security administration, not evidence that an LLM can reliably audit or repair other environments without close human review.
What the experiment tested
A security analyst studying for CySA+ asked whether a local model could audit a Splunk installation, identify what was broken, and fix issues without being told exactly where to look. The setup used Splunk under a dev license, Sysmon for Windows endpoint telemetry, a quantized Qwen3.8-27B model (IQ2_M), llama-server, and an agent. The author reports running it on one 16 GB GPU with a reported 128K context window, and says the workflow ran locally without third-party data or borrowed infrastructure.
As an Amazon Associate I earn from qualifying purchases.
Those details describe one lab configuration, not a hardware recipe or a privacy guarantee for local inference generally. The account does not compare quantizations, GPUs, model servers, or agents, and does not establish that another 27B model will fit or perform similarly with the same memory and context settings.
The author reports five audit areas and ten findings in total. The available account describes some examples and outcomes, not enough detail to reconstruct or independently verify every finding.
#1 Best Overall

- A great fit for 1-2 bedroom homes, this kit includes one base station, one keypad, four contact sensors, one motion detector, and one range extender.
- Includes an intuitive Keypad that can arm and disarm your Alarm and Contact Sensors that detect when doors or windows open.
- Choose the Ring Alarm Kit that fits your needs and detect even more with additional Alarm Sensors and accessories (sold separately) at any time.
- Receive mobile notifications when your system is triggered and monitor all your Ring devices all through the Ring app.
- More peace of mind. Subscribe to a compatible Ring Protect Plan (sold separately) to Arm your Alarm from anywhere, keep your system online if the Wi-Fi goes down, and more. Plus, get 24/7 Professional Monitoring for emergency police, fire and medical response, and more.
What it found—and what remained uncertain
| Audit area or issue | What the account reports | What to take from it |
|---|---|---|
| Configuration inspection | Part of five audits; the account does not enumerate every finding. | Ask for the exact setting, source evidence, and expected behavior before accepting a claim. |
| Data pipeline | The audit identified duplicate log ingestion. | Confirm duplication in the actual ingest path and assess its effect before changing inputs or transforms. |
| Logging hardening | The audit identified disabled Windows event channels and a Sysmon configuration that did not detect access to LSASS. | Verify channel state and configuration coverage on the endpoint; do not infer coverage from a configuration file alone. |
| Performance counters | A reported issue involved a missing parameter and localization on a Spanish Windows installation. | Check the affected host’s language, counter names, and exact error rather than assuming an identifier is universal. |
| 24-hour log analysis and IoC detection | These were among the five audit areas, but the account does not supply enough detail here to assess their individual findings. | Require the time range, event identifiers, query logic, and supporting events for each conclusion. |
| Remediation | The author says some issues were corrected, while at least one binary debugging problem remained unresolved. | A proposed change is not a verified fix. Record unresolved work as unresolved. |
The finding count is the author’s 2026 tally for this lab, not a benchmark or a measure of typical model performance.
Why Sysmon still needs configuration and a SIEM
Sysmon is a Windows system-monitoring service and driver that records activity to the Windows Event Log. Microsoft Learn states: “Sysmon records system activity and writes events to the Windows Event Log.” It also states: “Sysmon doesn’t analyze events or generate alerts” and “Sysmon doesn’t block or prevent activity.” Splunk or another downstream system is responsible for searching, correlating, and alerting on collected events; Sysmon itself is not an alerting or prevention tool.
Coverage depends on the selected event types and filters. Microsoft documents configuration for events such as Process Create, Network Connect, and File Create, with include and exclude filters. A configuration can omit activity an analyst needs, while broad collection can create substantial event volume. Splunk’s Sysmon add-on guidance likewise advises tailoring filters to the security team’s needs: an uncustomized setup may collect too little useful data or send unnecessary events into the Event Log and Splunk.
Rank #2

- A great fit for 2-4 bedroom homes, this Alarm Kit includes one Base Station, two Keypads, eight Contact Sensors, two Motion Detectors, and one Range Extender.
- Includes an intuitive Keypad that can arm and disarm your Alarm and Contact Sensors that detect when doors or windows open.
- Choose the Ring Alarm Kit that fits your needs and detect even more with additional Alarm Sensors and accessories (sold separately) at any time.
- Receive mobile notifications when your system is triggered and monitor all your Ring devices all through the Ring app.
- More peace of mind. Subscribe to a compatible Ring Protect Plan (sold separately) to Arm your Alarm from anywhere, keep your system online if the Wi-Fi goes down, and more. Plus, get 24/7 Professional Monitoring for emergency police, fire and medical response, and more.
Verify collection before trusting an audit
- Check the endpoint. In Event Viewer, open Applications and Services Logs > Microsoft > Windows > Sysmon > Operational. Confirm the expected events are present on the machine and within the time range under review.
- Check the configuration. Review the installed Sysmon configuration and confirm that its event types and filters cover the behavior being investigated. Microsoft documents applying a configuration with
sysmon -c <configfile>; configuration changes take effect without a restart. - Check the downstream path. Confirm that the relevant Operational log events reach Splunk and are not duplicated or lost. Splunk describes collecting Sysmon events from that log; Windows Event Forwarding/Windows Event Collector is another possible route, which also needs careful tuning.
- Test the resulting coverage. Review event volume and representative events after a change. A configuration that loads successfully does not, by itself, prove that the desired activity is visible or that the volume is appropriate.
Splunk’s add-on guidance recommends adapting a maintained configuration template, such as SwiftOnSecurity’s sysmon-config, to local requirements rather than treating a generic configuration as universally suitable.
Where the model made mistakes
The author describes two false positives from earlier audits. In one case, the model declared a Windows event channel disabled after checking the wrong channel; the channel was enabled and recording events. In another, a rule flagged processes touching temporary files under a user profile, including ordinary Electron applications and the agent itself. The account says the model later identified and corrected those assumptions.
That is a reason to inspect evidence, not to assume an LLM will catch its own mistakes. For a finding, ask for the precise host, channel or event identifier, time range, observed value, and the rule or configuration that supports the conclusion. Then verify the relevant state independently. A plausible explanation is not proof, and a later correction does not erase the cost of an earlier false alarm.
Rank #3

- Home Security Systems
Audit first; remediate only with evidence
The most useful operational distinction in the account is between broad inspection and bounded change. An audit can search widely for anomalies; remediation should stop at a root cause supported by evidence. The author says the agent’s working rules emphasized answering only the question asked, being exhaustive when auditing, checking IDs, ports, and GUIDs before asserting them, avoiding invented facts, and using scripts for mechanical operations.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Scan for outdated or missing drivers - takes under a minute3Clear out junk files and repair common Windows errorsA safer sequence for AI-assisted changes
- Start read-only. Have the model report commands, configuration excerpts, event records, and the reason each observation matters. Do not let an initial audit silently edit a live configuration.
- Check the claim yourself. Validate identifiers and compare the proposed diagnosis with the actual host, logs, and installed software. Ask the model to distinguish observed facts from hypotheses.
- Make a bounded proposal. Request the smallest change that addresses the supported root cause, plus expected results and possible side effects. Keep mechanical edits in a reviewed script rather than relying on free-form text generation.
- Back up before changing state. Preserve the current configuration and relevant data, identify the exact target, and have a human approve commands that alter or remove software, ingest settings, or endpoint monitoring.
- Verify after the change. Check the relevant event or pipeline behavior again and record whether the issue is fixed, still present, or requires further debugging. Do not label a suggestion successful just because a command ran.
The author reports that a suggested configuration change did not fix a binary that continued to fail. The account treated it as a debugging problem still in progress rather than claiming remediation succeeded. It also describes carefully distinguishing a removable Universal Forwarder from Splunk itself, which held the lab data, during an MSI uninstall scenario. That is a reminder to confirm exactly what a destructive command targets before running it.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Context limits and prompt discipline
One investigation reportedly used 97.4% of the model’s reported 128K context window while pursuing an irrelevant detail. In a later run, the author reports 49.7% context use after reducing temperature from 0.8 to 0.3 and adding working rules. The author also reports four findings in a row in the later run, compared with one finding in 30 minutes in the earlier run. These are observations from the author’s runs, not controlled measurements of model quality or evidence that those settings will improve another workflow.
Rank #4
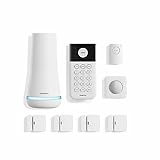
- Simple to set up. Seriously secure - Get ready to protect right out of the box. Just plug in the Base Station, download the SimpliSafe App, place your sensors, and start protecting your home. No wiring or drilling required. Or contact SimpliSafe directly if you need help installing your system.
- 1 FREE month of professional monitoring for fast police response when you need it most. With optional monitoring services, our agents keep watch even when you can't, ready to instantly alert emergency responders. Starting at less than $1/day with no long-term contracts or hidden fees. (SimpliSafe products and professional monitoring services are only offered for sale and supported in the US)
- Complete control of your system with the SimpliSafe App - Arm, disarm and protect anytime, anywhere.
- Protection for entry points - Entry Sensors protect windows, doors, and cabinets and alert you when someone tries to enter. Customizable and can send Secret Alerts so you are quietly alerted if someone accesses private areas, without sounding an alarm.
- Blanket a whole room - Motion sensors detect motion within 35 feet, have a 90 degree field of view and get along great with pets under 60lbs. Perfect for full room coverage when placed in a corner.
The practical lesson is to bound tasks and preserve evidence. Ask for a concise finding with its supporting records, then investigate a specific root cause separately. A large context window does not guarantee that an agent will spend its attention on the relevant issue.
Local execution is not the same as auditability
The author says no third-party data or infrastructure was used in this setup. That is a claim about this particular workflow, not proof that every local deployment keeps all data on-device: model servers, agents, plugins, telemetry, and surrounding applications must be checked in the actual environment.
Free tools Windows power users keep installed
One-click scans. No signup required.
There is also a distinction between keeping inference local and retaining an audit trail of prompts and responses. Splunk Threat Research Team’s October 31, 2025 article about its Ollama technology add-on says recent standard Ollama versions no longer log individual prompts and responses in server logs by default; organizations that need prompt-level auditing must implement application-layer logging. That statement is specific to the Ollama versions discussed and should be checked against the version actually deployed. The reported experiment used llama-server, not the Ollama workflow described in that article, so the Ollama logging behavior should not be assumed to describe its setup.
What the case shows—and what it does not
This home SOC report shows a local agent helping its operator inspect a real Splunk-and-Sysmon stack, identify several concrete problems, and make some corrections. It also shows why a human must validate findings, keep changes bounded, and leave failed fixes marked as unresolved. The reported ten findings and context figures belong to this single account. They do not establish general SOC capability, a reliable success rate, or a universal hardware requirement for local 27B models.
Splunk separately documents a local-model route through its Data Science and Deep Learning app: retrieve a model from Ollama through the LLM management interface, then use the Standalone LLM dashboard to run inference on text stored in Splunk. That is a documented integration option, not the workflow used in this case report and not evidence that an LLM can safely administer a deployment unattended.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




