Potentially, yes—but “billions” is an estimate, not a device-by-device count. A 2026 NDSS paper called BLERP found design flaws in Bluetooth Low Energy (BLE) re-pairing that can let an attacker replace pairing keys, impersonate a trusted device, downgrade security, inject commands, or establish a man-in-the-middle (MitM) position. A separate 2025 preprint, Stealtooth, found silent link-key replacement in Bluetooth Classic audio products. The practical risk depends on the operating system, Bluetooth stack, firmware, pairing mode and whether a fix is available.
What the “secret Bluetooth chip commands” headline really means
These attacks do not generally give someone arbitrary access to a Bluetooth radio chip or prove that every device is vulnerable. They exploit pairing and session-management behavior in the Bluetooth stack—the software and firmware that negotiate trust and encryption.
As an Amazon Associate I earn from qualifying purchases.
If an attack succeeds, the adversary may be able to act as an already trusted keyboard, mouse, headset or other peripheral; force a new pairing without knowing the old key; reduce the negotiated security; inject traffic or commands; or relay communications between the two legitimate devices.
The strongest evidence currently comes from two different studies:
#1 Best Overall

- JBL Deep Bass Sound: Get the most from your mixes with high-quality audio from secure, reliable earbuds with 8mm drivers featuring JBL Deep Bass Sound
- Comfortable fit: The ergonomic, stick-closed design of the JBL Vibe Beam fits so comfortably you may forget you're wearing them. The closed design excludes external sounds, enhancing the bass performance
- Up to 32 (8h + 24h) hours of battery life and speed charging: With 8 hours of battery life in the earbuds and 24 in the case, the JBL Vibe Beam provide all-day audio. When you need more power, you can speed charge an extra two hours in just 10 minutes.
- Hands-free calls with VoiceAware: When you're making hands-free stereo calls on the go, VoiceAware lets you balance how much of your own voice you hear while talking with others
- Water and dust resistant: From the beach to the bike trail, the IP54-certified earbuds and IPX2 charging case are water and dust resistant for all-day experiences
- BLERP (2026 NDSS): six flaws in BLE re-pairing, tested across a broad set of hosts and controllers.
- Stealtooth (July 2025 preprint): abuse of automatic pairing in Bluetooth Classic audio devices, including a man-in-the-middle variant combined with the previously described Breaktooth session-hijacking technique.
How BLERP breaks BLE re-pairing
Pairing keys are replaced without proving the old relationship
BLE pairing creates a long-term Pairing Key (PK). Later sessions derive a fresh Session Key (SK). The Bluetooth specification permits a device that was paired before to enter the pairing process again. BLERP abuses that transition: an attacker can impersonate the central or peripheral, start a new pairing, and obtain a replacement relationship without demonstrating possession of the original key.
Negotiation can be manipulated
During re-pairing, the attacker can alter feature negotiation, lower the security level or reduce key entropy. The result can be an impersonation or MitM position even when the devices advertise strong settings. The BLERP authors describe both single-channel and double-channel MitM variants.
The paper characterizes these as design flaws affecting “any standard-compliant BLE device that uses pairing,” regardless of Bluetooth version or nominal security level. That is a statement about the protocol design, not proof that every implementation is exploitable in the same way.
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallRank #2

- WORLD’S BEST IN-EAR ACTIVE NOISE CANCELLATION — Removes up to 2x more unwanted noise than AirPods Pro 2* so you can stay fully immersed in the moment.*
- BREAKTHROUGH AUDIO PERFORMANCE — Experience breathtaking, three-dimensional audio with AirPods Pro 3. A new acoustic architecture delivers transformed bass, detailed clarity so you can hear every instrument, and stunningly vivid vocals.
- HEART RATE SENSING — Built-in heart rate sensing lets you track your heart rate and calories burned for up to 50 different workout types.* With iPhone, you will have access to the Move ring, step count, and the new Workout Buddy,* powered by Apple Intelligence.*
- LIVE TRANSLATION — Communicate across language barriers using Live Translation,* enabled by Apple Intelligence.*
- EXTENDED BATTERY LIFE — Get up to 8 hours of listening time with Active Noise Cancellation on a single charge. Or up to 10 hours in Transparency using the Hearing Aid feature.*
How much user interaction is required?
- Keyboards and mice: the demonstrated attacks can be zero-click on input-limited devices, so there may be no confirmation dialog for the victim to approve.
- Phones and laptops: the researchers generally needed one confirmation, depending on the pairing mode.
A successful attack could therefore be especially serious for a computer that accepts input from a trusted Bluetooth keyboard or mouse.
What Stealtooth adds—and how it differs
Stealtooth targets Bluetooth Classic (BR/EDR), the variant widely used by many audio products, rather than BLE re-pairing. The researchers found commercial devices that automatically enter pairing mode after a failed reconnection or similar condition. An attacker impersonates a previously paired device and silently overwrites the victim’s link key.
In the reported MitM version, Stealtooth is combined with Breaktooth, a sleep-mode session-hijacking technique. That combination can intercept and relay traffic without the victim approving a visible pairing flow. The team tested 10 commercial products from major manufacturers, including Sony, Anker, Google and Xiaomi.
Rank #3

- Powerful Bass: soundcore P20i true wireless earbuds have oversized 10mm drivers that deliver powerful sound with boosted bass so you can lose yourself in your favorite songs.
- Personalized Listening Experience: Use the soundcore app to customize the controls and choose from 22 EQ presets. With "Find My Earbuds", a lost earbud can emit noise to help you locate it.
- Long Playtime, Fast Charging: Get 10 hours of battery life on a single charge with a case that extends it to 30 hours. If P20i true wireless earbuds are low on power, a quick 10-minute charge will give you 2 hours of playtime.
- Portable On-the-Go Design: soundcore P20i true wireless earbuds and the charging case are compact and lightweight with a lanyard attached. It's small enough to slip in your pocket, or clip on your bag or keys–so you never worry about space.
- AI-Enhanced Clear Calls: 2 built-in mics and an AI algorithm work together to pick up your voice so that you never have to shout over the phone.
| Aspect | BLERP | Stealtooth |
|---|---|---|
| Bluetooth variant | Bluetooth Low Energy (BLE) | Bluetooth Classic (BR/EDR), especially audio products |
| Entry condition | Re-pairing permitted after an existing relationship | Automatic pairing after failed reconnection or a similar trigger |
| Typical interaction shown | Zero-click on some keyboards and mice; usually one confirmation on phones and laptops, depending on mode | Silent on the tested automatic-pairing paths |
| Potential outcome | Peripheral impersonation, key replacement, downgrade, command or traffic injection, and MitM | Silent link-key overwrite and, with Breaktooth, MitM interception and relay |
| Evaluation | 22 targets spanning 15 BLE Hosts and 12 Controllers | 10 commercial Bluetooth devices |
How broad is the affected population?
BLERP testing covered 22 targets: 15 BLE Hosts, 12 Controllers, 16 Centrals and nine Peripherals. The Bluetooth versions represented ranged from 4.2 through 5.4, and the tests included Secure Connections, authenticated pairing and SCO settings. This demonstrates cross-version and cross-implementation exposure; it is not a census of all products in the world.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →The authors’ “billions” estimate extrapolates from widely deployed software stacks and shipment figures. They cite approximately 225 million iPhones shipped in 2024 and approximately 222 million Samsung Android smartphones shipped in 2024 as examples. Those are annual shipment numbers, not a measured total of vulnerable phones, and they do not establish that every unit shipped is exploitable.
What the researchers found in major stacks
| Platform or stack | Finding reported by the BLERP study |
|---|---|
| Apple | Three tested Apple devices were vulnerable to peripheral-impersonation and MitM attacks. The paper also reports an Apple-specific comparison bug that can force re-pairing even at the highest theoretical security level. |
| Android 10–15 | The Fluoride BLE stack was vulnerable to the principal impersonation and MitM attacks. Researchers also found a flaw that can delete a paired peripheral’s key after repeated encryption rejection. |
| Windows 11 | Several design flaws were exploitable. Automatic disconnection after encryption failure blocked one attack route but did not provide complete protection. |
| Linux 6.10.9 | Several design flaws were exploitable; the same encryption-failure disconnect behavior blocked one path but was not a universal defense. |
| NimBLE | All tested BLERP vulnerabilities and attacks were present. A bonding-flag issue was assigned CVE-2025-62235. |
| Zephyr | Custom logic blocked downgrade and entropy-reduction attacks, while some impersonation attacks remained possible when the security level was not reduced. |
| ESP32, BTstack and Garmin | Each showed a different subset of vulnerabilities, underscoring that product behavior and stack configuration determine practical exposure. |
Can an attacker secretly pair with your keyboard or phone?
Bluetooth keyboards and mice
They are among the most concerning cases because the demonstrated BLE attacks can require no click or approval on input-limited devices. If an attacker succeeds, a counterfeit peripheral could send keystrokes or pointer actions as though it were the trusted device.
Rank #4
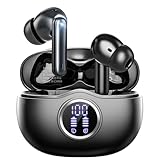
- Smart LED Display & 50H Sport Headphones: The A10 Bluetooth 5.3 earbuds feature an LED screen that shows real-time power levels for both the case and each earbud (0-100%). With 8 hours of playtime per charge and an IPX7 waterproof case, they deliver a total of 50 hours of use—ideal for gym sessions. They support fast charging via Type-C, taking just 1.5 hours to fully charge. Boasting an ultra-light 0.008lbs design, they stay secure during marathons.
- 3
- 4
- 5
- 6
Phones and laptops
The studies do not show universal silent compromise of every phone or laptop. In the tested BLE scenarios, these devices generally required one confirmation, depending on the pairing method. A prompt that appears unexpectedly should still be treated as suspicious, especially in a public place.
Earbuds and other audio products
Stealtooth specifically concerns Bluetooth Classic products with automatic pairing behavior. Whether a particular headset is exposed depends on its firmware and reconnection logic; the 10-device evaluation is evidence of a product class problem, not a complete catalog.
Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Repair Windows errors before they cause bigger problems3Scan for outdated or missing drivers - takes under a minuteWhat users should do now
- Install updates. Apply operating-system, Bluetooth-stack, headset, keyboard, mouse and IoT firmware updates when the manufacturer provides them. Affected-version lists and patches can change as vendors respond.
- Reject unexpected pairing confirmations. Do not approve a request that appears without a deliberate pairing action. Remove unknown or duplicate entries from the device’s Bluetooth settings.
- Disable Bluetooth when it is unnecessary in higher-risk settings. This reduces the available attack surface, although it is not a substitute for vendor fixes.
- Use wired input for sensitive work when practical. A wired keyboard or mouse avoids the specific wireless pairing path.
- Do not rely on discoverable mode alone. BLERP exploits re-pairing logic, and Stealtooth exploits automatic pairing behavior; simply hiding a device does not correct those implementation or protocol conditions.
No single consumer setting established by these papers eliminates the risk across all devices.
Best Value

- JBL Pure Bass sound: JBL Vibe Beam 2 earbuds feature 8mm dynamic drivers that deliver exciting JBL Pure Bass sound.
- Active Noise Cancelling:Listen to your surroundings & filter out distracting noise. Smart Ambient lets you control how much of the outside world you want to hear, so you can talk with others or stay aware of your surroundings while keeping your earbuds in
- 4 mics for crisp, clear calls: Two mics on each earbud pick up and clearly transmit your voice while canceling out ambient noise. So you can make clear, crisp calls even when you're walking through a busy park on a breezy day.
- 40 total hours of playback: Enjoy 10 hours of playtime, plus another three full charges (30Hrs) in the charging case.* Need to recharge even faster? 10 minutes on a USB type-C charging cable will give you another three hours of playtime. (*with ANC off)
- JBL Headphones app: Select the EQ that fits your style or customize your own. Voice Prompts in multiple languages give you useful information (e.g.if battery is running low). Or chill out and recharge in Relax Mode by choosing one of five peaceful sounds.
What vendors and stack maintainers should change
Backward-compatible hardening
The BLERP authors recommend disconnecting after encryption failure and blocking security downgrades. Their empirical tests found this approach stops some attack paths while retaining compatibility with existing devices.
Authenticated re-pairing
The stronger design binds the new key to the old key and to the complete negotiation transcript. The paper reports formal verification of this design with ProVerif, in addition to implementation testing.
Product-specific safeguards
Manufacturers should review automatic pairing triggers, bonding-flag handling, key deletion after repeated encryption failures, comparison logic and behavior when a peer requests a lower security level. The differing results across Apple, Android, Windows, Linux, NimBLE, Zephyr, ESP32, BTstack and Garmin show why a generic “Bluetooth version” label is not enough to assess exposure.
Recommended Free Tools
Could you reproduce the research in a lab?
The primary BLERP artifact lists two Nordic nRF52840-DK boards and publishes a toolkit, patches, Docker image and setup procedure. An nRF52840 development board is research hardware for controlled experiments, not a consumer security product. Reproduction should be limited to devices you own or are explicitly authorized to test.
The bottom line on “billions”
Bluetooth security researchers have demonstrated real, cross-version weaknesses in BLE re-pairing and automatic Bluetooth Classic pairing. The evidence supports concern about a very large installed base, but “billions of vulnerable devices” remains an extrapolation from shared stacks and shipment data—not a global count. Your actual risk is determined by the device model, stack implementation, firmware version, pairing mode and whether the vendor has deployed the recommended fixes.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




