Freedom251 › Threat Intelligence Platforms
Pulse Intelligence
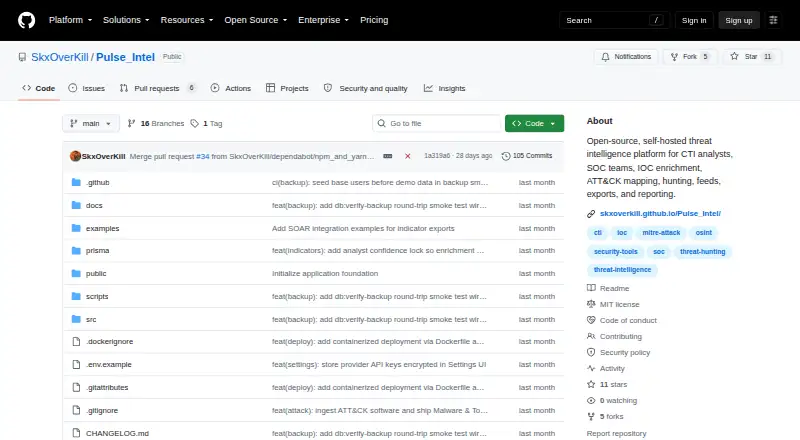
What Pulse Intelligence is
Pulse Intelligence is an open-source, self-hosted threat intelligence workspace for analysts, junior CTI teams, and SOC teams. It brings threat actors, aliases, campaigns, indicators, reports, sources, CVEs, and ATT&CK mappings into one platform. The platform ingests public feeds from CISA KEV, NVD, FIRST EPSS, abuse.ch, OTX, vendor blogs, and security news. It can enrich indicators through OTX, AbuseIPDB, and VirusTotal, with Redis-backed quota controls.
Analysts can save hunts across indicator fields, get alerts when new matches appear, and export hunt results. Filtered indicators can also be exported as CSV, STIX 2.1, MISP JSON, or Snort and Suricata rules. Scheduled Markdown reports can cover new indicators, KEV additions, hunt alerts, and feed health. A read-only public API uses scoped keys for analyst scripts, SOAR playbooks, internal tools, and other integrations. Its default rate limit is 120 requests per API key per 60-second window, and indicator pages are capped at 500. The project lists Argon2id passwords, database-backed session cookies, hashed API keys, and an admin-only audit log. Whitelisted indicators are excluded from API responses and exports, while expired indicators are excluded from API results. Deployment requires Node.js 20.9 or later, PostgreSQL 17 or compatible PostgreSQL, and a Redis-compatible server.
Who it suits
Pulse Intelligence suits analysts, junior CTI teams, and SOC teams that want a self-hosted workspace for threat data, hunts, and reporting. It also fits teams connecting threat intelligence to analyst scripts, SOAR playbooks, or internal tools through a read-only API.
What it does well
- Tracks actors, campaigns, indicators, CVEs, and ATT&CK mappings.
- Ingests public feeds from CISA KEV, NVD, OTX, and others.
- Enriches indicators through OTX, AbuseIPDB, and VirusTotal.
- Exports filtered indicators in CSV, STIX 2.1, MISP JSON, and rule formats.
- Creates scheduled Markdown reports and alerts for new hunt matches.
What to know first
- Requires Node.js 20.9+, PostgreSQL, and a Redis-compatible server.
- The API defaults to 120 requests per key per 60 seconds.
- Indicator page size is capped at 500.
- The README says the final hardening phase is still in progress.
Limits
The open-source self-hosted plan costs nothing and requires Node.js 20.9+, PostgreSQL 17 or compatible PostgreSQL, and a Redis-compatible server. API routes default to 120 requests per key per 60-second window, and indicator page size is capped at 500.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Open-source self-hosted | Self-hosted; requires Node.js 20.9+, PostgreSQL 17, and a Redis-compatible server | Free |
As github.com lists them, read 8 Oct 2026. The maker's own page has the final word.
Getting started
- Open the project website on GitHub.
- Choose the documented direct Node deployment or Docker Compose full-stack deployment.
- Provide Node.js 20.9 or later, PostgreSQL 17 or compatible PostgreSQL, and a Redis-compatible server.
- Keep both the web app and worker running.
Overview
Pulse Intelligence brings threat data and analyst workflows into a self-hosted workspace. It is aimed at analysts and junior CTI or SOC teams, particularly those that want to manage their own deployment and shape intelligence into hunts, exports, and reports. Its broad workflow coverage is a strong fit for that audience, but operating its web app and worker alongside a database and Redis-compatible service is a real commitment.
Key features
The workspace covers threat actors and aliases, campaigns, indicators, reports, sources, CVEs, and ATT&CK mappings. It pulls in public material from CISA KEV, NVD, FIRST EPSS, abuse.ch, OTX, vendor blogs, and security news, giving teams several kinds of intelligence to correlate rather than limiting them to one feed type.
Indicator enrichment uses OTX, AbuseIPDB, and VirusTotal, with Redis-backed quota controls. Saved hunts can search indicator fields, alert on new matches, and export results. Filtered IOCs can also be exported as CSV, STIX 2.1, MISP JSON, or Snort and Suricata rules. Together, these options make the platform useful for teams that need to move findings into analysis and detection workflows; teams seeking a managed service should look elsewhere.
Scheduled Markdown reports can cover new indicators, KEV additions, hunt alerts, and feed health. A read-only API with scoped keys supports scripts, SOAR playbooks, and internal tools. Its default limit is 120 requests per API key in a 60-second window, configurable through environment variables, and indicator page size is capped at 500. The listed safeguards include Argon2id passwords, database-backed session cookies, hashed API keys, and an admin-only audit log. Whitelisted indicators are excluded from API responses and exports; expired indicators are excluded from API results.
Pricing
The Open-source self-hosted plan costs nothing. It includes the self-hosted software, with no free trial; the trade-off is that teams must provide the deployment environment and keep both the web app and worker running. There are no paid tiers to weigh against the free plan in this offering.
Platforms
Pulse Intelligence supports API, Linux, macOS, web, Windows, and self-hosted use. Deployment requires Node.js 20.9 or later, PostgreSQL 17 or a compatible PostgreSQL service, and a Redis-compatible server. The project documents both direct Node deployment and a Docker Compose full-stack option, but neither removes the need to operate the supporting components. The project describes phases 1–7 of 8 as implemented, with the final phase covering hardening, large-table partitioning, and deeper security review.
Who it's for
Analysts and junior CTI teams that want a self-managed place to ingest feeds, enrich indicators, save hunts, and produce reports are the clearest fit. SOC teams can also make use of the API and detection-oriented export formats. The technical requirements and ongoing app-and-worker operation make it a poor match for organizations that want a turnkey hosted workspace or lack capacity to manage its dependencies.
Pros and cons
- Pros: Broad threat tracking and multiple public feed sources give analysts a wider base for investigations.
- Pros: Enrichment, alerting saved hunts, scheduled reports, and several IOC export formats support work beyond simply collecting indicators.
- Pros: Scoped read-only API keys and explicit indicator safeguards give teams useful integration and handling controls.
- Cons: Node.js, PostgreSQL, and Redis-compatible infrastructure, plus a continuously running worker, add operational overhead.
- Cons: API throughput is bounded by the default 120 requests per key per 60 seconds, and indicator pages cannot exceed 500 entries.
- Cons: The project still has a final hardening phase underway, so teams seeking a fully mature security review should take that status into account.
Alternatives
Choose OpenAEV instead if attack simulation and tabletop exercises are the priority: its free Community Edition is on-premise and centers on those capabilities. IBM X-Force Exchange offers a freemium web portal, but its free tier does not include X-Force API access. IntelOwl is another free, open-source self-hosted option for teams comparing intelligence tools.
Kaspersky Threat Intelligence Portal may suit teams looking for curated portal access, though its free access limits features and the number of suspicious files and URLs for Cloud Sandbox. MISP is a free open-source alternative under AGPL; a yearly support contract is also offered. ThreatForge has an open-source Community Edition and a commercial Enterprise Edition. Threat Intelligence Platform is a freemium web and API option whose free subscription uses credits for analysis and API requests. Security Vision TIP is a paid option with individually calculated pricing.
Browse more options in Threat Intelligence Platforms; Container Monitoring is a separate category for teams evaluating that kind of software.
Verdict
Pulse Intelligence is a strong choice for analyst and junior CTI teams that want an open-source, self-hosted workspace spanning feed ingestion, enrichment, saved hunts, exports, and scheduled reporting. Its breadth is the main reason to choose it; the need to deploy and maintain Node.js, PostgreSQL, Redis-compatible infrastructure, and a running worker is the main reason to look elsewhere.
Verdict
Choose Pulse Intelligence if your team wants an open-source, self-hosted threat intelligence workspace with feed ingestion, enrichment, saved hunts, exports, and scheduled reports. It requires a Node.js, PostgreSQL, and Redis-compatible deployment, so teams without those components should look elsewhere.
Questions
Is Pulse Intelligence free?
Yes. The Open-source self-hosted plan is free.
Does it offer a free trial?
No free trial is listed; the product is offered as a free plan.
What platforms does it support?
The listed platforms are API, Linux, macOS, self-hosted, web, and Windows.
What does deployment require?
Deployment requires Node.js 20.9 or later, PostgreSQL 17 or compatible PostgreSQL, and a Redis-compatible server.
Can it export threat indicators?
Yes. Filtered indicators can be exported as CSV, STIX 2.1, MISP JSON, and Snort or Suricata rules.
What is the API rate limit?
API routes default to 120 requests per API key per 60-second window. Indicator page size is capped at 500.
Facts from Pulse Intelligence's own pages
- API
- The public API is read-only, supports scoped API keys, and is intended for analyst scripts, SOAR playbooks, internal tools, and integrations. · github.com, 8 Oct 2026
- API limits
- The API defaults to 120 requests per API key per 60-second window, and indicator page size is capped at 500. · github.com, 8 Oct 2026
- API rate limit
- API routes default to 120 requests per API key per 60-second window, configurable by environment variables. · github.com, 8 Oct 2026
- Audience
- The project describes its users as analysts, junior CTI teams, and SOC teams. · github.com, 8 Oct 2026
- Data handling
- Whitelisted indicators are excluded from API responses and exports, and expired indicators are excluded from API results. · github.com, 8 Oct 2026
- Deployment
- The maker documents direct Node deployment and a Docker Compose full-stack deployment, with both the web app and worker kept running. · github.com, 8 Oct 2026
- Deployment requirements
- Deployment requires Node.js 20.9+, PostgreSQL 17, and a Redis-compatible server; the project documents native and Docker deployment paths. · github.com, 8 Oct 2026
- Enrichment
- It enriches indicators through OTX, AbuseIPDB, and VirusTotal, with Redis-backed quota controls. · github.com, 8 Oct 2026
- Exports
- Filtered IOCs can be exported as CSV, STIX 2.1, MISP JSON, and Snort or Suricata rules. · github.com, 8 Oct 2026
- Feeds
- It ingests public feeds from CISA KEV, NVD, FIRST EPSS, abuse.ch, OTX, vendor blogs, and security news. · github.com, 8 Oct 2026
- Hunting
- Users can create saved hunts over indicator fields, receive alerts for new matches, and export hunt matches. · github.com, 8 Oct 2026
- Integrations
- Its public read-only API supports scoped keys and integrations such as analyst scripts, SOAR playbooks, and internal tools. · github.com, 8 Oct 2026
- IOC safeguards
- Whitelisted indicators are never returned by public API or export routes, and expired indicators are also excluded from the API. · github.com, 8 Oct 2026
- Product
- Pulse Intelligence is an open-source, self-hosted threat intelligence platform for analyst workflows. · github.com, 8 Oct 2026
- Project status
- The README says phases 1–7 of 8 are implemented and phase 8 covers hardening, large-table partitioning, and deeper security review. · github.com, 8 Oct 2026
- Purpose
- Pulse Intelligence is an open-source, self-hosted threat intelligence workspace for analysts and junior CTI teams. · github.com, 8 Oct 2026
- Reports
- The platform can generate scheduled Markdown reports from new indicators, KEV additions, hunt alerts, and feed health. · github.com, 8 Oct 2026
- Requirements
- The documented deployment requires Node.js 20.9+, PostgreSQL 17 or compatible PostgreSQL, and a Redis-compatible server. · github.com, 8 Oct 2026
- Security
- The repository lists Argon2id passwords, database-backed session cookies, hashed API keys, and an admin-only audit log. · github.com, 8 Oct 2026
- Security controls
- The README lists Argon2id passwords, database-backed session cookies, hashed API keys, and an admin-only audit log. · github.com, 8 Oct 2026
- Threat data
- It tracks threat actors, aliases, campaigns, indicators, reports, sources, CVEs, and ATT&CK mappings. · github.com, 8 Oct 2026
- Threat tracking
- It tracks threat actors, aliases, campaigns, indicators, reports, sources, CVEs, and ATT&CK mappings. · github.com, 8 Oct 2026
Where Pulse Intelligence stands on Freedom251
- Threat Intelligence Platforms#3 of 32
- Container Monitoring#24 of 49