Freedom251 › Container Image Scanning Tools
Clair
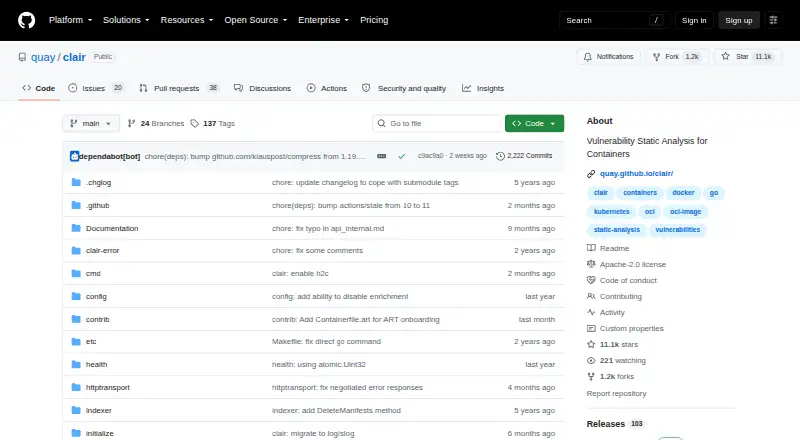
What Clair is
Clair is a free, open-source project for static vulnerability analysis of application container images, including OCI and Docker images. Clients submit image manifests to the Clair API for indexing and vulnerability matching. Clair fetches and scans image layers, then returns a persisted IndexReport; it analyzes image contents rather than runtime behavior. Content-addressed OCI manifests and layers help reduce repeated indexing work. Clair continually ingests security data, while matcher requests provide current vulnerability analysis for an IndexReport. Its notifier checks indexed manifests for newly discovered vulnerabilities and responds according to its configuration. The documented support matrix includes Ubuntu, Debian, RHEL, SUSE, Oracle, Alpine, AWS Linux, VMware Photon, and Python base containers. Clair v4 uses ClairCore to examine image contents and report vulnerabilities. Release notes for v4.9.0 describe NVD 2.0 JSON feeds for CVSS enrichment and encoding index reports as SPDX 2.3 documents. Clair is licensed under Apache 2.0 and is intended for self-hosted use. The project README warns that the main branch may be unstable or broken and directs users to releases for stable binaries. Community contact options include a mailing list, IRC channel, and GitHub issues.
Who it suits
Clair suits teams that need to analyze container image contents for vulnerabilities and can operate a self-hosted Linux or API-based setup. Its documented image support covers several Linux distributions and Python base containers.
What it does well
- Free and licensed under Apache 2.0.
- Analyzes OCI and Docker images statically.
- Content-addressed layers reduce duplicated indexing work.
- Supports SPDX 2.3 index report output.
- Provides mailing list, IRC, and GitHub issue contacts.
What to know first
- The main branch may be unstable or broken.
- Analysis covers image contents, not runtime behavior.
- The documented support matrix covers specific image contents.
Limits
The free plan is self-hosted container vulnerability analysis. Clair analyzes image contents statically rather than runtime behavior.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Clair | Open source · self-hosted container vulnerability analysis | Free |
As github.com lists them, read 4 Oct 2026. The maker's own page has the final word.
Getting started
- Open the Clair GitHub project website.
- Choose a release for stable binaries; the README warns the main branch may be unstable or broken.
- Deploy Clair in a self-hosted Linux environment.
- Submit container image manifests to its API for indexing and vulnerability matching.
Verdict
Clair provides a self-hosted path for indexing container images and matching their contents against vulnerability data. Use stable releases rather than the main branch when stable binaries are needed.
Questions
Is Clair free?
Yes. Its free plan is listed as free.
What platforms does Clair support?
The listed platforms are API, Linux, and self-hosted deployment.
Is Clair open source?
Yes. Clair is licensed under Apache 2.0.
What images can it analyze?
The documented support matrix includes Ubuntu, Debian, RHEL, SUSE, Oracle, Alpine, AWS Linux, VMware Photon, and Python base containers.
Does Clair generate SBOM documents?
ClairCore can encode index reports as SPDX 2.3 documents.
How can users contact the project?
The README lists a mailing list, an IRC channel, and GitHub issues as community contact options.
Facts from Clair's own pages
- Analysis mode
- Clair parses image contents and reports vulnerabilities using static analysis rather than runtime analysis. · quay.github.io, 4 Oct 2026
- Current vulnerability data
- Clair continually ingests security data, and matcher requests provide up-to-date vulnerability analysis for an IndexReport. · quay.github.io, 4 Oct 2026
- Deduplication
- Clair uses content-addressed OCI manifests and layers to reduce duplicated indexing work. · quay.github.io, 4 Oct 2026
- Engine
- Clair v4 uses the ClairCore library as its engine for examining image contents and reporting vulnerabilities. · quay.github.io, 4 Oct 2026
- Indexing
- Clair fetches image layers, scans their contents, and returns a persisted IndexReport. · quay.github.io, 4 Oct 2026
- License
- The project is licensed under Apache 2.0. · github.com, 4 Oct 2026
- Notifications
- The notifier checks whether newly discovered vulnerabilities affect indexed manifests and acts according to its configuration. · quay.github.io, 4 Oct 2026
- Output format
- The v4.9.0 release notes state that ClairCore can encode index reports as SPDX 2.3 documents. · github.com, 4 Oct 2026
- Purpose
- Clair is an open source project for static analysis of vulnerabilities in application containers, including OCI and Docker images. · github.com, 4 Oct 2026
- Security data update
- The v4.9.0 release notes state that ClairCore switched to NVD 2.0 JSON feeds for CVSS enrichment data. · github.com, 4 Oct 2026
- Stable builds
- The README warns that the main branch may be unstable or broken and directs users to releases for stable binaries. · github.com, 4 Oct 2026
- Support
- The project README lists a mailing list, an IRC channel, and GitHub issues as community contact options. · github.com, 4 Oct 2026
- Supported image contents
- The documented support matrix lists Ubuntu, Debian, RHEL, SUSE, Oracle, Alpine, AWS Linux, VMware Photon, and Python base containers. · quay.github.io, 4 Oct 2026
- Workflow
- Clients submit container image manifests to the Clair API for indexing and vulnerability matching. · github.com, 4 Oct 2026
Where Clair stands on Freedom251
- Container Image Scanning Tools#4 of 29