Freedom251 › Cloud Security Posture Management Software
Mondoo CSPM
What Mondoo CSPM is
Mondoo CSPM scans cloud environments and helps teams address misconfigurations by prioritizing them according to exploitability and business exposure. It covers AWS, Azure, and Google Cloud through a shared posture and remediation workflow. Proposed fixes arrive as code changes and pull requests, which users review and approve. Mondoo rechecks completed fixes and records evidence to keep posture and compliance information current. Teams can version, audit, and enforce security and compliance rules as policy code across accounts and clouds. Listed posture mappings include CIS Benchmarks, PCI DSS, HIPAA, GDPR, SOC 2, ISO 27001, and NIS2. Other listed capabilities include infrastructure-as-code scanning, identity risk analysis, attack path analysis, asset inventory, and automated remediation. Mondoo lists 106 integrations, including AWS, Azure, Google Cloud, Kubernetes, Terraform, and GitHub Actions, and can import findings from Qualys, CrowdStrike Falcon, and Snyk. The free Open Source Tools plan includes scanning for cloud, Kubernetes, OS, SaaS, and API environments. Managed Service pricing is custom and not listed.
Who it suits
Mondoo CSPM suits teams managing cloud posture and remediation across AWS, Azure, or Google Cloud. Its policy-as-code and compliance mappings may also fit teams tracking security requirements across accounts and clouds.
What it does well
- AWS, Azure, and Google Cloud in one workflow
- Proposed fixes require human review and approval
- Rechecks fixes and records evidence
- 106 integrations listed
- Free forever Open Source Tools plan
What to know first
- Managed Service pricing is custom and not listed
- Every agent-generated fix requires user review and approval
Limits
The free Open Source Tools plan includes base vulnerability management. Risk-based vulnerability management, security posture management, automated remediation, compliance and evidence collection, and expert support are listed with the custom-priced Managed Service.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Open Source Tools | Free forever · Cloud, Kubernetes, OS, SaaS and API scanning · Kubernetes operator · extensible providers · asset inventory · open-source policies · base vulnerability management | Free |
| Managed Service | Custom Pricing · Risk-based vulnerability management · posture management · automated remediation · dashboards · compliance evidence · executive reporting · success manager | On request |
As mondoo.com lists them, read 14 Oct 2026. The maker's own page has the final word.
Getting started
- Visit the Mondoo CSPM website.
- Choose the free Open Source Tools plan or request details about the custom-priced Managed Service.
- Connect cloud environments or other supported sources through the listed integrations.
- Use policy code to define and enforce security and compliance rules.
- Review and approve proposed fixes, then use Mondoo's rechecks and recorded evidence to track posture.
Mondoo CSPM is a cloud security posture management service for organizations securing AWS, Azure, and Google Cloud. It is best suited to teams that want risk findings connected to controlled remediation and evidence, rather than a scanner that ends at alerts. Its central trade-off is deliberate: proposed fixes require human review and approval.
Overview
Mondoo brings cloud posture work across three major cloud providers into one remediation workflow. It continuously scans environments and prioritizes misconfigurations by exploitability and business exposure, helping teams direct attention beyond a raw list of findings.
Fixes are delivered as code changes and pull requests, then rechecked after remediation with evidence recorded to keep posture and compliance information current. This creates a traceable loop from finding to proposed change to verification, though teams must be prepared to review agent-generated changes rather than rely on unattended application.
Founded in 2020 in Berlin, Mondoo was established by DevOps and security specialists who previously created Chef InSpec and DevSec.io and contributed to OpenStack. The company says its core tools, cnquery and cnspec, are open source and used by thousands of organizations.
Readers comparing this space can also explore Cloud Security Posture Management Software, Security Configuration Management Software, Cloud Vulnerability Scanners, Exposure Management Software, and Container Image Scanning Tools.
Key features
Prioritized multi-cloud findings
Continuous scanning covers AWS, Azure, and Google Cloud through a shared posture and remediation workflow. Ranking issues by exploitability and business exposure is more decision-oriented than treating every misconfiguration equally, particularly for teams managing several cloud accounts. Mondoo also supports asset inventory, identity risk analysis, attack path analysis, and infrastructure-as-code scanning, extending the assessment beyond configuration checks alone.
Remediation with a human checkpoint
Automated remediation proposals take the form of reviewable code changes and pull requests, and users approve every agent-generated fix. That is a useful safeguard for teams that need control over production changes; it is less suitable for buyers whose priority is fully automatic correction without an approval step.
Verification, policy, and compliance
Mondoo rechecks fixes and records evidence. Security and compliance rules can be maintained as version-controlled, auditable policy code and enforced across accounts and clouds. Its posture mappings cover CIS Benchmarks, PCI DSS, HIPAA, GDPR, SOC 2, ISO 27001, and NIS2, making the evidence workflow relevant to teams tracking several frameworks.
Mondoo lists 106 integrations, including AWS, Azure, Google Cloud, Kubernetes, Terraform, and GitHub Actions. It can also import vulnerability or security findings from tools such as Qualys, CrowdStrike Falcon, and Snyk, which may help consolidate existing tool output. Mondoo identifies SOC 2 Type II and ISO 27001 among its own security and compliance credentials.
Pricing
Mondoo uses a freemium model with a free forever plan and a custom-priced managed offering. There is no seat or scan quota stated for the free plan in the plan terms below, so buyers should not assume a particular capacity ceiling from the plan name alone.
| Plan | Price | What it includes | Best fit |
|---|---|---|---|
| Open Source Tools | free | Free forever; cloud, Kubernetes, OS, SaaS, and API scanning; Kubernetes operator; extensible provider system; asset inventory; open-source policies; base vulnerability management. | Teams that want broad scanning and a starting point for vulnerability management without a subscription price. |
| Managed Service | Custom pricing | Tailored to infrastructure size and needs; risk-based vulnerability management, security posture management, automated remediation, compliance and evidence collection, and an expert Mondoo Vulnerability Management Success Manager. | Organizations seeking managed support and a service shaped around their infrastructure. |
The free plan is a meaningful entry point, but it is explicitly base vulnerability management rather than the fuller managed service, which adds risk-based management, posture work, remediation, compliance evidence, and expert support. Buyers that need that service should expect a custom quote.
Platforms
Mondoo supports API, Linux, macOS, web, and Windows environments. Its cloud posture coverage includes AWS, Azure, and Google Cloud, while the free plan also names Kubernetes, OS, SaaS, and API scanning.
Who it's for
Mondoo is a strong fit for organizations with multi-cloud estates that need prioritized configuration risk, reviewable code-based fixes, and evidence that remediation was checked. The policy-as-code approach also suits teams that want security and compliance rules versioned and auditable across accounts.
It is a weaker fit for buyers who want remediation to happen without human approval, or who need a clearly priced managed service before discussing infrastructure needs. Teams seeking only a narrow, free configuration utility may find the broader workflow unnecessary.
Pros and cons
- Shared AWS, Azure, and Google Cloud workflow: supports posture assessment and remediation across these providers without splitting the process by cloud.
- Findings tied to controlled fixes and evidence: code changes require approval, and fixes are rechecked with evidence recorded.
- Broad policy and integration reach: mappings span seven named frameworks, while integrations include cloud, Kubernetes, infrastructure-as-code, CI, and third-party security tools.
- Free forever starting plan: includes several scanning types, inventory, policies, and base vulnerability management.
- Approval remains part of remediation: teams looking for fully unattended fixes will need to account for the review step.
- Managed Service is custom priced: organizations cannot compare it against a published fixed fee without obtaining a tailored price.
Alternatives
Choose Puppet if a freemium option with a free trial and custom-priced Enterprise plans, including 10 free nodes for Puppet Enterprise, better matches the purchase being considered. Choose Steampipe if an open-source CLI that needs no database is the priority. Chef InSpec is another freemium option, with a free tier limited to non-production workloads and personal, non-commercial use, plus a 30-day trial.
Choose Kubescape for a free, Apache 2.0-licensed CLI and Kubernetes operator that can be self-hosted. OpenSCAP is a free, open-source choice for readers looking for its suite of tools across supported environments. Prowler Cloud offers a 15-day free trial with no cloud-account limit and access to every check and compliance framework, alongside an open-source plan.
DigitalOcean Cloud Security Posture Management is worth considering for readers seeking a DigitalOcean-focused option, with unlimited manual scans for standard rules on its free plan and a $5 a month Basic plan billed per covered workload. Lynis is a free and open-source alternative with a paid SaaS premium plan.
Verdict
Mondoo CSPM is a compelling choice for multi-cloud teams that want findings prioritized by potential impact, proposed fixes kept under human control, and remediation evidence carried into compliance work. Its free forever scanning and base vulnerability management make it approachable, while its strongest managed capabilities require custom pricing. Choose it when that connected workflow matters; look elsewhere if you need approval-free remediation or a predictable published managed-service price.
Verdict
Mondoo CSPM pairs cloud scanning and risk prioritization with reviewable remediation proposals and evidence tracking. A free forever plan covers scanning and base vulnerability management; Managed Service pricing is custom and not listed.
Questions
Is Mondoo CSPM free?
Yes. The Open Source Tools plan is free forever and includes cloud, Kubernetes, OS, SaaS, and API scanning, among other tools.
What does the Managed Service cost?
Its price is custom and tailored to infrastructure size and needs.
Which cloud providers does it cover?
It covers AWS, Azure, and Google Cloud in one posture and remediation workflow.
Does Mondoo CSPM support compliance frameworks?
Yes. Listed posture mappings include CIS Benchmarks, PCI DSS, HIPAA, GDPR, SOC 2, ISO 27001, and NIS2.
Is it open source?
Mondoo says its core tools, cnquery and cnspec, are open source. The free plan includes open-source policies.
Who makes Mondoo?
Mondoo was founded in 2020 and is headquartered in Berlin, Germany.
Facts from Mondoo CSPM's own pages
- AI prioritization
- Mondoo scores findings by exploitability and business exposure instead of relying only on raw severity. · mondoo.com, 14 Oct 2026
- API
- Mondoo exposes a GraphQL API authenticated with scoped bearer API tokens, service accounts or workload identity federation. · mondoo.com, 14 Oct 2026
- Closed-loop remediation
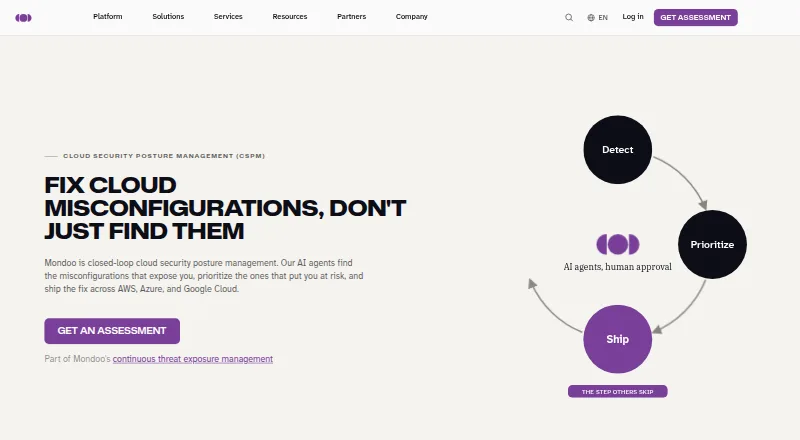
- The CSPM workflow detects findings, scores them, generates reviewable code changes or pull requests, and rechecks fixes as evidence. · mondoo.com, 14 Oct 2026
- Cloud coverage
- CSPM covers AWS, Azure, and Google Cloud in one posture and remediation workflow. · mondoo.com, 29 Sept 2026
- Company founding
- Mondoo says it was founded in 2020 by DevOps and security experts formerly associated with Chef InSpec, DevSec.io and OpenStack. · mondoo.com, 14 Oct 2026
- Company history
- Mondoo says it was founded in 2020 by DevOps and security experts who previously created Chef InSpec and DevSec.io and contributed to OpenStack. · mondoo.com, 29 Sept 2026
- Company legal name
- Crunchbase identifies the legal name as Mondoo, Inc. · crunchbase.com, 14 Oct 2026
- Compliance
- The CSPM page lists CIS Benchmarks, PCI DSS, HIPAA, GDPR, SOC 2, ISO 27001, and NIS2 posture mappings. · mondoo.com, 29 Sept 2026
- Continuous compliance
- The CSPM maps posture to CIS Benchmarks, PCI DSS, HIPAA, GDPR, SOC 2, ISO 27001 and NIS2. · mondoo.com, 14 Oct 2026
- CSPM purpose
- Mondoo CSPM continuously scans cloud environments, prioritizes misconfigurations by exploitability and business exposure, and delivers fixes as reviewable code changes and pull requests. · mondoo.com, 29 Sept 2026
- Deployment options
- cnspec can be installed with scripts, package managers, MSI or standalone binaries and can scan remote targets without installing software on the target. · mondoo.com, 14 Oct 2026
- Developer tooling
- Mondoo provides the cnspec CLI, cnquery, MQL and an xgrep code scanner, plus a Visual Studio Code security extension. · mondoo.com, 14 Oct 2026
- Documentation depth
- Documentation includes platform quickstarts, installation, provider management, MQL resource references, compliance, reporting, access control, API tokens and audit logs. · mondoo.com, 14 Oct 2026
- Founded
- 2020 · mondoo.com, 23 Sept 2026
- Funding
- Mondoo announced $15 million raised from Atomico, First Minute Capital and System.One in October 2021. · mondoo.com, 14 Oct 2026
- Headquarters
- Berlin, Germany · mondoo.com, 23 Sept 2026
- Headquarters and size
- LinkedIn lists San Francisco, California headquarters and 51–200 employees. · linkedin.com, 14 Oct 2026
- Human approval
- The CSPM page says users review and approve every agent-generated fix. · mondoo.com, 29 Sept 2026
- Identity and data exposure
- Policies identify over-permissive IAM, public data stores, missing encryption and internet-exposed services. · mondoo.com, 14 Oct 2026
- Independent certification
- CIS lists Mondoo products certified against numerous CIS benchmarks for AWS, Azure, Google Cloud, Kubernetes, operating systems and other technologies. · cisecurity.org, 14 Oct 2026
- Integrations
- Mondoo lists 118 integrations, including AWS, Azure, Google Cloud, Kubernetes, Terraform, GitHub Actions, Qualys, CrowdStrike, Snyk, Jira and ServiceNow. · mondoo.com, 14 Oct 2026
- License
- The cnspec GitHub repository identifies its license as Business Source License 1.1 (BUSL 1.1). · github.com, 14 Oct 2026
- Limit: custom pricing
- Toolradar and Mondoo list enterprise or managed-service pricing as custom, so buyers cannot calculate a public price from the site. · toolradar.com, 14 Oct 2026
- Limit: Splunk dependency
- The Splunk app supplies dashboards only and cannot collect Mondoo data without the separate Technology Add-on. · splunkbase.splunk.com, 14 Oct 2026