Freedom251 › Monorepo Management Tools
affected
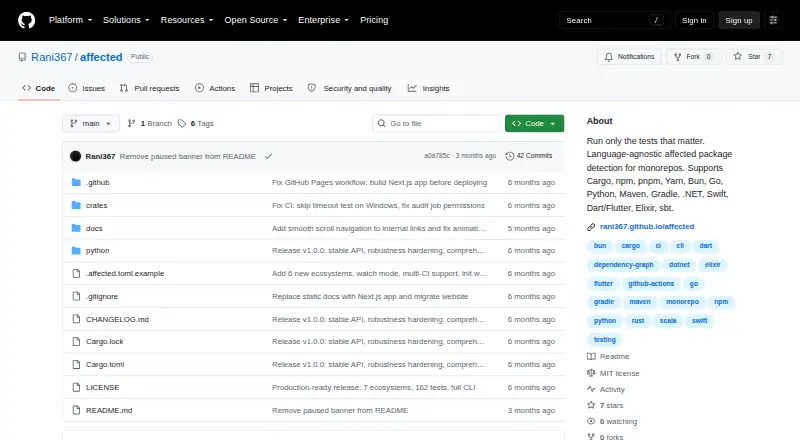
What affected is
affected is a free, MIT-licensed command-line tool for monorepos. It identifies packages affected by Git changes and can run tests or other commands on them. The README says it detects the project type and dependency graph automatically to get started without configuration. Its dependency analysis follows transitive links and can show the chain that connects a change to an affected package. Supported ecosystems include Cargo, npm, pnpm, Yarn, Bun, Go, Python, Maven, Gradle, .NET, Swift, Dart/Flutter, Elixir, and Scala/sbt. Commands cover listing packages, testing, running tasks, viewing graphs, CI, initialization, and watch mode. Execution can use parallel jobs, dry-run previews, timeouts, package filters, and skip patterns. Results can be provided as JSON, JUnit XML, CI output, shell completions, dependency trees, or DOT graphs. GitHub Actions support includes setup and dynamic job matrices, and a companion action can post and update pull request comments with affected packages and reasons. Installation options include Homebrew, Python tools, Cargo, GitHub Actions, or a release binary. It runs on Linux, macOS, and Windows.
Who it suits
affected suits developers and teams working in monorepos who want to target tests or other commands to packages touched by Git changes. Its CI formats and GitHub Actions support are relevant to teams automating affected-package checks.
What it does well
- Traces transitive dependencies and explains the chain.
- Supports a broad range of ecosystems.
- Commands can run in parallel.
- Supports GitHub Actions job matrices.
- MIT licensed and free.
What to know first
- It is a command-line tool.
- Package support is limited to the listed ecosystems.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| affected | MIT-licensed software · standalone CLI | Free |
As github.com lists them, read 3 Oct 2026. The maker's own page has the final word.
Getting started
- Choose an installation route: Homebrew, uv, pipx, pip, Cargo, GitHub Actions or a binary from Releases.
- Use the CLI in a project; its README says it detects the project type and dependency graph without configuration to start.
- Use list, test or run to select packages and execute commands.
- Use ci for CI output, or graph to inspect dependencies.
- For GitHub Actions, use the documented setup action and dynamic job matrices; the companion action can post or update pull request comments.
Verdict
affected combines package-impact analysis with commands for testing, CI, and other tasks. Its ecosystem support and output options make it applicable across varied monorepo setups.
Questions
Is affected free?
Yes. The listed plan is free, and the software is open source under the MIT license.
Which operating systems does it support?
It supports Linux, macOS and Windows.
Which package ecosystems does it support?
Listed ecosystems include Cargo, npm, pnpm, Yarn, Bun, Go, Python, Poetry, uv, Maven, Gradle, .NET/C#, Swift/SPM, Dart/Flutter, Elixir/Mix and Scala/sbt.
Can it integrate with CI?
Its CI output supports GitHub Actions, GitLab, CircleCI, Azure Pipelines and generic key-value output. GitHub Actions features include setup, dynamic job matrices and a companion action for pull request comments.
How can I install it?
Documented options include Homebrew, uv, pipx, pip, Cargo, GitHub Actions and a binary downloaded from Releases.
What does it do with package dependencies?
It traces transitive dependencies to identify packages affected by a Git change and can explain the dependency chain.
Facts from affected's own pages
- CI integrations
- Its CI output supports GitHub Actions, GitLab, CircleCI, Azure Pipelines and generic key-value output. · github.com, 3 Oct 2026
- Commands
- The CLI provides list, test, run, graph, ci, init and watch commands. · github.com, 3 Oct 2026
- Dependency analysis
- It traces transitive dependencies to identify packages affected by a change and can explain the dependency chain. · github.com, 3 Oct 2026
- Distribution
- The README documents installation through Homebrew, uv, pipx, pip, Cargo, GitHub Actions or a binary downloaded from Releases. · github.com, 3 Oct 2026
- Ecosystems
- It lists support for Cargo, npm, pnpm, Yarn, Bun, Go, Python, Maven, Gradle, .NET, Swift, Dart/Flutter, Elixir and Scala/sbt. · github.com, 3 Oct 2026
- Execution
- Commands can run in parallel across multiple jobs, and the CLI supports dry-run previews, timeouts, package filters and skip patterns. · github.com, 3 Oct 2026
- GitHub Actions
- The README documents a setup action and dynamic CI job matrices for affected packages. · github.com, 3 Oct 2026
- License
- The repository identifies the software as MIT licensed. · github.com, 3 Oct 2026
- Outputs
- The CLI supports JSON output, JUnit XML, shell completions and a Unicode dependency tree, with DOT graph output also available. · github.com, 3 Oct 2026
- PR comments
- A companion GitHub Action can post and update pull request comments showing affected packages and reasons. · github.com, 3 Oct 2026
- Purpose
- affected detects which monorepo packages are affected by Git changes and runs tests or other commands on those packages. · github.com, 3 Oct 2026
- Setup
- The README says it auto-detects project type and dependency graph with zero configuration to start. · github.com, 3 Oct 2026
- Support
- The README welcomes contributions and directs users to the repository's GitHub issues. · github.com, 3 Oct 2026
Where affected stands on Freedom251
- Monorepo Management Tools#2 of 33