A clean vulnerability scan does not, by itself, prove an Alpine-based container is secure. It means the scanner reported no findings within its detected packages, advisory data, settings, and scan scope. Verify those pieces—especially Alpine package recognition and advisory coverage—before treating the result as conclusive.
Why a clean Alpine scan can leave questions unanswered
Alpine Linux is built around musl libc and BusyBox, and its project emphasizes small size and security-oriented design. Those are distribution characteristics, not proof that any particular image is secure. Alpine’s About page describes it as “an independent, non-commercial, general purpose Linux distribution designed for power users who appreciate security, simplicity and resource efficiency.” Alpine Linux About


As an Amazon Associate I earn from qualifying purchases.
The practical blind spot is about visibility and interpretation, not an inherent Alpine weakness. A scanner must identify what is installed, connect those components to relevant vulnerability information, and apply its configured detection policy. For Alpine operating-system packages, that means recognizing apk-managed packages and using applicable Alpine advisory data. Docker Scout documents Alpine secdb as an advisory source, and Trivy lists Alpine secdb among its sources. Docker Scout advisory matching Trivy vulnerability detection
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallDetection settings also affect what appears. Trivy describes a precision-focused mode that may miss potential vulnerabilities and a more comprehensive approach that can increase false positives. Broader results are candidates to investigate, not automatic evidence that a component is exploitable. A scan report should be read alongside its detection mode, data sources, database freshness, and exclusions.
#1 Best Overall
What to verify in an Alpine vulnerability report
- Confirm distribution and release recognition. Check that the report identifies the image as Alpine and shows the expected release or version. If the scanner misidentifies the base image, investigate that before interpreting its OS findings.
- Check apk package inventory. Confirm that expected operating-system packages managed by apk appear in the scanner’s inventory. Missing packages can make a clean result incomplete.
- Check Alpine advisory coverage. Verify that the tool uses Alpine advisory information, such as Alpine secdb, for the relevant packages and release.
- Review detection settings and data freshness. Note whether detection is precision-focused or comprehensive, when vulnerability data was last updated, and whether exclusions or severity filters suppress findings. The report’s scope matters as much as its headline result.
- Inspect the full image contents. OS package findings are only one category. Where appropriate, scan for language-specific dependencies, misconfigurations, and secrets as separate concerns.
- Review runtime configuration. Assess capabilities, mounts, daemon exposure, isolation, and kernel-related security configuration. Remove capabilities the workload does not need.
These checks help establish what a scan covered; no single workflow guarantees that an image is secure.
What vulnerability scanning does—and does not—cover
Vulnerability scanning is not a complete security review. Trivy documents distinct checks for image vulnerabilities, misconfigurations, and secrets, so a vulnerability-only result should not be read as having checked those other categories. Trivy container image scanning
Rank #2
Runtime protections matter too. Docker’s security guidance discusses isolation, daemon exposure, capabilities, mounts, and kernel hardening as separate considerations. A package scan cannot establish that a container is configured or operated safely. Docker Engine security
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →When an SBOM helps, and what to check
A software bill of materials (SBOM) can make an image’s components easier to inventory and can itself be scanned. Its usefulness depends on what the SBOM includes and how accurately its package metadata maps to components. Trivy cautions that SBOMs generated by other tools can lead to inaccurate detection. Trivy SBOM scanning
Rank #3
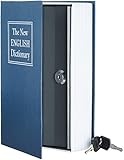
- Portable lock box that looks like a book; great for hiding small valuables on a bookshelf
- Fabric cover and spine designed to look like a book; does not contain paper pages; recommended to store in-between two books on a bookshelf
- Front cover lifts to reveal safe’s actual cover; key lock designed to deter theft; 2 keys included
- Interior space for hiding cash, credit cards, important documents, jewelry, and more
- Ideal for traveling or at home; backed by an Amazon Basics limited 1-year warranty
- Check that the SBOM represents the image you intend to assess.
- Verify that expected Alpine packages and relevant application dependencies are present.
- If the SBOM came from another tool, account for compatibility and metadata limitations when interpreting results.
How to interpret Alpine’s small-size claim
Alpine’s About page says that “a container requires no more than 8 MB.” This is an Alpine-published illustrative claim; the page does not state a version-specific measurement method. Do not treat it as a measured guarantee for every current Alpine-based application image. Alpine Linux About
Quick Recap
Rank #4

- Secure Storage Box: In addition to the realistic book appearance on the outside, these real paper transfer book safe have a thickened key lock box embedded inside to provide additional storage and secret hidden book safe box are strong enough; Hollow diversion book safe, don't hesitate to choose the style you need
- Hollow Book Safe: The book safe code lock money box is ideal for storing valuable personal items such as coins, bank cards, ID cards, secret hidden metal book box is great for home security or to carry valuables, travel in cash, keep your cash, passport, jewelry and other personal items safe and safe secret hidden metal lock box not easily found
- Book Appearance Combination Box: The safe looks like a book, just put book safe box for home on a desk or a bookshelf, or put diversion book money hiding box on a coffee table or bedside table, and book safe box for office can be fully integrated with books and other objects
- Versatile and Portable: This money hiding book box and faux book box hidden suits a variety of settings, including home, office, school, and travel; Diversion book storage box, portable design ensures easy access to your hidden items wherever you go
- Widely Use: These faux book hidden storage box, diversion book safe box for money can not only be used for bookcase decoration, coffee table book decoration, modern living room decoration, family warm home decoration, bookshelf decoration, TV rack decoration supplies; Diversion book safe box also has the function of secretly storing your small objects
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




