Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchPC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11If WordPress malware returns after cleanup, assume the site is not fully understood yet—not that one more scan will necessarily fix it. An attacker may still have access, a backup may contain the infection, or an overlooked file, database change, account, or hosting issue may be restoring it. Contain access, preserve a copy, investigate the whole environment, and validate each cleanup decision before bringing the site fully back online.
This is a general incident-response workflow, not a diagnosis of a particular installation. The right scope and remedy depend on the symptoms, available logs and backups, and how the site is hosted.
As an Amazon Associate I earn from qualifying purchases.
How can you tell whether a WordPress site may still be infected?
A visible warning is a reason to investigate, not a complete description of what changed. WordPress.org’s “FAQ – My site was hacked” identifies several practical indicators:
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Scan for outdated or missing drivers - takes under a minute3Repair Windows errors before they cause bigger problems- A browser, search service, or security provider reports a blacklist or malware warning.
- Your hosting provider suspends the site or tells you it is distributing malware.
- Visitors report redirects, suspicious pages, or antivirus alerts.
- You find unexpected administrator accounts, injected content, or file changes you cannot explain.
Record the exact warning, affected URLs, when symptoms began, and what visitors see. Save host notifications and relevant logs before they are overwritten. A clean-looking homepage does not establish that other pages, user accounts, or server files are clean.
#1 Best Overall

- 1. 【Multi-Functional USB-C Hub & Security】** Upgraded design features a built-in **USB-C pass-through charging and data port**. Unlike basic fingerprint scanners, this allows you to simultaneously use your fingerprint login while keeping your USB-C port free for charging your laptop or connecting a wireless mouse/keyboard. Perfect for modern laptops with limited ports.
- 2. 【Premium Aluminum Build & Portability】** Crafted from a **durable aluminum alloy** casing, this scanner is built to withstand the rigors of daily travel and desk life. Included **3M adhesive backing** allows you to securely mount it to your laptop lid or desk, ensuring it stays put in your bag and is always ready for instant access.
- 3. 【Instant Windows Hello Login (<1 Sec)】** Experience **password-less login in under one second**. With full support for **Windows 10/11 and Windows Hello**, this biometric reader provides seamless, secure access to your device, apps, and websites. Just a touch and you're in—no more typing complex passwords in coffee shops or airports.
- 4. 【360° Touch & Data Pass-Through】** Equipped with **360-degree capacitive touch** technology, it reads your fingerprint accurately from any angle. The upgraded USB-C port supports **data synchronization**, allowing you to connect and read a flash drive or external hard drive through the scanner without any loss in speed.
- 5. 【Universal Compatibility for On-the-Go Pros】** Designed for modern hybrid workers. Simply plug-and-play on any **Windows 10/11 laptop or PC** with a USB-C port. No complicated setup required. The compact size and detachable cable (with the adhesive mount) make it the ideal security companion for business travel and hot-desking.
WordPress’s Site Health screen can provide diagnostic information and identify critical issues, but it is not a malware certificate. A “healthy” status does not prove that a backdoor or other persistence mechanism is absent.
What should you do before deleting suspicious files?
Contain access and preserve evidence before making destructive changes. A copy of the current, possibly infected site can help you compare changes or recover information if cleanup goes wrong. Keep it separate from any known-good backup, and avoid overwriting the only copies of suspicious files or logs.
- Restrict access where practical. If you can safely take the site offline or limit public access while investigating, do so. Ask your hosting provider about account isolation, especially if the site shares an account with other websites.
- Secure administrator access. Reset passwords for WordPress administrators and other affected accounts, and remove access you cannot verify. Do not assume that resetting one password closes every route an attacker may have.
- Invalidate existing WordPress sessions. Update the secret keys and salts in
wp-config.phpusing trusted WordPress guidance. This signs users out, but does not remove malicious code or eliminate other access paths. - Make a fresh snapshot. Preserve the current files and database before cleanup, even if you suspect they are infected. Store the copy somewhere separate from the live installation.
- Protect earlier recovery points. Keep known-good backups separate. Check that a candidate backup includes both the files and database and predates the suspected compromise; a restore point can bring malware back if it was created after infection.
WordPress Developer Resources’ “Hardening WordPress – Advanced Administration Handbook,” updated January 7, 2026, recommends planning for backups and recovery. A backup is useful only if it is intact, covers what you need, and can be restored.
Rank #2

- 📱 QR CODE SETUP GUIDE: Scan the QR code on the packaging to access the setup page with Windows drivers and installation instructions. The package includes the main item and a Japanese manual. On the website, tap the 🌐 World icon to switch to English, then scroll down to download the English manual.
- 🚀 INSTANT ACCESS: Login 10x faster than typing passwords - Under 1 second!
- 🛡️ HIGH-LEVEL SECURITY: Match-On-Chip technology = Your fingerprint NEVER leaves the device
- 🎯 WORKS EVERY TIME: 99.999% accuracy with 360° recognition - Touch from any angle!
- 💻 PLUG & PLAY MAGIC: Zero software installation - Works instantly with Windows 10/11 Hello
How do you scope the infection?
Build a working list of what is known before deciding what to replace. Note affected URLs, redirects, injected content, alerts, unknown users, unusual file timestamps, and host notifications. Record when each observation was made; timestamps can help establish a timeline, but by themselves do not prove when or how a file was changed.
Ask the host what account isolation is available, how long relevant logs and backups are retained, and whether other sites or files in the hosting account may be affected. WordPress’s hacked-site guidance warns that an infection can extend beyond one WordPress site, particularly in a shared hosting environment. Without access to the account and its evidence, the scope cannot be inferred from the visible website alone.
Consider the full installation as evidence warrants: WordPress core, plugins, themes, configuration, uploads, database content, scheduled tasks, user accounts, and the hosting environment. These are investigation areas, not a claim that every infection modifies all of them.
Rank #3

- "Hot swappable Play Arrange with 1.5m Cablemail: Enjoy bother complimentary installation and flexible placement with a generous 1.5m USB cable, allowing accessible positioning for any computer arrange lacking driver demands"
- Tap Hook for Strengthened Security: Day night private data by simply poignant the transducer to instantly hook your computer
- "FIDO Licensed Multiple Function Security: Beyond Windowslogin, this reader serves as a FIDO U2F/FIDO2 security code for websites/apps like Two processor , providing immune 2FA security"
- "Sophisticated Controlled Breathing Ligheight: Board game with a smooth sensitive light club highlighting modifiable breathing consequences, reducing organ of sight strain while enhancing beauty"
- "Recognition & Immediate Loginumberebog: Knowledge extreme fast fingerprint scanning with recognition corner, facilitating secure passcode complimentary signin through Windowslogin for 10/11 PCs and laptops in under 1 second"
How do you inspect files and find a hidden backdoor?
Compare files against trusted originals rather than relying on filenames or a scan result alone. WordPress.org’s hacked-site documentation calls out files such as index.php, header.php, footer.php, and function.php as common targets, while noting that the approach depends on the symptoms. Those examples are not an exhaustive list, and legitimate site customizations can also make files differ from stock versions.
Free tools Windows power users keep installed
One-click scans. No signup required.
- Preserve suspicious material first. Copy it into your evidence snapshot before removing or changing it. It may help explain how the compromise occurred or whether related files were altered.
- Check core files against the matching official WordPress release. Use clean downloads from WordPress.org, not an unfamiliar mirror. Compare changes carefully before replacing anything, and account for legitimate modifications.
- Check plugins and themes against trusted distributions. Obtain clean copies from WordPress.org or the original trusted publisher. A file that looks familiar is not necessarily unmodified.
- Follow evidence beyond the obvious targets. Investigate unusual executable files in uploads, configuration and drop-in files, database injections, scheduled tasks, and users you cannot explain when the symptoms point to them.
- Check whether the suspected change is site-wide or account-wide. If the host confirms other sites share the account, treat them as possible scope—not as automatically infected—and investigate them before declaring the incident resolved.
Replacing a known-good core or extension file can remove an altered copy, but it does not necessarily remove database changes, unauthorized users, or a separate foothold on the hosting account. Review the evidence across these areas before concluding that the backdoor is gone.
What can a malware scanner do—and what can’t it prove?
A scanner can help identify suspicious changes and reduce manual comparison work. Wordfence’s documentation describes comparing compromised core, theme, and plugin files with originals, then allowing an operator to repair or delete modified files. That is assistance with file review, not proof that an entire site has been restored.
Rank #4

- Instant Windows Hello Integration: Quickly unlock your Windows 10/11 PC with your fingerprint. No need to type passwords—just one touch for fast and secure access. Works directly with Windows Hello, no extra software needed.
- Plug & Play Simplicity: No drivers needed for genuine Windows systems—just plug it in and it works. Automatically recognized in most cases (95%+ compatibility). Tip: Manual driver update may be required for non-genuine systems.
- USB Fingerprint Reader: A compact metal fingerprint scanner for PCs and laptops that makes logging in quick and easy—just plug it into any USB port and start using it. Its ultra-portable design fits perfectly in your laptop bag.
- Microsoft-Certified Security: Fully supports Windows Hello and the Windows Biometric Framework for safe and reliable login. Features high accuracy (0.001% false acceptance / 0.1% false rejection) to keep your data secure. Also supports password and file encryption for most websites.
- Multi-User Flexibility: Store up to 10 fingerprints—perfect for shared devices at home or work. Enjoy fast and smooth access with lightning-speed authentication in under 0.5 seconds.
Wordfence’s hacked-site guidance says its plugin is not a complete or automatic restoration solution. Treat flagged results as leads to assess, and investigate database and account state where needed. A scan that reports no findings does not certify that every persistence mechanism or affected part of the hosting environment has been found.
Likewise, a Site Health result is diagnostic information, not malware certification. Use tools as part of the investigation; do not make a tool’s status the sole basis for declaring the site clean.
Should you restore a backup, rebuild, clean in place, or get help?
There is no single best option for every compromise. Choose based on the reliability of the recovery point, how much unique material must be preserved, what evidence is available, and whether you can isolate the site while work proceeds.
Best Value
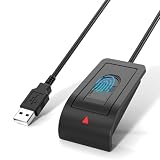
- Windows Hello Fingerprint Login: Designed for windows hello fingerprint reader compatibility on Windows 10/11 PCs, this usb fingerprint reader replaces passwords with fast one-touch biometric access. Enjoy convenient, secure login through your PC’s built-in Windows Hello system without extra software.
- Match-in-Sensor Security Protection: This fingerprint reader uses advanced biometric processing to verify fingerprints inside the sensor, helping protect your personal data. Your fingerprint information stays stored locally on your Windows device and is never uploaded or shared externally.
- Fast & Accurate Biometric Recognition: Built as a reliable fingerprint scanner for everyday computer security, this fingerprint reader for windows 11 provides quick recognition and stable performance. Access your PC, lock screens, and manage user accounts with a simple touch.
- Plug & Play Desktop Convenience: The usb fingerprint reader windows 11 solution connects easily through USB with no complicated drivers or third-party apps. The included 4ft cable provides flexible placement for desktops, workstations, and home office setups.
- Designed for Windows PC Security: This fingerprint scanner for pc supports password-free login through Windows Hello and works as a practical windows fingerprint reader for compatible systems. Compact design and angled sensor placement offer comfortable daily use.
| Approach | When it may fit | What to verify or weigh |
|---|---|---|
| Restore a backup | A candidate backup appears to predate the compromise. | Verify that it is intact and includes both files and database. A backup made after the infection may restore the backdoor. |
| Rebuild replaceable code | You can replace core, plugins, and themes with trusted originals while preserving legitimate content and configuration. | Identify and account for customizations. Replacing code alone does not address database, account, or hosting-level changes. |
| Clean in place | You can investigate the affected areas and preserve site-specific material that cannot be readily replaced. | It requires careful review of files and other evidence; piecemeal deletion can miss a separate access path or persistence mechanism. |
| Engage a qualified incident responder | The site repeatedly becomes infected, the entry point remains unknown, the scope is unclear, or business-critical systems are involved. | Consider your access to logs and server-level support, the need to preserve evidence, and whether the site can be isolated during the investigation. |
These options can overlap. For example, a site owner may preserve an infected snapshot, have a specialist assess scope, and then rebuild from a verified recovery point. The evidence—not a universal ranking—should determine the sequence.
How do you validate cleanup and reduce the chance of reinfection?
After remediation, validate the areas that were implicated and address the route that allowed access. WordPress’s “FAQ – My site was hacked” advises updating the installation and changing passwords again once the site is clean. Rotating credentials after cleanup helps avoid carrying forward credentials that may have been exposed during the incident.
- Update WordPress, plugins, and themes from trusted sources, and remove components you do not use.
- Change relevant passwords again after cleanup. If database credentials changed, ensure the current values are reflected in
wp-config.php. - Review administrator and other privileged accounts for access you cannot explain.
- Investigate host and account-level weaknesses, not only WordPress files. Ask the provider for help if logs, isolation, or shared-account scope require server access.
- Keep separate backups and test that your recovery plan works; continue monitoring file integrity and site behavior.
- Consider the owner’s workstation and other systems involved in site administration as possible parts of the incident.
If you need community support, WordPress.org’s Hacked or Malware forum is a noncommercial option. Share symptoms and relevant details without posting passwords, secret keys, or other credentials publicly.
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Reinfection is a sign to reopen the investigation: the original entry point may still exist, another access path may remain, or a restored copy may contain the same problem. If you cannot establish scope or confirm that the recovery point is safe, ask your host or a qualified incident responder for help before treating the incident as resolved.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




