Recommended Free Tools
Low-cost KVM-over-IP devices are often treated as simple convenience hardware, but they can sit at one of the most sensitive points in an environment: remote keyboard, video, and mouse access to servers. If that device is poorly designed, misconfigured, or exposed to the internet, it can give an attacker a path that bypasses many of the protections placed around operating systems and applications.
The risk is not limited to obscure bugs. Weak firmware, default passwords, outdated web interfaces, hardcoded credentials, and insecure remote access features have all turned inexpensive management hardware into entry points for compromise. Once an attacker controls a KVM, they may be able to view consoles, send keystrokes, alter boot settings, mount virtual media, or interfere with recovery workflows.
As an Amazon Associate I earn from qualifying purchases.
Organizations should know where these devices are deployed, whether their management interfaces are reachable, and whether the vendor provides meaningful security updates. Hardening remote console access—or replacing risky hardware entirely—can prevent a cheap administrative shortcut from becoming a direct route into the network.
Free tools Windows power users keep installed
One-click scans. No signup required.
Why budget KVM devices are attractive attack targets
Budget KVM-over-IP devices sit in a privileged position: they provide remote keyboard, video, and mouse access to servers, workstations, storage appliances, and sometimes network gear. To an administrator, that is convenient out-of-band access when an operating system is down or a server needs BIOS-level changes. To an attacker, it can be a direct path around many of the controls that protect normal remote administration, such as endpoint detection, host firewalls, VPN logging, and identity-aware access gateways.
#1 Best Overall
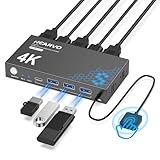
- 【KVM Switch 1 Monitors 2 Computers】This HDMI KVM Switch with two HDMI ports allows control of two computers, enabling them to share a single monitor along with keyboard and mouse. It's complete USB switch and HDMI switch rolled into one. This KVM Switch also supports various input devices such as PCs, Laptops, PS4, etc. It is compatible with various operating systems including Windows 7/8/10/11/Vista/XP, Linux, Mac, and more.
- 【Four USB 3.0 Ports (3×USB-A + 1×USB-C)】 This KVM switch features 4 USB 3.0 ports with ultra-fast data transfer speeds up to 5Gbps, including 3 USB-A ports and 1 USB-C port for broader device compatibility. It allows you to seamlessly share peripherals between two computers, reducing cable clutter and improving workspace efficiency. Perfect for connecting and sharing USB devices such as keyboards, mice, scanners, printers, flash drives, headsets, and webcams. The switch automatically detects and recognizes connected devices for stable and reliable performance.
- 【4K Resolution & HDCP 2.2】HDMI KVM Switch supports stunning 4K resolution at 60Hz, ensuring crystal-clear and highly detailed visuals for your monitors. Additionally, it is HDCP 2.2 compliant, allowing you to seamlessly view HDCP-protected content on your monitors without any interruptions. It also supports 4K@30Hz, 2K, 3D, and 1080P, offering flexibility for various display needs. This guarantees both exceptional image quality and a smooth, secure multimedia experience.
- 【Two Ways of Switching】4K HDMI KVM Switch features two switching options: On-KVM Switch Button and Wired Remote Switch. The Wired Remote Switch allows you to place the HDMI KVM switch in hidden or distant location, keeping your desk tidy. Simply place the remote control within easy reach on your desk for quick access. With a press, you can switch between computers seamlessly, enhancing productivity and reducing clutter on your monitors.
- 【Adaptive EDID & Plug and Play】This USB 3.0 HDMI KVM Switch features Adaptive EDID, ensuring stable and smooth image transmission by automatically optimizing display settings on your monitors. Easy to install, this HDMI KVM switch requires no power supply or driver software—just plug it in and connect all cables for seamless operation between two computers and one monitor.
Low-cost models are especially attractive because they are often bought to solve an immediate operational problem rather than as part of a managed remote access architecture. A small office, lab, branch site, industrial cabinet, or MSP-managed customer rack may add a cheap KVM so staff can reboot systems or watch a console without traveling. The device then stays in place for years, frequently with minimal patching, weak documentation, and little visibility in asset inventories. If its web interface is exposed to the internet, reachable through a broad VPN, or accessible from a flat internal network, it becomes a durable target.
Attackers value what a KVM can do after login
A compromised KVM is not just another web appliance. It may let an intruder view the live console, send keystrokes, mount virtual media, change boot order, interact with recovery shells, or access pre-boot configuration screens. Those capabilities can enable password theft from login prompts, offline tampering with disks, installation of a malicious operating system image, or disabling security settings before the host fully starts. In some environments, console access can be equivalent to standing in front of the machine with a keyboard and USB stick.
- High privilege by design: KVMs often connect to critical hosts such as domain controllers, hypervisors, backup servers, firewalls, and jump boxes.
- Weak management history: Cheaper devices may receive infrequent firmware updates, lack signed update enforcement, or ship with outdated web components.
- Reusable access patterns: Default usernames, shared admin passwords, and common port-forwarding habits make scanning and credential attacks easier.
- Poor monitoring: Many devices have limited logs, no central audit integration, and no alerting when someone opens a remote console session.
Another reason these devices draw attention is that they often expose a small set of predictable services: a browser-based admin panel, legacy Java or ActiveX console components, VNC-like viewers, SSH or Telnet, and vendor-specific remote media features. Attackers can scan for banners, TLS certificates, favicons, login page titles, and open ports to identify models at scale. Once a model is known, they can test for default credentials, known firmware flaws, authentication bypasses, command injection bugs, weak session cookies, or file upload issues in the management interface.
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Budget KVMs also tend to outlive the assumptions made when they were installed. A device that was originally reachable only from a technician’s workstation may later become exposed through a firewall rule, a cloud VPN, a remote management VLAN, or a temporary port forward that never gets removed. Even if the KVM is not directly internet-facing, compromise of a single user laptop or low-privilege internal account can put the attacker close enough to reach it. From there, console control of a more sensitive system can become the next step in the intrusion.
The core risk is the combination of remote reachability, hardware-level control, and weak operational hygiene. A low-cost KVM may look like a simple utility box, but on the network it behaves like a management server with physical-console authority. That makes it worth cataloging, restricting, monitoring, and replacing when it cannot meet the same security expectations applied to other administrative access tools.
Common weaknesses in cheap KVM-over-IP hardware
Low-cost KVM-over-IP appliances often combine keyboard, video, mouse, virtual media, and remote power-control features into a small embedded device, but the security engineering behind them may lag far behind the sensitivity of what they can access. A KVM is not just another peripheral: it can view boot screens, enter BIOS settings, mount ISO images, unlock encrypted disks during startup, and interact with servers before endpoint security tools are running. When the firmware is weak, the device becomes a privileged remote console with the security posture of an outdated router.
One of the most common problems is stale or poorly maintained firmware. Budget vendors may ship devices with old Linux kernels, outdated web servers, vulnerable Java or ActiveX console components, and third-party libraries that never receive timely patches. Some products are rebranded across mulle suppliers, making it hard to identify the true manufacturer or find reliable updates. Even when firmware downloads exist, they may be unsigned, distributed over insecure channels, or accompanied by vague changelogs that do not clearly state which vulnerabilities were fixed.
Management interfaces are another weak point. Many inexpensive KVMs expose HTTP, HTTPS, VNC, Telnet, SSH, proprietary console ports, or API endpoints with minimal hardening. TLS may use expired certificates, weak ciphers, or self-signed defaults that administrators learn to ignore. Web interfaces can suffer from basic flaws such as weak session cookies, missing CSRF protections, command injection, directory traversal, authentication bypass, or file upload bugs in virtual media features. Because these devices are designed for emergency access, administrators may place them on reachable networks and leave services enabled long after installation.
Rank #2

- KVM Switch 3 Monitors 2 Computers: This 2*Displayport + 1*HDMI KVM Switches allows you to switch effortlessly between two computers with one click — share 3 monitors and 4 USB 3.0 ports (keyboard, mouse, printer, webcam) without swapping cables. Space-saving KVM for home offices, content creators, and IT professionals. NOTE: Both computers must support triple-monitor output to use all 3 displays simultaneously. If either PC only supports 1 or 2 displays, the extra monitor(s) won’t activate
- Ultra HD 8K@60Hz/4K@240Hz Resolution: This USB KVM switch output features two DisplayPort 1.4 ports + one HDMI 2.1 port, each supporting up to 8K@60Hz resolution, and backward compatible with 8K@30Hz, 4K@240Hz/144Hz/120Hz/60Hz/30Hz. It also supports HDR10+, HDCP 2.3/1.4, VRR, FreeSync, and G-Sync, eliminating screen tearing and stuttering across three monitors, even at high frame rates. NOTE: If need to achieve 8K resolution, your computers and monitors both need to support 8K@60Hz resolution, and please make sure the length of your cables are within 2 meters 28AWG
- Two Switching Ways & Two Dispaly Modes: This KVM switch displayport HDMI supports button switching and desktop controller switching, freely switch between 2 computers. With the desktop controller, you can place this monitor switch for 2 computers outside your work area, making your desktop cleaner and tidier. Two Dispaly Modes, Mirror mode: Triple monitors output the same images, Extend mode: Triple monitors output different images. NOTE: Not support Keyboard shortcuts (hotkeys) toggles
- Wide Compatibility & Package List: This triple monitor KVM switch driver-free and plug and play, and supports Windows, and Linux systems. PACKAGE LIST: 1*KVM switch, 4*DP cables, 2*HDMI cables, 2*USB A cables, 1*power adapters, 1*desktop controller, 1*user guide
- NOTE: 1, To ensure normal usage, please make sure to connect the power supply via the power adapter. 2, To display content across three screens simultaneously, make sure each of your PC is equipped with 2 DisplayPort ports + 1 HDMI port. 3, Each computer at the input needs to be connected with 2* DP cables + 1* HDMI cable+1* USB cable. 4, Please make sure your PC supports 3 screens or above display function before purchasing. 5, If a signal converter or docking station is used, there may be compatibility issues. 6, NOT support EDID emulation
- Default or hard-coded credentials: Some devices ship with admin accounts that are never changed, hidden support users, or password reset mechanisms that can be triggered locally or remotely.
- Weak authentication: Short password limits, no account lockout, no multi-factor authentication, and poor logging make brute force and credential stuffing easier.
- Insecure remote console components: Legacy Java applets, browser plugins, unsigned viewers, and proprietary clients can introduce additional vulnerabilities on administrator workstations.
- Over-permissive virtual media: ISO mounting and file-transfer functions can be abused to boot rescue environments, implant tools, or bypass normal operating system controls.
- Poor network isolation: A KVM connected to both a management network and production-adjacent systems can become a bridge into more sensitive areas.
Credential handling is especially risky. Some devices store passwords in recoverable formats, expose configuration backups without adequate protection, or transmit credentials to companion software in ways that can be intercepted on the local network. If LDAP, RADIUS, or Active Directory integration is supported, implementation flaws can create a false sense of central control while local fallback accounts remain active. Shared administrator passwords across several KVMs make compromise even more damaging, since one exposed unit can lead to access across an entire rack or site.
Remote access convenience features can also expand the attack surface. Cloud relay portals, vendor mobile apps, dynamic DNS options, email alerting, and outbound callback services may punch through firewall boundaries that would otherwise protect the management interface. If the vendor backend is weak, abandoned, or opaque, administrators may not know who can broker sessions to the device or how access is audited. On very cheap hardware, “remote access” sometimes means enabling a plain web server or VNC-like service with little more than a password between the internet and a live server console.
The result is a device class where small weaknesses combine into serious exposure: an old firmware image, a default account, a browser-based console, and an internet-reachable management page can be enough for an attacker to gain hands-on control of critical machines. Treat every low-cost KVM-over-IP appliance as a privileged embedded system, not as a passive cable replacement, and evaluate its firmware lifecycle, authentication model, enabled services, and network placement before trusting it with administrative access.
How exposed KVMs can lead to full network compromise
A KVM-over-IP device is not just another management appliance. It often has direct keyboard, video, and mouse control over servers, storage systems, firewalls, hypervisors, and recovery consoles. If an attacker reaches the KVM’s web interface, VNC-like console service, serial console, or vendor remote access portal, they may be able to operate connected machines as if they were standing in the server room. That turns a small, low-cost box into a bridge between the internet and the most privileged layer of the environment.
The most direct abuse path is credential-based access. Many exposed KVMs still use factory usernames and passwords, reused administrator credentials, or weak local accounts that are not protected by multifactor authentication. Once signed in, an attacker can view live consoles, reboot systems, change boot options, enter BIOS or UEFI setup, mount virtual media, or interrupt startup sequences. On a domain controller, backup server, virtualization host, or network appliance, those actions can quickly become more damaging than access to an ordinary user workstation.
Common attacker paths after KVM access
- Console takeover: The attacker controls the attached host directly, including login prompts, recovery screens, and pre-boot environments.
- Credential capture: They can watch administrators type passwords during maintenance, recovery, or failed login attempts.
- Virtual media abuse: If the KVM supports remote ISO or USB mounting, the attacker may boot a rescue image, implant tools, copy data, or reset local credentials.
- Firmware and boot manipulation: Access to BIOS, UEFI, RAID controllers, or boot menus can allow persistence below the operating system.
- Pivoting through management networks: A compromised KVM may have access to IPMI, iDRAC, iLO, switches, storage arrays, or other out-of-band systems that are not reachable from normal user subnets.
Even when the KVM is connected to only one server, the impact can spread. A host running virtual machines may expose dozens of workloads through a single console. A backup server can provide access to offline copies of sensitive systems and credentials stored in scripts or backup jobs. A firewall or router console can let an intruder alter access rules, create VPN accounts, mirror traffic, or disable logging. In ransomware incidents, attackers often target this kind of management access because it helps them shut down defenses and recover control after administrators try to contain the breach.
Weak firmware makes the situation worse. Some low-cost KVMs run outdated web stacks, hard-coded service accounts, unsigned firmware updates, or remote access daemons that are difficult to audit. If a flaw allows command execution on the appliance itself, the attacker may not even need valid KVM credentials. From there, they can scan internal networks, capture traffic on the management VLAN, attack nearby administrative interfaces, or maintain a foothold that survives server reinstallation because the compromised device sits outside the monitored operating system.
Rank #3

- 【USB 3.0 KVM Switch with 2 Switching Methods】This KVM Switch 2 Port HDMI can control 2 PCs to share 1 monitor with 1 set of USB 3.0 keyboard and mouse. You can quickly switch between 2 computers, and the KVM switch supports 2 switching methods: wired remote and button switching. Please Note: This product does not support hotkey switching.
- 【KVM Switch HDMI with 3 USB 3.0 Ports】This HDMI KVM Switch comes with 3 USB 3.0 ports for sharing USB devices, such as keybaord, mouse, scanners, printers, U disks and more other USB devices, automatically recognize and match various display devices. This KVM Switches also supports a variety of input devices, such as PC, Laptop, PS4, etc. Compatible with a variety of computer systems like Windows 7/8/10/Vista/xp, Linux, Mac, and so on.
- 【Support Ultra HD 4K Resolution】This KVM Switch 1 monitor 2 computer can support the resolution up to 3840*2160@60Hz, and can also be backward compatible with 3840*2160@30Hz, 1920*1080P@60Hz etc., which will bring you ultra-high-definition visual senses. The 4K KVM Switch can support a maximum refresh rate of 60Hz, please pay attention to the setting of this parameter when you use it.
- 【Adaptive EDID & Plug and Play】This USB 3.0 HDMI KVM Switch can adaptive to EDID, which makes image transmission more stable and more smoothly. Support HDMI 2.0, HDCP2.2 standards. This KVM Switch 2 computers 1 monitor can be easily to install, just plug it in, no power and driver software required. When using this product, please connect all the cables.
- 【After-sales Service】This KVM Switch 2 Port is equipped with USB 3.0 cables(1.2m)*2 , 3.5mm remote control cable (1m)*1, wired remote*1. You need to prepare the 3 HDMI cables required to connect 2 computers and 1 monitor. Our products provide lifetime warranty service. If you have any questions or concerns about our products, please contact us directly through the order number. We will provide you with a solution.
Exposure is especially dangerous when management interfaces are published directly to the internet for convenience. Search engines that index internet-connected services regularly reveal KVM login pages, Java or HTML5 console endpoints, SSL certificates with vendor names, and banners from embedded web servers. Attackers can combine that visibility with default credential lists, leaked manuals, old vulnerability advisories, and automated password spraying. A device installed years ago for emergency access can become an unguarded remote entry point into the entire organization.
The risk is not limited to large enterprises. Small offices, labs, hosting providers, schools, and industrial sites often use budget KVMs because they are cheaper than enterprise out-of-band platforms. The danger comes from the privilege level, not the price of the target. If the KVM can power-cycle a system, mount media, or view administrative consoles, compromise of that device should be treated as potential compromise of every connected machine and any management network it can reach.
Warning signs your KVM is reachable or vulnerable
A KVM-over-IP appliance should normally be reachable only from a tightly controlled administration network, VPN, or bastion host. If you can open its web interface from a home connection, mobile hotspot, or public cloud VM without first authenticating to a private access layer, treat that as a serious exposure. Many low-cost units present web, VNC, SSH, Telnet, Java KVM, or proprietary remote console services directly on the network, and any one of those can become the initial entry point for an attacker.
Start by checking where the device is visible. Review firewall and router rules for port forwards to the KVM, especially common management ports such as 80, 443, 5900, 5901, 22, 23, 623, 7578, 7582, and vendor-specific high ports. Look for NAT rules labeled “remote console,” “server admin,” “KVM,” “IPKVM,” or older names left by previous administrators. If the device has a public IP address, appears in internet-wide search results, or responds from outside your organization, it is reachable enough to be targeted by automated scanning.
Exposure indicators to check
- Public login page: The KVM’s web interface loads from the internet or from networks that do not need console access.
- Default or weak credentials: Accounts such as admin/admin, admin/password, superuser, root, or vendor defaults still work, or there are shared passwords used by multiple technicians.
- Old firmware: The firmware version is several years behind, the vendor no longer publishes updates, or release notes mention authentication, command injection, or remote code execution fixes you have not applied.
- Legacy services enabled: Telnet, unencrypted HTTP, old Java applets, insecure VNC, or anonymous discovery services are active.
- Weak TLS: The HTTPS interface uses an expired certificate, self-signed certificate with no internal trust process, obsolete ciphers, or allows downgrade to plain HTTP.
- No access logging: The appliance provides little or no record of login attempts, source IPs, session starts, virtual media use, or configuration changes.
Authentication behavior is another strong signal. A vulnerable or poorly configured KVM may not enforce account lockout, may allow unlimited password attempts, or may expose mulle independent login surfaces that do not share the same security policy. For example, the web UI may have a strong password while a VNC, serial-over-LAN, or vendor client service still accepts a factory credential. If multi-factor authentication is absent and the device is reachable beyond a restricted management segment, a stolen or guessed password may be enough to give an attacker hands-on console access.
Inspect the device configuration for remote access features that increase impact. Virtual media mounting, remote ISO boot, power control, keyboard injection, clipboard sharing, and BIOS-level console access are powerful administrative tools, but they also let an intruder bypass operating system controls. If those features are enabled for all accounts, exposed to the internet, or not logged, the KVM is not just a viewing tool; it is a path to reinstall systems, alter boot settings, capture credentials, or implant malware before endpoint protections load.
Operational warning signs
- Unexpected reboots, power cycles, or console sessions outside maintenance windows.
- Failed login bursts from unfamiliar countries, hosting providers, or residential ISPs.
- New user accounts, changed DNS settings, altered gateway settings, or modified firewall rules on the KVM.
- Unknown firmware images, configuration backups, or virtual media entries in recent history.
- Management traffic crossing production VLANs instead of staying inside a dedicated admin network.
For a quick assessment, inventory every KVM by IP address, model, firmware version, open ports, network segment, and owner. Compare that list against vendor advisories and your firewall rules. Then test reachability from an external network and from ordinary internal user subnets. If a non-admin workstation can reach the login page, or if the KVM cannot be patched to a currently supported firmware release, it should be treated as vulnerable until isolated, hardened, or replaced.
Steps to secure remote console access
Securing a KVM-over-IP device starts with treating it like a privileged administrative system, not a convenience accessory. A remote console can view boot screens, change BIOS settings, mount virtual media, and control servers even when the operating system is down. That level of access should never be placed directly on the public internet or mixed casually with ordinary office traffic.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Scan for outdated or missing drivers - takes under a minute3Repair Windows errors before they cause bigger problemsRank #4

- Share Multiple USB Devices between 2 Computer : The BENFEI 2 in 4 out USB 3.0 kvm switch supports 2 computers share 4 USB devices like keyboards, mouses, U disk, printers, scanners, USB cameras, headphones, etc. It's convenient for you to switch freely between your work computer and personal computer, driver free and compatible with multiple OS, such as windows 7/10/8/8.1/7/Vista/XP and Mac OS, Linux, and Chrome OS.
- Transfer Files in Seconds: With the 4x USB 3.0 ports, BENFEI USB Switcher supports up to 5Gbps data transfer speed. You can easily transfer data from U disk, mobile hard disk to computer. It's backward compatible with USB 2.0, too.
- Switch Easily: With the USB switcher button and LED indicator design, you can freely switch multiple USB devices between two computers with one click and clearly know the working status. Please note: When connected, it could work only when using the BENFEI USB A to USB A cable.
- Multiple USB Devices Support: BENFEI USB Switch provides an extra USB C(5V 3A) power supply slot. If you use some high power consumption devices such as HDD, USB cameras, headphones, etc, please connect extra power for stable performance. (The USB A-USB Charging cable is included, but the power adapter is not)
- 18 MONTH WARRANTY : Exclusive BENFEI Unconditional 18-month Warranty ensures long-time satisfaction of your purchase; Friendly and easy-to-reach customer service to solve your problems timely
The first move is to remove direct exposure. Place the KVM on a dedicated management VLAN or physically separate management network, reachable only through a hardened VPN, bastion host, or privileged access workstation. Block inbound access from the internet at the firewall, and restrict allowed source addresses to specific admin subnets. If the device supports mulle services, disable anything not required, including legacy web interfaces, Telnet, unencrypted VNC, old Java viewers, UPnP, and cloud relay features that bypass your perimeter controls.
- Change all default credentials: Replace vendor default usernames and passwords with unique, high-entropy credentials. Remove unused accounts and shared admin logins.
- Enforce strong authentication: Enable multi-factor authentication if supported. If the KVM cannot enforce MFA, put it behind a VPN or identity-aware proxy that can.
- Patch firmware promptly: Check the vendor support site for current firmware, security advisories, and release history. Apply updates from trusted sources only, and verify that the device is still supported.
- Use encrypted management only: Require HTTPS or SSH with modern ciphers. Disable HTTP redirects that still leave cleartext login pages available.
- Limit virtual media access: Disable remote ISO mounting unless it is needed for a maintenance window. This feature can be abused to introduce malicious installers or tools.
Logging and monitoring matter because many compromises begin with quiet probing. Send KVM logs to a central logging system if the device supports syslog. Watch for failed logins, successful logins outside maintenance windows, configuration changes, firmware uploads, and unexpected remote media sessions. On the network side, alert on management traffic from unusual locations and scan internally for exposed KVM ports such as web management, VNC, SSH, Telnet, and vendor-specific console services.
Access should also be temporary where possible. Use named accounts rather than shared credentials, grant access only to administrators who need hardware console control, and review those permissions regularly. For vendors or contractors, create time-limited VPN access and record the maintenance window. After emergency work, rotate credentials if they were shared, confirm that remote media is disconnected, and verify that no new local accounts or port-forwarding rules were added.
If the device is old, unsupported, or missing basic controls, compensate aggressively until it can be replaced. Put it behind a jump host, firewall it to a tiny allowlist, power it off when not needed, or connect it only during scheduled maintenance. Document the model, firmware version, network location, exposed services, and business owner so the device does not become forgotten infrastructure with administrator-level reach into the environment.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
When to replace a risky KVM device
Hardening can reduce exposure, but some KVM-over-IP appliances are not worth keeping in service. A device that provides keyboard, video, mouse, virtual media, and power control has a privileged path into your servers. If its firmware is abandoned, its authentication model is weak, or its remote access stack cannot be safely restricted, replacement should be treated as a security control rather than a convenience upgrade.
Start by checking the vendor’s support status and update history. If the latest firmware is several years old, security advisories are missing, or the vendor cannot provide a clear fix for known vulnerabilities, the device should be considered end-of-life for production use. The same applies to appliances that require obsolete browser plug-ins, Java applets, ActiveX controls, unsigned clients, deprecated TLS versions, or hardcoded service accounts. These are not minor annoyances; they usually indicate that the management plane was designed for a threat model that no longer exists.
Replace the device if any of these conditions apply
- No supported firmware path: the vendor no longer ships updates, or updates do not address authentication, encryption, and remote code execution flaws.
- Insecure access cannot be disabled: Telnet, HTTP, weak SSL/TLS, UPnP, cloud relay, or legacy viewer services remain active after configuration changes.
- Credentials are structurally weak: default accounts cannot be removed, password length is limited, MFA is unavailable, or role-based access is missing.
- Exposure cannot be contained: the KVM must be reachable from broad internal networks, contractor VPNs, or the public internet to remain useful.
- Poor auditability: the device does not log successful and failed logins, virtual media mounts, configuration changes, firmware updates, and remote console sessions.
- Untrusted supply chain: firmware provenance is unclear, downloads are unsigned, the manufacturer is unknown, or the device was bought through a marketplace with uncertain sourcing.
A modern replacement should support current TLS, signed firmware, secure boot or firmware integrity checks where available, per-user accounts, MFA through SSO/RADIUS/TACACS+ where appropriate, detailed logging to a central syslog or SIEM platform, and the ability to disable every unused service. It should also fit your network design: management access should live on a dedicated management VLAN or out-of-band network, reachable only through a VPN, bastion host, or privileged access management workflow.
Best Value
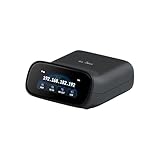
- 【Dual-Band Wi-Fi 6 Desktop KVM Device】Comet Pro supports both 2.4 GHz and 5 GHz Wi-Fi bands for a cleaner setup with less cabling. By providing both wired and wireless connectivity, it eliminates single points of failure and redefines flexibility for remote access.
- 【4K Video Passthrough & Two-Way Audio】The GL-RM10 features 4K@30FPS video passthrough and two-way audio, delivering ultra-clear, low-latency streams via H.264 encoding without interrupting the local display. Its audio support ensures crystal-clear voice interaction —ideal for remote meetings and IT support to create a natural "face-to-face" experience.
- 【Touchscreen Interface】The 2.22-inch built-in touchscreen features an intuitive user interface that is easy to operate and requires no technical expertise, allowing you to effortlessly view and manage important functions—such as connecting to Wi-Fi networks and enabling or disabling cloud services.
- 【Built-in Tailscale】 Enables secure, efficient data transfer between devices using WireGuard's encrypted transmission and direct connection features. Ideal for home labs, offices, and multiple networking scenarios.
- 【Flexible Remote Access】Remote access can be achieved through our web based cloud control functionality, supporting Windows, macOS, and Linux systems without needing to install any software. Additionally, there is remote support via the GLKVM app available to Windows, macOS, iOS and Android devices.
Before buying, test the candidate device like any other infrastructure component. Review its security advisories, confirm update frequency, inspect the admin interface for service controls, verify that factory accounts can be removed, and validate logging during real console sessions. If possible, place one unit in a lab and scan it from the same network positions an attacker might reach. A slightly more expensive enterprise-grade KVM is often cheaper than incident response, server rebuilds, credential rotation, and the loss of confidence that follows a compromise through a forgotten management appliance.
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →Frequently Asked Questions
How can I tell if my KVM-over-IP device is exposed to the internet?
Check your firewall and router for port forwarding rules that point to the KVM, especially for web, SSH, Telnet, VNC, or proprietary remote console ports. You can also search your public IP with exposure-scanning services or run an external port scan from a trusted network. If the KVM login page appears from outside your VPN, it should be treated as exposed and fixed immediately.
Are cheap KVM-over-IP devices dangerous even if I changed the default password?
Yes. Changing default credentials is necessary, but it does not fix outdated firmware, hardcoded accounts, weak session handling, insecure encryption, or vulnerable remote console components. Many budget devices also stop receiving security updates quickly, leaving known flaws permanently exploitable. A strong password helps, but it should not be the only control protecting the device.
What can an attacker actually do if they compromise a KVM device?
A compromised KVM can give an attacker remote keyboard, video, and mouse access to connected servers, often before the operating system even loads. They may change BIOS settings, boot from malicious media, capture credentials typed into consoles, or install backdoors on critical systems. If the KVM is connected to a management network, it can also become a foothold for scanning and attacking other infrastructure.
What is the safest way to access a KVM remotely?
Do not expose the KVM directly to the public internet. Put it on a dedicated management VLAN, restrict access with firewall rules, and require a VPN or zero-trust access gateway with multi-factor authentication. Disable unused services such as Telnet or legacy Java consoles, keep firmware updated, and log access so unusual connections are easier to investigate.
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchWhen should I replace a low-cost KVM instead of trying to secure it?
Replace it if the vendor no longer provides firmware updates, if you cannot disable insecure services, or if the device relies on obsolete plugins, weak TLS, or hardcoded accounts. You should also replace it if it cannot integrate with your access controls, logging, or network segmentation requirements. For systems with administrative or production access, unsupported KVM hardware is usually not worth the risk.
Bottom Line
Low-cost KVM-over-IP devices can be far more than a convenience risk: if their firmware, credentials, or management interfaces are weak, they can become a direct path into servers and internal networks. Treat them like privileged infrastructure, not simple accessories.
Your next step is to inventory every KVM device, remove public exposure, change defaults, update firmware, enforce VPN or zero-trust access, and replace unsupported hardware. If a device cannot be patched, monitored, or securely isolated, it should not remain connected to critical systems.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




