Free tools Windows power users keep installed
One-click scans. No signup required.
Subdomain delegation lets you keep a parent domain with one DNS provider while sending authority for a specific subdomain to another provider. For example, example.com can remain hosted at your current DNS service, while app.example.com is managed in a separate DNS zone with its own nameservers, records, policies, and automation.
This setup is common when different teams, platforms, or environments need independent DNS control without moving the entire domain. It can support SaaS integrations, staging environments, regional infrastructure, cloud migrations, or vendor-managed services while preserving the existing parent-domain configuration.
As an Amazon Associate I earn from qualifying purchases.
A successful delegation depends on two matching pieces: a correctly created subdomain zone at the new DNS provider and accurate NS records in the parent domain zone pointing to that provider’s authoritative nameservers. Once both sides are configured, DNS resolution follows the delegation chain from the parent zone to the delegated subdomain zone.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
How Subdomain Delegation Works
Subdomain delegation lets one part of a DNS namespace be managed by a different DNS service than the parent domain. For example, example.com might remain hosted at Provider A, while app.example.com is hosted at Provider B. The parent zone does not need to contain every record for the subdomain. Instead, it publishes nameserver records that point resolvers to the DNS servers responsible for that subdomain.
#1 Best Overall

- rv toilet brush: Engineered specifically for RVs, this brush features a silicone head that gently cleans without damaging the toilet bowl or seals, a must for traditional toilet brushes.
- Compact Wall-Mounted Toilet Brush: With its space-saving design, this brush is easy to stow away discreetly, perfect for the limited space in RVs.
- silicone toilet brush: This brush is designed for thorough cleaning of the toilet bowl without causing any harm to the porcelain or seals. The drip-free toilet brush holder is crafted to collect water from the brush, preventing any mess on your RV's floor.
- Wall-Mounted Toilet Brush for RV Travel: The brush head is conveniently attachable to the bathroom wall, ensuring that there's no rolling around during your trips. With this setup, you can travel with peace of mind, knowing your toilet brush is securely in place.
The delegation boundary is created with NS records in the parent zone. If app.example.com is delegated, the example.com zone contains NS records at the name app, such as:
| Host in parent zone | Record type | Value |
|---|---|---|
| app | NS | ns1.provider-b.example |
| app | NS | ns2.provider-b.example |
After this delegation is in place, recursive resolvers follow the DNS chain. They query the parent domain’s authoritative nameservers, receive a referral for app.example.com, then query Provider B’s authoritative nameservers for records under that subdomain. Records such as www.app.example.com, api.app.example.com, _acme-challenge.app.example.com, or MX records for app.example.com are then answered by Provider B, not by the parent domain’s DNS provider.
Parent zone versus delegated zone
The parent zone and the delegated zone have separate responsibilities. The parent zone keeps control of example.com and any non-delegated names below it. The delegated zone becomes authoritative only for the delegated subtree, starting at app.example.com. In practice, this means the parent zone should contain the NS records for app.example.com, while Provider B should contain the actual DNS zone named app.example.com with its own records.
Recommended Free Tools
- Parent provider: hosts
example.comand publishes the delegation NS records forapp.example.com. - Subdomain provider: hosts an authoritative zone named
app.example.com. - Recursive resolver: follows the referral from the parent zone to the delegated zone.
- End users and applications: receive answers from the provider authoritative for the specific name being queried.
A delegation is not the same as creating a CNAME or A record. A CNAME redirects one hostname to another name, and an A record maps a hostname to an IPv4 address. Delegation transfers DNS authority for an entire branch of the namespace. Once app.example.com is delegated, the parent zone generally should not also define ordinary records for names inside that subdomain, because those records will not be authoritative in the delegated zone.
Delegation also depends on the subdomain provider having a matching zone already configured. If the parent publishes NS records pointing to Provider B, but Provider B has no app.example.com zone, queries can fail with empty or inconsistent responses. The two sides must align: the NS records in the parent zone should match the nameservers assigned to the subdomain zone at the new provider, and the delegated zone should contain the records that clients need to resolve.
When to Delegate a Subdomain to Another DNS Provider
Delegating a subdomain to another DNS provider is useful when a specific part of a domain needs to be managed independently from the parent zone. The parent domain, such as example.com, can remain hosted with the current DNS provider, while a subdomain such as app.example.com, dev.example.com, or customer.example.com is served by a separate authoritative DNS service. This approach avoids moving the entire domain and limits the scope of changes to the delegated namespace.
A common use case is separating infrastructure ownership between teams. For example, a central IT or platform team may control example.com, while an application team manages api.example.com in a DNS provider integrated with its deployment pipeline. The application team can create and update A, AAAA, CNAME, TXT, MX, or service-discovery records inside its delegated zone without needing edit access to the parent domain. This reduces bottlenecks and keeps permissions aligned with operational responsibility.
Typical scenarios for delegation
- Cloud platform integration: Some platforms, CDNs, hosting services, and Kubernetes ingress controllers work best when they can manage DNS records directly through their own provider or automation.
- Environment separation: Subdomains such as staging.example.com, test.example.com, and dev.example.com can be delegated to teams that frequently create and delete records.
- Customer or tenant isolation: SaaS providers may delegate customer.example.com or regional subdomains to separate DNS accounts for operational or compliance boundaries.
- Acquisitions and organizational boundaries: A subsidiary or acquired business can manage brand.example.com independently while the parent company retains control of the root domain.
- Different DNS feature requirements: The parent DNS provider may not support features needed for a workload, such as API-driven record management, advanced traffic steering, health checks, DNSSEC options, or low-latency global authoritative DNS.
- Security and access control: Delegation allows limited DNS administration for a subdomain without granting broad access to sensitive parent-domain records like apex A records, MX records, SPF, DKIM, or domain verification TXT records.
Delegation is also helpful when DNS changes need to follow a different release cadence. Parent-domain records are often stable and tightly controlled, while application subdomains may change as services scale, migrate, or move between regions. By delegating only the subdomain, teams can make routine changes without affecting email routing, website apex records, domain ownership validations, or other high-impact records in the parent zone.
Rank #2
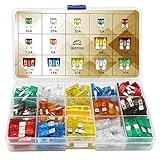
- Easy Identification: Made of a high quality zinc alloy, with a transparent cover and color coded
- 14 Most Common Fuses: Standard and Mini. (5A/ 7.5A/ 10A/ 15A/ 20A/ 25A/ 30A)
- Wide Applications: Fits most vehicles like car, truck, marine, SUV, travel trailer and other vehicles
- Note: Please use the right amp fuse to protect the vehicle and electronic equipment from short-circuit/overload
- ll Sizes You Need: The package contains 140pcs fuse and 2pcs fuse puller - 70pcs standard fuse and 70pcs mini fuse. (10pcs of each AMP)
It is not always the right choice for every subdomain. If the subdomain only needs one or two static records, adding those records directly in the parent zone is usually simpler. Delegation adds another authoritative DNS zone to monitor, renew, secure, and document. It is most valuable when the delegated subdomain has mulle records, frequent changes, separate administrators, automation requirements, or a need for DNS features that the parent provider does not offer.
Creating the Subdomain Zone at the New DNS Provider
Before adding delegation records in the parent domain, create the subdomain as its own DNS zone at the provider that will host it. For example, if the parent domain is example.com and the delegated name is app.example.com, the new provider should have a zone named exactly app.example.com, not example.com. This zone becomes authoritative for records beneath that subdomain, such as www.app.example.com, api.app.example.com, and _acme-challenge.app.example.com.
During zone creation, most DNS providers generate a set of authoritative nameservers. These are the hostnames you will later publish as NS records in the parent zone. A provider may assign two, four, or more nameservers, often with names such as ns1.provider.net and ns2.provider.net. Copy the full nameserver hostnames exactly as shown, including trailing dots if your DNS control panel requires them. Do not create glue records unless the delegated nameservers are inside the delegated domain itself, such as ns1.app.example.com.
Records to add inside the new subdomain zone
After the zone exists, populate it with the DNS records that the subdomain needs. The new provider does not automatically inherit records from the parent zone. If app.example.com should resolve to a web server, add an A or AAAA record at the zone apex. If mail will be handled under the subdomain, add the relevant MX, SPF, DKIM, and DMARC records. If certificates will be issued for names under the subdomain, add any required CNAME or TXT validation records.
- Apex record: Use @ or the full name app.example.com, depending on the provider interface.
- Host records: A record named api inside the zone usually means api.app.example.com.
- TXT records: Preserve quotation marks, spaces, and underscores exactly as required by the service using them.
- CNAME records: Avoid placing a CNAME at the zone apex if the provider does not support CNAME flattening or ALIAS-style records.
Confirm that the new zone contains an SOA record and the provider-assigned NS records at the zone apex. These are normally created automatically. The SOA record identifies the zone’s authority metadata, while the apex NS records describe which nameservers serve the zone. These apex NS records alone do not complete delegation; matching NS records still need to be added in the parent domain’s DNS zone.
| Item | Example for app.example.com | Purpose |
|---|---|---|
| Zone name | app.example.com | Defines the delegated DNS boundary |
| Provider NS | ns1.provider.net, ns2.provider.net | Nameservers to publish in the parent zone |
| Apex A record | app.example.com → 203.0.113.10 | Routes the subdomain itself to a service |
| Child host record | api → 203.0.113.20 | Creates api.app.example.com |
If you are migrating existing records from the parent DNS provider, export or copy them before delegation goes live. Match record names carefully, because DNS provider interfaces differ: one may expect api, another may expect api.app.example.com. Set moderate TTL values during setup, such as 300 or 600 seconds, so corrections can take effect quickly while you validate the new zone.
Adding NS Records in the Parent Domain Zone
After the subdomain zone exists at the new DNS provider, the parent domain must publish delegation records that point resolvers to that provider’s authoritative nameservers. If the parent domain is example.com and the delegated subdomain is app.example.com, the parent zone needs NS records at the name app. These records do not go into the new provider’s zone as the delegation step; they are added where example.com is currently hosted.
Use the exact nameserver hostnames assigned by the new DNS provider for the subdomain zone. They often look like ns1.provider.net, ns2.provider.net, or provider-specific names such as lina.ns.cloudflare.com and max.ns.cloudflare.com. Add one NS record for each assigned nameserver, all with the same record name: the delegated subdomain label.
Rank #3

- ✅ Organize Your Freezer with a Complete Ice System: This ice cube tray with lid and bin set solves freezer clutter by combining 4 silicone ice cube trays, a central storage container, and a scoop. Keep your kitchen tidy while always having ice ready for daily drinks, cooking, or entertaining.
- ✅ Easy-Pop Ice Release with Secure Non-Spill Lids: Each silicone ice tray features a flexible bottom for effortless ice cube removal—simply push from below. The ice tray with lid has lift tabs for easy handling and minimizes spills when moving (note: lids allow airflow and are not airtight).
- ✅ Maximize Freezer Space with Stackable Design: These ice trays for freezer stack neatly to save vertical space. Perfect for compact apartment freezers, RV refrigerators, or organizing multiple ice cube trays for freezer for parties and home use.
- ✅ BPA-Free and Odor-Resistant for Pure Ice Taste: Made from food-grade silicone and durable plastic, these ice trays resist absorbing freezer odors. Ensure clean, tasteless ice for your cocktails, coffee, or family meals with these BPA-free ice trays.
- ✅ Versatile and Dishwasher Safe for Easy Cleanup: Create clear cubes or infuse with fruits for flavored ice. The entire ice bucket kits set is top-rack dishwasher safe, making cleanup simple and convenient after parties or daily use.
| Parent zone | Record name | Type | Value |
|---|---|---|---|
| example.com | app | NS | ns1.new-dns-provider.net |
| example.com | app | NS | ns2.new-dns-provider.net |
Many DNS control panels accept the short label, such as app, because the zone origin is already example.com. Others require the fully qualified name, such as app.example.com. Avoid entering app.example.com.example.com, which can happen when a panel automatically appends the parent domain to a fully qualified name that was not terminated or recognized properly. If the interface has a separate “Name” or “Host” field, confirm how it displays the resulting record before saving.
Records to avoid at the delegation point
At the delegated name in the parent zone, keep the configuration clean. The parent zone should normally contain only the NS records for app.example.com, not A, AAAA, CNAME, MX, or TXT records for that same name. Once delegation exists, authoritative answers for hosts under the subdomain come from the new provider’s zone. For example, www.app.example.com, api.app.example.com, and TXT validation records under app.example.com should be created at the new provider, not in the parent zone.
- Add NS records in the parent provider: create NS records for the subdomain label, pointing to the new provider’s assigned nameservers.
- Do not change parent domain nameservers: the registrar-level nameservers for example.com remain with the existing DNS host.
- Use all assigned nameservers: if the new provider gives four nameservers, publish all four unless the provider instructs otherwise.
- Match the subdomain exactly: delegate app.example.com only if the zone at the new provider is also created as app.example.com.
Set a practical TTL for the NS records. During migration or testing, a shorter value such as 300 or 600 seconds can make corrections faster. After the delegation is stable, increasing the TTL to 3600 or higher can reduce query load and improve cache efficiency. Some managed DNS platforms enforce minimum TTL values, so use the closest available setting.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Fix the driver behind crashes, sound loss and screen glitches3Clear out junk files and repair common Windows errorsIf the delegated subdomain’s nameservers are themselves inside the subdomain being delegated, such as ns1.app.example.com, glue records may be required in the parent zone or at the registrar, depending on the hierarchy and provider. Most cloud DNS providers avoid this by assigning nameservers in their own domains, which do not require glue from your parent zone. After saving the NS records, allow for caching based on the previous TTL and then test from mulle resolvers to confirm that queries for the subdomain are being referred to the new authoritative nameservers.
Verifying Delegation and DNS Propagation
After the parent zone contains the subdomain’s NS records and the new DNS provider hosts an authoritative zone for that subdomain, verify the delegation from the top down. The goal is to confirm that resolvers can start at the parent domain, discover the delegated nameservers, and then receive authoritative answers from the new provider for records inside the subdomain.
Check the delegation path
Use a DNS lookup tool that can query specific record types, such as dig, nslookup, or an online DNS checker. First, query the parent domain’s authoritative nameservers for the subdomain’s NS records. For example, if the parent domain is example.com and the delegated subdomain is app.example.com, query for NS app.example.com. The response should list the nameservers assigned by the new DNS provider, such as ns1.newdns.example and ns2.newdns.example.
Next, query one of those delegated nameservers directly for a record that exists in the subdomain zone. For example, if the new provider’s zone contains www.app.example.com as an A or CNAME record, query the delegated nameserver directly. The response should be marked as authoritative, commonly shown by the aa flag in dig output. This confirms that the new provider is not merely returning cached data but is actually authoritative for the delegated subdomain.
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Useful verification commands
- Find the delegated nameservers:
dig NS app.example.com - Trace the full lookup path:
dig +trace www.app.example.com - Query the new provider directly:
dig @ns1.newdns.example www.app.example.com A - Check DNSSEC-related records, if used:
dig DS app.example.comanddig DNSKEY app.example.com
Propagation is mostly about resolver caching. Once the parent zone is updated, recursive resolvers may continue using previously cached data until the old TTL expires. If the subdomain did not exist before, propagation is often faster because there may be no cached NS answer. If the subdomain previously had records in the parent zone, stale answers can persist until the cached records expire. Testing from mulle networks or public resolvers, such as Google Public DNS, Cloudflare, or Quad9, can show whether the change is visible broadly or only from certain locations.
Rank #4

- 【Food Grade Material】Made from eco-friendly PP+TPR material that is BPA Free and Food-Grade. The flexible material allows the dish strainers for kitchen counter to collapse flat for easy space-saving and storage, making the most of your kitchen countertop.
- 【Built-in Utensil Drying Rack】Separate storage area for utensils and gadgets, the non-slip dish drying rack is scratch-proof and offers a safe place for plates and cups, and has a separate compartment for cutlery. Perfect for storage and draining dinnerware and glassware.
- 【Compact and Portable】The collapsible dish drainer is simply pop-up to open when using and collapses to flat for space-saving storage, you can easily store it under the sink or slip it into any cabinet. Suitable for both indoors & outdoors uses, such as camping, BBQ, RV and boats, campsite cleanup, and vacation homes, etc.
- 【Drying Water Quickly】The collapsible dish storage rack versatile tool for all your household tasks, at the same time, will not hurt your hands or scratch the sink. The Bottom with an adjustable swivel drain strip allows water to run directly into the sink, keeping your counters clean and dry.
- 【Easy to Maintain】Heavy-duty plastic is simple to wipe clean, and there’s no rusting like the old clunky metal dish drying rack. The kitchen organizers for dishes is scratch-proof and offers a safe place for plates and cups, and prevent the rack from shifting and scratching any counter top.
What a successful result looks like
| Check | Expected result |
|---|---|
| NS lookup for the subdomain | Returns only the new provider’s nameservers for the delegated subdomain |
| Direct query to delegated nameserver | Returns the intended record with an authoritative answer |
| Trace lookup | Shows the parent domain handing off the subdomain to the new provider |
| Public resolver checks | Eventually return the same records as the delegated nameservers |
If results are inconsistent, compare the parent-side NS records with the nameservers listed in the new provider’s control panel. They must match exactly. Also confirm that the zone name at the new provider is the delegated subdomain itself, such as app.example.com, not the parent domain unless that is the intended design. When DNSSEC is enabled on the parent domain, make sure the DS record for the subdomain is either correctly published or absent if the delegated zone is unsigned; a mismatched DS record can cause validating resolvers to fail even when the NS records are correct.
Common Configuration Mistakes and Troubleshooting
Most subdomain delegation problems come from a mismatch between the parent zone, the child zone, and the name servers assigned by the new DNS provider. A delegated subdomain such as app.example.com needs two separate pieces to line up: the parent zone for example.com must contain NS records for app.example.com, and the new provider must host an authoritative zone for that exact subdomain. If either side is missing or uses a different name, resolvers may return NXDOMAIN, stale answers, or inconsistent results depending on which resolver is queried.
Frequent delegation errors
- Creating records in the wrong zone: adding www.app.example.com or api.app.example.com records in the parent zone does not delegate app.example.com. The parent zone should usually contain only the child-zone NS records, unless you are intentionally keeping some records undelegated.
- Using the wrong owner name for NS records: the NS records in the parent must be attached to the delegated subdomain name, such as app.example.com, not to the apex example.com.
- Copying incomplete name server sets: many providers assign two, three, or four authoritative name servers. Add the full set exactly as shown by the new provider to avoid uneven resolution.
- Forgetting the trailing dot in zone-file style editors: some DNS interfaces require ns1.provider.net. with a trailing dot. Without it, the value may be interpreted as ns1.provider.net.example.com.
- Creating the wrong child zone: a zone named example.com at the new provider will not answer authoritatively for app.example.com unless the provider also has the correct subdomain zone or records configured under it.
- Mixing CNAME and NS at the same name: a delegated name such as app.example.com should not also have a CNAME at that same owner name in the parent zone.
Start troubleshooting by querying the delegation path rather than only checking a public DNS lookup page. First, confirm that the parent domain’s authoritative name servers return the expected NS records for the subdomain. Then query one of the child zone’s authoritative name servers directly for a record you expect to exist, such as an A, AAAA, MX, or TXT record. This separates parent-side delegation issues from child-zone content issues. If the parent returns no NS records, fix the parent zone. If the child name server does not answer authoritatively for the subdomain, fix the zone setup at the new provider.
Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Repair Windows errors before they cause bigger problemsFix Now →| Symptom | Likely cause | What to check |
|---|---|---|
| Subdomain returns NXDOMAIN | Missing child zone or missing record inside the child zone | Confirm the zone exists at the new provider and contains the queried hostname |
| Some resolvers work, others fail | Incomplete or inconsistent name server configuration | Compare all parent NS records with the provider-assigned name server list |
| Old answers still appear | Cached data from previous TTL values | Wait for prior TTLs to expire and test against authoritative servers |
| Provider says zone is not delegated | Parent NS records not published or not saved | Check the parent domain’s authoritative servers, not only the registrar dashboard |
Also review DNSSEC if the parent domain uses it. A signed parent zone with an incorrect DS record for the delegated subdomain can cause validating resolvers to reject otherwise valid DNS answers. If the child provider supports DNSSEC, publish the correct DS record from that provider in the parent zone. If DNSSEC is not being used for the subdomain, remove stale DS records for that delegated name. After each correction, test from authoritative servers first, then from mulle recursive resolvers to confirm that delegation and cached responses have converged.
Security, TTL, and Maintenance Best Practices
After a subdomain has been delegated, treat it as a separate DNS zone with its own security controls, change process, and operational owner. The parent domain still controls the delegation through its NS records, but the delegated provider controls the answers beneath the subdomain. That split is useful, but it also means mistakes can be harder to spot unless both sides are documented. Record the delegated zone name, authoritative nameservers, account owner, registrar or DNS provider, support contacts, DNSSEC status, and the intended purpose of the subdomain.
Use clear access controls
Limit access to the delegated DNS provider to the team or service that actually manages the subdomain. Enable multi-factor authentication for all accounts, avoid shared logins, and use role-based permissions where the provider supports them. If automation updates records through an API, create scoped API tokens that can modify only the delegated zone, not the entire DNS account. Rotate those tokens on a schedule and immediately revoke them when systems or staff change.
- Separate ownership: make it clear who can change records in the delegated zone and who can change the parent NS delegation.
- Audit logging: use a provider that records DNS changes, user activity, API calls, and failed login attempts.
- Change review: require review for high-impact records such as MX, CAA, TXT verification records, wildcard records, and apex records within the delegated zone.
- Zone backups: export zone files or maintain records in infrastructure-as-code so the zone can be rebuilt if needed.
Choose TTLs based on stability
TTL values affect how long recursive resolvers and clients may cache DNS answers. For the parent-zone NS records that delegate the subdomain, use a moderate TTL such as 3600 seconds or 14400 seconds when the delegation is stable. Avoid extremely long TTLs unless the nameservers are unlikely to change, because moving the subdomain to another DNS provider will take longer to complete. During a planned migration, lower the parent NS TTL and any critical records inside the delegated zone at least one previous-TTL period before the change.
| Record type | Common TTL range | Use case |
|---|---|---|
| Parent NS records | 3600-14400 seconds | Stable subdomain delegation |
| A, AAAA, CNAME | 300-3600 seconds | Application endpoints that may change during releases |
| MX, TXT, CAA | 3600-86400 seconds | Mail, verification, and certificate policy records |
Maintain DNSSEC deliberately
If the parent domain uses DNSSEC and the delegated subdomain should also be signed, configure DNSSEC at the new provider and publish the correct DS record in the parent zone. The DS record must match the delegated provider’s DNSKEY data. A stale or incorrect DS record can make the entire delegated subdomain fail validation for DNSSEC-validating resolvers. If the delegated provider does not support DNSSEC, do not publish a DS record for that subdomain in the parent zone.
Best Value

- Advanced 6-Step Filtration Technology: Discover the impressive power of the Tastepure RV water filter’s Hex-Flow Technology and its 6-step filtration process. Each layer seamlessly works together to deliver water that’s exceptionally clean.
- Certified Lead-Free: This camping water filter is independently tested & listed to standards NSF/ANSI 42 & NSF/ANSI 53. It’s CSA lead-free content certified to NSF/ANSI 372 & compliant with all federal & state-level lead-free laws.
- Access to Pure, Great-Tasting Water: Enjoy clean water anywhere! This RV inline filter reduces bad tastes, odor, chlorine, sediment, etc. GAC filtration, combined with KDF controls bacteria & mold growth when the outdoor water filter isn’t in use.
- Patented Technology & Made in the USA: This in-line water filter is proudly made in the USA with top-notch materials and expert craftsmanship. The patented design has undergone rigorous testing and quality control to meet the highest standards.
- Versatile Applications: Easily attach this multi-purpose hose water filter to any standard garden or drinking water hose to receive cleaner drinking water. It’s great for campers, boats, pets, gardening, car washes, car detailing, & more.
Schedule routine checks for delegation health. Query the parent zone to confirm the NS set still matches the provider’s assigned nameservers, then query each authoritative nameserver directly to confirm it serves the zone and returns consistent SOA and record data. Monitor certificate issuance, mail delivery, and application availability for services under the delegated subdomain. Also review the zone periodically for obsolete TXT verification records, unused hostnames, overly broad wildcards, and records pointing to decommissioned cloud resources, since these can create takeover or impersonation risk.
Frequently Asked Questions
Do I need to move the whole domain to delegate one subdomain?
No. You can keep the parent domain, such as example.com, at its current DNS provider and delegate only a subdomain, such as app.example.com, to another provider. The parent zone only needs NS records for the subdomain that point to the authoritative nameservers assigned by the new DNS provider.
Where do I create the DNS records for the delegated subdomain?
After delegation is in place, records for the delegated subdomain belong in the zone at the new DNS provider. For example, if app.example.com is delegated, A, AAAA, CNAME, MX, TXT, or other records for app.example.com and names below it should be managed in that provider’s app.example.com zone. Records in the parent example.com zone will not control the delegated subdomain except for the NS delegation itself.
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallCrashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteWhat NS records should I add in the parent DNS zone?
Add NS records at the exact subdomain name you want to delegate, such as app.example.com, using the nameserver hostnames supplied by the new DNS provider. Include all assigned nameservers, not just one, and do not invent or shorten the values. If the delegated nameservers are inside the delegated subdomain itself, you may also need glue records, but most third-party DNS providers use nameserver names under their own domains.
How can I check whether the subdomain delegation is working?
Query the NS records for the subdomain and confirm they match the new provider’s authoritative nameservers. Then query a test record, such as an A or TXT record created in the delegated zone, directly against one of those nameservers and through a public resolver. If direct authoritative queries work but public resolvers still show old data, you may be waiting for cached DNS responses to expire.
What are the most common mistakes when delegating a subdomain?
Common errors include creating the subdomain zone at the new provider but forgetting to add NS records in the parent zone, adding NS records at the wrong name, or leaving conflicting records in the parent zone. Another frequent issue is using nameservers from the wrong zone or only copying part of the provider’s assigned NS set. Keep TTLs low before planned changes, verify with authoritative DNS queries, and document which provider controls each zone.
Bottom Line
Delegating a subdomain to another DNS provider is straightforward: create the subdomain zone at the new provider, copy its authoritative nameservers, and add matching NS records for that subdomain in the parent domain’s DNS zone. Once propagation completes, the parent domain stays where it is while the delegated subdomain is managed independently.
Before relying on it in production, verify the delegation with DNS lookup tools, confirm the child zone has the records it needs, and monitor for DNSSEC, TTL, or stale-record issues. Your next step is to document the delegated zone’s owners, nameservers, and change process so future updates don’t break resolution.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




