Pakistan Telecommunication Authority has issued an urgent cybersecurity alert warning organizations about a critical vulnerability affecting Oracle WebServer, a widely used platform for hosting enterprise applications. The alert calls for immediate attention from system administrators, IT security teams, government entities, telecom operators, financial institutions, and businesses that rely on WebLogic-based services.
The vulnerability could allow attackers to compromise exposed servers, disrupt services, steal sensitive data, or gain unauthorized control over affected systems if left unpatched. Because WebServer is often connected to business-critical applications, exploitation can quickly escalate into operational outages, regulatory exposure, and wider network compromise.
As an Amazon Associate I earn from qualifying purchases.
Organizations using Oracle WebServer should review their deployments, apply the latest Oracle security patches, restrict unnecessary internet exposure, monitor for suspicious activity, and implement recommended mitigation controls without delay. Rapid action is essential to reduce the risk of active exploitation and protect critical digital infrastructure.
What PTA’s Cybersecurity Alert Says
The Pakistan Telecommunication Authority has issued an urgent cybersecurity alert warning organizations about a critical vulnerability affecting Oracle WebServer. The advisory is directed at enterprises, government departments, telecom operators, banks, internet service providers, hosting companies, software vendors, and any organization running WebLogic-based applications that are accessible from internal or public networks. PTA’s message is clear: exposed and unpatched WebLogic instances can become immediate targets for cyberattacks, especially where administrative consoles or application endpoints are reachable over the internet.
#1 Best Overall

- rv toilet brush: Engineered specifically for RVs, this brush features a silicone head that gently cleans without damaging the toilet bowl or seals, a must for traditional toilet brushes.
- Compact Wall-Mounted Toilet Brush: With its space-saving design, this brush is easy to stow away discreetly, perfect for the limited space in RVs.
- silicone toilet brush: This brush is designed for thorough cleaning of the toilet bowl without causing any harm to the porcelain or seals. The drip-free toilet brush holder is crafted to collect water from the brush, preventing any mess on your RV's floor.
- Wall-Mounted Toilet Brush for RV Travel: The brush head is conveniently attachable to the bathroom wall, ensuring that there's no rolling around during your trips. With this setup, you can travel with peace of mind, knowing your toilet brush is securely in place.
The alert highlights the severity of the vulnerability because Oracle WebServer is widely used to host enterprise Java applications, business portals, authentication services, middleware platforms, and backend systems. A successful exploit could allow an attacker to compromise the server, execute malicious commands, deploy unauthorized web shells, steal sensitive data, disrupt services, or pivot deeper into an organization’s network. In environments where WebLogic is connected to databases, identity systems, payment platforms, or customer-facing applications, the impact can extend beyond a single server and affect critical business operations.
Core points in the PTA advisory
- Urgent review required: Organizations should immediately identify whether Oracle WebLogic Server is deployed in their environment, including production, staging, development, and disaster recovery systems.
- Internet-facing systems are highest risk: WebLogic servers exposed to the public internet, especially those with management interfaces enabled, should be treated as priority assets for remediation.
- Security patches must be applied: Administrators are advised to install the latest Oracle security updates and Critical Patch Update fixes relevant to their WebLogic Server versions.
- Access should be restricted: Management consoles and administrative ports should not be publicly accessible and should be limited to trusted networks, VPNs, or dedicated management segments.
- Monitoring is required: Organizations should inspect logs, network traffic, running processes, and application directories for signs of exploitation or suspicious changes.
PTA’s alert also points to the need for coordinated action between IT operations, security teams, application owners, and senior management. This is not only a routine software maintenance issue; it is a high-risk exposure that can lead to service outages, data theft, ransomware deployment, and regulatory consequences if left unresolved. Organizations that rely on third-party vendors or managed service providers for Webadministration should contact them immediately to confirm patch status, hardening measures, and incident response readiness.
The advisory urges organizations to act quickly because vulnerabilities in widely deployed enterprise servers are often exploited soon after public disclosure or patch release. Attackers routinely scan the internet for vulnerable Webinstances and use automated tools to attempt compromise at scale. For this reason, PTA recommends immediate asset discovery, patch deployment, exposure reduction, and continuous monitoring rather than waiting for visible signs of an attack. Early action can significantly reduce the likelihood of compromise and help protect critical digital services from disruption.
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →Understanding the Critical Oracle WebLogic Server Vulnerability
Oracle WebServer is widely used to run enterprise Java applications, middleware services, internal portals, financial systems, telecom platforms, and customer-facing web applications. A critical vulnerability in this environment is especially serious because WebLogic often sits at the center of application delivery, connecting databases, identity systems, APIs, and business workflows. PTA’s alert highlights the need to treat exposed WebLogic instances as high-risk assets, particularly when they are reachable from the internet or accessible through poorly segmented internal networks.
The vulnerability can allow attackers to target affected WebServer components and, in severe cases, execute unauthorized commands on the server. Depending on the vulnerable version, configuration, and network exposure, exploitation may lead to remote code execution, application takeover, data theft, service disruption, deployment of web shells, or movement into other connected systems. Attackers commonly scan for vulnerable WebLogic endpoints soon after public advisories are issued, making unpatched servers attractive targets for automated exploitation campaigns.
How attackers may exploit exposed WebLogic systems
Threat actors typically begin by identifying Webservices through open ports, management consoles, exposed application paths, or recognizable server responses. If a vulnerable component is accessible, they may send crafted requests designed to trigger the flaw and gain control over the application server process. Once successful, attackers can attempt to upload malicious files, create persistence mechanisms, harvest credentials, access sensitive application data, or use the compromised server as a foothold for broader network compromise.
- Remote code execution: An attacker may run arbitrary commands with the privileges of the WebLogic service account.
- Credential compromise: Configuration files, application secrets, database passwords, and integration tokens may be exposed.
- Data breach risk: Applications hosted on WebLogic may process customer records, billing data, operational information, or government-related datasets.
- Service outage: Exploitation can crash services, corrupt deployments, or support ransomware activity.
- Lateral movement: A compromised middleware server can provide access to backend databases, directory services, or internal APIs.
The risk level increases when organizations run outdated Oracle WebServer versions, delay Critical Patch Update installation, expose the administration console to public networks, use default or weak credentials, or operate servers with excessive privileges. Systems that support public-facing services, managed service platforms, telecom infrastructure, financial applications, or e-government portals require immediate review because the operational impact of compromise can be significant.
Rank #2
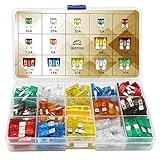
- Easy Identification: Made of a high quality zinc alloy, with a transparent cover and color coded
- 14 Most Common Fuses: Standard and Mini. (5A/ 7.5A/ 10A/ 15A/ 20A/ 25A/ 30A)
- Wide Applications: Fits most vehicles like car, truck, marine, SUV, travel trailer and other vehicles
- Note: Please use the right amp fuse to protect the vehicle and electronic equipment from short-circuit/overload
- ll Sizes You Need: The package contains 140pcs fuse and 2pcs fuse puller - 70pcs standard fuse and 70pcs mini fuse. (10pcs of each AMP)
This vulnerability should not be viewed as a routine software defect. Webservers often hold trusted positions inside enterprise environments, and a single compromised instance can undermine multiple business applications. Organizations should identify affected versions, confirm whether vulnerable components are enabled, review exposure to the internet, and prioritize remediation based on business criticality and attack surface. Rapid assessment is essential because exploitation attempts may occur before security teams observe clear signs of compromise.
Who Is at Risk and Potential Business Impact
Organizations running Oracle WebServer are directly exposed if their deployments include vulnerable versions, incomplete patch levels, internet-facing administration consoles, or applications reachable through public networks. This includes enterprises, government bodies, telecom operators, banks, universities, healthcare providers, cloud service customers, and software vendors that use WebLogic as part of their middleware stack. The risk is higher where servers are connected to critical business applications such as customer portals, billing systems, identity services, enterprise resource planning platforms, or internal workflow tools.
Systems are especially vulnerable when Webinstances are exposed to the internet without strict access controls, when legacy versions remain in production, or when patching has been delayed because of operational dependencies. Environments using default configurations, weak administrative credentials, unnecessary services, or poorly segmented networks may face a broader compromise if an attacker gains initial access. Managed service providers and hosting companies should also treat the alert as high priority because a single exposed platform may support multiple downstream customers.
Entities most likely to be affected
- Public-sector organizations that operate citizen services, licensing portals, tax systems, or internal administrative platforms on Oracle middleware.
- Financial institutions using WebLogic to support online banking, payment gateways, reporting systems, or back-office transaction processing.
- Telecom and internet service providers that rely on Java-based enterprise applications for customer management, billing, provisioning, or network operations.
- Healthcare and education institutions with web portals connected to sensitive records, identity data, or research systems.
- Large enterprises and supply-chain partners that host business applications, APIs, or vendor-integrated platforms on affected WebLogic servers.
The potential impact can be severe because Weboften sits at the center of high-value enterprise environments. A successful exploit may allow unauthorized access, remote code execution, malware deployment, data theft, service disruption, or lateral movement into connected systems. Attackers may use a compromised server to steal credentials, alter application data, deploy web shells, encrypt files, or establish persistent access. In regulated sectors, such an incident can also trigger reporting obligations, legal exposure, audit findings, and reputational damage.
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteBusiness disruption may extend beyond the affected server. If Websupports customer-facing services, exploitation could result in portal outages, failed transactions, delayed service delivery, or loss of user trust. If it supports internal operations, organizations may face interrupted workflows, unavailable dashboards, suspended integrations, or degraded productivity across departments. For companies with contractual service-level agreements, downtime or data exposure may also create financial penalties and customer claims.
| Risk Area | Potential Business Impact |
|---|---|
| Data confidentiality | Exposure of customer records, credentials, financial data, or sensitive government and corporate information. |
| Service availability | Application outages affecting public portals, payment systems, internal platforms, or partner integrations. |
| Operational continuity | Disruption to billing, reporting, case management, provisioning, or enterprise workflows. |
| Compliance and trust | Regulatory scrutiny, incident disclosure requirements, reputational harm, and loss of stakeholder confidence. |
Organizations should treat exposure as time-sensitive because critical Webvulnerabilities are frequently targeted soon after public disclosure. Threat actors often scan the internet for affected servers and attempt automated exploitation against unpatched systems. Any organization that cannot immediately confirm its WebLogic version, patch status, network exposure, and access controls should assume elevated risk until validation is complete.
Immediate Actions Organizations Should Take
Organizations running Oracle WebServer should treat PTA’s alert as an active operational priority, not a routine advisory. The first step is to identify every WebLogic instance across production, staging, testing, disaster recovery, and cloud environments. Security teams should confirm the exact WebLogic Server versions in use, whether the affected components are enabled, and whether any instance is exposed to the public internet or reachable from untrusted network segments.
Rank #3

- ✅ Organize Your Freezer with a Complete Ice System: This ice cube tray with lid and bin set solves freezer clutter by combining 4 silicone ice cube trays, a central storage container, and a scoop. Keep your kitchen tidy while always having ice ready for daily drinks, cooking, or entertaining.
- ✅ Easy-Pop Ice Release with Secure Non-Spill Lids: Each silicone ice tray features a flexible bottom for effortless ice cube removal—simply push from below. The ice tray with lid has lift tabs for easy handling and minimizes spills when moving (note: lids allow airflow and are not airtight).
- ✅ Maximize Freezer Space with Stackable Design: These ice trays for freezer stack neatly to save vertical space. Perfect for compact apartment freezers, RV refrigerators, or organizing multiple ice cube trays for freezer for parties and home use.
- ✅ BPA-Free and Odor-Resistant for Pure Ice Taste: Made from food-grade silicone and durable plastic, these ice trays resist absorbing freezer odors. Ensure clean, tasteless ice for your cocktails, coffee, or family meals with these BPA-free ice trays.
- ✅ Versatile and Dishwasher Safe for Easy Cleanup: Create clear cubes or infuse with fruits for flavored ice. The entire ice bucket kits set is top-rack dishwasher safe, making cleanup simple and convenient after parties or daily use.
Once the asset scope is clear, administrators should apply Oracle’s relevant Critical Patch Update or emergency security patch without delay. Internet-facing Webservers should be prioritized first, followed by systems that support sensitive business functions, authentication workflows, customer portals, payment systems, internal applications, or integrations with databases and identity providers. If patching cannot be completed immediately, organizations should apply temporary mitigations recommended by Oracle and restrict access to vulnerable services until updates are in place.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Priority response checklist
- Inventory WebLogic deployments: Locate all servers, domains, clusters, managed servers, admin consoles, and middleware environments using Oracle WebLogic Server.
- Check exposure: Determine whether WebLogic ports, administration consoles, T3 services, HTTP endpoints, or related interfaces are accessible from the internet.
- Apply security patches: Install the latest Oracle patches that address the reported vulnerability, following Oracle’s official documentation and compatibility guidance.
- Restrict network access: Limit access to WebLogic administration interfaces using VPNs, firewalls, allowlists, private networks, or jump hosts.
- Review logs: Examine access logs, server logs, audit logs, and web application logs for unusual requests, failed exploit attempts, unexpected outbound traffic, or suspicious authentication activity.
- Hunt for compromise: Look for unknown web shells, unauthorized user accounts, modified application files, unusual Java processes, scheduled tasks, and unfamiliar deployments.
- Back up critical systems: Create verified backups of configurations, applications, databases, and domain files before major remediation work, while ensuring backups are not already compromised.
Security teams should also increase monitoring around affected systems during and after patching. This includes checking endpoint detection alerts, web application firewall events, SIEM correlation rules, outbound DNS queries, and unexpected connections from Webservers to external IP addresses. Any sign of exploitation should trigger incident response procedures, including isolating the affected host, preserving forensic evidence, rotating credentials, and reviewing connected systems for lateral movement.
Organizations that cannot immediately patch due to application dependency, uptime, or compatibility constraints should reduce risk through compensating controls. Disable unused Webservices, block unnecessary protocols, remove direct access to the administration console, enforce strong authentication, and segment WebLogic servers from databases and internal management networks. Load balancers, reverse proxies, and web application firewalls can help filter malicious traffic, but they should not be treated as replacements for vendor patches.
Executive and IT leadership should ensure that remediation has a clear owner, deadline, and verification process. After patches or mitigations are applied, teams should validate that the vulnerability is no longer exploitable by checking version numbers, reviewing patch inventory, running approved vulnerability scans, and documenting the actions taken. Because critical Webflaws have historically been targeted quickly by attackers, delays can increase the chance of remote code execution, data theft, service disruption, and deeper compromise across enterprise systems.
Patch Management and Mitigation Guidance
Organizations running Oracle WebServer should treat patching as the primary remediation path, not as a routine maintenance activity that can wait for the next service window. Administrators should first identify every WebLogic instance across production, staging, disaster recovery, and development environments, then compare installed versions against Oracle’s latest Critical Patch Update and security advisory guidance. This inventory should include internet-facing systems, middleware used by business applications, and embedded WebLogic components bundled with larger enterprise platforms.
Recommended Free Tools
Before applying updates, teams should take full backups of configurations, domains, application deployments, keystores, and relevant databases. Patches should be tested in a controlled environment that mirrors production as closely as possible, especially where custom Java applications, authentication integrations, or legacy dependencies are in use. Once compatibility is confirmed, the patched build should be moved into production using an approved change process with clear rollback steps, maintenance notifications, and post-deployment validation.
Recommended patching workflow
- Confirm exposure: Locate WebLogic servers and determine whether administrative consoles, T3/IIOP channels, or application endpoints are reachable from untrusted networks.
- Check versions: Verify the exact WebLogic Server release, patch set level, and Java runtime version on each host.
- Download trusted updates: Obtain patches only from Oracle’s official support portal or approved enterprise software repositories.
- Test before rollout: Validate application startup, authentication, clustering, managed server communication, and scheduled jobs after patch installation.
- Deploy quickly: Prioritize public-facing and business-critical systems, followed by internal servers that could be reached after lateral movement.
- Verify remediation: Re-scan systems, review patch logs, and confirm that vulnerable components are no longer present.
If immediate patching is not possible, temporary mitigation controls should be applied without delay. These may include restricting access to the WebAdministration Console, blocking unnecessary protocols such as T3 from external networks, enforcing firewall allowlists, disabling unused components, and placing affected services behind a properly configured reverse proxy or web application firewall. Network segmentation can also reduce the chance that a compromised WebLogic server becomes a pathway into databases, identity systems, or internal application servers.
Rank #4

- 【Food Grade Material】Made from eco-friendly PP+TPR material that is BPA Free and Food-Grade. The flexible material allows the dish strainers for kitchen counter to collapse flat for easy space-saving and storage, making the most of your kitchen countertop.
- 【Built-in Utensil Drying Rack】Separate storage area for utensils and gadgets, the non-slip dish drying rack is scratch-proof and offers a safe place for plates and cups, and has a separate compartment for cutlery. Perfect for storage and draining dinnerware and glassware.
- 【Compact and Portable】The collapsible dish drainer is simply pop-up to open when using and collapses to flat for space-saving storage, you can easily store it under the sink or slip it into any cabinet. Suitable for both indoors & outdoors uses, such as camping, BBQ, RV and boats, campsite cleanup, and vacation homes, etc.
- 【Drying Water Quickly】The collapsible dish storage rack versatile tool for all your household tasks, at the same time, will not hurt your hands or scratch the sink. The Bottom with an adjustable swivel drain strip allows water to run directly into the sink, keeping your counters clean and dry.
- 【Easy to Maintain】Heavy-duty plastic is simple to wipe clean, and there’s no rusting like the old clunky metal dish drying rack. The kitchen organizers for dishes is scratch-proof and offers a safe place for plates and cups, and prevent the rack from shifting and scratching any counter top.
Security teams should increase monitoring while patching is underway. Logs from Web, operating systems, endpoint tools, firewalls, and intrusion detection platforms should be reviewed for suspicious authentication attempts, unexpected Java process activity, outbound connections to unknown hosts, web shell indicators, or changes to deployed applications. Any sign of exploitation should trigger incident response procedures, including isolation of the affected server, forensic preservation, credential rotation, and review of connected systems.
| Control | Action | Purpose |
|---|---|---|
| Official security patch | Apply the latest Oracle update for the affected WebLogic version | Removes the vulnerable code path |
| Access restriction | Limit admin console and management ports to trusted IP addresses | Reduces exposure to remote attackers |
| Protocol hardening | Disable or restrict T3 and other unused services | Limits common exploitation channels |
| Monitoring | Correlate WebLogic, network, and endpoint logs | Detects exploitation attempts and compromise indicators |
After remediation, organizations should document the patch status, affected assets, compensating controls, and validation results. This record helps management, auditors, and incident response teams confirm that the vulnerability has been addressed across the environment rather than only on the most visible servers.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Scan for outdated or missing drivers - takes under a minute3Clear out junk files and repair common Windows errorsBest Practices to Strengthen WebLogic Server Security
After applying Oracle’s security updates and completing immediate containment steps, organizations should harden Oracle WebServer as part of routine security operations. A patched server can still be exposed if administrative consoles are internet-facing, default configurations remain unchanged, or privileged accounts are poorly controlled. Security teams should treat WebLogic as a high-value application platform because it often supports identity services, enterprise applications, payment workflows, customer portals, and internal business systems.
Reduce exposure and restrict administrative access
The WebAdministration Console, Node Manager, T3 services, and managed server interfaces should not be reachable from the public internet unless there is a verified business requirement. Administrative access should be limited through VPNs, bastion hosts, private networks, and firewall allowlists. Where possible, bind management services to internal interfaces only and block unnecessary ports at the network layer. Organizations should also review load balancer, reverse proxy, and cloud security group rules to ensure legacy access paths have not been left open.
- Disable unused services: Turn off components, sample applications, test deployments, and protocols that are not required in production.
- Restrict T3 and IIOP traffic: Allow these protocols only between trusted application components and block external access.
- Separate environments: Keep development, staging, and production WebLogic domains isolated with different credentials and network controls.
- Use least privilege: Assign users and service accounts only the permissions required for their role.
Strengthen authentication, secrets, and configuration
Administrative accounts should be protected with strong passwords, multi-factor authentication where supported through integrated identity providers, and strict account lockout policies. Default usernames, shared administrator accounts, and long-lived service credentials increase risk during exploitation attempts. Credentials stored in scripts, deployment plans, CI/CD pipelines, or configuration files should be rotated and moved into approved secrets management systems. Teams should also review Websecurity realms, authentication providers, role mappings, and trust relationships to confirm that access is intentional and current.
TLS should be enforced for administrative and application traffic, using valid certificates and modern cipher suites. Self-signed certificates may be acceptable in isolated lab environments, but production systems should rely on managed certificate lifecycles. Java versions, middleware dependencies, plugins, database drivers, and operating system packages should be maintained alongside Webpatches, since attackers often chain multiple weaknesses to gain access or move laterally.
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Improve monitoring, logging, and incident readiness
Weblogs should be forwarded to a centralized security monitoring platform and retained for investigation. Security teams should monitor failed login attempts, unexpected deployments, unusual outbound connections, changes to domain configuration, suspicious Java processes, and newly created files in application deployment directories. Alerts should be tuned for indicators such as unauthorized WAR uploads, abnormal use of administrative endpoints, and connections from unfamiliar geographies or hosting providers.
Best Value

- Advanced 6-Step Filtration Technology: Discover the impressive power of the Tastepure RV water filter’s Hex-Flow Technology and its 6-step filtration process. Each layer seamlessly works together to deliver water that’s exceptionally clean.
- Certified Lead-Free: This camping water filter is independently tested & listed to standards NSF/ANSI 42 & NSF/ANSI 53. It’s CSA lead-free content certified to NSF/ANSI 372 & compliant with all federal & state-level lead-free laws.
- Access to Pure, Great-Tasting Water: Enjoy clean water anywhere! This RV inline filter reduces bad tastes, odor, chlorine, sediment, etc. GAC filtration, combined with KDF controls bacteria & mold growth when the outdoor water filter isn’t in use.
- Patented Technology & Made in the USA: This in-line water filter is proudly made in the USA with top-notch materials and expert craftsmanship. The patented design has undergone rigorous testing and quality control to meet the highest standards.
- Versatile Applications: Easily attach this multi-purpose hose water filter to any standard garden or drinking water hose to receive cleaner drinking water. It’s great for campers, boats, pets, gardening, car washes, car detailing, & more.
| Security Area | Recommended Control |
|---|---|
| Network access | Limit management ports to trusted internal networks and approved administrator jump hosts. |
| Account security | Use role-based access, rotate privileged credentials, and remove inactive accounts. |
| Configuration | Disable sample applications, unused protocols, and unnecessary server components. |
| Monitoring | Centralize logs and alert on suspicious deployments, authentication failures, and configuration changes. |
Regular vulnerability scanning, configuration audits, backup testing, and incident response drills should be scheduled rather than handled only after a public alert. Asset inventories must clearly identify Webversions, domain owners, internet exposure, business criticality, and patch status. This gives leadership and technical teams a reliable view of risk and helps ensure that future Oracle Critical Patch Updates can be tested and deployed quickly without disrupting essential services.
Frequently Asked Questions
Which Oracle WebLogic Server versions are affected by this vulnerability?
Affected versions depend on the specific Oracle security advisory tied to the PTA alert, so administrators should check their installed WebServer version against Oracle’s latest Critical Patch Update. Organizations running internet-facing, unpatched, or older WebLogic Server deployments should treat the risk as urgent until verified. If the server is no longer supported by Oracle, upgrading to a supported version should be prioritized.
Can this vulnerability be exploited remotely?
Critical WebServer vulnerabilities often involve remote exploitation, and in many cases attackers can target exposed services without needing direct access to the internal network. If the vulnerable component is reachable from the internet, the risk is much higher. Teams should immediately restrict external access while they validate exposure and apply patches.
Free tools Windows power users keep installed
One-click scans. No signup required.
What should organizations do first after the PTA alert?
The first step is to identify all WebServer instances, including production, staging, disaster recovery, and forgotten legacy systems. Next, check whether they are exposed to the internet and confirm their patch level against Oracle’s advisory. High-risk systems should be isolated, access-controlled, monitored for suspicious activity, and patched as soon as possible.
Is applying the Oracle patch enough to secure WebLogic Server?
Applying the official Oracle patch is the most direct fix, but it should be paired with hardening measures. Organizations should disable unused services, limit administrative console access, enforce strong authentication, and review firewall rules. Security teams should also inspect logs for signs of attempted exploitation before and after patching.
How can we tell if our WebLogic Server has already been targeted?
Review Webaccess logs, server logs, authentication events, and network traffic for unusual requests, unexpected file uploads, new user accounts, or abnormal outbound connections. Indicators may include requests to vulnerable endpoints, suspicious Java processes, or unexplained changes in application directories. If compromise is suspected, isolate the server, preserve evidence, rotate credentials, and begin incident response procedures.
Bottom Line
PTA’s urgent alert on the critical Oracle WebServer vulnerability is a clear warning for organizations running affected versions to act without delay. Exposed or unpatched servers could give attackers a path to compromise systems, disrupt services, steal data, or move deeper into enterprise networks.
The next step is straightforward: identify all Webinstances, apply Oracle’s latest security patches immediately, restrict unnecessary internet exposure, and monitor logs for suspicious activity. Organizations should also strengthen access controls and incident response readiness to reduce risk while patching and verification are completed.




