Criminals have exploited long-known weaknesses in the SS7 telecom signaling system to intercept one-time authentication codes and drain victims’ bank accounts, turning a largely theoretical security concern into a real-world theft method. The incident has renewed scrutiny of SMS-based two-factor authentication, which still depends on phone networks originally designed for carrier trust rather than modern account security.
SS7 attacks work by abusing the signaling messages carriers use to route calls, texts, and roaming services, allowing attackers with network access to redirect or monitor text messages without touching the victim’s phone. That makes SMS codes vulnerable when criminals already have login credentials, personal details, or banking information and need only the final verification step to complete an account takeover.
As an Amazon Associate I earn from qualifying purchases.
The risk is not limited to high-profile targets, though people with valuable financial accounts, reused passwords, or exposed personal data face greater danger. Reducing exposure requires action across the chain: users should move away from SMS where possible, banks should adopt stronger authentication and fraud detection, and telecom providers must tighten SS7 access, monitoring, and inter-carrier controls.
What Happened in the SS7 Exploitation Case
Criminals used weaknesses in Signaling System No. 7, the decades-old telecom protocol that helps mobile networks exchange call-routing and roaming information, to intercept one-time authentication codes sent by banks. With those codes, they were able to complete logins and authorize transfers from victims’ accounts, turning a flaw long discussed by security researchers into a practical financial crime. The incident drew attention because it did not rely on stealing a phone, tricking a user into revealing a code, or installing malware on the victim’s device. Instead, attackers abused trust between telecom networks.
#1 Best Overall

- Thick Plastic for Enhanced Strength: The single - layer thickness has been increased to 12 mils, twice the standard 6 - mil thickness. This card protector can fully protect cards and effectively resist cracks, tears, and bends.
- Perfect Fit for a Variety of Cards: With inner dimensions of 3.7" x 2.2", the plastic card sleeves matche various cards perfectly, including social security cards, new medical cards, business cards, credit cards, debit cards, driver's licenses, and ID cards. The thin - offset opening is ingeniously designed for easy insertion and removal of cards.
- Keep Cards in Original Condition: The plastic card holder protects your cards from wearing, tearing, and bending. Especially ensuring the safety and cleanliness of cards.
- High Transparency: Crystal clear PVC credit card cover, offers complete transparency for easy viewing. Your cards can be quickly and smoothly identified when passing through a scanner.
- Trim to Fit Your Wallet: Easily cut the edges to customize the size, making these plastic sleeves for cards fit almost all wallet slots (please measure your wallet slots size before buying refers to our medicare card protector size)
In a typical SS7-enabled theft, the attackers first obtain online banking credentials through phishing, credential stuffing, malware, or data breaches. Those usernames and passwords are not enough when a bank requires a second factor by text message. The attackers then use access to an SS7-connected telecom environment to reroute or copy SMS messages intended for the victim’s phone number. When the bank sends a one-time passcode, the code silently reaches the attacker as well, allowing the fraudulent transaction to proceed before the victim notices anything unusual.
The most concerning aspect is that the victim’s phone may continue to appear normal. Unlike a SIM-swap attack, where service often drops because the number has been moved to a different SIM card, SS7 interception can be less visible. The victim may still have signal, receive ordinary calls, and use mobile data while selected messages are redirected or monitored. That makes detection harder for consumers and for banks that treat possession of the phone number as strong evidence that the real customer is approving the action.
How the attack chain typically unfolds
- Credential theft: Criminals acquire the victim’s banking login details through phishing pages, malware, reused passwords, or leaked credential databases.
- Telecom network access: The attackers gain access to SS7 signaling capabilities, either through a compromised provider, a rogue service, or intermediaries with connectivity into global telecom networks.
- Message interception: SS7 commands are used to manipulate routing information so SMS verification codes can be observed or redirected.
- Account takeover: The criminals log in, request transfers, receive the bank’s SMS codes, and authorize payments.
- Money movement: Funds are quickly sent through mule accounts, prepaid instruments, cryptocurrency ramps, or other channels designed to complicate recovery.
The case renewed scrutiny of a known structural problem: SS7 was built for a smaller world of trusted telecom operators, not for today’s global web of carriers, roaming partners, virtual network operators, and signaling intermediaries. Its design assumes that network participants making routing requests are legitimate. When that assumption fails, attackers can query subscriber locations, redirect communications, or interfere with SMS delivery in ways that bypass protections on the user’s handset and the bank’s website.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →This does not mean every customer using SMS codes is immediately exposed to the same level of danger. Successful exploitation usually requires several pieces to come together: stolen account credentials, access to SS7 signaling, a bank that relies on SMS for transaction approval, and a path for moving stolen funds. Still, the incident showed that SMS-based two-factor authentication can be defeated without attacking the user directly. That is banks, telecom providers, regulators, and security teams are reassessing whether text messages should remain a default method for protecting high-value accounts.
How SS7 Vulnerabilities Enable Account Takeovers
SS7, short for Signaling System No. 7, is the decades-old set of telecom protocols that lets mobile networks exchange routing and billing information. It was built for a world in which telecom operators were trusted parties, not for an environment where attackers could gain access through compromised carriers, rogue intermediaries, or poorly secured signaling gateways. When criminals get that access, they can query or manipulate network data in ways that make a victim’s phone number temporarily work for the attacker rather than the legitimate subscriber.
In a typical account takeover scenario, the attacker already knows enough about the victim to target a bank, email account, cryptocurrency wallet, or payment service. That may include a username, password, phone number, or partial identity data obtained through phishing, malware, data breaches, or social engineering. The SS7 abuse then comes into play when the service sends a one-time authentication code by SMS. By abusing signaling messages, the attacker can cause texts or calls intended for the victim to be redirected, copied, or made visible through the attacker’s own equipment or service provider access.
How the interception chain usually works
- Initial credentials are obtained: criminals collect login details through phishing pages, credential stuffing, infostealer malware, or leaked databases.
- The target phone number is identified: the attacker links the account to the victim’s mobile number, often from breached profile data or previous fraud attempts.
- SS7 signaling is abused: malicious network requests are used to locate the subscriber, alter routing behavior, or intercept SMS delivery paths.
- The one-time code is captured: the authentication message sent by the bank or online service is delivered to, or observed by, the attacker.
- The account is accessed: the attacker enters the intercepted code, completes the login or transaction approval, and moves funds or changes account settings.
These attacks are powerful because they do not require stealing the victim’s physical phone. The handset may remain in the owner’s pocket, still showing normal service, while authentication messages are silently diverted elsewhere. In some cases the victim may notice brief service disruption, delayed messages, unexpected password reset alerts, or unauthorized banking activity. In other cases there may be no obvious sign until money has already left the account.
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallSS7-based account takeovers also differ from SIM swapping. In a SIM swap, criminals convince a carrier to move the victim’s number to a new SIM card or eSIM. With SS7 exploitation, the attacker abuses telecom signaling between networks, which can happen without changing the subscriber’s SIM record at the retail carrier level. Both approaches target the same weakness: many online services treat control of a phone number as proof of identity, even though phone numbers were not designed to be secure identity tokens.
The people most exposed are those whose high-value accounts depend on SMS codes, especially if their passwords have appeared in breaches or they are visible targets for fraud. Business executives, cryptocurrency holders, online banking customers, journalists, public officials, and anyone with large account balances or privileged access can be attractive targets. Risk also rises when banks allow SMS codes to approve new payees, reset passwords, or authorize large transfers without additional behavioral checks.
Rank #2

- 𝐏𝐫𝐨𝐝𝐮𝐜𝐭 𝐒𝐢𝐳𝐞:𝟑.𝟖𝐱𝟐.𝟑𝟐 𝐢𝐧
- 𝐄𝐚𝐬𝐲 𝐬𝐥𝐢𝐝𝐞 & 𝐍𝐨𝐧-𝐬𝐭𝐢𝐜𝐤: 𝐒𝐩𝐞𝐜𝐢𝐚𝐥 𝐨𝐩𝐞𝐧𝐢𝐧𝐠 𝐝𝐞𝐬𝐢𝐠𝐧 𝐜𝐚𝐧 𝐢𝐧𝐬𝐞𝐫𝐭 𝐚𝐧𝐝 𝐫𝐞𝐦𝐨𝐯𝐞 𝐲𝐨𝐮𝐫 𝐜𝐚𝐫𝐝 𝐞𝐚𝐬𝐢𝐥𝐲
- 𝐅𝐢𝐭 𝐟𝐨𝐫 𝐀𝐥𝐥 𝐒𝐢𝐳𝐞 𝐂𝐚𝐫𝐝𝐬:𝐍𝐞𝐰 𝐌𝐞𝐝𝐢𝐜𝐚𝐫𝐞 𝐂𝐚𝐫𝐝, 𝐒𝐨𝐜𝐢𝐚𝐥 𝐒𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐂𝐚𝐫𝐝, 𝐛𝐮𝐬𝐢𝐧𝐞𝐬𝐬 𝐜𝐚𝐫𝐝, 𝐜𝐫𝐞𝐝𝐢𝐭 𝐜𝐚𝐫𝐝
- 𝐃𝐮𝐫𝐚𝐛𝐥𝐞 𝐌𝐚𝐭𝐞𝐫𝐢𝐚𝐥𝐬:𝐦𝐚𝐝𝐞 𝐨𝐟 𝐰𝐚𝐭𝐞𝐫-𝐫𝐞𝐬𝐢𝐬𝐭𝐚𝐧𝐭 𝐚𝐧𝐝 𝐜𝐨𝐫𝐫𝐨𝐬𝐢𝐨𝐧-𝐫𝐞𝐬𝐢𝐬𝐭𝐚𝐧𝐭 𝐏𝐕𝐂 𝐜𝐚𝐫𝐝 𝐬𝐥𝐞𝐞𝐯𝐞𝐬
- 𝐒𝐨𝐜𝐢𝐚𝐥 𝐒𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐂𝐚𝐫𝐝 𝐏𝐫𝐨𝐭𝐞𝐜𝐭𝐨𝐫,𝐍𝐞𝐰 𝐌𝐞𝐝𝐢𝐜𝐚𝐫𝐞 𝐂𝐚𝐫𝐝 𝐇𝐨𝐥𝐝𝐞𝐫 𝐏𝐫𝐨𝐭𝐞𝐜𝐭𝐨𝐫 𝐒𝐥𝐞𝐞𝐯𝐞𝐬
For attackers, SS7 abuse is usually part of a broader fraud operation rather than a standalone trick. The telecom weakness opens the door, but successful theft often depends on account reconnaissance, weak password hygiene, reusable credentials, real-time phishing, and gaps in bank fraud monitoring. That combination is what makes the vulnerability so concerning: even a technically old flaw can become highly damaging when paired with modern credential theft and automated financial fraud tools.
Why SMS-Based 2FA Is Especially Exposed
SMS-based two-factor authentication depends on a fragile assumption: that possession of a phone number is the same as possession of the phone. SS7 attacks break that assumption. If an attacker can manipulate telecom signaling to redirect, copy, or observe text messages, the one-time code sent by a bank or payment service can be captured before the legitimate user ever sees it. The victim may still have the phone in hand, with normal signal bars and no obvious warning that authentication traffic is being intercepted.
This exposure is different from a typical phishing attack because the weakness sits below the app or website layer. A bank may have strong passwords, rate limits, fraud scoring, and encrypted web sessions, yet still rely on a six-digit SMS code that travels through carrier infrastructure designed decades ago for trusted telecom operators. SS7 was built to help networks route calls, deliver roaming services, and exchange subscriber information. It was not built for a world where access to signaling networks could be abused by criminal groups, gray-market intermediaries, or compromised telecom partners.
Where SMS 2FA breaks down
- Codes are sent over a shared telecom ecosystem: Messages can pass through multiple carriers, aggregators, and roaming partners, increasing the number of places where signaling abuse can occur.
- The code is tied to a number, not a device: If traffic for that number is redirected or duplicated, the authentication system may still treat the attacker as the rightful user.
- Users often receive no alert: Unlike a stolen password or suspicious login email, SS7 interception may leave no visible trace on the handset.
- SMS codes are easy to reuse in real time: Many banking and wallet logins allow short-lived codes that are valid long enough for an attacker to enter them during an active session.
The highest-risk targets are people with accounts that can move money quickly: online banking customers, cryptocurrency holders, executives with corporate payment authority, and users of services that allow password resets by SMS. Public figures and high-net-worth individuals face additional exposure because their phone numbers may be easier to discover through data broker records, leaked databases, business filings, or social media. Still, ordinary consumers are not immune. Criminal groups often automate credential stuffing using breached passwords, then use telecom attacks only for accounts that pass the first stage and appear valuable.
SMS authentication also creates a single point of failure across many services. The same phone number may be used to approve bank transfers, reset email passwords, access cloud storage, and recover social media accounts. Once attackers can intercept messages for that number, they may chain compromises: first reset email, then find financial alerts, then access banking or investment accounts. This makes SMS weaker than authentication methods that bind approval to a physical device, cryptographic key, or app-generated credential that does not travel through the carrier signaling network.
| Authentication method | Main exposure | Relative resilience to SS7 abuse |
|---|---|---|
| SMS code | Intercepted or redirected text messages | Low |
| Voice call code | Call forwarding or signaling interception | Low |
| Authenticator app | Device theft, malware, phishing of codes | Higher |
| Hardware security key or passkey | Loss of key or device, weak recovery process | Highest |
SMS 2FA is still better than relying on passwords alone, especially for low-risk accounts, but it should no longer be treated as a strong control for sensitive transactions. Its biggest weakness is that the user, the bank, and the app provider do not fully control the delivery path. When authentication depends on telecom routing that can be manipulated outside the customer’s view, criminals gain an opening that traditional account security tools may miss.
The Impact on Banks, Telecoms, and Consumers
The exploitation of SS7 weaknesses turns a telecom-layer flaw into a financial crime problem. Banks may see transactions that appear legitimate because the customer’s password was entered and the one-time SMS code was successfully supplied. Telecom providers may see no conventional SIM swap, malware infection, or stolen handset. Consumers, meanwhile, may only discover the attack after money has left their account and the usual fraud alerts have failed to stop it.
For banks, the immediate impact is higher fraud exposure in scenarios where SMS codes are treated as strong proof of customer presence. An attacker who already has online banking credentials can use SS7 interception to receive login or transaction approval codes without touching the victim’s phone. That makes fraud investigations harder: logs may show a correct password, a valid session, and a valid one-time passcode. Banks then have to decide whether to reimburse the customer, absorb the loss, challenge the telecom provider, or argue that the customer’s credentials were compromised first.
Telecoms face a different but equally serious problem: trust in the mobile network as an identity channel. SS7 was designed for cooperation between carriers, not for the threat model of modern online banking and mass account recovery. If hostile actors can gain access through rogue operators, compromised telecom partners, or poorly controlled signaling gateways, they can request routing information or redirect messages in ways that are difficult for customers to detect. This places pressure on carriers to monitor signaling traffic more aggressively and to treat SMS authentication abuse as a network security incident, not merely a banking issue.
Rank #3

- Standard Card Size: 3.8 x 2.32 in. fits most SSN and credit cards.
- Multi-Card Compatible: Fits Social Security cards, Medicare cards, driver's licenses, and credit cards.
- Durable PVC Material: Flexible yet sturdy sleeves help prevent bending and edge damage.
- Slim & Wallet Friendly: Compact 3.8 x 2.32 in. size fits easily into wallets and card holders without adding bulk.
- Clear & Protective: Transparent sleeves keep card details visible while protecting against scratches and wear.
Who faces the greatest exposure
- High-value banking customers: People with large balances, business accounts, crypto holdings, or access to corporate payment systems are more attractive targets.
- Customers whose passwords are already leaked: SS7 interception is often most damaging when combined with credential stuffing, phishing, or database breaches.
- Users dependent on SMS recovery: Accounts that allow password resets or transaction approval through text messages remain vulnerable even if the primary login is protected.
- Banks relying heavily on SMS OTPs: Institutions that have not adopted app-based approvals, hardware keys, behavioral controls, or transaction signing carry more residual risk.
- Telecom networks with weak signaling controls: Carriers that lack SS7 firewalls, anomaly detection, and strict partner filtering may become unwitting channels for attacks.
Consumers are affected not only by direct account losses but also by the difficulty of proving what happened. An SS7 attack leaves little evidence on the victim’s device: no suspicious app, no missing SIM card, and no obvious text message if the code is silently redirected or intercepted in transit. Victims may still have normal mobile service while attackers receive enough authentication data to approve transfers. This creates a stressful dispute process in which the customer must explain a network-level attack that most people have no way to observe.
Recommended Free Tools
The broader consequence is a shift in how organizations should evaluate authentication risk. SMS can still be better than using only a password, especially for low-risk services, but it should not be treated as a resilient control for high-value transactions. Banks need layered fraud detection, step-up verification, transaction-specific approvals, and rapid response paths for suspected telecom interception. Telecoms need stronger signaling security, tighter roaming partner oversight, and better cooperation with financial institutions. Consumers should move critical accounts away from SMS where stronger options are available and treat unexpected login alerts, failed calls, or account recovery messages as potential warning signs.
Safer Alternatives to SMS Authentication
Replacing SMS codes does not mean abandoning two-factor authentication; it means moving the second factor away from the telephone signaling network. SS7 attacks are powerful because the attacker does not need to steal the phone itself. If a one-time password can be rerouted, read, or suppressed inside the mobile network, the account login flow can be defeated even when the user has done nothing wrong. Stronger methods bind authentication to a device, a cryptographic key, or a verified app session instead of trusting that a text message reached the correct subscriber.
The strongest consumer option today is usually a passkey or hardware security key based on FIDO2/WebAuthn standards. These methods use public-key cryptography: the service stores a public key, while the private key remains on the user’s device or hardware token. A fraudster who intercepts traffic, steals a password, or controls a phone number still cannot complete the login without that private key. Passkeys also reduce phishing because they are tied to the legitimate website or app, so a fake banking page cannot easily replay the authentication response to the real service.
Common alternatives and where they fit
- Authenticator apps: Apps such as Google Authenticator, Microsoft Authenticator, Authy, and similar tools generate time-based codes locally on the device. They are not delivered over SS7, making them safer than SMS, though users still need protection against phishing and device compromise.
- Push approvals: Banking or identity apps can send an encrypted approval request to a registered device. Better implementations show transaction details, location, and amount, making it harder for criminals to trick users into approving the wrong action.
- Hardware security keys: USB, NFC, or Bluetooth keys provide very strong protection for high-value accounts, administrators, executives, and cryptocurrency users. They are resistant to SIM swapping, SS7 interception, and most phishing kits.
- Passkeys: Built into platforms such as iOS, Android, Windows, and macOS, passkeys offer strong security with less friction than carrying a separate token. They can be unlocked with biometrics or a device PIN.
- In-app transaction signing: For banks, the user should approve a specific payment inside the banking app, with the payee and amount cryptographically bound to the approval. This is safer than sending a generic SMS code that can authorize anything.
Banks and payment providers should treat SMS as a fallback rather than the primary defense for sensitive actions. Password resets, new-device enrollment, payee creation, large transfers, and changes to contact details deserve stronger checks than a texted code. Risk-based controls can help: if a login comes from a new device, a foreign network, or shortly after a SIM change, the bank can require an app-based approval, biometric confirmation, a security key, or manual review before allowing money movement.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Telecom providers still have a role, even when services move away from SMS authentication. They can reduce exposure by filtering suspicious SS7 traffic, monitoring abnormal routing requests, limiting access by roaming partners, and improving controls around SIM swaps and call forwarding. Users can also reduce their personal risk by enabling app-based 2FA wherever available, protecting email accounts with passkeys or security keys, setting a carrier account PIN, and avoiding SMS as the recovery method for financial accounts. SMS codes are better than passwords alone, but for banking and other high-value services, they should no longer be considered the safest available option.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What Organizations and Users Should Do Next
The practical response to SS7 abuse is not to abandon two-factor authentication altogether, but to stop treating SMS as a high-assurance channel. Banks, fintech firms, crypto platforms, email providers, and telecom operators should assume that text messages and voice calls can be redirected, delayed, or observed by attackers with access to telecom signaling networks. That assumption changes how account recovery, transaction approval, and fraud monitoring should be designed.
Actions for banks and online service providers
Organizations that still rely on SMS codes should reduce their role in the riskiest workflows. A one-time text code may be acceptable for low-risk sign-ins, but it should not be the only barrier before adding a new payee, changing a password, replacing a registered device, or approving a large transfer. Those events should require stronger checks, such as app-based push approval, hardware security keys, passkeys, biometric re-verification inside a trusted app, or a cooling-off period before sensitive changes take effect.
- Move customers toward phishing-resistant authentication: Support FIDO2 security keys and passkeys for account login, especially for high-value accounts and business users.
- Limit SMS to backup status: Treat text codes as a fallback option, not the default or highest-trust method.
- Harden account recovery: Do not allow a phone number alone to reset passwords, disable stronger factors, or enroll a new device.
- Use risk-based controls: Flag logins involving new devices, unusual locations, recent SIM changes, number porting, or sudden changes to contact details.
- Monitor transaction patterns: Add step-up verification for large transfers, new beneficiaries, rapid withdrawals, or behavior that differs from the customer’s normal activity.
Actions for telecom providers
Telecom carriers have a direct role because SS7 weaknesses sit inside the signaling infrastructure that routes calls and messages between networks. Providers should deploy SS7 firewalls, filter suspicious signaling requests, monitor abnormal location-update activity, and restrict access from roaming partners or intermediaries that do not meet security standards. They should also tighten number-porting and SIM-swap procedures, since criminals often combine telecom redirection with social engineering to take control of a victim’s mobile identity.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Fix the driver behind crashes, sound loss and screen glitches3Clear out junk files and repair common Windows errorsRank #4
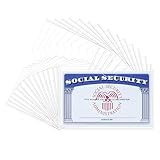
- Durable PVC Material:Made from high-quality PVC, these card protectors are waterproof, corrosion-resistant, and flexible, offering long-lasting protection against damage, dust, water, wear, and dirt to keep your cards in pristine condition.
- Crystal-Clear Visibility:Both sides of the protector are crystal-clear, allowing for easy visibility and scanning without removing the card. Dual-sided transparency also lets you store cards back-to-back for maximum storage efficiency.
- Convenient Slim Design:Features a thin, offset opening that ensures easy insertion and removal of cards while preventing accidental slips, making daily use hassle-free.
- Universal Fit: Measuring 3.82" x 2.32", these protectors fit cards up to 3.6" x 2.2". Ideal for Social Security cards, Medicare cards, credit cards, driver’s licenses, ID cards, business cards, membership cards, and more.
- Value Pack of 15 for Sharing: Includes 15 card protectors, providing enough for daily use or sharing with family and friends.
Carriers should give banks and major online platforms timely risk signals when a customer’s number has been recently ported, replaced, or associated with unusual routing events. These signals can help a bank decide whether to delay a payment, require stronger authentication, or contact the customer through an in-app secure message instead of relying on the same compromised phone channel. Better cooperation between telecoms and financial institutions can reduce the window in which attackers can drain accounts.
Actions for individual users
Users cannot patch SS7 themselves, but they can reduce how much of their digital life depends on a phone number. The strongest step is to enable passkeys, authenticator apps, or hardware security keys wherever they are available, starting with email, banking, investment, cloud storage, and password manager accounts. Email deserves special attention because it is often the recovery path for other services; if an attacker takes over email, many other accounts become easier to compromise.
- Replace SMS codes where possible: Use an authenticator app, passkey, or hardware key instead of text-message verification.
- Protect mobile account changes: Ask your carrier for a port-out PIN, account password, or number-transfer lock if available.
- Remove phone-based recovery: For critical accounts, disable SMS recovery options when stronger alternatives exist.
- Watch for warning signs: Unexpected loss of signal, messages about number changes, unknown login alerts, or unrequested verification codes should be treated as urgent.
- Set transaction alerts: Enable real-time notifications for bank transfers, card payments, password changes, and new device enrollments.
If suspicious activity appears, users should contact their bank and mobile provider immediately, freeze affected accounts where possible, revoke unknown sessions, change passwords from a trusted device, and move authentication away from SMS. The best defense is layered: stronger authentication, safer recovery processes, telecom-level filtering, and fraud systems that do not trust possession of a phone number as proof of identity.
Frequently Asked Questions
Can criminals really steal my SMS two-factor authentication codes through SS7?
Yes, if they can gain access to SS7 signaling networks or work through someone who has that access, they may be able to redirect or monitor text messages sent to your phone number. That can include one-time banking codes, password reset links, and login verification messages. These attacks are not usually random; they are more likely to target valuable accounts or people already identified through phishing, data leaks, or financial surveillance.
Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Repair Windows errors before they cause bigger problemsFix Now →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Does this mean SMS two-factor authentication is useless?
SMS-based 2FA is still better than using only a password, especially against basic credential theft. However, it is weaker than app-based authenticators, hardware security keys, or passkeys because phone numbers can be hijacked through SS7 abuse, SIM swapping, number porting fraud, or carrier account compromise. If a service offers a stronger method, you should switch away from SMS for accounts such as banking, email, crypto, and cloud storage.
How would I know if my phone number or bank account was targeted through SS7?
You may not see an obvious warning on your phone, because SS7 interception can happen inside telecom routing systems without changing your handset. Possible signs include unexpected login alerts, missing verification texts, sudden loss of mobile service, bank notifications you did not trigger, or transactions you do not recognize. If any of these occur, contact your bank and mobile carrier immediately, change passwords from a trusted device, and revoke active sessions on affected accounts.
What should I use instead of SMS codes for banking and other sensitive accounts?
Use a hardware security key, passkey, or authenticator app where available, because these do not rely on the phone network to deliver login codes. For banking, also enable transaction alerts, set transfer limits, and use the bank’s official app-based approval feature if it supports device binding or cryptographic confirmation. Avoid email and SMS as recovery methods when stronger recovery options are available.
What should banks and telecom providers do to reduce SS7-related fraud?
Banks should treat SMS codes as a lower-assurance method and add risk checks such as device fingerprinting, behavioral monitoring, transaction signing, and step-up authentication for large transfers. Telecom providers should filter suspicious SS7 traffic, monitor abnormal routing requests, restrict access to signaling networks, and strengthen number-porting and SIM-swap controls. Both industries need faster fraud reporting channels so suspicious authentication activity can be investigated before accounts are drained.
Free tools Windows power users keep installed
One-click scans. No signup required.
Bottom Line
SS7 abuse turns a long-known telecom weakness into a direct threat to accounts that still rely on SMS codes for protection. While most people are unlikely to be individually targeted, anyone with high-value financial, business, or crypto accounts should treat SMS-based 2FA as a fallback—not a primary defense.
The clearest next step is to move accounts to stronger authentication, such as app-based codes, passkeys, or hardware security keys, while asking banks and providers to offer safer options and monitor suspicious telecom activity. Telecom operators also need to keep tightening SS7 access, because account security is only as strong as the networks delivering those one-time codes.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




