Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →A privacy policy is more than a legal formality. It is a clear statement that tells users what personal data your website or app collects, how that data is used, who it may be shared with, how it is protected, and what choices users have.
Writing one well helps build trust, reduce confusion, and support compliance with privacy laws such as the GDPR, CCPA, and other data protection rules that may apply to your business. A strong policy should be accurate, easy to understand, simple to find, and kept current as your products, services, and data practices change.
As an Amazon Associate I earn from qualifying purchases.
These seven s cover the essentials of creating a privacy policy that is both practical and user-friendly, from identifying legal requirements to explaining user rights and making the policy accessible on your website or app.
What a Privacy Policy Is and Why You Need One
A privacy policy is a public statement that explains how your website, app, or business handles personal data. It tells users what information you collect, how you collect it, you use it, who you share it with, how long you keep it, and what choices users have. Personal data can include obvious details such as names, email addresses, phone numbers, billing addresses, and payment-related information, as well as less obvious data such as IP addresses, device identifiers, cookie IDs, location data, browsing activity, and analytics events.
#1 Best Overall

- You will receive 200 prerolled filter tips
- diameter : 6,5mm / length : 18mm
- Made of All Natural, Chemical and Chlorine Free Fibers
- Vegan Friendly
- Windmill powered product
You need a privacy policy because users are entitled to understand what happens to their information before they decide to create an account, submit a form, make a purchase, install an app, or accept cookies. A clear policy builds trust by showing that data is not being collected silently or used in unexpected ways. For example, if you collect email addresses for order confirmations, your policy should say so. If you also use those email addresses for marketing, referral tracking, abandoned cart reminders, or customer profiling, that should be explained separately and clearly.
A privacy policy is also a legal requirement for many businesses. Laws such as the GDPR in the European Union and United Kingdom, the CCPA/CPRA in California, and other privacy laws around the world require organizations to provide specific disclosures about data collection and user rights. Even if your business is small, you may still be covered if you serve users in regulated regions, use third-party analytics or advertising tools, collect leads, run an ecommerce store, or operate a mobile app. App stores, payment processors, advertising networks, and SaaS platforms may also require you to publish a privacy policy before using their services.
What a privacy policy typically covers
- Categories of personal data collected: such as contact details, account information, transaction data, usage data, cookies, and device information.
- Purposes for using data: such as providing services, processing payments, improving the product, sending support messages, preventing fraud, or delivering marketing.
- Data sharing: including service providers, hosting companies, payment processors, analytics tools, advertising partners, affiliates, or legal authorities.
- Data protection measures: such as access controls, encryption, secure hosting, staff training, and retention limits.
- User rights and choices: such as accessing, correcting, deleting, exporting, or objecting to certain uses of personal data.
Without a privacy policy, your business may face compliance risks, rejected app submissions, suspended advertising accounts, loss of customer confidence, or complaints from users and regulators. More practically, the process of writing one forces you to map your data practices. You may discover old email lists, unnecessary form fields, unused tracking scripts, or third-party tools that collect more information than you expected. That makes the policy more than a legal document; it becomes a useful checkpoint for better data governance.
A strong privacy policy should match what your business actually does. Copying a generic template can create problems if it promises rights you cannot support, omits tools you use, or describes security practices you have not implemented. The goal is to give users an accurate, easy-to-understand of your data practices while meeting the legal standards that apply to your business. From there, you can refine the details by identifying the privacy laws that apply and listing each type of personal data you collect.
Identify the Privacy Laws That Apply to Your Business
Before drafting the details of your privacy policy, identify which privacy laws apply to your business. Privacy obligations are usually based on where your users live, what type of data you collect, how your business operates, and whether you meet certain size or revenue thresholds. A small online store, SaaS platform, mobile app, health-related service, or children’s website may each face different requirements, even if they collect similar information such as names, email addresses, payment details, or device identifiers.
Start by mapping the locations of your customers, website visitors, app users, employees, and contractors. Many privacy laws apply based on the user’s location rather than the company’s headquarters. For example, the General Data Protection Regulation applies when you offer goods or services to people in the European Economic Area or monitor their behavior. The UK GDPR and Data Protection Act apply in similar ways for people in the United Kingdom. In the United States, state privacy laws such as the California Consumer Privacy Act, as amended by the CPRA, may apply if you meet certain thresholds involving revenue, consumer data volume, or data sales and sharing.
Common privacy laws to check
- GDPR: Applies to many businesses that collect or use personal data from people in the EU or EEA, including through websites, apps, analytics, advertising, and online sales.
- UK GDPR: Covers personal data relating to people in the United Kingdom and often requires similar disclosures to the EU GDPR.
- CCPA/CPRA: Applies to certain businesses handling California residents’ personal information and includes rights to know, delete, correct, opt out of sale or sharing, and limit use of sensitive personal information.
- Other U.S. state privacy laws: States such as Virginia, Colorado, Connecticut, Utah, Texas, Oregon, and others have consumer privacy laws with notice, rights request, and data processing requirements.
- COPPA: Applies in the United States when an online service collects personal information from children under 13, or is directed to them.
- HIPAA: Applies to covered entities and business associates handling protected health information in the United States.
- PIPEDA and provincial laws: Apply to many private-sector organizations handling personal information in Canada.
Once you know the relevant laws, translate their requirements into specific sections of your privacy policy. Some laws require you to disclose the categories of personal data collected, the purposes for collection, categories of third parties that receive data, retention periods, user rights, contact details, and complaint procedures. Others require additional wording around cookies, targeted advertising, automated decision-making, sensitive data, international transfers, or children’s privacy.
It also helps to create a simple compliance checklist before writing. Include the jurisdictions you serve, the data you collect, the legal basis or business purpose for using it, whether you sell or share data for advertising, whether you process sensitive data, and how users can exercise their rights. If your business operates across mulle regions, write your privacy policy broadly enough to cover all applicable rules, then add region-specific sections where needed. For higher-risk data uses or regulated industries, consult a privacy professional or attorney so your policy accurately reflects your legal duties and actual practices.
Rank #2

- Q-Tips Cotton Swabs are the ultimate home, hygiene, and beauty tool.
- The soft cotton buds on Q-tips Cotton Swabs are made with 100% cotton, and the paper sticks are sourced from sustainable forests.
- Use a Q-tip Cotton Swab as an ear cleaner (the cotton pads make perfect ear swabs) or as a beauty tool.
- The soft cotton sticks are delicate enough for sensitive jobs like baby hygiene; use a Q-tip to clean around your newborn's belly button or around your baby's nose.
- Q-tips cotton swabs are also great for cleaning electronics; the cotton tipped applicators are perfect for dusting between the keys on computer keyboards or cleaning out phone ports.
List the Personal Data You Collect and Why
A strong privacy policy should clearly state what personal data your website, app, or business collects and the purpose for collecting it. Users should be able to understand, at a glance, whether you collect basic contact details, account information, payment data, device identifiers, location data, analytics data, or information submitted through forms. Avoid vague wording like “we may collect information” without explaining what that information includes.
Start by auditing every point where your business receives data. This includes account registration pages, checkout forms, newsletter signups, contact forms, cookies, analytics tools, customer support chats, mobile app permissions, advertising pixels, and third-party integrations. For each category of data, connect it to a specific purpose. For example, an email address may be used to create an account, send order confirmations, provide customer support, or deliver marketing messages if the user has opted in.
| Type of personal data | Examples | Common purpose |
|---|---|---|
| Contact information | Name, email address, phone number, mailing address | Account setup, order delivery, customer support, service messages |
| Payment information | Billing address, card details, transaction records | Processing purchases, refunds, fraud prevention, accounting |
| Account information | Username, password, preferences, saved settings | Providing access, personalizing the service, maintaining security |
| Technical data | IP address, browser type, device ID, operating system | Website functionality, security monitoring, analytics, troubleshooting |
| Usage data | Pages viewed, clicks, session duration, app activity | Improving content, measuring performance, understanding user behavior |
| Marketing data | Email preferences, campaign interactions, cookie identifiers | Sending promotions, measuring ad performance, managing consent |
Be especially clear about sensitive personal data if you collect it. This can include health information, biometric data, precise location data, government identification numbers, financial details, information about children, or data revealing race, religion, political views, or sexual orientation. Many privacy laws treat these categories differently and may require explicit consent, stronger security measures, or a separate of how and why the data is used.
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallYour policy should also distinguish between data users provide directly and data collected automatically. A user may knowingly enter their name and address during checkout, but they may not realize your site also collects IP addresses, cookie IDs, referral URLs, or device information. Explaining both types of collection helps build trust and reduces the risk that your policy appears incomplete or misleading.
- Be specific: say “email address and shipping address” instead of “contact details” where possible.
- Match each data type to a purpose: explain whether the data supports account access, payments, security, analytics, marketing, legal compliance, or service improvement.
- Separate optional from required data: tell users which information is needed to provide the service and which is voluntary.
- Include data from third-party tools: cover analytics platforms, payment processors, CRM tools, advertising networks, plugins, and embedded content.
- Review forms and permissions: if a field, cookie, or app permission is not needed, consider removing it rather than disclosing unnecessary collection.
Collecting less data is often easier to explain and easier to protect. If you cannot identify a clear business or legal purpose for a category of information, it may not belong in your product or your privacy policy. A practical privacy policy should reflect your real data practices, not a generic template that lists every possible type of data.
Explain How Data Is Stored, Shared, and Protected
After you describe what personal data you collect and , explain what happens to that data behind the scenes. Users should be able to understand where their information goes, who can access it, how long it may be kept, and what safeguards you use to reduce the risk of misuse, loss, or unauthorized access. This section of your privacy policy should be specific enough to build trust without exposing sensitive security details that could weaken your systems.
Describe where and how data is stored
State whether personal data is stored on your own servers, with cloud hosting providers, in customer relationship management tools, payment platforms, analytics services, email marketing systems, or other business software. If data may be stored or processed in other countries, say so clearly, especially if privacy laws require disclosures about international transfers. You do not need to name every server location, but users should know if their data may leave their country or region.
Free tools Windows power users keep installed
One-click scans. No signup required.
You should also explain your retention practices. Avoid vague statements such as “we keep data as long as necessary” unless you also explain what that means in practice. For example, you might keep account data while an account remains active, transaction records for tax and accounting purposes, support messages for a set period after a case is closed, or marketing preferences until the user unsubscribes. If exact timeframes vary, describe the criteria you use to decide when data is deleted or anonymized.
Rank #3

- Upgrade 3xl Nail Tips No C Curve: We have upgraded this newest flat Non c curve nails based on the feedback about the old basic c curve nail tips. Now it's very natural easy to shape, stick to the nail instantly, saves so much time for shaping and glue on. We had try our best to solve the problem of "the nail tip is too curve and thick, its very hard to glue to natural nail"
- Newest Extra Long Sizes: We improved this long nail tips not only on shape but also on sizes. The longest size is 2.17inch in length for size 0 and shortest lenght 1.85inch for size 11. It's much longer than other nail tips on the market. And there are 12 different sizes are pre-numbered 0-11 individually which that you can choose the suitable size conveniently, you also can shape it and cut the length easily according to your needs
- High Quality ABS Material: The large quantity of 504pcs half cover acrylic nail tips are made with environmental friendly high quality ABS material, which is thick and sturdy enough to last about 2-3 weeks. What's more, it's no toxic, no smell, no harm to your nails, providing you a safe and comfortable manicure experience
- Try Different Shape: 3xl nail tips have a certain length and shape, you can make many different types of false nails by trimming and polishing, like xxl coffin ballerina nails, long french nails, long stiletto false nails, middle length ballerina tips. Just try all the types as you like feel free
- Multiple Uses: Our no c curve nail tips are great for both professional nail artist and nail art beginner, suitable for nail salons and DIY nail art at home, also it's a great gift for your wife, girlfriend, mother or sisters on Christmas/ThanksGiving/New Year/Parties/Wedding/Costume ball/Halloween/etc
Explain when data is shared
Your privacy policy should identify the categories of third parties that receive or process personal data. These may include payment processors, hosting providers, delivery companies, customer support tools, analytics providers, advertising partners, professional advisers, fraud prevention services, or legal authorities. For each category, explain the purpose of the sharing. For example, payment details may be shared with a payment processor to complete a purchase, while an email address may be shared with an email service provider to send account notices or newsletters.
- Service providers: companies that process data for business operations, such as hosting, payments, email, analytics, or support.
- Business partners: organizations involved in delivering a joint service, promotion, integration, or requested feature.
- Legal and safety disclosures: regulators, courts, law enforcement, or other parties when required to comply with law or protect rights and security.
- Business transfers: potential buyers, investors, or advisers if your company is involved in a merger, acquisition, financing, or sale of assets.
Summarize your security measures
Users want reassurance that you take reasonable steps to protect their information. Mention practical safeguards such as encryption in transit, access controls, password protection, staff confidentiality measures, secure backups, vendor due diligence, monitoring, and internal policies for handling personal data. Keep this section accurate and measured: do not promise absolute security, because no system can be guaranteed to be completely secure.
A strong privacy policy also explains what users can do to help protect their accounts, such as choosing strong passwords, keeping login details confidential, and contacting you if they suspect unauthorized access. If your website or app handles sensitive personal data, financial information, children’s data, or health-related information, your storage, sharing, and protection disclosures should be especially clear and aligned with the legal requirements that apply to those categories.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Scan for outdated or missing drivers - takes under a minute3Clear out junk files and repair common Windows errorsClearly Describe User Rights and Choices
A strong privacy policy should tell people not only what you do with their data, but also what they can do about it. This section should clearly explain the rights users may have under applicable privacy laws, such as the GDPR, UK GDPR, CCPA/CPRA, or other regional rules. Even if not every right applies to every user, your policy should make it easy for people to understand their options and how to exercise them.
Common privacy rights include the right to access personal data, correct inaccurate information, delete data, restrict or object to certain processing, and request a copy of data in a portable format. If your business sells personal information, shares it for cross-context behavioral advertising, uses targeted advertising, or makes automated decisions with legal or significant effects, you may need to describe additional opt-out rights. Be specific about what users can request and avoid vague statements such as “you may have certain rights.”
Rights to include where applicable
- Access: Users can ask what personal data you hold about them and receive a copy of it.
- Correction: Users can request changes if their information is incomplete or inaccurate.
- Deletion: Users can ask you to delete their personal data, subject to legal or operational exceptions.
- Objection or restriction: Users can object to certain uses of their data or ask you to limit processing.
- Data portability: Users can request their data in a structured, commonly used format.
- Marketing choices: Users can unsubscribe from promotional emails, SMS messages, or push notifications.
- Cookie and tracking choices: Users can manage analytics, advertising, and similar tracking technologies.
Your policy should also explain the process for submitting a privacy request. Provide a dedicated email address, web form, account setting, or postal address, depending on how your business operates. State whether users need to verify their identity before you respond, what information they may need to provide, and whether an authorized agent can act on their behalf. If you are subject to laws with response deadlines, mention the general timeframe, such as responding within 30 or 45 days, while allowing for extensions where permitted by law.
Be clear about choices that users can manage without making a formal request. For example, explain how they can update account details, change communication preferences, opt out of marketing emails using an unsubscribe link, adjust cookie settings through a consent banner, or disable certain app permissions in their device settings. If refusing or withdrawing consent affects the service, describe that impact in practical terms, such as being unable to receive location-based features or personalized recommendations.
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Finally, describe any appeal or complaint options required by law. Some privacy laws require businesses to let users appeal a denied request, while others give users the right to contact a supervisory authority or regulator. Your privacy policy should name the relevant contact point within your organization and, where appropriate, refer users to the regulator that handles privacy complaints in their region. This helps show that your business takes privacy requests seriously and gives users a clear path to control their personal information.
Use Plain Language and Make the Policy Easy to Find
A privacy policy is only useful if people can understand it and access it before or when they share their personal data. Dense legal wording, vague descriptions, or hidden links can undermine trust and may also create compliance issues under laws that require clear notice. Write for a typical customer, app user, newsletter subscriber, or website visitor—not only for lawyers or regulators.
Rank #4
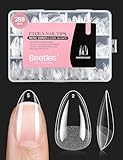
- Salon-Quality Nails Tips At Home: Get effortless salon-looking nails without expensive appointments. Beetles soft gel nail tips feature a natural almond shape with a seamless cuticle fit for elegant, everyday manicures that look professionally done. Lightweight, flexible, and comfortable for daily wear.
- Pre-Etched Design For Stronger Adhesion & Less Lifting: Our Etch-X pre-etched inner texture creates better grip with nail glue gel, helping reduce lifting and improving long-lasting retention. No extra filing inside the tips needed - perfect for beginners who want faster, easier, and more reliable application.
- Comfort Fit Soft Gel For Natural Feel: Made from soft soak-off gel material that feels lighter and more natural than traditional acrylic tips. The flexible structure fits comfortably on natural nails with less pressure, making them ideal for typing, work, daily activities, and long wear.
- Long-Lasting Wear Up To 28+ Days: Designed for durable everyday wear with proper prep and application. These short almond gel tips resist cracking, chipping, and breakage while maintaining a clean salon finish for weeks. Great for DIY nail extensions, gel polish, French nails, and minimalist nail looks.
- 288pcs In 12 Sizes: Beginner Friendly & Easy To Use: Includes 288 short almond nail tips in 12 inclusive sizes for easier matching across different nail beds. Pre-shaped and ready to apply with minimal filing required, helping you create beautiful manicures faster whether you're a beginner or experienced nail lover.
Use direct language that explains what happens in practical terms. For example, instead of saying, “We may process identifiers for legitimate commercial purposes,” say, “We use your name and email address to create your account, send order updates, and respond to support requests.” Replace broad phrases such as “improve our services” with concrete examples, such as analyzing feature usage, fixing bugs, personalizing content, or measuring ad performance.
Make the wording clear and scannable
Organize the policy with headings that match the questions users are likely to have: what data you collect, how you collect it, you use it, who you share it with, how long you keep it, and how users can exercise their rights. Short sections, bullet points, and tables can make complex information easier to review, especially on mobile screens.
Recommended Free Tools
- Use common terms: Say “personal information” or “personal data” and define any technical terms, such as cookies, analytics tools, or advertising identifiers.
- Be specific: Name the categories of data collected, such as contact details, payment information, location data, device data, or support messages.
- Avoid overbroad claims: Do not say you “never share data” if you use payment processors, hosting providers, analytics services, or email platforms.
- Use consistent wording: If you call your company “we” at the beginning, keep using “we” throughout the policy.
- Write for mobile users: Keep paragraphs short and make links easy to tap.
Placement matters as much as wording. Add a visible “Privacy Policy” link in your website footer, account sign-up pages, checkout pages, contact forms, newsletter forms, and anywhere users submit personal data. In an app, include it in the app store listing where available, on the sign-up screen, in account settings, and in any consent or permission flow that involves personal data.
Show the policy at the right moment
Users should not have to search for your privacy policy after data collection has already happened. If you collect email addresses for marketing, place a link near the subscription box. If you collect precise location data, provide a clear notice before enabling the feature. If you use cookies or similar technologies, connect your cookie banner or preference center to the relevant privacy and cookie disclosures.
| Location | Good practice |
|---|---|
| Website footer | Add a persistent link labeled “Privacy Policy” on every page. |
| Sign-up or checkout | Link to the policy before the user creates an account or completes a purchase. |
| Mobile app settings | Include the policy under privacy, legal, or account settings. |
| Marketing forms | Explain that the email address will be used for marketing and link to unsubscribe details. |
Finally, make sure the link works across devices, does not require a login, and opens in a readable format. A privacy policy hidden behind an account wall, broken link, PDF that is hard to read on mobile, or vague “Legal” menu can frustrate users and weaken your privacy notice. A clear, visible, and accessible policy helps users make informed choices and shows that privacy is part of your product experience, not an afterthought.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Keep Your Privacy Policy Updated as Your Business Changes
A privacy policy should not be treated as a one-time document. As your website, app, products, vendors, analytics tools, advertising practices, or customer workflows change, your privacy policy may need to change too. An outdated policy can mislead users, create compliance gaps, and expose your business to regulatory complaints if it no longer reflects how personal data is actually collected, used, stored, shared, or deleted.
Review your privacy policy whenever you introduce a new feature that affects personal data. For example, if you add account registration, live chat, SMS marketing, payment processing, location-based services, AI-powered recommendations, or a customer support portal, your data practices may change. You may begin collecting new categories of information, using data for new purposes, sharing it with new service providers, or retaining it for different periods. Each of these changes should be reflected clearly in the policy before or at the time the feature goes live.
Set a regular review schedule
In addition to reviewing the policy after major business changes, set a routine schedule for checking it. Many businesses review their privacy policy at least once a year, while companies operating in highly regulated industries or mulle jurisdictions may need more frequent reviews. A scheduled review helps you catch changes that happen gradually, such as switching email marketing platforms, adding analytics tags, changing hosting providers, or expanding into new regions with different privacy requirements.
- Check data collection points: Review forms, checkout pages, cookies, tracking pixels, app permissions, newsletter signups, and customer service channels.
- Review third-party vendors: Confirm which processors, plugins, payment providers, advertising networks, and analytics services receive personal data.
- Confirm legal requirements: Reassess whether laws such as the GDPR, CCPA/CPRA, UK GDPR, PIPEDA, or other regional rules apply as your audience grows.
- Verify user rights processes: Make sure users can still access, delete, correct, opt out, or withdraw consent as described in the policy.
- Update contact details: Ensure your privacy contact, mailing address, data protection officer details, or request forms are accurate.
When you make material changes, tell users in a clear and timely way. Material changes may include using personal data for a new purpose, sharing data with new categories of third parties, changing how long data is kept, introducing targeted advertising, or expanding the types of sensitive data collected. Depending on the laws that apply and the nature of the change, you may need to provide advance notice, request renewed consent, or give users a new opportunity to opt out.
Best Value

- Upgrade xxxl Nail Tips No C Curve- We have upgraded this newest flat Non c curve nails based on the feedback about the old basic c curve nail tips. Now it's very natural easy to shape, stick to the nail instantly, saves so much time for shaping and glue on. We had try our best to solve the problem of "the nail tip is too curve and thick, its very hard to glue to natural nail"
- Newest Extra Long Sizes- We improved this long nail tips not only on shape but also on sizes. The longest size is 2.17inch in length for size 0 and shortest lenght 1.85inch for size 11. It's much longer than other nail tips on the market. And there are 12 different sizes are pre-numbered 0-11 individually which that you can choose the suitable size conveniently, you also can shape it and cut the length easily according to your needs
- High Quality ABS Material- The large quantity of 504pcs half cover acrylic nail tips are made with environmental friendly high quality ABS material, which is thick and sturdy enough to last about 2-3 weeks. What's more, it's no toxic, no smell, no harm to your nails, providing you a safe and comfortable manicure experience
- Try Different Shape- 3xl nail tips have a certain length and shape, you can make many different types of false nails by trimming and polishing, like xxl coffin ballerina nails, long french nails, long stiletto false nails, middle length ballerina tips. Just try all the types as you like feel free
- Multiple Uses- Our no c curve nail tips nail tips are great for both professional nail artist and nail art beginner, suitable for nail salons and DIY nail art at home, also it's a great gift for your wife, girlfriend, mother or sisters on Christmas/ThanksGiving/New Year/Parties/Wedding/Costume ball/Halloween/etc
It is also useful to maintain version control for your privacy policy. Add an “effective date” or “last updated” date near the top of the policy so users can see when it was revised. Keep internal records of previous versions, what changed, who approved the update, and when it was published. This creates a clear audit trail and helps your team respond consistently if a user, regulator, partner, or platform asks about your privacy practices at a specific point in time.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Finally, make privacy policy updates part of your launch process. Before releasing a new website feature, mobile app update, marketing campaign, integration, or data-sharing arrangement, include a privacy review in your checklist. This ensures your policy stays aligned with your real practices and that privacy is considered before personal data starts moving through a new system. A current, accurate policy builds trust because users can rely on it to understand what is happening with their information today, not what your business did several years ago.
Frequently Asked Questions
Can I write my own privacy policy, or do I need a lawyer?
You can write your own privacy policy if your data practices are simple and you understand which privacy laws apply to your business. However, if you collect sensitive data, operate internationally, use complex advertising tools, or share data with many vendors, it is wise to have a privacy lawyer review it.
What should a privacy policy include?
A privacy policy should explain what personal data you collect, you collect it, how you use it, who you share it with, how long you keep it, and how you protect it. It should also describe users’ rights, how they can contact you, and when the policy was last updated.
Where should I put my privacy policy on my website or app?
Place your privacy policy somewhere users can easily find it, such as your website footer, account sign-up pages, checkout pages, and any forms where personal data is collected. In an app, include it in the settings, account, or legal section, and link to it before users create an account or submit personal information.
How often should I update my privacy policy?
Update your privacy policy whenever your business changes how it collects, uses, stores, or shares personal data. You should also review it regularly when you add new analytics tools, advertising platforms, payment providers, third-party integrations, or expand into new regions with different privacy laws.
Do small businesses really need a privacy policy?
Yes, most small businesses need a privacy policy if they collect personal data such as names, email addresses, phone numbers, payment details, IP addresses, or cookie data. Many privacy laws require one, and platforms like app stores, payment processors, and advertising networks often require a privacy policy before you can use their services.
Bottom Line
A strong privacy policy is more than a legal checkbox: it is a clear promise to users about how their personal data is collected, used, protected, shared, and controlled. By focusing on accuracy, plain language, applicable legal requirements, regular updates, and easy access on your website or app, you can build trust while reducing compliance risk.
Your next step is to review your current data practices, match them against the laws that apply to your audience, and turn that information into a policy users can actually understand. If your business handles sensitive data or operates across mulle regions, consider getting legal guidance before publishing or updating your policy.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




