Protect customer data in messaging apps by controlling the full path it takes: what customers send, where messages and copies are stored, who can see them, how long they are kept, and what happens if an account or device is compromised. Encryption helps, but it does not by itself protect an unlocked phone, an exported chat, a cloud backup, or a connected support system.
For a small business, a practical program starts with collecting less, restricting access, securing staff devices and accounts, setting retention rules, and preparing for incidents. The safeguards should match the sensitivity of the information and the laws that apply to your business.


Map the customer-data journey before changing settings
Start by tracing a customer message from the moment it arrives until every copy is deleted. A conversation may appear in more places than the original chat: on an employee’s phone, a linked computer, a shared inbox, a CRM or help desk, an export, or a backup. Include service providers and employee-owned devices in the map.
| Stage | Questions to answer | What to record |
|---|---|---|
| Collection | What information do staff request or customers send? Is every field needed to resolve the issue? | Types of customer information in messages, attachments, and forms |
| Access | Which staff accounts, linked devices, and administrators can view conversations? | People and systems with access, including how access is granted and removed |
| Storage and sharing | Does the provider store messages? Are there cloud backups, exports, or integrations that receive copies? | Storage locations, connected services, backup arrangements, and relevant provider access |
| Retention and deletion | How long does the business need each record? What happens to copies in exports, backups, and connected systems? | Retention reason, deletion method, and responsibility for carrying it out |
| Incident handling | Who acts if an account is taken over or a device is lost? How will service continue? | Response owner, containment steps, evidence handling, and customer-notification decision process |
This inventory should cover both the messaging service and the devices and systems around it. The FTC’s business guidance organizes a security program around taking stock, scaling down, locking information, disposing of what is no longer needed, and planning ahead.
Recommended Free Tools
#1 Best Overall
Collect less and avoid unnecessary sensitive details
The simplest way to reduce exposure is not to collect information the business does not need. Ask only for the details required to identify the issue and provide support. If a customer sends extra personal information, avoid copying it into additional systems unless there is a defined business need.
- Do not ask customers to send payment credentials or similarly sensitive information through chat when a suitably protected workflow is available.
- Limit attachments and screenshots to what is needed to troubleshoot; they can contain more customer information than the visible question.
- Tell staff what information is appropriate to request in chat and how to redirect customers when a different process is needed.
Minimization reduces the amount of information exposed if an account, device, or connected service is compromised. It also makes retention and deletion easier to manage.
Check what encryption covers in your business setup
End-to-end encryption is useful, but it is not a complete data-protection program. Check the precise app, business product, and configuration your team uses. Establish whether message contents are encrypted end to end, what message types or business functions are outside that protection, where business records and backups are stored, and which linked devices or integrations can access them.
WhatsApp’s published privacy explanation distinguishes personal messaging from business messaging: it says personal messages are end-to-end encrypted, but says it does not consider business messages end-to-end encrypted when a business chooses Meta cloud storage. WhatsApp also says businesses may use information customers provide for their own marketing. That distinction is a reason to check the business configuration and privacy terms, not to assume that a consumer-app privacy description applies to every business workflow.
Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Repair Windows errors before they cause bigger problems3Scan for outdated or missing drivers - takes under a minuteEncryption in transit and at rest can reduce the risk of data being read if communications or storage are intercepted or accessed improperly. It does not prevent exposure when someone can open an unlocked device, view a conversation through a permitted account, or access a copy in another system. The UK Information Commissioner’s Office (ICO) also notes that metadata or DNS queries may remain visible during communications; its encryption guidance is marked as under review following the Data (Use and Access) Act.
Restrict staff access and strengthen account security
Give access only to people who need customer conversations for their work. Use individual staff accounts where the service supports them rather than relying on a shared login, and require multifactor authentication (MFA) for accounts that can access customer information.
- Review who has access when job duties change, and remove access promptly when staff leave.
- Review permissions for administrators, shared inboxes, connected apps, and integrations, not just the main messaging account.
- Use the service’s available access controls and review logs or active sessions if those capabilities are provided.
- Train staff not to share credentials or approve unexpected sign-in requests.
MFA adds a second verification step beyond a password. The FTC’s small-business cybersecurity guidance gives a USB hardware token that generates temporary codes as one example. Before choosing a hardware key or token, confirm that the messaging account and identity provider support it. The FTC Safeguards Rule also requires MFA and periodic access-control review for covered financial institutions; that requirement should not be treated as a universal rule for every business.
Rank #2
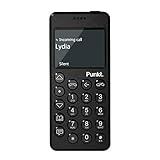
- Distraction Free: The MP02 4G cell phone makes it easier to be where you are—whether that’s a weekend away or an important business meeting. Keep what matters close with calls and SMS-first texting, without the constant onslaught of designed-for-addiction notifications.
- Privacy & Security Focused: Built with security in mind from the start, the MP02 is designed to help safeguard your information without requiring you to share more personal data than necessary. Enjoy peace of mind with a phone experience that prioritizes discretion and control.
- Carrier Compatibility & Connection: AT&T is supported (coverage verified, VoLTE supported). T-Mobile is supported, but VoLTE is not supported. Verizon is not supported. Many US carriers use VoLTE for voice calls - if VoLTE isn’t supported on your carrier, call performance may be limited even with signal. The MP02 supports 4G LTE across key bands (2G: 850/900/1800/1900 3G: WCDMA 1/2/4/5/6/8/19 4G: FDD LTE 1/2/3/4/5/7/8/12/17/19/20).
- Simple By Design: A minimalist interface keeps everyday actions straightforward. Call and text buttons provide quick access, while a streamlined menu helps you stay focused on essentials. Note: messaging is SMS-first (MMS group chats aren’t supported), helping to keep communication simple.
- Built for Everyday: Designed for comfortable one-handed use with a clean, minimalist silhouette. Reinforced glass fiber construction supports daily use, while the lightweight shape makes it easy to carry anywhere.
Secure phones and computers that display conversations
A protected account can still be exposed through a lost, stolen, shared, or unattended device. Keep operating systems and messaging apps updated, enable device encryption and a screen lock, and avoid saving message exports locally unless there is a clear need.
Decide how the business handles both company-owned and personally owned phones or computers used for customer service. NIST Special Publication 800-124 Revision 2 addresses mobile-device security across organization-provided and personally owned devices, including deployment, use, disposal, centralized device management, and endpoint protection.
- Maintain a process for reporting a lost or stolen device quickly.
- Know how to revoke a device’s access or sign out an active session, where the service provides those controls.
- Remove customer-data access before a device is reassigned, retired, or returned to an employee.
- Limit local downloads and exports, then securely dispose of records the business no longer needs.
Set retention and deletion rules for messages and copies
Keep conversation records only for a defined business or legal reason. A retention rule should say what is kept, for how long, who is responsible, and how unneeded information is disposed of. Apply it to the places identified in the inventory: the messaging service, staff devices, backups, exports, shared inboxes, and connected customer-service systems.
Deleting a conversation in one app may not delete every copy elsewhere. Confirm how the business product handles records and backups and how connected systems manage their own copies. Where a copy cannot be removed immediately, document the applicable retention behavior and restrict access to it.
Prepare for a compromised account or lost device
Write down who takes charge if a staff account is compromised or a device containing customer conversations goes missing. The FTC recommends planning for security incidents; a usable plan should support prompt containment as well as continued customer service.
Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →- Report and assess. Make sure staff know whom to contact, what to report, and how quickly. Identify the affected account, device, conversations, and connected services.
- Contain access. Use available account and session controls to secure or revoke access, and follow the business’s process for a lost device.
- Preserve what is needed. Assign responsibility for handling relevant evidence and records while preventing unnecessary sharing or copying.
- Maintain service safely. Identify how staff can continue responding to customers without reusing a compromised account or device.
- Decide on notifications. Assign responsibility for evaluating whether customers, regulators, or other parties must be notified under applicable obligations.
- Review and correct. Identify how the incident occurred and update access, device, training, or retention practices as needed.
Understand which legal requirements apply
Legal duties depend on jurisdiction, sector, the information involved, and the circumstances. Do not assume that one security rule applies to every business or that encryption alone establishes compliance.
United States: FTC Safeguards Rule
The FTC Safeguards Rule applies to covered financial institutions, not universally to all businesses. The FTC describes the rule as requiring a written information-security program appropriate to the institution and the information it handles. Its provisions include risk assessment, inventory, access controls, encryption, evaluation of apps that handle customer information, and MFA, with specific provisions and exceptions. A business should determine whether it is covered before treating the rule’s requirements as its own legal obligations.
United Kingdom: ICO security guidance
The ICO explains that the UK GDPR security principle calls for appropriate technical and organizational measures based on factors including the state of the art, implementation cost, and risk. Its guidance recommends encryption but says the law does not specifically require encryption in every case. The page is under review following the Data (Use and Access) Act, so check current official guidance before relying on it for a UK legal conclusion. It is not a general statement of law in other jurisdictions.
Questions to ask when selecting a business messaging setup
When comparing services or configurations, evaluate the specific business product rather than relying on a consumer-app label or a general encryption claim. Ask:
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →- Which message types and business features are end-to-end encrypted, and which are not?
- Where are message content, attachments, and backups stored, and who can access them?
- What retention and deletion controls apply to conversations and copies?
- Are MFA, individual staff accounts, role-based permissions, access logs, and session or device revocation available?
- How are linked devices, employee-owned devices, and integrations controlled?
- How does the provider use customer information, including any use by the business for marketing?
Record the answers for the configuration the business actually operates. Controls and data handling can differ between a personal account, a business product, and a connected customer-service system.
Frequently Asked Questions
Are business messages end-to-end encrypted?
Not necessarily. Encryption depends on the specific business product and configuration. WhatsApp says it does not consider business messages end-to-end encrypted when a business chooses Meta cloud storage, even though its explanation says personal messages are end-to-end encrypted.
Does the FTC Safeguards Rule apply to every small business?
No. The FTC describes the Safeguards Rule as applying to covered financial institutions. Its provisions should not be presented as universal requirements for every business.
Does UK GDPR require encryption in every case?
The ICO says UK GDPR does not specifically require encryption in every case. Its guidance recommends encryption as an appropriate measure depending on risk and other factors, and the page is under review following the Data (Use and Access) Act.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




