Hosting mulle domains on one server lets you run several websites, apps, or client projects from the same machine while keeping each domain reachable at its own address. Instead of needing a separate server for every site, the web server checks the requested hostname and serves the matching configuration, files, logs, and certificates.
The core pieces are DNS records that point each domain to the server, virtual hosts or server blocks that route requests to the right site, and SSL certificates that secure each domain over HTTPS. With careful directory structure, permissions, monitoring, and resource planning, a single server can host mulle domains cleanly and reliably.
As an Amazon Associate I earn from qualifying purchases.
How Multi-Domain Hosting Works on One Server
Hosting mulle domains on one server means a single machine answers requests for several websites, such as example.com, example.net, and client-site.org. The server may have one public IP address or several, but in most modern setups all domains share the same IP and are separated at the web server layer. When a browser connects, it sends the requested hostname in the HTTP Host header. The web server reads that hostname and serves the matching site configuration, document root, logs, and security settings.
Recommended Free Tools
This separation is handled by virtual hosts in Apache and server blocks in Nginx. Each virtual host or server block defines rules for one domain or a group of related names. For example, one configuration can serve example.com and www.example.com from /var/www/example.com/public, while another serves example.net from /var/www/example.net/public. The same server process listens on ports 80 and 443, but it chooses the correct site based on the incoming hostname.
#1 Best Overall

- rv toilet brush: Engineered specifically for RVs, this brush features a silicone head that gently cleans without damaging the toilet bowl or seals, a must for traditional toilet brushes.
- Compact Wall-Mounted Toilet Brush: With its space-saving design, this brush is easy to stow away discreetly, perfect for the limited space in RVs.
- silicone toilet brush: This brush is designed for thorough cleaning of the toilet bowl without causing any harm to the porcelain or seals. The drip-free toilet brush holder is crafted to collect water from the brush, preventing any mess on your RV's floor.
- Wall-Mounted Toilet Brush for RV Travel: The brush head is conveniently attachable to the bathroom wall, ensuring that there's no rolling around during your trips. With this setup, you can travel with peace of mind, knowing your toilet brush is securely in place.
Common ways domains share a server
- Name-based hosting: Multiple domains share one IP address. This is the standard approach for most websites and works well with Apache, Nginx, Caddy, and many control panels.
- IP-based hosting: Each domain uses a dedicated IP address. This is less common now but may be used for legacy applications, strict client separation, or specialized network policies.
- Port-based hosting: Different sites run on different ports, such as 8080 or 8443. This is usually used for internal services, development environments, or reverse proxy setups rather than public websites.
- Reverse proxy hosting: A front-end web server receives all public traffic and forwards requests to different back-end applications, containers, or local ports based on the domain name.
For HTTPS sites, the browser also uses SNI, or Server Name Indication, during the TLS handshake. SNI tells the server which domain the browser is trying to reach before the encrypted HTTP request is sent. This allows the server to present the correct SSL certificate for each domain while still using the same IP address. Without SNI, hosting many HTTPS domains on a single IP would be much harder and would often require a separate IP for each certificate.
A typical multi-domain server has a predictable structure: DNS records point each domain to the server, the web server maps each hostname to a site configuration, SSL certificates secure each hostname, and separate directories store files for each site. Logs are also usually separated, so access and error entries for one domain do not mix with another. This makes maintenance easier, especially when several projects, clients, or applications run on the same machine.
| Layer | Role in multi-domain hosting |
|---|---|
| DNS | Points each domain or subdomain to the server IP address. |
| Web server | Matches the requested hostname to the correct virtual host or server block. |
| SSL/TLS | Uses SNI and certificates to secure each domain over HTTPS. |
| Filesystem | Keeps website files, uploads, and application code in separate directories. |
| Permissions | Limits access between sites so one compromised site cannot easily affect another. |
The main benefit is efficiency: one server can host many small or medium sites without paying for separate infrastructure for each domain. The tradeoff is shared risk and shared resources. CPU, memory, disk I/O, network bandwidth, and database capacity are all used by the same machine. A high-traffic site, runaway script, or security issue on one domain can affect the others unless limits, monitoring, backups, and permission boundaries are planned from the start.
Pointing Each Domain to the Server with DNS
Before Apache virtual hosts or Nginx server blocks can serve different sites, each domain must resolve to the same server. DNS is the public mapping layer that tells browsers where to connect when someone visits example.com, example.net, or any other hosted name. For a single-server setup, this usually means creating DNS records for every domain and subdomain that point to your server’s public IP address.
At your domain registrar or DNS provider, open the DNS zone for each domain and add an A record for IPv4 and, if your server supports it, an AAAA record for IPv6. The root domain is commonly represented by @, while subdomains such as www, blog, or app are added as separate host records. If all domains should load from the same machine, each record can point to the same IP address.
| Host | Record type | Value | Purpose |
|---|---|---|---|
| @ | A | 203.0.113.10 | Points the root domain to the server |
| www | A | 203.0.113.10 | Points www.domain.com to the server |
| app | A | 203.0.113.10 | Points a subdomain to the same server |
| @ | AAAA | 2001:db8::10 | Optional IPv6 mapping |
For the www version of a domain, you can use either an A record pointing directly to the server IP or a CNAME record pointing to the root domain. For example, www can be a CNAME to example.com. Avoid using a CNAME at the root domain unless your DNS provider supports CNAME flattening or ALIAS/ANAME records, because traditional DNS rules do not allow a root CNAME alongside records such as MX for email.
If you are moving an existing domain, lower the record’s TTL several hours before migration, such as from 86400 seconds to 300 seconds. This helps DNS changes spread faster when you switch the domain to the new server IP. After the move is stable, you can raise the TTL again to reduce DNS lookup frequency. If email is handled elsewhere, keep existing MX, SPF, DKIM, and DMARC records intact so web hosting changes do not interrupt mail delivery.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Practical DNS setup checklist
- Confirm the server’s public IPv4 address, and IPv6 address if available.
- Create an A record for each root domain pointing to the server IP.
- Create records for required subdomains, such as
www,api, orshop. - Use CNAME records for aliases when appropriate, especially for subdomains.
- Keep mail-related DNS records unchanged unless email is also being migrated.
- Wait for DNS propagation before testing SSL issuance or browser access.
You can verify DNS resolution with tools such as dig, nslookup, or online DNS checkers. Query both the root and www names to make sure they return the expected address. Once DNS points to the server, HTTP requests will arrive at the same IP address, and the web server can use the requested hostname to route each visitor to the correct site configuration.
Configuring Virtual Hosts or Server Blocks
Once DNS records send each domain to your server’s IP address, the web server must decide which site to serve for each request. Apache calls these configurations virtual hosts, while Nginx commonly calls them server blocks. In both cases, the server reads the requested hostname from the HTTP Host header, matches it to a configured domain name, and serves content from the correct document root.
Rank #2
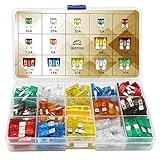
- Easy Identification: Made of a high quality zinc alloy, with a transparent cover and color coded
- 14 Most Common Fuses: Standard and Mini. (5A/ 7.5A/ 10A/ 15A/ 20A/ 25A/ 30A)
- Wide Applications: Fits most vehicles like car, truck, marine, SUV, travel trailer and other vehicles
- Note: Please use the right amp fuse to protect the vehicle and electronic equipment from short-circuit/overload
- ll Sizes You Need: The package contains 140pcs fuse and 2pcs fuse puller - 70pcs standard fuse and 70pcs mini fuse. (10pcs of each AMP)
A practical layout is to give every domain its own directory, configuration file, and log files. For example, you might store site files under /var/www/example.com/public and /var/www/example.net/public, then create one web server configuration per domain. This keeps deployments predictable and makes it easier to troubleshoot one site without touching another.
Apache virtual host example
On Apache, virtual host files are often placed in /etc/apache2/sites-available/ on Debian and Ubuntu systems. A basic HTTP configuration for one domain looks like this:
Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Repair Windows errors before they cause bigger problems3Fix the driver behind crashes, sound loss and screen glitches<VirtualHost *:80>
ServerName example.com
ServerAlias www.example.com
DocumentRoot /var/www/example.com/public
ErrorLog ${APACHE_LOG_DIR}/example.com-error.log
CustomLog ${APACHE_LOG_DIR}/example.com-access.log combined
<Directory /var/www/example.com/public>
AllowOverride All
Require all granted
</Directory>
</VirtualHost>
After creating the file, enable it and reload Apache. On Ubuntu or Debian, that typically means running a2ensite example.com.conf, checking the syntax with apachectl configtest, and applying the change with systemctl reload apache2. Repeat the pattern for each additional domain, changing ServerName, ServerAlias, DocumentRoot, and log paths.
Nginx server block example
On Nginx, server blocks are commonly stored in /etc/nginx/sites-available/ and symlinked into /etc/nginx/sites-enabled/. A simple HTTP server block can look like this:
Free tools Windows power users keep installed
One-click scans. No signup required.
server {

    listen 80;

    server_name example.com www.example.com;
root /var/www/example.com/public;
index index.html index.php;
access_log /var/log/nginx/example.com-access.log;
error_log /var/log/nginx/example.com-error.log;
Rank #3

- ✅ Organize Your Freezer with a Complete Ice System: This ice cube tray with lid and bin set solves freezer clutter by combining 4 silicone ice cube trays, a central storage container, and a scoop. Keep your kitchen tidy while always having ice ready for daily drinks, cooking, or entertaining.
- ✅ Easy-Pop Ice Release with Secure Non-Spill Lids: Each silicone ice tray features a flexible bottom for effortless ice cube removal—simply push from below. The ice tray with lid has lift tabs for easy handling and minimizes spills when moving (note: lids allow airflow and are not airtight).
- ✅ Maximize Freezer Space with Stackable Design: These ice trays for freezer stack neatly to save vertical space. Perfect for compact apartment freezers, RV refrigerators, or organizing multiple ice cube trays for freezer for parties and home use.
- ✅ BPA-Free and Odor-Resistant for Pure Ice Taste: Made from food-grade silicone and durable plastic, these ice trays resist absorbing freezer odors. Ensure clean, tasteless ice for your cocktails, coffee, or family meals with these BPA-free ice trays.
- ✅ Versatile and Dishwasher Safe for Easy Cleanup: Create clear cubes or infuse with fruits for flavored ice. The entire ice bucket kits set is top-rack dishwasher safe, making cleanup simple and convenient after parties or daily use.
location / {
try_files $uri $uri/ =404;
}
}
After saving the file, enable it with a symlink such as ln -s /etc/nginx/sites-available/example.com /etc/nginx/sites-enabled/, then run nginx -t to validate the configuration. If the test passes, reload Nginx with systemctl reload nginx. Create a separate block for every domain and make sure each server_name value is unique enough to avoid accidental matches.
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Common configuration details
- Default site: Configure a default virtual host or server block for unmatched requests, preferably returning a generic page or a 404 response instead of exposing one of your hosted domains.
- Aliases: Add both apex and
wwwhostnames when needed, such asexample.comandwww.example.com. - Application backends: For Node.js, Python, Ruby, or containerized apps, use the domain block to reverse proxy traffic to the correct local port or Unix socket.
- Config validation: Always run
apachectl configtestornginx -tbefore reloading, especially when adding several domains at once.
If a domain shows the wrong website, the most common causes are a missing ServerName or server_name, an enabled default site taking precedence, a typo in the hostname, or DNS still pointing somewhere else. Testing with curl -H "Host: example.com" http://SERVER_IP can confirm whether the web server is routing the domain correctly before DNS propagation is complete.
Setting Up SSL Certificates for Each Domain
After each domain resolves to the server and has its own virtual host or server block, the next step is enabling HTTPS for every site. Each hostname that visitors use needs to be covered by a valid SSL/TLS certificate, including both the root domain and any subdomains you serve, such as example.com, www.example.com, or app.example.com. The most common approach is to use Let’s Encrypt with Certbot, which can issue free certificates and configure Apache or Nginx automatically in many environments.
For an Nginx server, the usual command is domain-specific and can include mulle names in one certificate. For example, you would request a certificate for one site with certbot –nginx -d example.com -d www.example.com, then repeat the process for another domain, such as certbot –nginx -d anotherdomain.com -d www.anotherdomain.com. On Apache, the equivalent flow uses certbot –apache. Certbot reads your enabled virtual hosts or server blocks, matches them to the requested domain names, installs certificate paths, and can add HTTP-to-HTTPS redirects if you choose that option during setup.
Choosing the right certificate layout
You can either issue separate certificates per domain or group related names into one certificate. Separate certificates are usually cleaner for multi-site hosting because each domain can be renewed, replaced, or removed independently. A single certificate with many Subject Alternative Names can work for closely related hostnames, but it becomes harder to manage as the server grows. Wildcard certificates, such as *.example.com, are useful when you host many subdomains, but they require DNS-based validation rather than the simpler HTTP validation method.
- Separate certificate: Best for unrelated domains owned by different clients or projects.
- Multi-name certificate: Useful for one site with root, www, and a few related subdomains.
- Wildcard certificate: Useful for many dynamic subdomains under the same parent domain.
Before issuing certificates, make sure port 80 and port 443 are open in the server firewall and any cloud security group. Let’s Encrypt HTTP validation requires the certificate authority to reach your server over plain HTTP, even if the final site will force HTTPS. Also check that each domain’s DNS record points to the correct public IP address; otherwise, certificate issuance may fail because the validation request reaches the wrong server.
Renewal and web server configuration
Let’s Encrypt certificates expire after 90 days, so automated renewal is essential. Certbot typically installs a systemd timer or cron job that runs renewal checks automatically. You can test this with certbot renew –dry-run. If the test succeeds, the server should be able to renew all managed certificates without manual work. After renewal, the web server may need to reload so it starts using the updated certificate files; Certbot commonly handles this with deploy hooks or installer integration.
For each HTTPS virtual host or server block, verify that the certificate paths match the intended domain. A typical Nginx configuration uses ssl_certificate and ssl_certificate_key inside the correct server block, while Apache uses SSLCertificateFile and SSLCertificateKeyFile inside the matching <VirtualHost *:443>. Misplaced certificate paths can cause visitors to see a certificate for a different domain, especially when several sites share the same IP address.
Modern servers rely on SNI, or Server Name Indication, to present the right certificate for each domain on a shared IP address. This works well with current browsers and clients, but it depends on having a distinct HTTPS configuration for each hostname. Once certificates are installed, test every domain directly in a browser and with an SSL checker. Look for mixed-content warnings, expired intermediate chains, missing redirects, and cases where www works but the root domain does not. Fixing these issues early prevents trust errors and keeps each hosted site isolated at the TLS layer.
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Rank #4

- 【Food Grade Material】Made from eco-friendly PP+TPR material that is BPA Free and Food-Grade. The flexible material allows the dish strainers for kitchen counter to collapse flat for easy space-saving and storage, making the most of your kitchen countertop.
- 【Built-in Utensil Drying Rack】Separate storage area for utensils and gadgets, the non-slip dish drying rack is scratch-proof and offers a safe place for plates and cups, and has a separate compartment for cutlery. Perfect for storage and draining dinnerware and glassware.
- 【Compact and Portable】The collapsible dish drainer is simply pop-up to open when using and collapses to flat for space-saving storage, you can easily store it under the sink or slip it into any cabinet. Suitable for both indoors & outdoors uses, such as camping, BBQ, RV and boats, campsite cleanup, and vacation homes, etc.
- 【Drying Water Quickly】The collapsible dish storage rack versatile tool for all your household tasks, at the same time, will not hurt your hands or scratch the sink. The Bottom with an adjustable swivel drain strip allows water to run directly into the sink, keeping your counters clean and dry.
- 【Easy to Maintain】Heavy-duty plastic is simple to wipe clean, and there’s no rusting like the old clunky metal dish drying rack. The kitchen organizers for dishes is scratch-proof and offers a safe place for plates and cups, and prevent the rack from shifting and scratching any counter top.
Separating Files, Logs, and Permissions by Domain
After DNS, virtual hosts, and SSL are working, the next step is keeping each domain’s files, logs, and permissions separate. This makes day-to-day administration safer and cleaner: one site can be updated, backed up, inspected, or removed without disturbing the others. A common layout is to give every domain its own directory under a shared parent such as /var/www/example.com, with separate folders for public files, private application files, logs, and backups.
Use a predictable directory structure
For each domain, create a document root that only contains files meant to be served by the web server. For example, the public directory for example.com might be /var/www/example.com/public, while configuration files, uploads, cache files, or application secrets stay outside that document root. This reduces the chance of exposing sensitive files through a misconfigured server block or virtual host.
- Public web root:
/var/www/example.com/public - Application files:
/var/www/example.com/app - Private storage:
/var/www/example.com/private - Site-specific logs:
/var/log/nginx/example.com-access.logand/var/log/nginx/example.com-error.log
In Apache, the DocumentRoot, ErrorLog, and CustomLog directives can be set per virtual host. In Nginx, the equivalent settings are usually root, access_log, and error_log inside each server block. Keeping logs separate by domain makes it much easier to investigate 404 errors, application failures, traffic spikes, suspicious requests, and certificate renewal issues without filtering through a single combined log file.
Assign ownership and permissions carefully
Permissions should allow the web server to read public files while limiting write access to only the directories that need it, such as upload or cache folders. Avoid making entire site directories writable by the web server user. A safer pattern is to use one Linux user per domain, such as site_example for example.com, and place that user in a controlled group that the web server can read from.
| Path | Typical owner | Typical permission | Purpose |
|---|---|---|---|
/var/www/example.com/public |
site_example:www-data |
750 or 755 |
Served website files |
/var/www/example.com/private |
site_example:site_example |
700 |
Secrets, private uploads, internal files |
/var/www/example.com/public/uploads |
site_example:www-data |
770 |
Writable upload directory |
If you run PHP, Python, Node.js, or Ruby applications, stronger isolation is possible by running each site under its own process user. With PHP-FPM, for example, create a separate pool per domain and assign a unique Unix user, socket, and log file to each pool. For Node.js or Python apps managed by systemd, create one service per domain with its own User=, working directory, environment file, and restart policy. This prevents a compromised application on one domain from easily reading files or environment variables belonging to another domain.
Separation also helps with backups and maintenance. You can back up /var/www/example.com and the matching database as a unit, rotate that domain’s logs independently, and grant SFTP access to a developer for only the site they manage. For shared servers, also consider disk quotas, database users with access to only their own databases, and firewall rules that restrict internal services. The goal is to treat each domain as its own small deployment, even though all of them share the same operating system and web server.
Testing, Troubleshooting, and Monitoring Each Site
After DNS, virtual hosts, SSL, and file permissions are in place, test each domain as if it were a separate production site. Start by checking that every hostname resolves to the expected server IP address. For example, verify both example.com and www.example.com, and repeat the same process for each additional domain and subdomain. DNS propagation can vary by provider and resolver, so compare results from your local machine, a public DNS resolver, and an external DNS lookup tool if a domain behaves differently depending on where you test it from.
Next, confirm that the web server is selecting the correct virtual host or server block. Open each domain in a browser over both http:// and https://. The correct site content should load, redirects should point to the intended canonical hostname, and HTTPS should present the matching certificate for that domain. If one domain shows another site’s content, the most common causes are a missing server_name or ServerName, an unmatched alias, an incorrectly enabled configuration file, or a default virtual host catching the request. On Nginx, review enabled files under directories such as sites-enabled; on Apache, check enabled virtual hosts and run a configuration test before reloading.
Practical checks for every hosted domain
- DNS: Confirm A, AAAA, and CNAME records point where expected.
- Web routing: Make sure each hostname serves the correct document root or application.
- SSL: Check certificate names, expiration dates, intermediate chains, and HTTP-to-HTTPS redirects.
- Logs: Review separate access and error logs for each domain to avoid confusing one site’s issue with another’s.
- Permissions: Test uploads, cache writes, and application-generated files under the correct system user or group.
- Application health: Verify database connections, environment variables, background jobs, and external API access per site.
When troubleshooting, isolate the layer that is failing. A browser error such as DNS_PROBE_FINISHED_NXDOMAIN points toward DNS, while a connection timeout may indicate firewall, routing, or service availability problems. A 403 Forbidden often means the web server can see the site but lacks permission to read files or enter directories. A 404 Not Found can mean the request reached the correct virtual host but the application routing or document root is wrong. A 502 Bad Gateway or 504 Gateway Timeout usually appears when a reverse proxy cannot reach the upstream application process, such as PHP-FPM, Node.js, Gunicorn, or another backend service.
Best Value

- Advanced 6-Step Filtration Technology: Discover the impressive power of the Tastepure RV water filter’s Hex-Flow Technology and its 6-step filtration process. Each layer seamlessly works together to deliver water that’s exceptionally clean.
- Certified Lead-Free: This camping water filter is independently tested & listed to standards NSF/ANSI 42 & NSF/ANSI 53. It’s CSA lead-free content certified to NSF/ANSI 372 & compliant with all federal & state-level lead-free laws.
- Access to Pure, Great-Tasting Water: Enjoy clean water anywhere! This RV inline filter reduces bad tastes, odor, chlorine, sediment, etc. GAC filtration, combined with KDF controls bacteria & mold growth when the outdoor water filter isn’t in use.
- Patented Technology & Made in the USA: This in-line water filter is proudly made in the USA with top-notch materials and expert craftsmanship. The patented design has undergone rigorous testing and quality control to meet the highest standards.
- Versatile Applications: Easily attach this multi-purpose hose water filter to any standard garden or drinking water hose to receive cleaner drinking water. It’s great for campers, boats, pets, gardening, car washes, car detailing, & more.
Monitoring should also be domain-specific. Track uptime for each hostname, not just the server’s IP address, because one misconfigured virtual host can fail while the server remains online. Monitor disk usage by site directory and log directory, especially when mulle domains share the same storage volume. Set alerts for high CPU, memory pressure, SSL certificate expiration, repeated 5xx responses, and unusual traffic spikes. For busy servers, collect per-site metrics from web server logs so you can identify which domain is consuming bandwidth or generating errors before it affects the others.
Before making changes, use configuration validation commands such as nginx -t for Nginx or apachectl configtest for Apache, then reload rather than restart when possible to reduce downtime. Keep a small test file or health endpoint for each site, and document the expected document root, log paths, certificate name, backend port, and deployment user. This makes future debugging faster, especially when the same server hosts many unrelated domains.
Frequently Asked Questions
Can I host multiple domains on one server with a single IP address?
Yes. Most modern web servers use the requested domain name in the HTTP Host header to decide which site to serve, so one public IP address can host many domains. For HTTPS, this also works with SNI, which lets the server present the correct SSL certificate for each domain.
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallCrashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minuteDo I need separate SSL certificates for every domain?
You can use separate certificates for each domain, or one certificate that includes mulle domains as Subject Alternative Names. Let’s Encrypt is commonly used because it can issue free certificates and automate renewal. If the sites belong to different clients or projects, separate certificates are usually easier to manage and revoke independently.
How should I organize files for multiple websites on the same server?
Create a separate document root for each domain, such as /var/www/example.com and /var/www/example.net. Give each site its own log files so errors and traffic are easier to diagnose. For better isolation, use separate system users, restricted file permissions, and avoid giving all sites write access to shared directories.
What should I check if the wrong website loads for a domain?
First confirm the domain’s DNS records point to the correct server IP address. Then check that the virtual host or server block has the correct server_name or ServerName value and that the configuration is enabled. Also make sure the default site is not catching requests because of a typo, missing domain alias, or configuration order issue.
When should I move a domain to another server instead of hosting everything together?
Move a site when it regularly consumes too much CPU, memory, disk I/O, or bandwidth for the shared server. You should also separate sites with different security requirements, high traffic, or different owners who need stronger isolation. For growing setups, a load balancer, containers, VPS separation, or managed hosting can make scaling and maintenance safer.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Bottom Line
Hosting mulle domains on one server is straightforward when DNS, virtual hosts or server blocks, SSL certificates, and directory permissions are configured carefully. Start with one domain, verify routing and HTTPS, then repeat the same tested pattern for each additional site.
As your traffic grows, monitor resource usage, isolate sites where possible, and move heavier workloads to separate services or servers before performance or security becomes an issue. Keep backups, logs, and certificate renewals in place so each domain remains reliable and easy to manage.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




