Freedom251 › Application Security Posture Management Software
SecurStack
What SecurStack is
SecurStack is a cloud platform for finding, prioritizing and addressing application security risks before production. It combines static and dynamic application security testing, software composition analysis with SBOM, and secrets scanning. Risk scores factor in severity, exposure, service criticality, exploitability and repository history. Teams can set policies to block builds that miss a security baseline. AI Drive accepts natural-language requests about risks, releases, repositories, owners and SLAs; AI suggestions include remediation paths, code snippets, validations and policies. Listed CI/CD integrations include GitHub Actions, GitLab CI, Bitbucket Pipelines, Azure DevOps, Jenkins and CircleCI. Plugins are listed for JetBrains IDEs and VS Code, and its MCP server works with Codex, Claude Code and other agents. AI Vault stores credentials by collection, provides scoped access through MCP and audits reveals without exposing secret values in listings, logs or reports. The Free plan includes 500 scan credits monthly, 3 users and 10 projects. Paid plans start at $5 a month.
Who it suits
SecurStack is aimed at engineering, security and compliance teams, including engineering leaders and CISOs. It may suit teams seeking security scans and build policies integrated with their CI/CD tools.
What it does well
- Combines SAST, DAST, SCA and secrets scanning
- Risk scoring considers repository history and exploitability
- Free plan includes 500 monthly scan credits
- Integrations span six named CI/CD services
- AI Vault scopes credential access through MCP
What to know first
- Free plan limited to 3 users
- Free plan limited to 10 projects
- Free plan has 500 scan credits monthly
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Free | 500 scan credits/month · 3 users · 10 projects · SAST + SCA + Secrets | Free |
| Pro | 10,000 scan credits/month · 25 users · Unlimited projects · SSO and quality gates | $15 a month |
| Basic | 2,500 scan credits/month · 10 users · 25 projects · 10 API keys | $5 a month |
| Enterprise | 50,000+ credits/month · 100+ users · 100+ API keys · Private runners and SLA | On request |
As securstack.io lists them, read 30 Sept 2026. The maker's own page has the final word.
Overview
SecurStack is a cloud application-security platform that connects scanning with risk prioritization, remediation and build controls. It suits engineering and security teams that want to work through findings in the development cycle; teams needing broad scan coverage can start free, but should expect to manage plan caps as usage grows.
Its combination of code, dependency and secrets scanning is paired with workflows for correlating findings, assigning ownership and guiding remediation. That makes it a more natural fit for teams managing security across repositories than for buyers seeking only a standalone report.
Key features
SecurStack combines static and dynamic application security testing (SAST and DAST), software composition analysis with software bills of materials (SBOM), and secrets scanning. Together, these cover code, dependencies and credentials. Finding correlation and ownership mapping help teams organize results and connect them to responsible owners, while remediation workflows and SBOM management carry the work beyond detection.
Risk scoring combines severity with exposure, service criticality, exploitability and repository history. This can give teams more context for prioritization than severity alone. AI Drive accepts natural-language commands about risks, releases, repositories, owners and service-level agreements; AI remediation suggestions include paths, code snippets, validations and policies aimed at preventing repeat findings.
Teams can set quality gates to block builds that miss their security baseline. That ties policy to delivery, though quality gates are included in Pro rather than Free or Basic. CI/CD integrations cover GitHub Actions, GitLab CI, Bitbucket Pipelines, Azure DevOps, Jenkins and CircleCI. Plugins for JetBrains IDEs and VS Code, plus an MCP server compatible with Codex, Claude Code and other agents, offer additional ways to bring security work into developer workflows.
AI Vault stores credentials in collections, grants scoped access through MCP and audits reveals without exposing secret values in listings, logs or reports. SecurStack also describes tenant isolation, granular role-based access, immutable audit logs, secret redaction, encryption in transit and at rest, and workers without public ingress. Those controls address access and data handling concerns; private runners are reserved for Enterprise.
Pricing
The Free plan costs nothing and includes 500 scan credits per month, 3 users, 10 projects, and SAST, SCA and Secrets scanning. It is a sensible starting point for a small team, but it excludes DAST from its stated scan coverage and has tight user, project and credit limits.
Basic costs $5 a month and raises the allowance to 2,500 scan credits per month, 10 users and 25 projects, with 10 API keys. It suits a team that has outgrown the Free caps, but does not include the SSO and quality gates specified for Pro.
Pro costs $15 a month and includes 10,000 scan credits per month, 25 users, unlimited projects, SSO and quality gates. The larger quotas and build policies make it the stronger fit for teams that need to scale scans and enforce a security baseline in CI/CD.
Enterprise has custom pricing and includes 50,000+ credits per month, 100+ users, 100+ API keys, private runners and an SLA. Those allowances and deployment controls are aimed at larger organizations; the step up from Pro is difficult to assess without a published price.
Platforms
SecurStack is available through a web platform and an extension, and its deployment option is cloud. The IDE plugins and CI/CD integrations extend its reach across development workflows, but teams requiring self-hosted deployment should look elsewhere.
Who it's for
Engineering and security teams that need to triage application risks across repositories, map findings to owners and link remediation to build policies are the clearest fit. Engineering leaders and CISOs may also value the scoring and governance controls. The Free plan can suit a small evaluation or limited workload; teams with larger scan volumes, more users or a need for quality gates will need a paid tier.
The contact page offers a personalized demo and says the team responds within one business day, a useful route for organizations assessing Enterprise requirements.
Pros and cons
- Broad scanning in one platform: SAST, DAST, SCA with SBOM and secrets scanning address several application-security needs, though the Free plan includes only SAST, SCA and Secrets.
- Prioritization and remediation are connected: contextual scoring, ownership mapping and AI-assisted guidance can help teams move from finding to action.
- Build policies can enforce a baseline: Pro includes quality gates, but Free and Basic do not.
- Low-cost entry with defined caps: Free and Basic provide clear monthly credit allowances, but users and projects are also limited on those tiers.
- Cloud-only deployment: the web and extension options suit cloud workflows, but not teams seeking a self-hosted deployment.
Alternatives
Application Security Posture Management Software is a useful category page for comparing products beyond this shortlist.
- Arnica Secrets Security is worth considering when weekly automated reports, SSO and a free plan billed per identity per year are a better match; its free tier also includes SAST, SCA, IaC, licensing, reputation and secrets scanning.
- Conviso Platform may suit teams that want a free tier capped at 5 contributing developers, 5 assets, 10 users and 2 integrations, or a Developers plan starting at $19 a month.
- OWASP DefectDojo is the alternative to consider for an open-source Community Edition that is free forever, with support through OWASP Slack and GitHub.
- Phoenix Security offers a free tier for up to 1000 assets, 2 Premium Users plus guests, dashboard reporting and community support; consider it when those asset and user allowances fit better.
- Strobes ASPM has a free plan for up to 100 assets and 500 tasks per month, with ASM, RBVM, ASPM and one connector; it may fit teams whose needs align with those stated caps.
- OX Security is a paid alternative with named products including OX Code and OX VibeSec; its OX Code coverage includes SAST, SCA, secrets/PII, SBOM, IaC, CI/CD, container scanning, IDE and CLI.
- Foxnode ASPM is another free alternative.
- Ivanti Neurons for Zero Trust Access is a paid alternative for buyers considering that product category.
Verdict
SecurStack is a strong choice for engineering and security teams that want scanning, prioritization and remediation linked to development, especially if Pro’s 10,000 monthly credits, unlimited projects, SSO and quality gates fit the workload. Its main drawback is that lower tiers cap credits, users and projects, while Enterprise pricing is custom. Choose it for an integrated cloud workflow with a low-cost starting point; look elsewhere if self-hosting or a clearly priced enterprise tier is essential.
Verdict
SecurStack brings several application-security scans, risk scoring and build policies into one cloud platform. The Free plan has defined user, project and credit limits; paid plans start at $5 a month.
Facts from SecurStack's own pages
- AI features
- AI Drive accepts natural-language commands about risks, releases, repositories, owners and SLAs. · securstack.io, 30 Sept 2026
- AI Vault
- AI Vault stores credentials by collection, grants scoped access through MCP and audits reveals without showing secret values in listings, logs or reports. · securstack.io, 30 Sept 2026
- CI/CD integrations
- The site lists GitHub Actions, GitLab CI, Bitbucket Pipelines, Azure DevOps, Jenkins and CircleCI. · securstack.io, 30 Sept 2026
- Developer tools
- The site lists plugins for JetBrains IDEs and VS Code, plus an MCP server compatible with Codex, Claude Code and other agents. · securstack.io, 30 Sept 2026
- Free plan limit
- The Free plan includes 500 scan credits per month, 3 users, 10 projects, and SAST, SCA and Secrets scanning. · securstack.io, 30 Sept 2026
- Intended users
- The platform describes its use cases for engineering, security and compliance teams, including engineering leadership and CISOs. · securstack.io, 30 Sept 2026
- Purpose
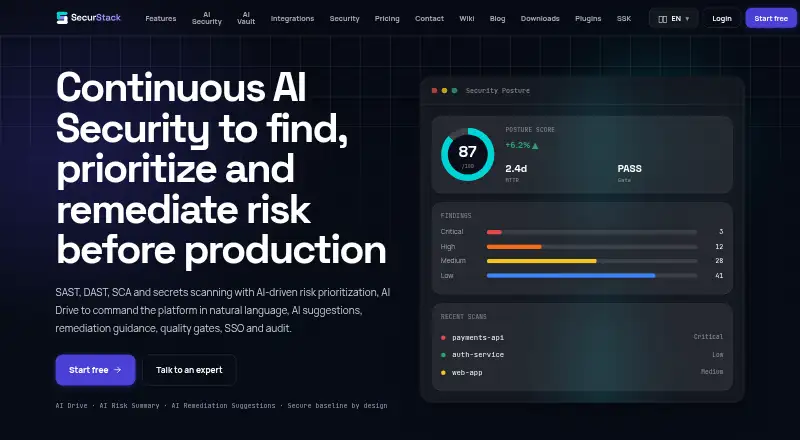
- SecurStack provides continuous application security to find, prioritize and remediate risk before production. · securstack.io, 30 Sept 2026
- Quality gates
- Teams can define policies that block builds that fall below their security baseline. · securstack.io, 30 Sept 2026
- Remediation
- AI suggestions provide remediation paths, code snippets, validations and policies to help prevent recurrence. · securstack.io, 30 Sept 2026
- Risk prioritization
- AI-driven risk scoring combines severity, exposure, service criticality, exploitability and repository history. · securstack.io, 30 Sept 2026
- Scanning
- The platform combines SAST, DAST, software composition analysis with SBOM, and secrets scanning. · securstack.io, 30 Sept 2026
- Security controls
- The site describes multi-tenant isolation, granular RBAC, immutable audit logs, secrets redaction, TLS in transit and at rest, and workers without public ingress. · securstack.io, 30 Sept 2026
- Support
- The contact page offers a personalized demo and says the team responds within one business day. · securstack.io, 30 Sept 2026