Freedom251 › Container Build Tools
rules_docker
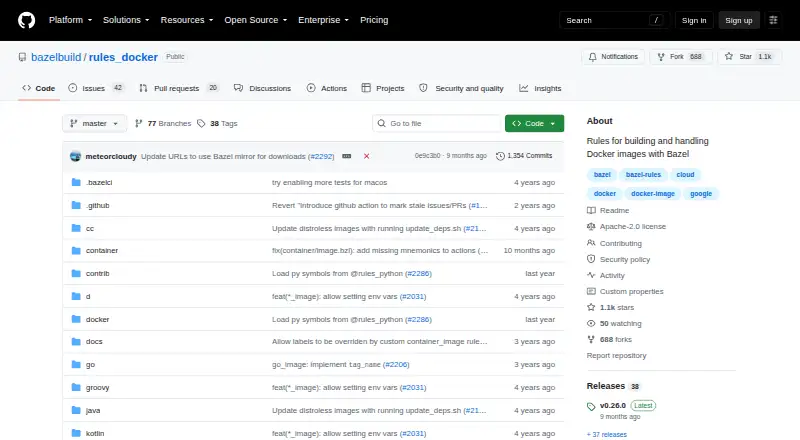
What rules_docker is
rules_docker is a set of Bazel rules for pulling base images, adding build artifacts and assets, and publishing container images. Its basic image pull, build, and push operations do not need or use Docker, and images made with container_image are described as deterministic and reproducible. The core rules include container_image, container_bundle, container_import, container_load, container_pull, and container_push. Pulling and pushing use google/go-containerregistry for registry access, with standard Docker authentication described for private images. Language image rules cover Python, Node.js, Java, Scala, Groovy, C++, Go, Rust, and D. They use distroless language runtimes by default and allow a configurable base. Separate rules for installing apt-get packages or running commands inside containers require a properly configured Docker binary. The rules can be used on macOS without boot2docker or docker-machine and do not require workstation root access, but Windows is not supported. The project is free under Apache License 2.0 and is maintained on an as-needed basis; its repository points to rules_oci as an alternative.
Who it suits
rules_docker suits developers using Bazel to build and publish container images, especially those who need Docker-free basic image operations. It supports Linux and macOS, but not Windows.
What it does well
- Basic image operations do not require or use Docker
- container_image outputs are described as reproducible
- Language rules cover nine programming languages
- Does not require workstation root access
What to know first
- Windows is not supported
- Package installation and in-container commands require Docker
- Maintained on an as-needed basis
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| rules_docker | Apache-2.0 · maintained on an as-needed basis · Windows is not supported | Free |
As github.com lists them, read 4 Oct 2026. The maker's own page has the final word.
Getting started
- Open the rules_docker repository on GitHub.
- Use the rules on Linux or macOS.
- Choose the basic image rules for pulling, building, bundling, importing, loading, or pushing images.
- Select a language image rule for a supported language and configure its base if needed.
- Configure a Docker binary before using rules for apt-get installation or commands inside containers.
Verdict
rules_docker provides a broad set of Bazel container rules, including basic operations that do not use Docker. Consider its maintenance status and Windows exclusion, and note that some additional container operations do require Docker.
Questions
What does rules_docker cost?
It is free under the Apache License 2.0.
Does it require Docker?
Basic image pull, build, and push rules do not require or use Docker. Rules for installing apt-get packages or running commands inside containers do require a properly configured Docker binary.
Which platforms are supported?
The listed platforms are Linux and macOS. Windows use is not supported.
Which programming languages have image rules?
The rules cover Python, Node.js, Java, Scala, Groovy, C++, Go, Rust, and D.
How does it handle private registries?
Pull and push use google/go-containerregistry for registry interactions, and the README describes standard Docker authentication for private images.
How is the project maintained?
The repository says it is maintained on an as-needed basis and points users to rules_oci as an alternative.
Facts from rules_docker's own pages
- Container operations
- Basic rules include container_image, container_bundle, container_import, container_load, container_pull, and container_push. · github.com, 4 Oct 2026
- Docker dependency
- The basic image pull, build, and push rules do not require or use Docker. · github.com, 4 Oct 2026
- Language rules
- The project provides image rules for Python, Node.js, Java, Scala, Groovy, C++, Go, Rust, and D. · github.com, 4 Oct 2026
- License
- The repository is licensed under Apache License 2.0. · github.com, 4 Oct 2026
- Maintenance
- The repository says rules_docker is maintained on an as-needed basis and points users to rules_oci as an alternative. · github.com, 4 Oct 2026
- Notable limitation
- The README says language image rules do not expose Docker-related attributes, so adding a custom environment variable or symlink requires using a container_image target. · github.com, 4 Oct 2026
- Package and run rules
- Additional rules can install apt-get packages and run commands inside containers, but they require a properly configured Docker binary. · github.com, 4 Oct 2026
- Platform support
- The README says the rules can be used on OSX without boot2docker or docker-machine, while Windows use is not supported. · github.com, 4 Oct 2026
- Purpose
- rules_docker is a set of Bazel rules for pulling base images, adding build artifacts and assets, and publishing container images. · github.com, 4 Oct 2026
- Registry integration
- container_pull and container_push use google/go-containerregistry for registry interactions, and the README describes standard Docker authentication for private images. · github.com, 4 Oct 2026
- Reproducibility
- The repository says images produced by container_image are deterministic and reproducible. · github.com, 4 Oct 2026
- Runtime base
- Higher-level language image rules use distroless language runtimes by default, with a configurable base attribute. · github.com, 4 Oct 2026
- Security reporting
- The security policy directs vulnerability reports to Google's g.co/vulnz intake and says the Google Security Team processes reports within a day and responds within a week, depending on severity. · github.com, 4 Oct 2026
- Workstation access
- The README says these rules do not require root access on the workstation. · github.com, 4 Oct 2026
Where rules_docker stands on Freedom251
- Container Build Tools#24 of 34