Freedom251 › Incident Response Software
ORNA
What ORNA is
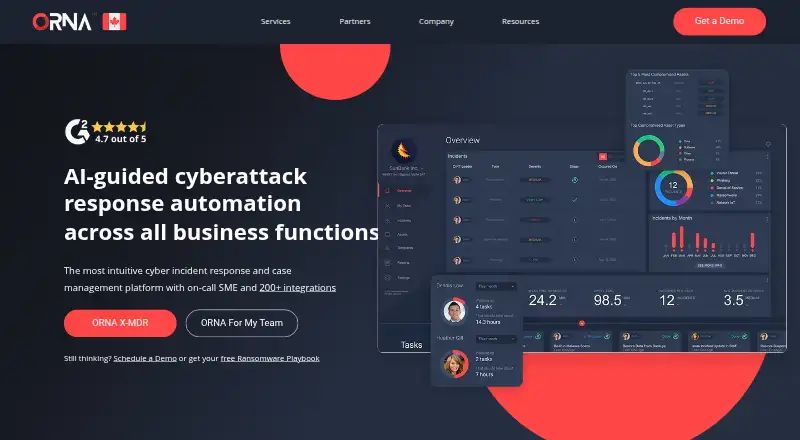
ORNA is an AI-guided platform for cyberattack response automation and incident case management. Its Scout agent detects infrastructure attacks and anomalies around the clock, groups findings by source, relevance, and criticality, and enriches them with threat intelligence from 28 public and private sources. AI analysis estimates severity and affected assets, with breakdowns by asset, attack type, technique, and time. Teams can escalate alerts into incidents; ORNA then generates and assigns attack-specific tasks based on team roles. Playbooks cover digital forensics and incident response as well as crisis work for HR, communications, and legal teams. It can produce executive or detailed reports with evidence analysis, and its Risk Dashboard supports NIST CSF management across five governance domains. ORNA lists more than 200 integrations and says it can be deployed on-premises or in the cloud. It also states that it encrypts data at rest and in transit, requires TOTP MFA, and segregates customer instances. A free self-managed plan is listed; managed and other self-managed plans require custom quotes.
Who it suits
ORNA is aimed at agile DFIR teams; the maker says free access is specifically for midsize businesses. Its playbooks also cover crisis activities involving HR, communications, and legal teams.
What it does well
- Threat intelligence draws on 28 sources.
- Tasks are assigned based on team roles.
- Playbooks cover DFIR and other crisis work.
- Free 24/7 incident-resolution support is included.
What to know first
- Managed and other self-managed plans require custom quotes.
- Deployment and security details are stated by the maker.
Limits
The Self-Managed Free plan is listed as free. Prices for Managed, Self-Managed Pro, and Self-Managed Pro + Alerts are custom quotes; no free-plan quotas or feature limits are stated.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Self-Managed Free | Free plan listed in comparison table | Free |
| Managed | custom quote · platform with all features · dedicated 24/7 SecOps team | On request |
| Self-Managed Pro | custom quote · Pro plan listed in comparison table | On request |
| Self-Managed Pro + Alerts | custom quote · Pro + Alerts plan listed in comparison table | On request |
As orna.app lists them, read 1 Oct 2026. The maker's own page has the final word.
Getting started
- Visit the ORNA website.
- Choose the Self-Managed Free plan or request a custom quote for another plan.
- Select web, API, self-hosted, on-premises, or cloud deployment.
- Connect relevant tools from ORNA’s integration options.
- Use Scout to review findings and escalate alerts into incidents.
ORNA is an AI-guided platform that links attack detection with incident response case management, reporting, and risk governance. It suits agile DFIR teams and midsize businesses that need technical and business responders working from the same workflow. The strongest case for it is breadth across detection, coordination, and compliance; the main drawback is that most paid deployments require a custom quote.
Overview
ORNA’s Scout agent watches infrastructure continuously, groups attacks and anomalies by source, relevance, and criticality, and enriches them with threat intelligence from 28 public and private sources. That gives response teams a way to prioritize activity instead of treating every alert alike, although the practical value still depends on the quality and volume of signals in each environment.
The product combines automated response workflows with evidence handling, collaboration, scheduling, audit records, API access, and a risk dashboard. It can run in the cloud or on premises, with hybrid deployment options and custom enterprise integrations. That flexibility favors organizations with deployment or data-location requirements, while teams seeking a narrowly focused detector may find the scope broader than necessary.
Key features
AI analysis estimates incident severity and affected assets, then displays attack breakdowns by asset, type, technique, and time. An alert can become an incident in one action, after which attack-specific tasks are generated and assigned according to team roles. This is a meaningful advantage during fast-moving incidents because coordination is built into the case rather than left to manual task lists.
Playbooks cover digital forensics and incident response, plus crisis activities for HR, communications, and legal teams. Detailed and executive reports can include built-in evidence analysis and be produced in seconds. Evidence tracking, responder collaboration, on-call scheduling, and audit logs provide the operational record needed for shared response and later review.
The Risk Dashboard supports NIST CSF management across five governance domains and supplies dynamic improvement recommendations. ORNA also states that it offers more than 200 integrations, including FortiGate, SonicWall, Entrust, Cisco VPN, Palo Alto firewalls, VMware Carbon Black EDR, Docker, Kaspersky, McAfee, and Microsoft Exchange. Reports use AES-256 protection with unique 32-symbol hexadecimal access codes; platform data is encrypted at rest and in transit with TLS 1.3, mandatory TOTP MFA, and segregated customer instances.
Pricing
Self-Managed Free — free. This is the no-cost self-managed entry point and is specifically positioned for midsize businesses. It is the sensible way to adopt ORNA without a software fee, but organizations needing managed operations or paid-tier capabilities should expect a commercial conversation.
Managed — custom pricing. This includes all platform features and a dedicated 24/7 SecOps team. It fits organizations that want continuous operational support rather than running response themselves, with the trade-off of a quote-based budget.
Self-Managed Pro — custom pricing. The paid self-managed tier is for teams that want to operate the platform internally at a higher service level than the free option. Self-Managed Pro + Alerts — custom pricing. This version is aimed at teams that specifically need the Pro package with alerting. Published plan terms do not provide a fixed seat or quota figure, so buyers should confirm scope during pricing discussions.
ORNA also includes free 24/7 SME incident-resolution and digital-forensics support and around-the-clock customer service, a notable benefit for a free self-managed deployment.
Platforms
ORNA is offered through web and API access, with self-hosted deployment and cloud operation. On-premises and hybrid choices, segregated instances, and custom enterprise integrations make it suitable for organizations with infrastructure or residency constraints.
Who it's for
Choose ORNA when an agile DFIR team needs detection, investigation, playbooks, reporting, and NIST-oriented risk work in one system. It is particularly well matched to midsize businesses using the free self-managed plan and to larger organizations willing to pay for managed SecOps or custom integrations. It is less compelling for a buyer who wants only endpoint tooling or a clearly priced, narrowly scoped service.
Pros and cons
- Pro: One workflow connects 24/7 attack monitoring, AI prioritization, task assignment, evidence, and reporting.
- Pro: Playbooks include HR, communications, and legal, extending response beyond the security team.
- Pro: Cloud, self-hosted, on-premises, and hybrid deployment support varied operational requirements.
- Pro: Free 24/7 specialist and customer support strengthens the no-cost self-managed option.
- Con: Paid plans use custom pricing, making comparisons and budgeting less transparent.
- Con: The broad feature set may exceed the needs of teams seeking only alert detection.
Alternatives
For a no-license, self-hosted incident-response case system, choose DFIR-IRIS. Forensicator is a free, open-source cross-platform incident-response toolkit, with an enterprise plan priced by quote. GRR Rapid Response is a free Apache-licensed, self-hosted option. LimaCharlie suits readers wanting a free tier with up to two endpoints and a free trial. DFIRe offers a case-by-case non-commercial plan and a free trial. SIFT Workstation is a free open-source workstation for Linux or Windows. TraceLock CRM is a free, open-source self-hosted CRM without per-seat pricing. Binalyze AIR is a paid product with a free trial.
See more options in Incident Response Software.
Verdict
ORNA is a strong choice for DFIR teams that want detection, automated case workflows, cross-functional playbooks, reporting, and risk management together, with self-managed and managed deployment paths. Choose it for that integrated operating model and its free entry plan; look elsewhere if fixed pricing or a smaller, specialist incident-response tool is more important.
Verdict
ORNA combines attack detection, incident workflows, reporting, and risk management, with cloud and on-premises deployment options. Pricing beyond the listed free self-managed plan is by custom quote.
Questions
How much does ORNA cost?
The Self-Managed Free plan is listed as free. Managed, Self-Managed Pro, and Self-Managed Pro + Alerts use custom quotes.
Does ORNA have a free plan?
Yes. The Self-Managed Free plan is listed in the plan comparison.
Where can ORNA be deployed?
ORNA supports web, API, and self-hosted access. It says it can be deployed on-premises or in the cloud.
How many integrations does ORNA list?
ORNA lists more than 200 integrations, including FortiGate, Cisco VPN, Palo Alto firewalls, VMware Carbon Black EDR, and Microsoft Exchange.
Who makes ORNA?
ORNA is headquartered in Toronto, Ontario, Canada.
What security measures does ORNA describe?
ORNA says data is AES-256 encrypted at rest and in transit with TLS 1.3, mandatory TOTP MFA is used, and customer instances are segregated. It also says reports are protected with AES-256 and unique 32-symbol hexadecimal access codes.
Facts from ORNA's own pages
- AI analysis
- ORNA’s AI estimates incident severity and affected assets and presents color-coded attack breakdowns by asset, type, technique and time. · orna.app, 1 Oct 2026
- Audience
- ORNA describes its product as created and priced for agile DFIR teams and says its free access is specifically for midsize businesses. · orna.app, 1 Oct 2026
- Case management
- Alerts can be escalated into incidents with one action, while ORNA automatically generates and assigns attack-specific tasks based on team roles. · orna.app, 1 Oct 2026
- Customer reach
- ORNA says its AI cloud-security products and advisory services benefit more than 450 organizations in 11 countries. · orna.app, 1 Oct 2026
- Deployment
- ORNA says it can be deployed on-premises as well as in the cloud and can receive custom enterprise features and integrations. · orna.app, 1 Oct 2026
- Detection
- Its Scout agent detects attacks and anomalies across infrastructure 24/7/365, groups them by source, relevance and criticality, and enriches them with threat intelligence from 28 public and private sources. · orna.app, 1 Oct 2026
- Headquarters
- Toronto, Ontario, Canada · orna.app, 28 Sept 2026
- Integrations
- ORNA states that it has 200+ integrations, including FortiGate, SonicWall, Entrust, Cisco VPN, Palo Alto firewalls, Symantec WAF, VMware Carbon Black EDR, Docker, Kaspersky, McAfee and Microsoft Exchange. · orna.app, 1 Oct 2026
- Platform security
- ORNA states that data is AES-256 encrypted at rest and in transit with TLS 1.3, mandatory TOTP MFA is used, and customer instances are segregated. · orna.app, 1 Oct 2026
- Playbooks
- Built-in playbooks cover DFIR and non-InfoSec crisis activities for teams including HR, communications and legal. · orna.app, 1 Oct 2026
- Product
- ORNA is an AI-guided cyberattack response automation and cyber incident response case-management platform. · orna.app, 1 Oct 2026
- Reporting
- ORNA produces detailed or executive incident reports with built-in evidence analysis in seconds. · orna.app, 1 Oct 2026
- Risk and compliance
- Its Risk Dashboard supports NIST CSF management across five governance domains with dynamic improvement recommendations. · orna.app, 1 Oct 2026
- Security
- ORNA says reports are secured with AES-256 and unique 32-symbol hexadecimal access codes. · orna.app, 1 Oct 2026
- Support
- The platform includes free 24/7 SME incident-resolution and digital-forensics support plus around-the-clock customer service. · orna.app, 1 Oct 2026
Where ORNA stands on Freedom251
- Incident Response Software#7 of 21