Freedom251 › Open Source License Compliance Software
OpossumUI
What OpossumUI is
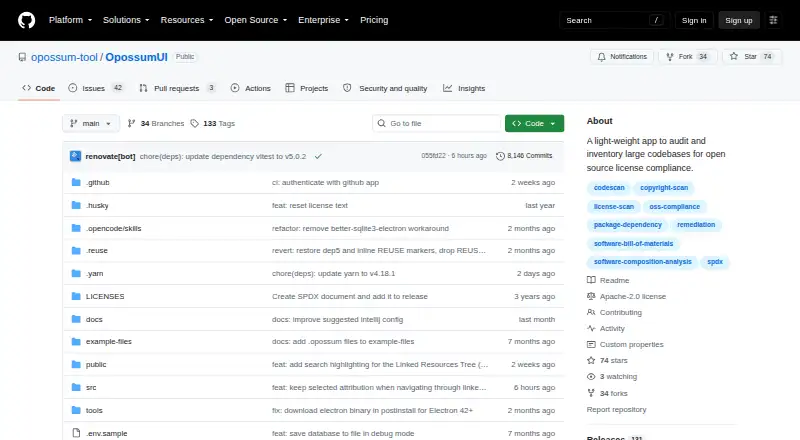
OpossumUI is a free desktop application for exploring open-source components, reviewing license compliance, and producing reports from code scans. It combines findings from scanners such as OSS Review Toolkit and ScanCode in one interface. Users can browse scanner evidence, move through a codebase file tree, and create or edit attributions for individual files or groups. The app works with .opossum files containing license-compliance data. It directly imports ScanCode JSON and OWASP Dependency-Check JSON, while OSS Review Toolkit results can be converted with a reporter before import. Exports include SPDX documents in JSON or YAML, component lists in CSV, and follow-up documents for items sent for legal review. The project lists license audits, software bills of materials, and blind intellectual-property audits during mergers and acquisitions as use cases. Downloads support Linux, macOS, and Windows, with on-premise deployment. OpossumUI uses Apache-2.0; its documentation uses CC0-1.0.
Who it suits
It suits teams reviewing open-source licenses, preparing software bills of materials, or creating attribution records. It can also support blind intellectual-property audits where compliance metadata is shared without source code.
What it does well
- Free plan is available
- Combines OSS Review Toolkit and ScanCode findings
- Imports ScanCode and OWASP Dependency-Check JSON
- Exports SPDX JSON or YAML
- Runs on Linux, macOS, and Windows
What to know first
- Ubuntu 22.04 and later may need --no-sandbox
- macOS app is not officially signed
- SPDX expressions are only partially supported
Limits
SPDX license expressions have only partial support, so the full applicable license text should also be entered in the license-text field. Ubuntu 22.04 and later may require the documented --no-sandbox launch workaround.
Getting started
- Open the OpossumUI GitHub project page
- Download the build for Linux, macOS, or Windows
- On macOS, allow the unsigned app in System Settings
- Import ScanCode JSON or OWASP Dependency-Check JSON files
- Convert OSS Review Toolkit results with a reporter before importing
- Open or create .opossum license-compliance files
Verdict
OpossumUI brings scanner evidence, attribution work, imports, and compliance exports into one desktop workflow. Check its Linux sandboxing, macOS signing, and SPDX expression limits before adopting it.
Questions
Is OpossumUI free?
Yes. OpossumUI has a free plan.
Which platforms does it support?
Downloads are provided for Linux, macOS, and Windows.
What scanner formats can it import?
It directly imports ScanCode JSON and OWASP Dependency-Check JSON. OSS Review Toolkit results require conversion with a reporter first.
What can it export?
It exports SPDX documents as JSON or YAML, component lists as CSV, and follow-up documents for legal-review items.
Is OpossumUI open source?
The project states that OpossumUI is licensed under Apache-2.0, and its documentation is under CC0-1.0.
How is it deployed?
The listed deployment option is on-premise.
Facts from OpossumUI's own pages
- Attribution review
- Users can create and edit attributions for individual files or groups of resources. · github.com, 4 Oct 2026
- Audit workflow
- The app provides a unified interface for browsing scanner evidence, navigating a codebase file tree, and creating attributions for files or groups. · github.com, 4 Oct 2026
- Core workflow
- It lets users explore software components, review licenses, and generate reports from open-source scans. · github.com, 4 Oct 2026
- Exports
- It exports SPDX documents as JSON or YAML, component lists as CSV, and follow-up documents for items flagged for legal review. · github.com, 4 Oct 2026
- File formats
- OpossumUI works with `.opossum` files and can directly import ScanCode JSON and OWASP Dependency-Check JSON files. · github.com, 4 Oct 2026
- File handling
- OpossumUI works with .opossum files containing license-compliance data that can be visualized and edited in the app. · github.com, 4 Oct 2026
- Imports
- It can directly import ScanCode JSON and OWASP Dependency Check JSON files; OSS Review Toolkit results can be converted using a reporter and imported. · github.com, 4 Oct 2026
- License
- The project states that OpossumUI is licensed under Apache-2.0 and its documentation under CC0-1.0. · github.com, 4 Oct 2026
- License expression limit
- SPDX license expressions are only partially supported; the README says the full applicable license text should also be entered in the license-text field. · github.com, 4 Oct 2026
- Linux caveat
- The README says Ubuntu 22.04 and later can have an AppImage sandboxing issue, with a documented --no-sandbox workaround. · github.com, 4 Oct 2026
- macOS caveat
- The README says the macOS app is not officially signed and must be explicitly allowed in System Settings. · github.com, 4 Oct 2026
- macOS signing
- The project says the macOS app is not officially signed and must be explicitly allowed in System Settings. · github.com, 4 Oct 2026
- Maintainer
- The GitHub organization identifies itself as opossum-tool and describes OpossumUI as a lightweight app for open-source license compliance audits and inventory. · github.com, 4 Oct 2026
- Notable limitation
- SPDX license expressions are only partially supported; the guide says the full license text should also be entered in the license-text field. · github.com, 4 Oct 2026
- Platforms
- The user guide provides downloads and run instructions for Linux, macOS, and Windows. · github.com, 4 Oct 2026
- Purpose
- OpossumUI helps explore open-source components, review licenses in codebases, and generate reports from open-source code scans. · github.com, 4 Oct 2026
- Scanner integrations
- It combines findings from multiple scanners and names OSS Review Toolkit and ScanCode as integrations. · github.com, 4 Oct 2026
- Security use case
- For blind intellectual-property audits during mergers and acquisitions, the project says only compliance-relevant metadata needs to be exposed in the app, without sharing source code. · github.com, 4 Oct 2026
- Source-code handling
- For blind audits, the project says the app can expose only compliance-relevant metadata without sharing source code. · github.com, 4 Oct 2026
- Support and updates
- The user guide directs users to GitHub releases and says they can check for updates through the app’s Help menu. · github.com, 4 Oct 2026
- Supported downloads
- The user guide provides downloads for Linux, macOS, and Windows. · github.com, 4 Oct 2026
- Use cases
- The project describes license-compliance audits, software bills of materials, and blind intellectual-property audits during mergers and acquisitions as use cases. · github.com, 4 Oct 2026