Freedom251 › Open Source License Compliance Software
SourceTrust
What SourceTrust is
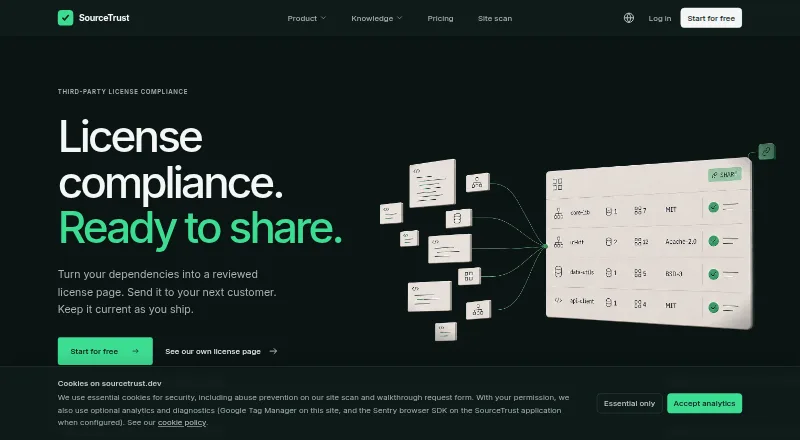
SourceTrust helps teams review third-party software licenses and publish a shareable compliance page for products they ship. It collects direct and transitive dependencies from repositories, lockfiles, and SBOMs into one inventory, then retrieves shipped packages, checks registry digests, and reads license text inside each package. Teams must review and confirm records before publication, and the platform flags packages that need a decision. Listed connections include GitHub, GitLab, and Azure DevOps; imports include lockfiles and SBOMs, with 14 formats across 9 ecosystems. Outputs include a hosted attestation page, THIRD_PARTY_LICENSES.md, NOTICE, CycloneDX, SPDX, JSON, CSV, plist, and branded PDF. Repository sync and publish-drift checks flag differences from a published snapshot. Pages can be password-protected and kept out of search engines. SourceTrust says it reads lockfiles and SBOMs rather than source code, parsing lockfiles in the browser before upload. Eligible public GitHub projects can publish for free, subject to fair use and attribution. Standard project billing begins on first publication or export download; yearly billing is $299 a year.
Who it suits
SourceTrust suits teams that need to review third-party licenses and publish compliance information for shipped products. It is software tooling, not a law firm or legal advice.
What it does well
- Combines dependencies from repositories, lockfiles, and SBOMs
- Flags packages that need a decision
- Offers multiple compliance and inventory export formats
- Checks for changes from published inventory
- Lockfiles are parsed in the browser before upload
What to know first
- Standard billing starts on first publish or export download
- Free publishing is limited to eligible public GitHub projects
- No free trial is offered
- The product is not legal advice
Limits
The Open source plan is limited to eligible public GitHub repositories, subject to fair use and SourceTrust attribution. Per-project plans include two watched branches; additional watched branches are a separate plan.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Open source | eligible public GitHub repository · fair use applies · SourceTrust attribution | Free |
| Per project — monthly | Monthly · per shipped product · unlimited users · two watched branches | $29 a month |
| Per project — yearly | Yearly · per shipped product · unlimited users · two watched branches | $299 a year |
| Custom domain | Same monthly or yearly choice as your plan · one hostname for every attestation page in your organization · non-refundable once provisioned | $49,499 a month |
| Extra watched branch | Same monthly or yearly choice as your plan · per project · beyond the two included branches | $550 a month |
| Security monitoring | Same monthly or yearly choice as your plan · organization-wide · daily OSV advisory scans · vendor-only findings | On request |
As sourcetrust.dev lists them, read 29 Sept 2026. The maker's own page has the final word.
Getting started
- Visit https://sourcetrust.dev/.
- Connect a repository through GitHub, GitLab, or Azure DevOps, or import a lockfile or SBOM.
- Review the dependency records and decide on packages flagged for a decision.
- Confirm the records before publishing an attestation page or downloading an export.
Verdict
SourceTrust combines dependency inventory, license review, and shareable compliance outputs, with review required before publication. Teams should check eligibility and billing triggers, and treat it as software tooling rather than legal advice.
Questions
Is there a free plan?
Yes. Eligible public GitHub projects can use the Open source plan for $0, subject to fair use and SourceTrust attribution. Projects, imports, and license reviews are free for as long as needed.
How much do paid plans cost?
Per-project billing is $29 a month or $299 a year. Each option includes two watched branches per shipped product.
Does SourceTrust offer a free trial?
No. Projects, dependency imports, and license reviews are free for as long as needed; standard project billing begins on the first publish or export download.
Which inputs and integrations does it support?
Listed repository connections are GitHub, GitLab, and Azure DevOps. It also accepts lockfiles and SBOMs, including CycloneDX and SPDX, and lists support for 14 formats across 9 ecosystems.
Does SourceTrust read source code?
SourceTrust says it reads lockfiles and SBOMs, not source code, and parses lockfiles in the browser before upload.
Is SourceTrust legal advice?
No. The company describes it as software tooling for license compliance, not a law firm or legal advice.
Facts from SourceTrust's own pages
- Audience and limitation
- The company describes the product as license compliance infrastructure for shipped products and says it is software tooling, not a law firm or legal advice. · sourcetrust.dev, 29 Sept 2026
- Change monitoring
- Repository sync and publish-drift checks flag when the live inventory differs from the published snapshot. · sourcetrust.dev, 29 Sept 2026
- Data access
- SourceTrust says it reads lockfiles and SBOMs, never source code, and parses lockfiles in the browser before upload. · sourcetrust.dev, 29 Sept 2026
- Exports
- Outputs include a hosted attestation page, THIRD_PARTY_LICENSES.md, NOTICE, CycloneDX, SPDX, JSON, CSV, plist, and branded PDF. · sourcetrust.dev, 29 Sept 2026
- Founded
- 2026 · sourcetrust.dev, 28 Sept 2026
- Free review
- Projects, dependency imports, and license reviews are free for as long as needed; standard project billing starts on first publish or export download. · sourcetrust.dev, 29 Sept 2026
- Headquarters
- Copenhagen, Denmark · sourcetrust.dev, 28 Sept 2026
- Integrations
- The site lists GitHub, GitLab, and Azure DevOps repository connections, plus lockfile and SBOM imports. · sourcetrust.dev, 29 Sept 2026
- Inventory
- It gathers direct and transitive dependencies from repositories, lockfiles, and SBOMs into one inventory. · sourcetrust.dev, 29 Sept 2026
- Open source eligibility
- Eligible public GitHub projects can publish an attestation page for $0 with no card or trial clock, subject to fair use and SourceTrust attribution. · sourcetrust.dev, 29 Sept 2026
- Purpose
- SourceTrust helps teams review third-party software licenses and publish a shareable license compliance page for products they ship. · sourcetrust.dev, 29 Sept 2026
- Review gates
- Nothing is published until the team has reviewed and confirmed the record, and the product flags packages that need a decision. · sourcetrust.dev, 29 Sept 2026
- Security controls
- Pages can be password-protected and excluded from search engines, and optional vulnerability findings remain vendor-only. · sourcetrust.dev, 29 Sept 2026
- Support
- SourceTrust offers a live walkthrough and lists [email protected] for platform questions. · sourcetrust.dev, 29 Sept 2026
- Supported inputs
- The platform overview says it supports 14 formats across 9 ecosystems, including CycloneDX SBOM uploads. · sourcetrust.dev, 29 Sept 2026
- Verification
- SourceTrust retrieves the shipped package, checks it against the registry digest, and reads the license text inside it. · sourcetrust.dev, 29 Sept 2026