Freedom251 › Open Source License Compliance Software
license-comply
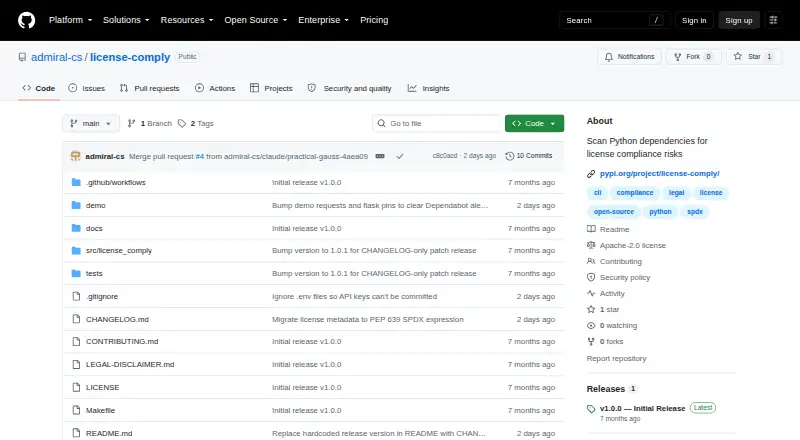
What license-comply is
license-comply is a self-hosted tool for reviewing open-source license risks in Python project dependencies. It reads dependencies from pyproject.toml or requirements.txt and includes installed transitive dependencies by default. Findings are classified as clean, notice, warning, or critical, with plain-English explanations and remediation steps. Organizations can set policies to allow, deny, or flag licenses for review. Reports are available in the terminal and as Markdown, HTML, or JSON; CI mode provides exit codes for build pipelines. The tool retrieves license metadata through the PyPI JSON API and caches lookup results locally for seven days by default. Optional executive summaries use Claude by default or OpenAI, and require an API key. The free Open-source plan costs nothing and supports Python 3.9 or later. The project is intended to help lawyers and compliance professionals understand license findings, but its output is not legal advice. It relies on PyPI metadata rather than reading package LICENSE files, supports Python packages only, and does not detect copied code.
Who it suits
It suits compliance professionals and lawyers reviewing Python dependencies, as well as development teams that want license checks in build pipelines. Organizations using other package ecosystems will need a different scope of coverage.
What it does well
- Scans declared and installed transitive dependencies
- Findings include explanations and remediation steps
- Custom policies can allow, deny, or flag licenses
- Reports support terminal, Markdown, HTML, and JSON
- Free plan supports Python 3.9 or later
What to know first
- Supports Python packages only
- Relies on PyPI metadata, not LICENSE files
- Does not detect copied code
- Complex nested SPDX expressions are unsupported
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Open-source | Python dependencies only · Python 3.9+ | Free |
| Open source | Python packages only · requires Python 3.9 or later | Free |
As github.com lists them, read 7 Oct 2026. The maker's own page has the final word.
Verdict
license-comply offers free Python dependency checks with customizable policies and multiple report formats. Treat findings as an aid rather than legal advice, and keep in mind that metadata errors can affect results.
Facts from license-comply's own pages
- AI summaries
- Optional executive summaries use Claude by default or OpenAI and require an API key. · github.com, 7 Oct 2026
- Caching
- PyPI lookup results are cached locally for seven days by default. · github.com, 7 Oct 2026
- Custom policies
- Policy files let organizations allow, deny, or flag licenses for review. · github.com, 7 Oct 2026
- Dependency discovery
- Reads dependencies from pyproject.toml or requirements.txt and scans installed transitive dependencies by default. · github.com, 7 Oct 2026
- Ecosystem limitation
- It supports Python packages and does not yet support npm, Go modules, or other ecosystems. · github.com, 7 Oct 2026
- Integrations
- Looks up license metadata through the PyPI JSON API and supports optional AI summaries using Claude or OpenAI, which require an API key. · github.com, 7 Oct 2026
- Intended audience
- The author says the tool is intended to help lawyers and compliance professionals who may not have deep software engineering backgrounds understand what it does and why. · github.com, 7 Oct 2026
- Legal limitation
- The project says its output is not legal advice and recommends consulting qualified legal counsel for situation-specific advice. · github.com, 7 Oct 2026
- License expression support
- It handles SPDX OR and AND expressions but not complex nested expressions. · github.com, 7 Oct 2026
- Limits
- The tool relies on declared PyPI metadata rather than scanning license files, supports Python packages only, and does not detect copied code. · github.com, 7 Oct 2026
- Maker
- The project says it was built by Sam Clearwater, a technology and AI lawyer. · github.com, 7 Oct 2026
- Metadata limitation
- The tool relies on PyPI metadata rather than scanning the actual text of package LICENSE files, so inaccurate or missing metadata may produce incorrect results. · github.com, 7 Oct 2026
- Policy rules
- A customizable policy engine lets organizations allow, deny, or flag licenses for review. · github.com, 7 Oct 2026
- Purpose
- Scans Python project dependencies for open-source licenses and analyzes compliance risks based on project type. · github.com, 7 Oct 2026
- Report formats
- Reports can be generated in terminal, Markdown, HTML, and JSON formats. · github.com, 7 Oct 2026
- Reports
- Generates terminal, Markdown, HTML, and JSON reports, with CI mode and exit codes for build pipelines. · github.com, 7 Oct 2026
- Risk analysis
- Findings are rated clean, notice, warning, or critical and include plain-English explanations and remediation steps. · github.com, 7 Oct 2026
- Risk reports
- Reports findings as clean, notice, warning, or critical, with plain-English explanations and remediation steps. · github.com, 7 Oct 2026
- Security reporting
- The security policy asks users to report vulnerabilities through GitHub private vulnerability reporting and says not to open a public issue for them. · github.com, 7 Oct 2026
- Support
- The project invites bug reports and feature requests through GitHub issues and welcomes pull requests. · github.com, 7 Oct 2026