Freedom251 › Honeypot Software
OpenCanary
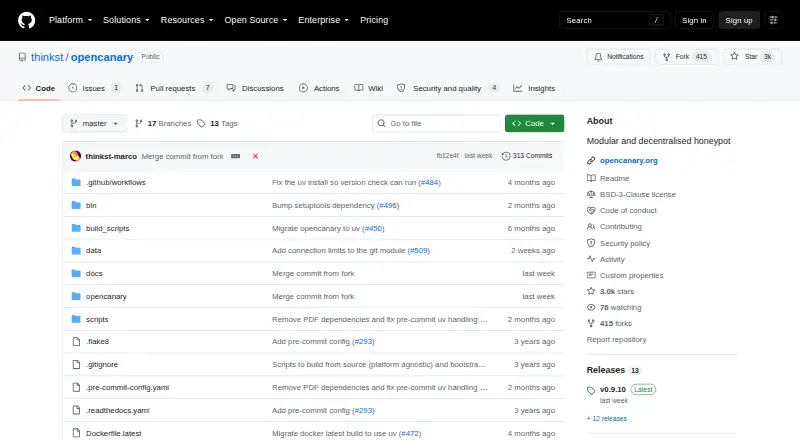
What OpenCanary is
OpenCanary is free, self-hosted software that acts as a network honeypot: it imitates services and alerts when someone interacts with them after entering a non-public network. It runs as a daemon and can report a source IP address and a possible breach location. Its service modules include SSH, FTP, Git, web services, databases, Telnet, SNMP, SIP, VNC, Redis, TFTP, NTP and TCP banners. Alerts can go to files, Syslog, email, HTTP webhooks, Slack, Microsoft Teams or HPFeeds-compatible daemons. Webhooks support GET, POST and PUT. The companion opencanary-correlator can combine related events, such as repeated login attempts, into one email or SMS alert. The project describes its resource requirements as very low, with use on a Raspberry Pi or a minimally resourced virtual machine. Documentation covers Ubuntu and macOS installation and Docker deployment on Linux hosts. Linux has the broadest options: SMB monitoring is unavailable on macOS, and portscan monitoring is Linux-only and disabled in Docker. The configuration file should be root-owned and writable only by root because it is read with root privileges.
Who it suits
It suits administrators who want a self-hosted way to detect interactions with decoy network services and route alerts to their chosen destinations. Linux deployments have the most module options.
What it does well
- Imitates a broad range of network services.
- Supports email, Syslog, webhooks and chat alerts.
- Correlator groups related events into one alert.
- Can run on a Raspberry Pi.
- Free plan: free.
What to know first
- SMB monitoring is unavailable on macOS.
- Portscan monitoring is Linux-only.
- Portscan monitoring is disabled in Docker.
- Configuration must be writable only by root.
Limits
OpenCanary is listed as free, with self-hosted deployment. Linux offers the most options: SMB monitoring is unavailable on macOS, while portscan monitoring is Linux-only and disabled in Docker.
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| OpenCanary | Open-source software · self-hosted deployment | Free |
As github.com lists them, read 2 Oct 2026. The maker's own page has the final word.
Getting started
- Open the OpenCanary project website on GitHub.
- Choose an installation route documented for Ubuntu or macOS, or Docker on a Linux host using host networking.
- Configure the decoy service modules and alert destinations you want to use.
- Make the configuration file root-owned and writable only by root.
- If using optional SNMP or Windows File Share monitoring, provide Scapy or Samba as required.
OpenCanary is a self-hosted honeypot that raises alerts when someone interacts with decoy network services. It suits defenders who want to monitor non-public networks on modest Linux or macOS infrastructure. Its wide range of decoys and alert routes make it a capable free option, but Linux offers more modules and safe operation depends on protecting its configuration.
Overview
Running as a daemon, OpenCanary mimics network-accessible services to catch activity after an attacker reaches a network that is not public. Native modules cover SSH, FTP, Git, HTTP, HTTPS, HTTP proxy, MSSQL, MySQL, Telnet, SNMP, SIP, VNC, Redis, TFTP, NTP and TCP banners. Alerts can include the source IP and an indication of where a breach may have occurred, giving defenders useful leads for investigation.
Its very low resource requirements make it practical to run on a Raspberry Pi or a minimally resourced virtual machine. OpenCanary is BSD-licensed open-source software maintained by Thinkst Canary, and is the open-source version of the company's commercial honeypot.
Key features
Alerting is flexible: destinations include files, Syslog, SMTP email, HTTP webhooks, Slack, Microsoft Teams and HPFeeds-compatible daemons. The customizable webhook handler supports GET, POST and PUT, so teams can send events to an HTTP endpoint and adapt delivery to their own systems. Chat notifications through Slack or Teams are available via webhooks.
The companion opencanary-correlator can combine related events, such as a sequence of individual brute-force login attempts, into one email or SMS alert. That reduces repetitive notifications while preserving a signal of the broader activity. Optional modules extend monitoring: SMB watches Samba logs for files opened in a Windows file share, while portscan monitoring uses iptables to detect scans.
These additions bring dependencies and deployment constraints. SNMP requires Scapy, and SMB monitoring requires Samba. Portscan monitoring is Linux-only, relies on iptables rather than nftables, and is automatically disabled in Dockerized OpenCanary.
Pricing
OpenCanary: free. This is open-source software for self-hosted deployment, with no software charge. The free plan suits operators able to provide and maintain their own host; it does not remove the need to configure alert delivery or secure the installation.
Platforms
OpenCanary supports Linux, macOS and self-hosted deployment, with the broadest options on Linux. The SMB module is unavailable on macOS, and portscan detection is limited to Linux. Docker deployment is documented for Linux hosts using host networking; the portscan module is disabled in Dockerized deployments.
Privilege handling deserves particular care. Because the configuration file is read while the process has root privileges, the project recommends making it root-owned and writable only by root; a writable configuration can permit privilege escalation. When started with uid and gid flags, OpenCanary drops root privileges after binding to its ports.
Who it's for
OpenCanary is a good fit for defenders who can self-host a network honeypot and want numerous service decoys without dedicating much compute capacity. Its alert options suit teams that can manage their own email, syslog, webhook or chat routing. It is a weaker fit for deployments that need portscan monitoring on macOS or in Docker, or SMB monitoring on macOS.
Pros and cons
- Broad native decoy coverage: modules span network, database and other common services, giving defenders multiple ways to attract and flag interaction.
- Lightweight self-hosting: Raspberry Pi and minimally resourced virtual machine support lowers the infrastructure hurdle.
- Flexible notifications: webhooks, chat routes and event correlation support different alert workflows and can consolidate related events.
- Uneven platform support: Linux has the fullest module set; macOS lacks SMB monitoring, while portscan detection requires Linux and iptables.
- Configuration security is operationally important: the root-read configuration must be writable only by root to avoid creating a privilege-escalation path.
Alternatives
Canarytokens is another free option, with platforms spanning Android, iOS, self-hosted, web and Windows; consider it when those platforms matter more than OpenCanary's network-service decoy approach. T-Pot is a free, self-hosted alternative for Linux, macOS and Windows, though its hardware and network requirements apply.
Beelzebub offers a free self-hosted core framework on Linux and API platforms, with a free trial also available. Cowrie is a free, BSD-licensed SSH and Telnet honeypot for Linux and self-hosting, a narrower stated scope than OpenCanary's multiple service modules.
Endlessh is a free standalone C SSH tarpit for Linux, with a default maximum of 4096 clients. Dionaea is a free, open-source Linux honeypot under GPLv2+. Heralding is a free Linux honeypot under GPL-3.0. Conpot is another free Linux honeypot.
Browse the Honeypot Software category for more options.
Verdict
Choose OpenCanary if you want a lightweight, free, self-hosted honeypot with broad network-service decoys and multiple alert routes. Its main advantage is the combination of protocol breadth and low resource needs; look elsewhere if your deployment depends on portscan monitoring outside Linux with iptables, or on SMB monitoring under macOS.
Verdict
OpenCanary offers a range of decoy services and alert routes for self-hosted network monitoring. Review platform and module limits, and secure its root-read configuration file.
Questions
How much does OpenCanary cost?
The listed plan is free. It is free and self-hosted.
Which platforms does it support?
The listed platforms are Linux, macOS, and self-hosted deployment. Docker deployment is documented for Linux hosts using host networking.
What alert destinations are available?
Documented destinations include files, Syslog, SMTP email, HTTP webhooks, Slack, Microsoft Teams, and HPFeeds-compatible daemons.
Is OpenCanary open source?
Yes. The PyPI listing identifies it as OSI Approved BSD licensed software.
Who maintains OpenCanary?
It is maintained by Thinkst Canary and is described as the open-source version of Thinkst Canary's commercial honeypot.
What platform limits should I know about?
The SMB module is unavailable on macOS. Portscan monitoring is Linux-only, uses iptables rather than nftables, and is automatically disabled in Dockerized OpenCanary.
Facts from OpenCanary's own pages
- Alert channels
- The documentation lists Syslog, email, and the opencanary-correlator as alert destinations. · github.com, 1 Oct 2026
- Alert destinations
- Documented logging and alert options include files, Syslog, SMTP email, HTTP webhooks, Slack, Microsoft Teams, and HPFeeds-compatible daemons. · opencanary.readthedocs.io, 2 Oct 2026
- Alert details
- Alerts can identify the threat source IP address and where the breach may have occurred. · github.com, 1 Oct 2026
- Chat integrations
- Webhooks can post to Slack or Microsoft Teams channels. · github.com, 1 Oct 2026
- Correlator
- The companion opencanary-correlator can combine related events into a single email or SMS alert. · opencanary.readthedocs.io, 2 Oct 2026
- Deployment
- The project documents installation on Ubuntu and macOS, plus Docker deployment on Linux hosts using host networking. · github.com, 2 Oct 2026
- Event correlation
- The correlator coalesces multiple related events, such as individual brute-force login attempts, into one alert sent by email or SMS. · github.com, 1 Oct 2026
- Extra modules
- Optional SMB monitoring watches Samba logs for files opened in a Windows file share, and optional portscan monitoring uses iptables to detect scans. · opencanary.readthedocs.io, 2 Oct 2026
- License
- The PyPI listing identifies OpenCanary as OSI Approved BSD licensed software. · pypi.org, 1 Oct 2026
- Maintainer and commercial relation
- OpenCanary is maintained by Thinkst Canary and described as the open-source version of its commercial Thinkst Canary honeypot. · github.com, 2 Oct 2026
- Operation
- It runs as a daemon that imitates network services and sends alerts when they are accessed. · github.com, 2 Oct 2026
- Optional modules
- The optional SNMP module requires Scapy, while the Windows File Share module requires Samba. · github.com, 1 Oct 2026
- Platform limits
- Linux offers the most options; the SMB module is unavailable on macOS, and portscan is Linux-only and uses iptables rather than nftables. · github.com, 2 Oct 2026
- Portscan limit
- The portscan module is supported only on Linux hosts because it modifies iptables rules, and it is automatically disabled in Dockerized OpenCanary. · github.com, 1 Oct 2026
- Privilege handling
- When started with uid and gid flags, OpenCanary drops root privileges after binding to its ports. · github.com, 2 Oct 2026
- Protocol mimicry
- It can mimic an array of network-accessible services for attackers to interact with. · github.com, 1 Oct 2026
- Protocols
- Native service modules include SSH, FTP, Git, HTTP, HTTPS, HTTP proxy, MSSQL, MySQL, Telnet, SNMP, SIP, VNC, Redis, TFTP, NTP, and TCP banner. · opencanary.readthedocs.io, 2 Oct 2026
- Purpose
- OpenCanary is a multi-protocol network honeypot intended to detect attackers interacting with services on non-public networks. · github.com, 2 Oct 2026
- Resource needs
- The project says it has very low resource requirements and can run on a Raspberry Pi or a minimally resourced virtual machine. · github.com, 2 Oct 2026
- Resource use
- OpenCanary has extremely low resource requirements and can run on a Raspberry Pi or a minimally resourced virtual machine. · github.com, 1 Oct 2026
- Security configuration
- The project recommends making its configuration file root-owned and writable only by root because it is read while the process has root privileges. · github.com, 2 Oct 2026
- Security guidance
- The project recommends making the configuration file root-owned and writable only by root because writable configuration can allow privilege escalation. · github.com, 1 Oct 2026
- Security reports
- Thinkst accepts vulnerability reports at [email protected] or through GitHub and says it will request a CVE on the reporter’s behalf for reported security bugs. · github.com, 2 Oct 2026
- Support
- Bug reports are requested through GitHub, security vulnerabilities through the project security policy, and feature requests through the project tracker. · github.com, 1 Oct 2026
Where OpenCanary stands on Freedom251
- Honeypot Software#10 of 21