nono
What nono is
nono is a free, open-source, self-hosted runtime for isolating AI agents, scripts, build tools, and other processes. It creates short-lived sandboxes for each tool invocation, limiting files, network routes, arguments, and credentials. Kernel enforcement uses Landlock on Linux and Windows through WSL2, and Seatbelt on macOS; the product says root access is unnecessary. Filesystem allow-lists cannot be loosened after an application starts. JSON policy profiles describe agent access and can be version-controlled with code. nono records SHA-256, content-addressed filesystem snapshots before and after sessions and describes atomic session restoration. Its audit log forms a Merkle tree and commits a SHA-256 root when a session ends. Credentials can be injected at the boundary so agents do not see real keys. Network policies can block access, permit domains, filter endpoints, or send requests through an upstream proxy for approval. Listed integrations include Claude Code, OpenCode, Codex, Antigravity, Goose, OpenClaw, GitHub Copilot, Qwen Code, Pi, and Hermes. Interfaces include a CLI, Rust core library, and Go, TypeScript, and Python SDKs.
Who it suits
nono suits developers and teams that need policy-controlled isolation for AI agents or other automated processes. It is aimed at use from individual laptops to fleets, with composable policies, credential protection, and auditable execution.
What it does well
- Free and open source
- Invocation-scoped sandboxes isolate tool calls
- Kernel-enforced filesystem allow-lists
- Proxy controls network requests and credentials
- SHA-256 snapshots support session rollback
- CLI plus Rust, Go, TypeScript, and Python interfaces
What to know first
- Native Windows is not supported
- WSL2 reports 84% feature coverage
- Advanced WSL2 capabilities have limitations
Limits
Windows support runs through WSL2, where the site reports 84% feature coverage. Capability elevation and per-port network rules have limitations there, and native Windows is unsupported.
Getting started
- Open the nono website
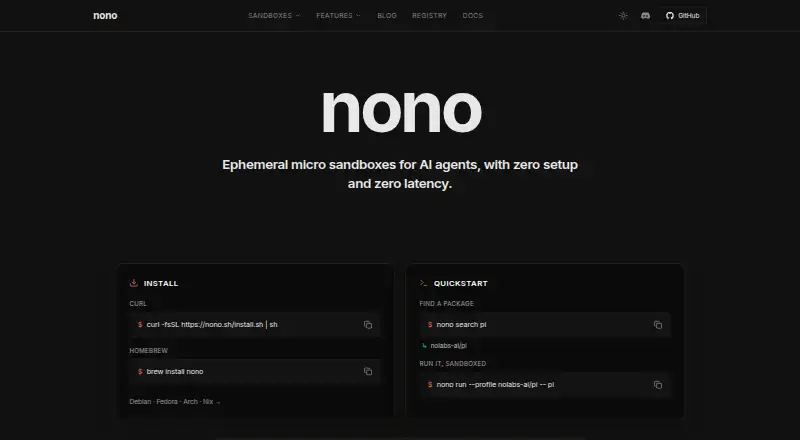
- Install with the shell installer or Homebrew
- Follow the Debian, Fedora, Arch, or Nix installation instructions
- Run it through the CLI or integrate with the Rust, Go, TypeScript, or Python interfaces
- Apply a JSON policy profile and connect a listed agent
Verdict
Pick nono if you want a free, self-hosted sandbox for agents with kernel enforcement, policy files, credential boundaries, and audit records. Look elsewhere if native Windows support is required or if you need capabilities limited on WSL2.
Questions
Is nono free?
Yes. The maker describes it as free and open source, with no paid plan listed.
Which platforms does nono support?
It supports Linux kernel 5.13 or newer, macOS, and Windows through WSL2. Native Windows is not supported.
Which agents can connect to nono?
Listed integrations include Claude Code, OpenCode, Codex, Antigravity, Goose, OpenClaw, GitHub Copilot, Qwen Code, Pi, and Hermes.
Does nono provide developer APIs?
Yes. Documentation lists a CLI, a Rust core library, and SDKs for Go, TypeScript, and Python.
How are credentials handled?
Proxy-based injection keeps real API keys outside the agent while requests pass through a localhost proxy.
Facts from nono's own pages
- Agent compatibility
- The site lists Claude Code, OpenCode, Codex, Antigravity, Goose, OpenClaw, GitHub Copilot, Qwen Code, Pi, and Hermes. · nono.sh, 4 Oct 2026
- Agent integrations
- The site lists profiles or registry packages for Claude Code, OpenCode, Codex, Antigravity, Goose, OpenClaw, GitHub Copilot, Qwen Code, Pi, and Hermes. · nono.sh, 8 Oct 2026
- Audience
- The maker describes use from individual laptops through fleets of agents and highlights composable policies, per-tool sandboxing, credential protection, and auditable execution. · nono.sh, 8 Oct 2026
- Audit
- Filesystem operations, network attempts, and command executions can be recorded in a SHA-256 Merkle-tree audit trail and exported as JSON. · nono.sh, 8 Oct 2026
- Credential handling
- The site says credentials are injected at the boundary and never exposed to the agent. · nono.sh, 4 Oct 2026
- Credential protection
- With proxy-based credential injection, the agent uses a localhost proxy and does not see the real API key. · nono.sh, 8 Oct 2026
- Developer interfaces
- The documentation lists a CLI, a Rust core library, and Go, TypeScript, and Python SDKs. · nono.sh, 4 Oct 2026
- Execution isolation
- It creates ephemeral, invocation-scoped micro sandboxes for tool calls, with scoped files, network routes, arguments, and credentials. · nono.sh, 4 Oct 2026
- Installation
- The homepage offers a shell installer, Homebrew, and links to Debian, Fedora, Arch, and Nix installation instructions. · nono.sh, 4 Oct 2026
- Instruction verification
- Its Sigstore-based provenance feature verifies whether agent instruction files were signed by trusted identities before execution. · nono.sh, 8 Oct 2026
- Isolation
- It uses Landlock on Linux and WSL2 and Seatbelt on macOS to enforce filesystem allow-lists that cannot be loosened after application. · nono.sh, 8 Oct 2026
- Kernel enforcement
- The OS sandbox uses Landlock on Linux and Windows/WSL2 and Seatbelt on macOS; the page says no root is required. · nono.sh, 4 Oct 2026
- Network control
- The homepage describes proxy-mediated network access where policy can allow or deny requests and route out-of-policy actions for human approval. · nono.sh, 4 Oct 2026
- Network controls
- It can block network access, allow specific domains, filter API endpoints, and route filtered traffic through an upstream proxy. · nono.sh, 8 Oct 2026
- Policy profiles
- JSON profiles define agent access and can be version-controlled alongside code. · nono.sh, 4 Oct 2026
- Pricing
- The maker's site and opened product pages provide no subscription price or paid plan; a maker-authored article describes nono as free and open source. · nono.sh, 8 Oct 2026
- Product
- nono describes itself as agent runtime security with kernel-enforced boundaries for AI agents. · nono.sh, 4 Oct 2026
- Purpose
- nono is a kernel-enforced sandbox CLI and SDK for isolating AI agents, scripts, build tools, and other processes. · nono.sh, 8 Oct 2026
- Rollback
- nono can take SHA-256 content-addressed snapshots before and after a session and restore the original state with a command. · nono.sh, 8 Oct 2026
- SDKs
- The documentation describes a Rust core library and Go, TypeScript, and Python SDKs for integrating sandboxing into applications. · nono.sh, 8 Oct 2026
- Support
- The documentation links to GitHub for source code and issues and Discord for community support. · nono.sh, 8 Oct 2026
- Supported platforms
- The installation guide lists Linux kernel 5.13+, macOS, and Windows through WSL2 as supported, and says native Windows is not supported. · nono.sh, 8 Oct 2026
- Windows caveat
- On WSL2, the page reports 84% feature parity and says capability elevation and per-port network rules have limitations. · nono.sh, 4 Oct 2026
- WSL2 limitation
- The site reports 84% feature coverage on WSL2 and notes that some advanced capabilities are unavailable because of kernel limitations. · nono.sh, 8 Oct 2026
Where nono stands on Freedom251
- Sandbox Software#12 of 26