Freedom251 › Container Build Tools
nix2container
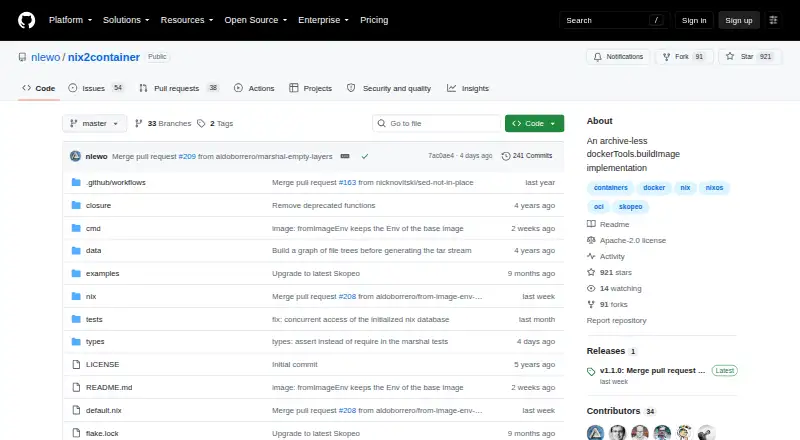
What nix2container is
nix2container is a free, open-source Nix library for building container images without writing tarballs to the Nix store. Its daemonless build method can skip layers that have already been pushed, while dedicated layers let dependencies remain separate so unchanged parts need not be rebuilt or pushed. Image configuration follows the OCI image specification, and examples show loading images into Docker and Podman. Base images can be pulled from a registry by digest or provided through a manifest file. When creating tar layers, file permissions can be set without writing those permissions to the Nix store. The documentation covers registry authentication for Nix daemon builds using Docker credentials and a Skopeo auth file. Image-pull functions default tlsVerify to true. Linux is the listed platform, and the getting-started example uses x86_64-linux. The repository includes the Apache License, Version 2.0. Commercial support is available from the maintainer for customizations, image optimization, guidance, and bug fixes. The documentation notes that container tests cannot run in the Nix sandbox.
Who it suits
nix2container suits Linux users building container images with Nix who want daemonless builds and control over image layers. Teams needing customizations or guidance can contact the maintainer about commercial support.
What it does well
- Builds images without writing tarballs to the Nix store
- Can skip layers already pushed to a registry
- Supports OCI image configuration
- Examples cover Docker and Podman loading
- Allows permissions to be set when creating tar layers
What to know first
- Listed platform is Linux
- Container tests do not run in the Nix sandbox
Plans
| Plan | Billed and limits | Price |
|---|---|---|
| Free | Open-source Nix library | Free |
As github.com lists them, read 4 Oct 2026. The maker's own page has the final word.
Getting started
- Open the project at https://github.com/nlewo/nix2container.
- Use the free, open-source Nix library.
- Follow the getting-started example, which selects x86_64-linux.
- Load images into Docker or Podman using the documented examples.
- Configure registry authentication for Nix daemon builds with Docker credentials and a Skopeo auth file if needed.
Verdict
nix2container offers a free way to build Nix container images with reusable layers and OCI configuration. Its Linux focus and documented sandbox testing limitation are worth noting.
Questions
What does nix2container cost?
It is free. The Free plan costs nothing.
Is nix2container open source?
Yes. The repository includes the Apache License, Version 2.0.
Which platforms are listed?
Linux is the listed platform. The getting-started example selects x86_64-linux.
Can it reuse container layers?
Yes. It can skip layers already pushed, and dedicated layers can keep unchanged dependencies from needing another build or push.
Can I load its images into Docker or Podman?
Examples show loading images into both Docker and Podman.
Is commercial support available?
Yes. The maintainer offers support for customizations, image optimization, best-practices guidance, and bug fixes.
Facts from nix2container's own pages
- Architecture
- The getting-started example selects the x86_64-linux system. · github.com, 4 Oct 2026
- Base images
- Can pull base images from a container registry by digest or from a supplied manifest file. · github.com, 4 Oct 2026
- Image formats
- The image configuration follows the OCI image specification. · github.com, 4 Oct 2026
- Image loading
- Examples show loading images into Docker and Podman. · github.com, 4 Oct 2026
- Layer caching
- Dedicated layers can isolate dependencies so unchanged layers need not be rebuilt or pushed. · github.com, 4 Oct 2026
- Layer reuse
- Can skip already pushed layers without rebuilding them. · github.com, 4 Oct 2026
- License
- The repository includes the Apache License, Version 2.0. · github.com, 4 Oct 2026
- Permissions
- File permissions can be set when a tar layer is created without writing those permissions to the Nix store. · github.com, 4 Oct 2026
- Purpose
- Builds container images with Nix without writing tarballs to the Nix store. · github.com, 4 Oct 2026
- Registry authentication
- The documentation describes configuring registry authentication for Nix daemon builds using Docker credentials and a Skopeo auth file. · github.com, 4 Oct 2026
- Security setting
- Image-pull functions default tlsVerify to true. · github.com, 4 Oct 2026
- Support
- Commercial support is available for customizations, image optimizations, best-practices guidance, and bug fixes by contacting the maintainer. · github.com, 4 Oct 2026
- Testing limitation
- The project documentation says its container tests do not run in the Nix sandbox because running a container there is currently not possible. · github.com, 4 Oct 2026
Where nix2container stands on Freedom251
- Container Build Tools#27 of 34